

CVE-2022-41114
 gmh5225/cve-2022-41114
Windows Bind Filter Driver Elevation of Privilege Vulnerability. CVE project by @Sn0wAlice
exploitationinformation-gatheringprivilege-escalation+1
1
gmh5225/cve-2022-41114Windows Bind Filter Driver Elevation of Privilege Vulnerability. CVE project by @Sn0wAlice
 skraft9/cve-2025-44823
Authenticated API Key Exposure in Nagios Log Server 2024R1.3.1
 nxploited/cve-2026-39987
marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability
 maikneysm/autopwn-titanic.htb
This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
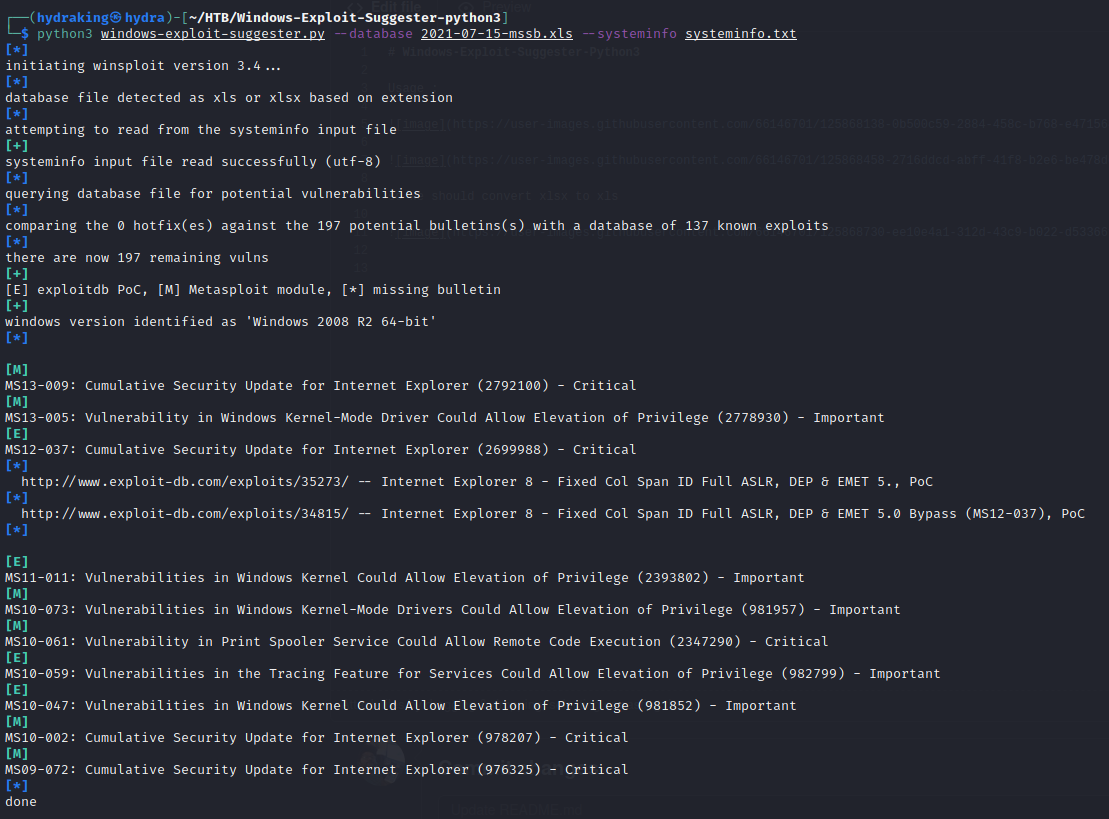 h3x0v3rl0rd/windows-exploit-suggester-python3
Python-based cross-referencing tool: uses Windows systeminfo and MS security bulletins to detect unpatched vulnerabilities and suggest privilege…
 padayali-jd/cve-2025-25968
Proof-of-concept exploit for CVE-2025-25968, an improper access control vulnerability in DDSN Interactive cm3 Acora CMS v10.1.1. Enables…
 inj3ction/cve-2017-7921-exp
Exploit for CVE-2017-7921 targeting Hikvision devices with improper authentication. Retrieves user lists, camera snapshots, and configuration files…
 dayiliwaseem/cve-2022-39196-
Black board CMS Escalation of Privileges
 sarpantkeltiek/cve-2024-37010
Exploit for the CVE-2024-37010: access other user's external storage & lateral movement
 h3x0v3rl0rd/cve-2019-14287
Shell script to detect CVE-2019-14287 sudo privilege escalation vulnerability. Scans systems for the flaw and reports affected configurations.
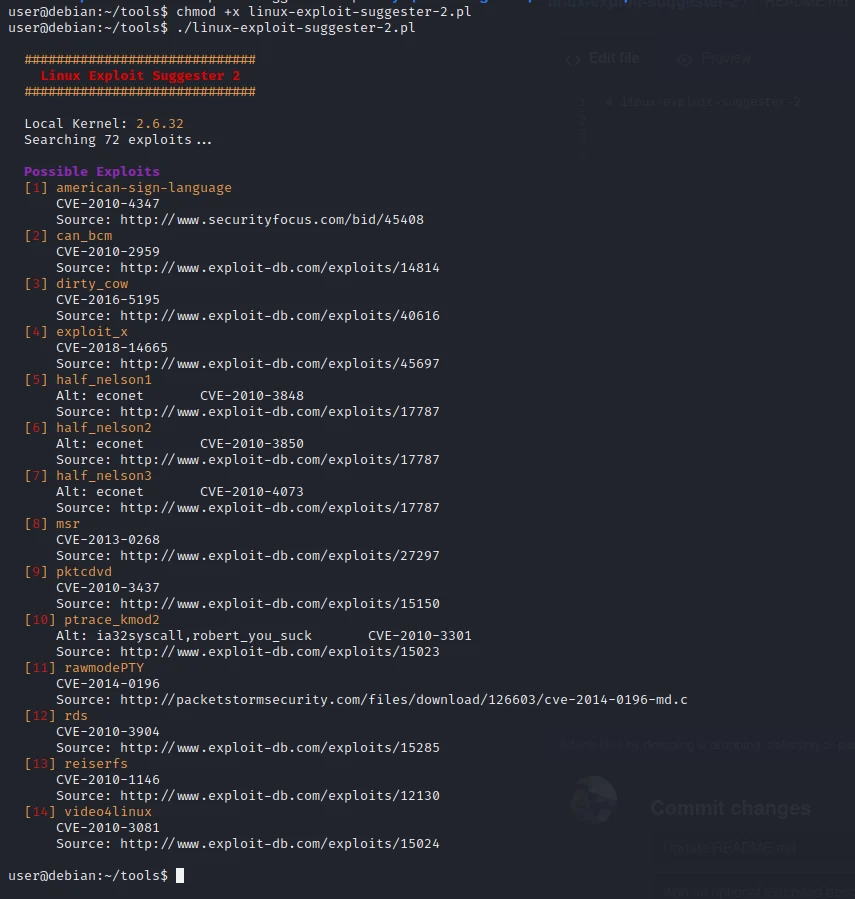 h3x0v3rl0rd/linux-exploit-suggester-2
Post-exploitation utility that scans kernel/OS version and configuration to suggest applicable local privilege escalation exploits.
 randomrobbiebf/cve-2024-52382
Matix Popup Builder <= 1.0.0 - Unauthenticated Arbitrary Options Update
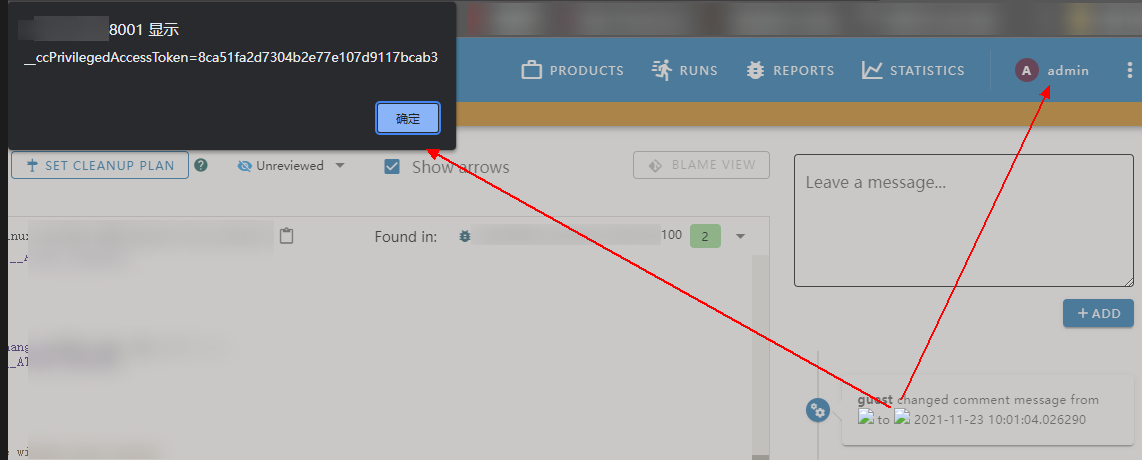 hyperkopite/cve-2021-44217
Proof-of-concept for a stored XSS vulnerability (CVE-2021-44217) in Ericsson CodeChecker's comments component, enabling cookie theft and sensitive…
 underprotection/cve-2020-24028
Proof-of-concept for CVE-2020-24028: authenticated privilege escalation via insecure permissions in ForLogic Qualiex v1 and v3, enabling user…
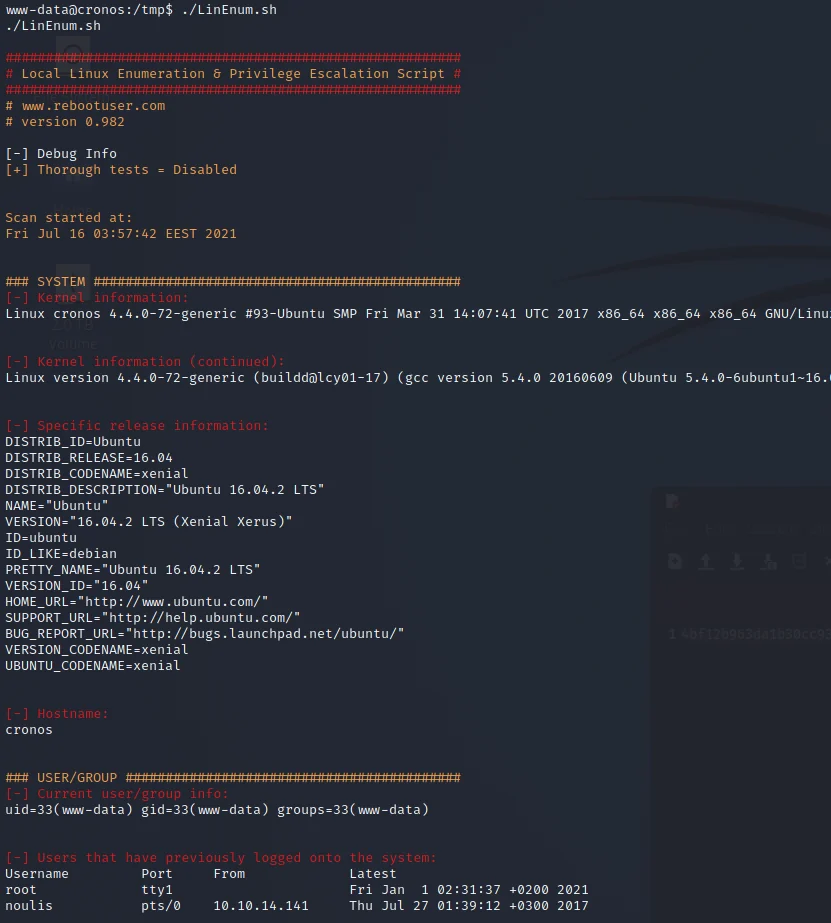 h3x0v3rl0rd/lin_enum
Shell script for automated enumeration of Linux systems to identify privilege escalation vectors and configuration weaknesses.
 hackwidmaddy/cve-2024-57523.
CVE-2024-57523 - CSRF Vulnerability in Users.php - SourceCodester Packers and Movers Management System 1.0
 notitssixtyn3in/cve-2025-4162029
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162029) in Copilot, enabling unauthorized account access via user ID…