
Vmware-ESXI
 wtn-arny/vmware-esxi
CVE-2024-37085 unauthenticated shell upload to full administrator on domain-joined esxi hypervisors.
authenticationexploitationpenetration-testing+3
wtn-arny/vmware-esxiCVE-2024-37085 unauthenticated shell upload to full administrator on domain-joined esxi hypervisors.
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 sh3lldon/fullbypass
A tool which bypasses AMSI (AntiMalware Scan Interface) and PowerShell CLM (Constrained Language Mode) and gives you a FullLanguage PowerShell…
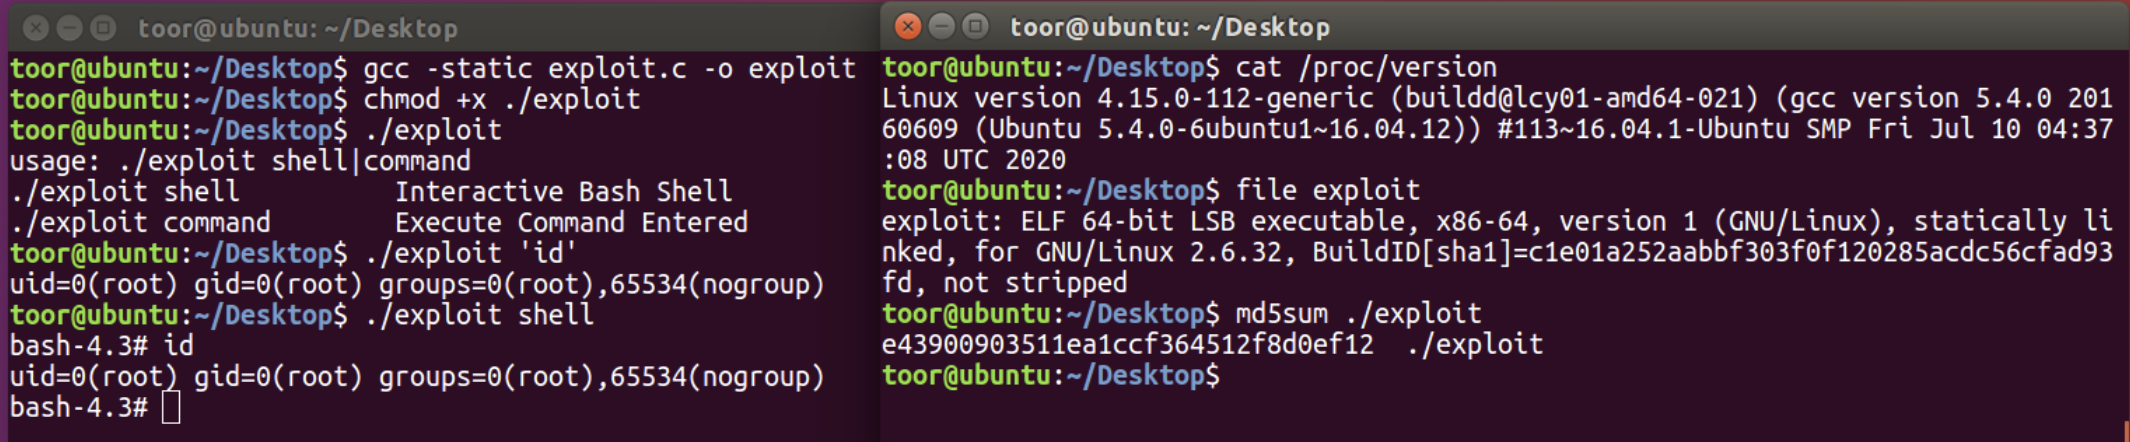 inspiringz/cve-2021-3493
CVE-2021-3493 Ubuntu OverlayFS Local Privesc (Interactive Bash Shell & Execute Command Entered)
 arinerron/cve-2022-0847-dirtypipe-exploit
A root exploit for CVE-2022-0847 (Dirty Pipe)
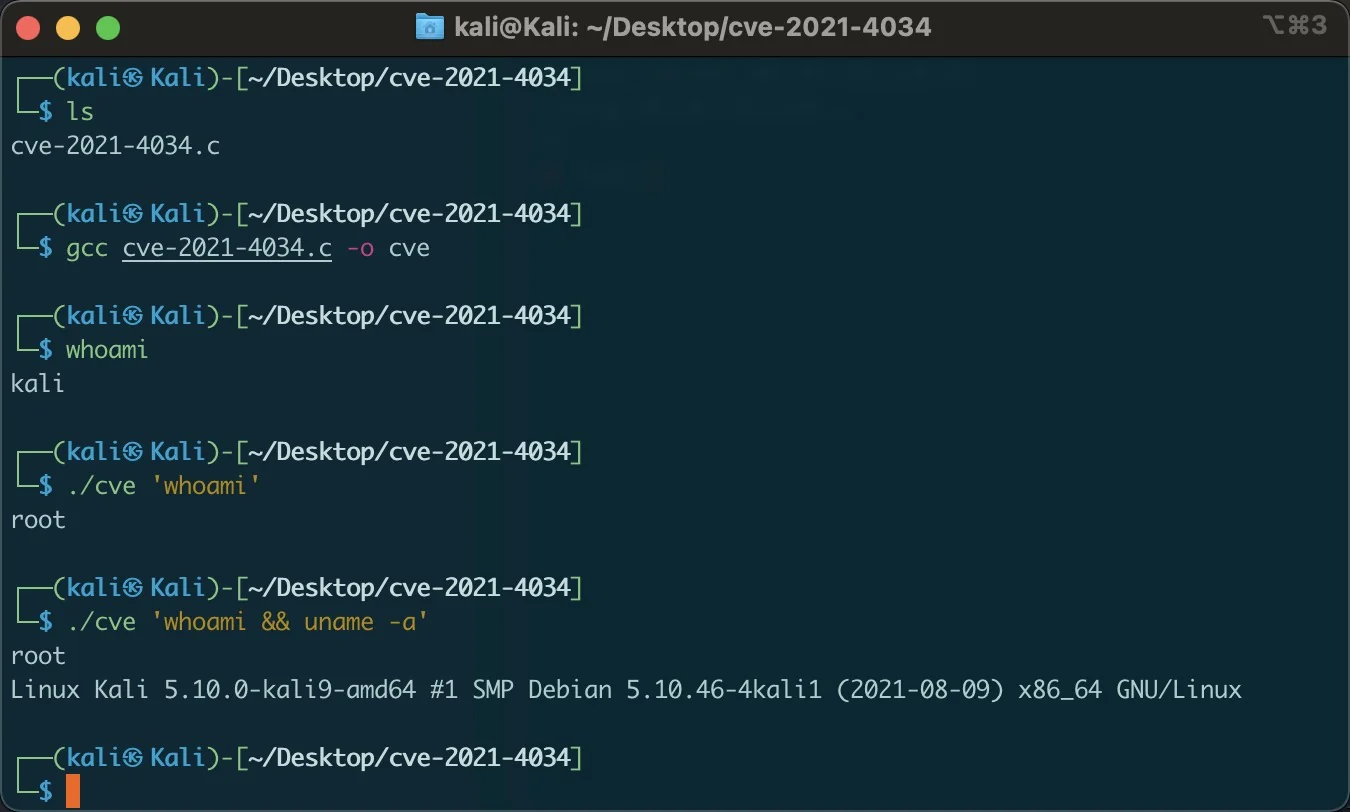 zhzyker/cve-2021-4034
polkit pkexec Local Privilege Vulnerability to Add custom commands
 frichetten/cve-2020-11108-poc
PoCs for CVE-2020-11108; an RCE and priv esc in Pi-hole
 withdk/pulse-secure-vpn-mitm-research
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 al1ex/cve-2021-4034
Local Privilege Escalation in polkit's pkexec (CVE-2021-4034)
 fuzzlove/sparstanboogie
Exploit chain utilizing directory traversal and iOS restore to overwrite protected files.

 hackspeak/cve-2026-60004
Gitea diffpatch RCE (CVE-2026-60004) PoC - repo-write to RCE as Gitea service account
 ozcanpng/cve-2025-57819-freepbx-rce2root
Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.
 sifatnotes/learn-secbyte-cms-cve-shell-to-root-privilege-escalation-ctf-labs
Hands-on cybersecurity and CTF labs covering port reconnaissance, CMS stack discovery, VulnCMS, CVE-2026-58225, shell-to-root paths, Python, sudo,…
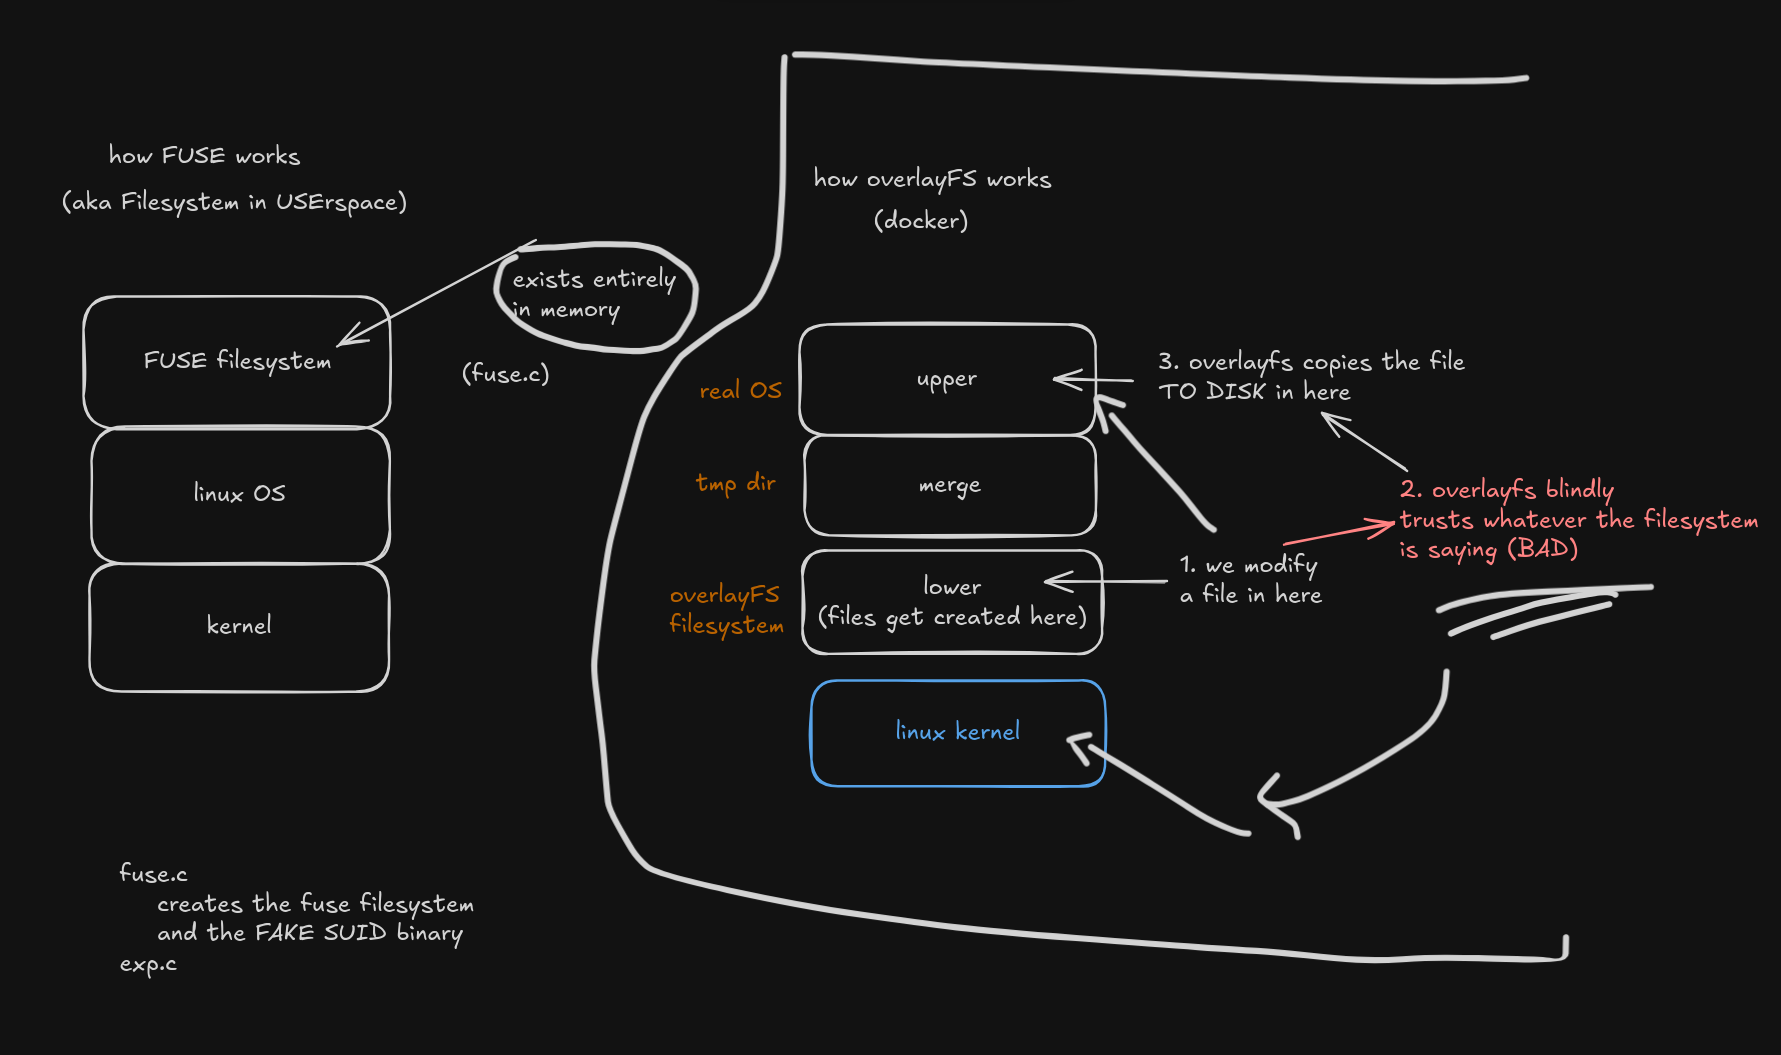 pwncone/cve-2023-0386-overlayfs
Copy fake in-memory files to disk using overlayFS
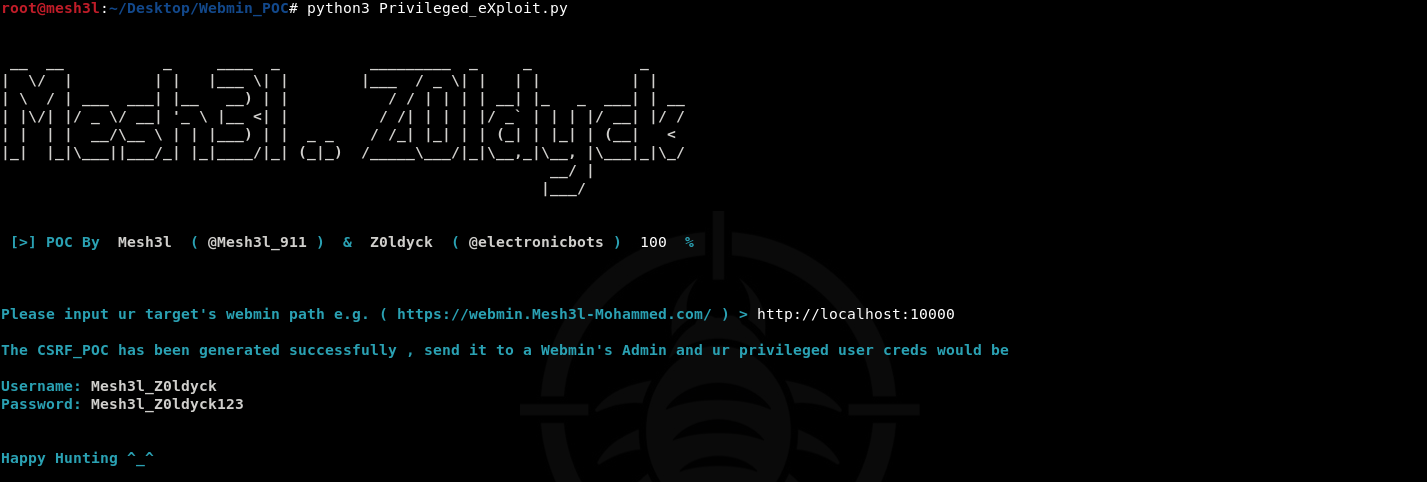 mesh3l911/cve-2021-31762
Exploiting a Cross-site request forgery (CSRF) attack to creat a new privileged user through the Webmin's add users feature