Windows_LPE_AFD_CVE-2023-21768

Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…

Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…

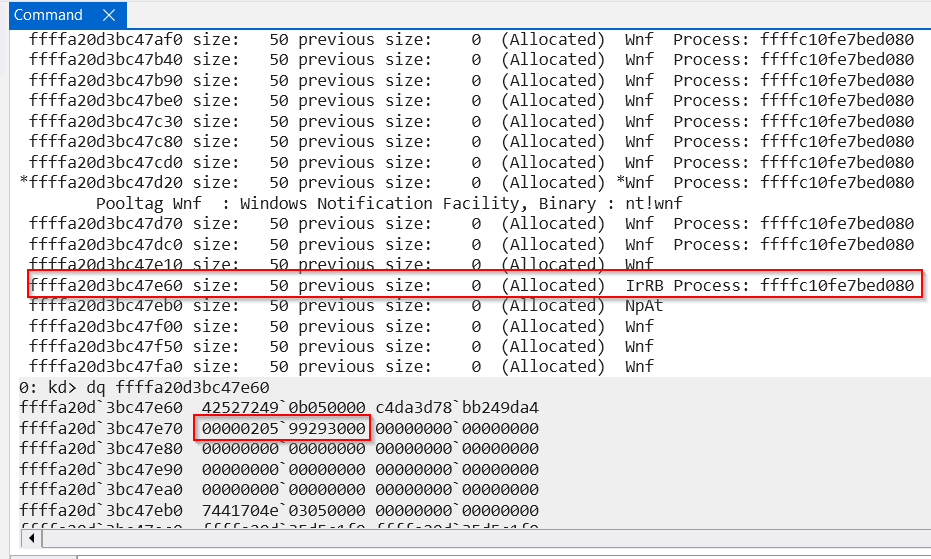
POC exploit for CVE-2025-21333 heap-based buffer overflow. It leverages WNF state data and I/O ring IOP_MC_BUFFER_ENTRY

Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…

Public proof-of-concept for CVE-2021-31727 and CVE-2021-31728 demonstrating unrestricted disk read/write and arbitrary ring 0 code execution in…

r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems

Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…

Proof-of-concept exploit for CVE-2022-23222, a Linux kernel local privilege escalation via eBPF. Demonstrates ring buffer manipulation and map…

Crash PoC for CVE-2015-3636, a Linux kernel ping socket vulnerability, demonstrating a denial-of-service condition.

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…

Proof-of-concept exploit for CVE-2023-21768, a Windows Ancillary Function Driver (AFD.sys) arbitrary kernel write vulnerability enabling local…

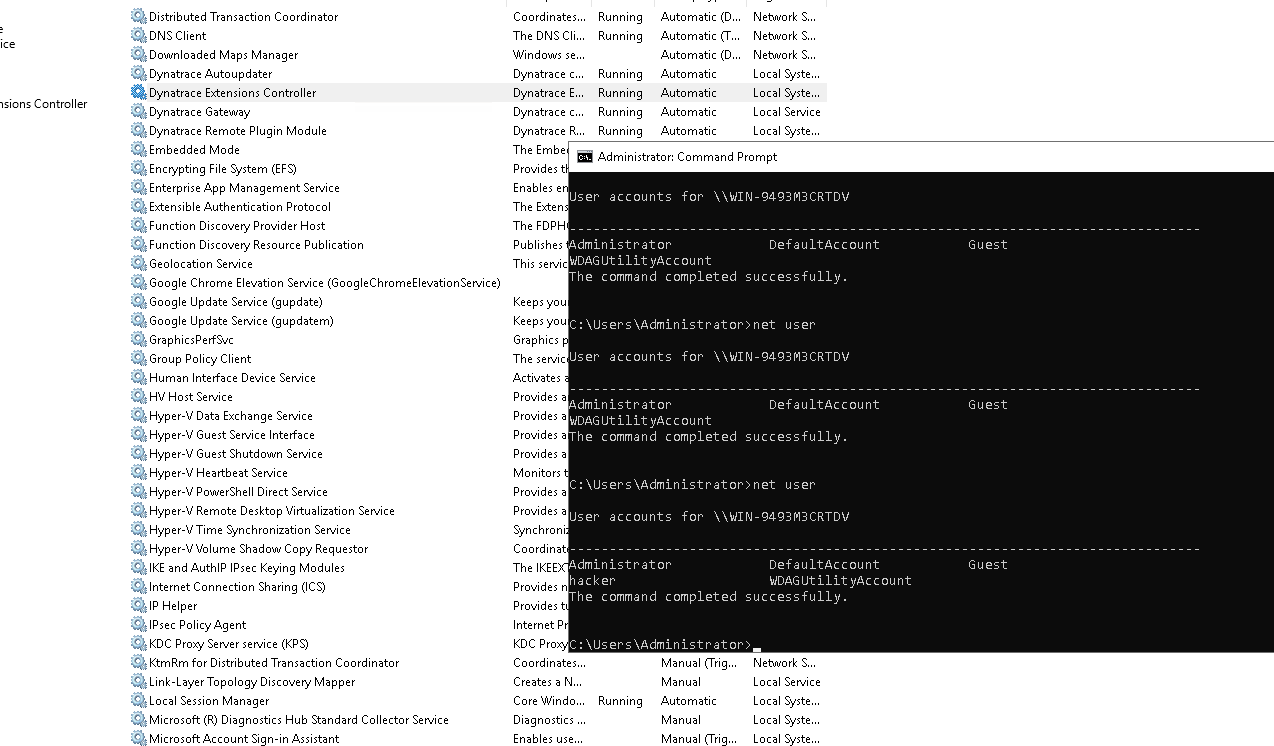
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address

Wing FTP Server 6.2.3 - Privilege Escalation

🔐 Estudo de caso completo do CVE-2026-31431 (CopyFail) — vulnerabilidade crítica de escalada de privilégio no kernel Linux. Inclui análise técnica,…

Wing FTP Server 6.2.5 - Privilege Escalation

Cronos is Windows 10/11 x64 ring 0 rootkit. Cronos is able to hide processes, protect and elevate them with token manipulation.

Now You See Me, Now You Don't

Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…