

aced
 garrettfoster13/aced
Parses and resolves a single Active Directory principal's DACL to identify inbound access privileges, resolve SIDs, and log LDAP attributes for…
information-gatheringpenetration-testingprivilege-escalation+1
203
garrettfoster13/acedParses and resolves a single Active Directory principal's DACL to identify inbound access privileges, resolve SIDs, and log LDAP attributes for…
 qazeer/farsightad
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 twelvesec/rootend
A *nix Enumerator & Auto Privilege Escalation tool.
 deadjakk/patch-checker
Web-based check for Windows privesc vulnerabilities
 ssteelfactor-oss/kestrel
Low-observability Active Directory security enumeration tool using native ADSI/COM interfaces. Enumerates ACLs, delegation, trusts, ADCS, Kerberoast…
 alperenugurlu/ad_enumeration_hunt
PowerShell toolkit for Active Directory penetration testing, featuring domain/user/group enumeration, trust relationship analysis, RDP configuration,…
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 lsecqt/find-adminaccess
This C# tool sprays for admin access over the entire domain
 shellster/ldapper
LDAP Querying without the Suck
 mitchmoser/lacheck
Multithreaded C# .NET assembly for enumerating local administrative privileges across Windows hosts via SMB, WMI, and WinRM, with BloodHound…
 puckblush/tofu
Windows offline filesystem hacking tool for Linux
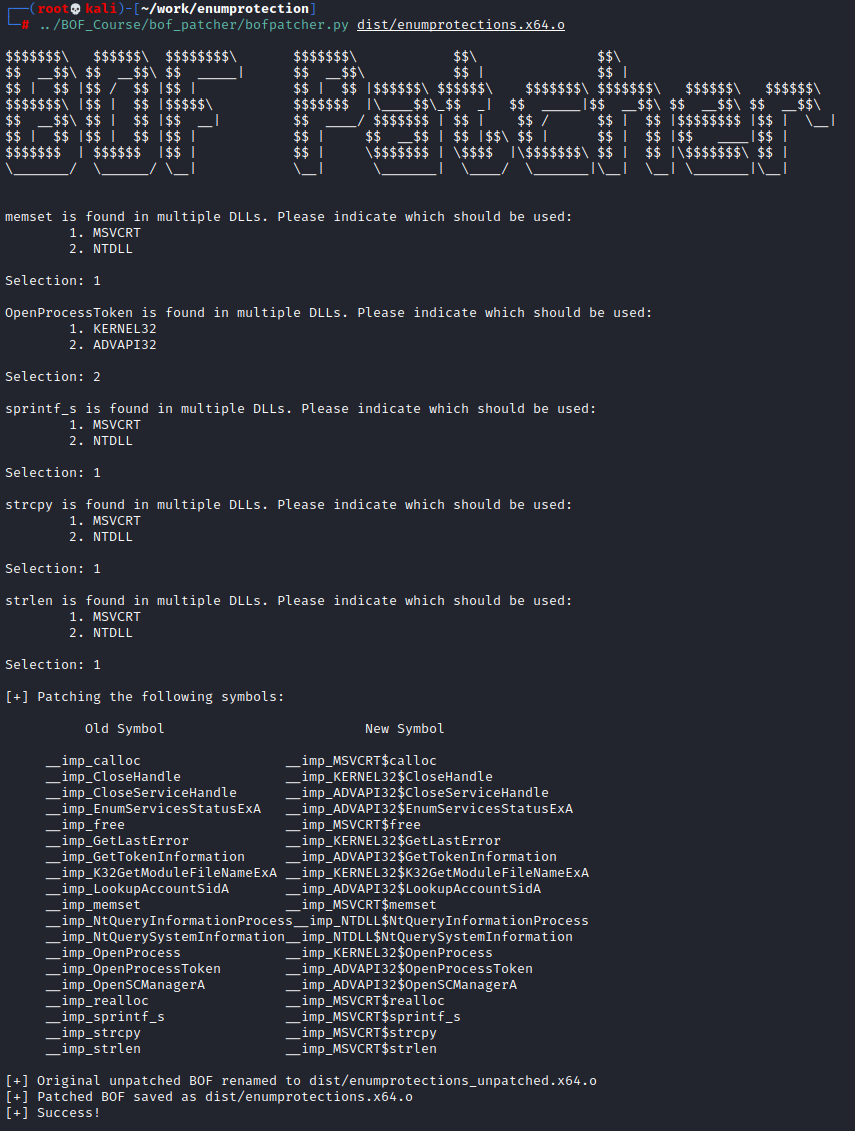 octoberfest7/enumprotections_bof
A BOF to enumerate system process, their protection levels, and more.
 xforcered/scmkit
Source Code Management Attack Toolkit
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
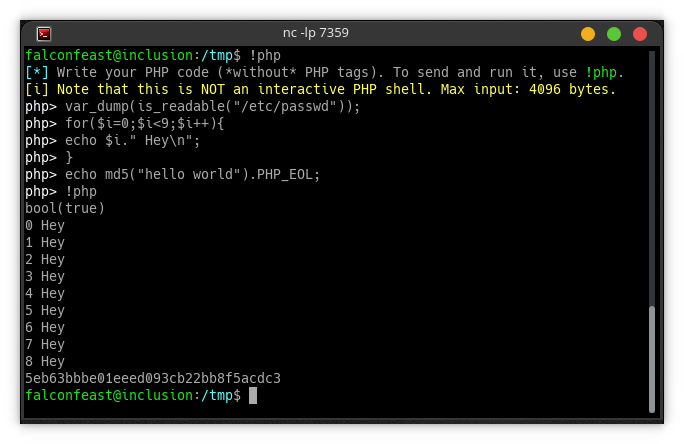 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 abstractclass/cloudprivs
Determine privileges from cloud credentials via brute-force testing.