
ad-autopwn
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
command-and-controlexploitationlateral-movement+7
37
jonaslejon/ad-autopwnAutomated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 msm8916-mainline/cve-2022-22063
Security issue in the hypervisor firmware of some older Qualcomm chipsets
 hika-sec/terminator_killer
Kernel-mode process killer exploiting CVE-2026-0828 (BYOVD) to terminate protected processes via a vulnerable signed driver, bypassing PPL and…
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 r3fr4kt/popcorn-tjnull-oscp-
Popcorn HTB write-up covering advanced directory fuzzing, file upload bypass via magic numbers/extension spoofing using Burp Suite, and privilege…
 rootsecnz/htb-ctf-walkthroughs
Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
 ghostpack/seatbelt
Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…
 k8gege/ladon
Ladon大型内网渗透扫描器,PowerShell、Cobalt Strike插件、内存加载、无文件扫描。含端口扫描、服务识别、网络资产探测、密码审计、高危漏洞检测、漏洞利用、密码读取以及一键GetShell,支持批量A段/B段/C段以及跨网段扫描,支持URL、主机、域名列表扫描等。网络资产探测32…
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 intelisecurelabs/linux_exploit_suggester
Linux Exploit Suggester; based on operating system release number
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
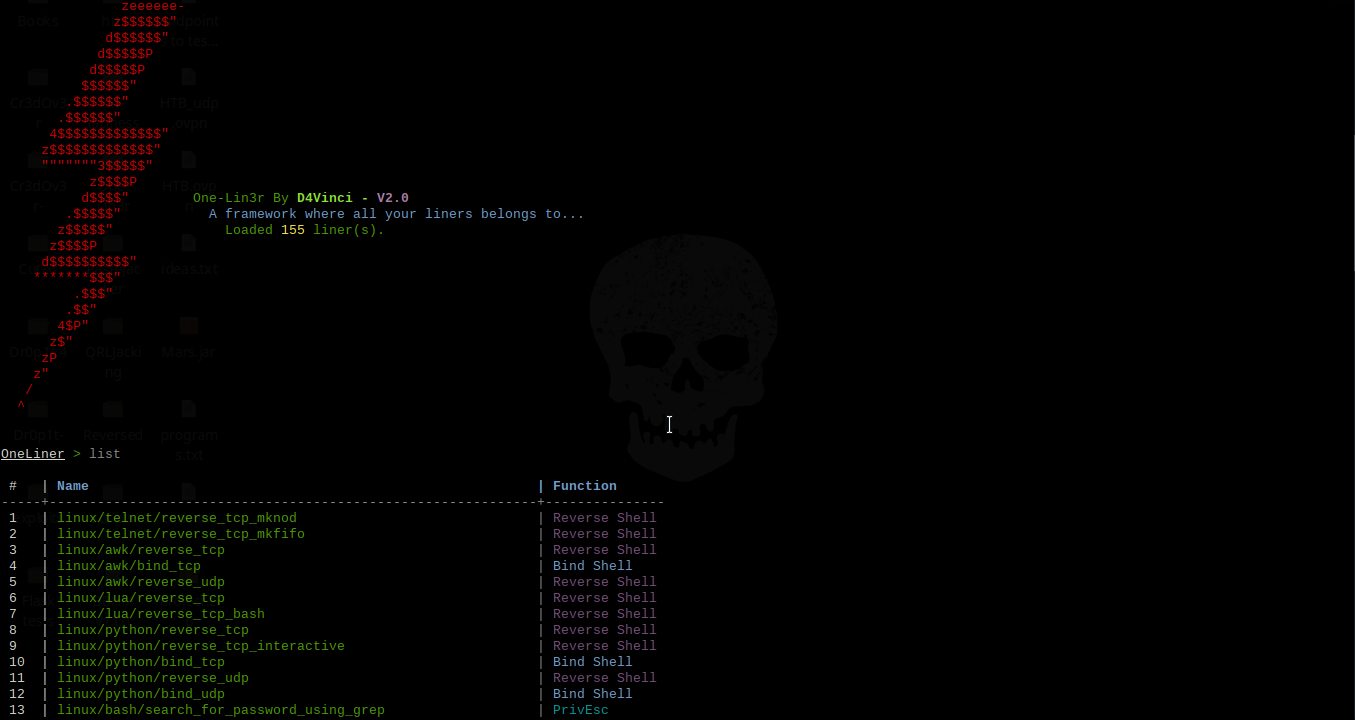 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
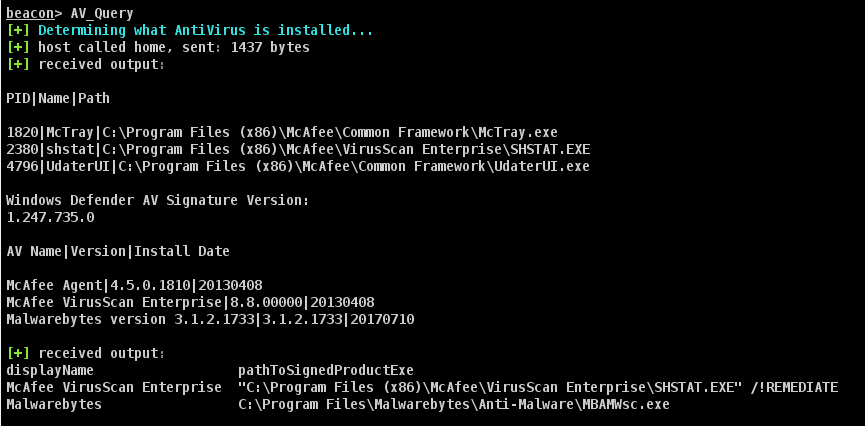 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds