

CVE-2022-0847-dirty-pipe-kernel-checker
 mrp1xel/cve-2022-0847-dirty-pipe-kernel-checker
Python script to check if your kernel is vulnerable to Dirty pipe CVE-2022-0847
exploitationprivilege-escalationscripting-automation+1
3
mrp1xel/cve-2022-0847-dirty-pipe-kernel-checkerPython script to check if your kernel is vulnerable to Dirty pipe CVE-2022-0847
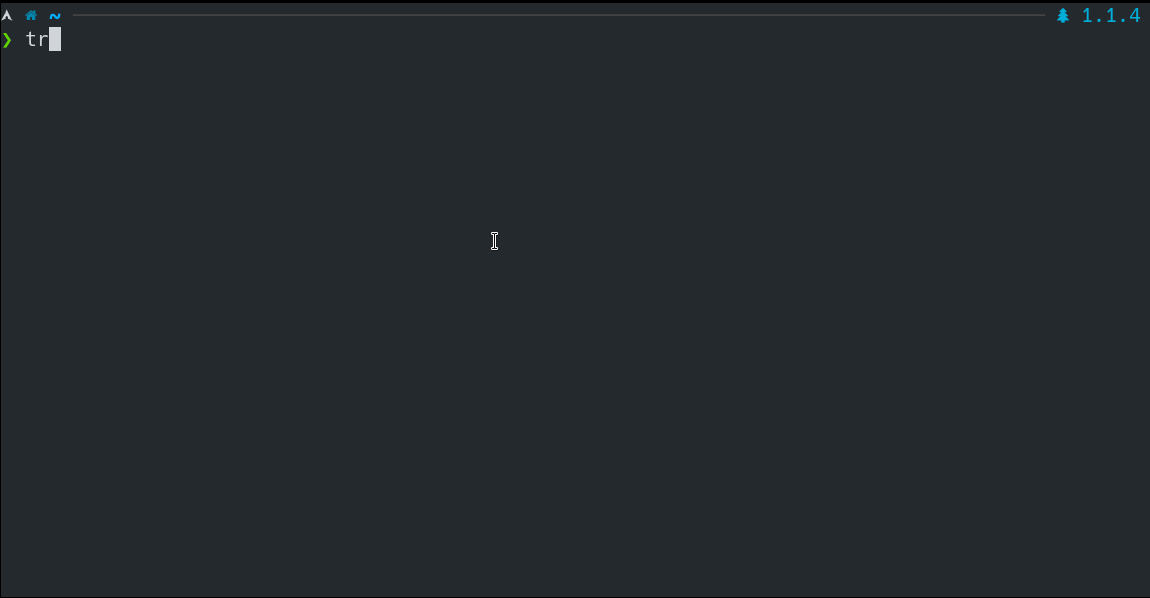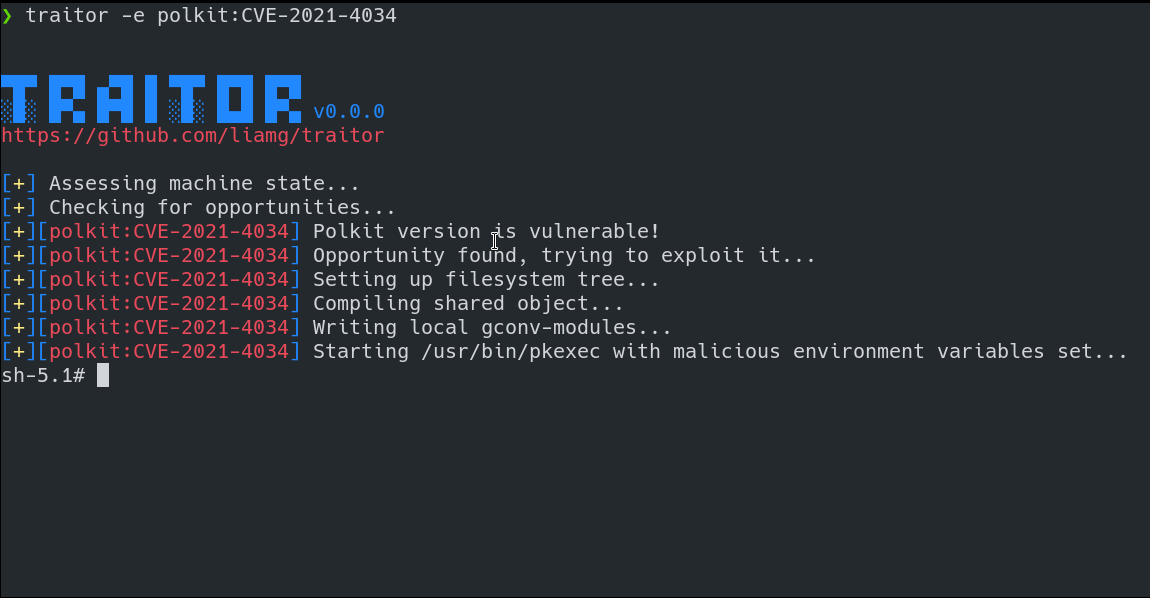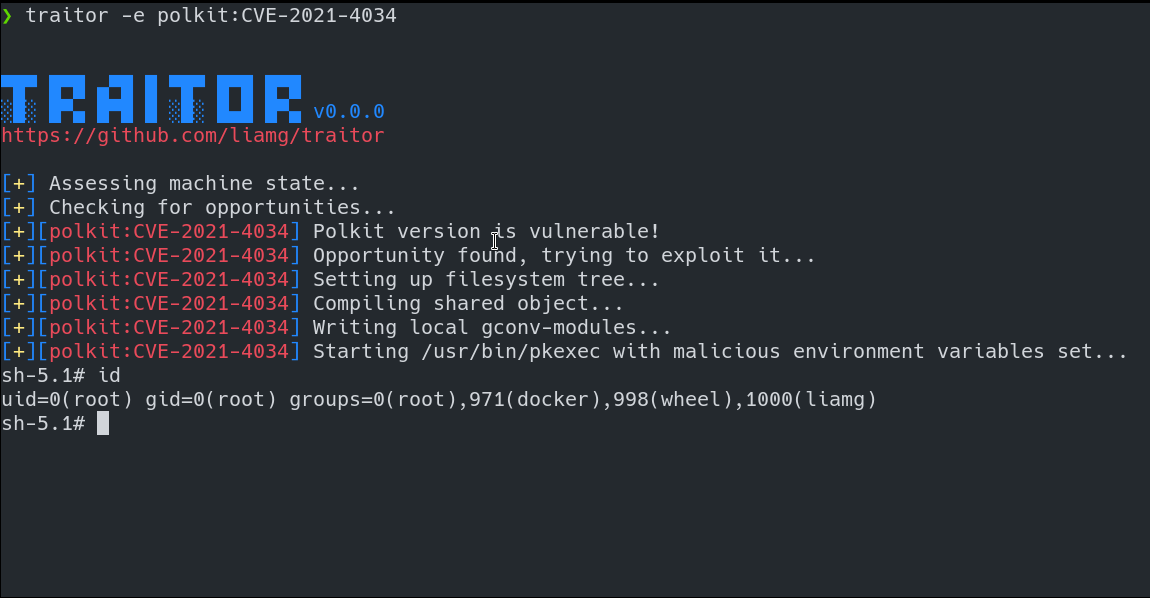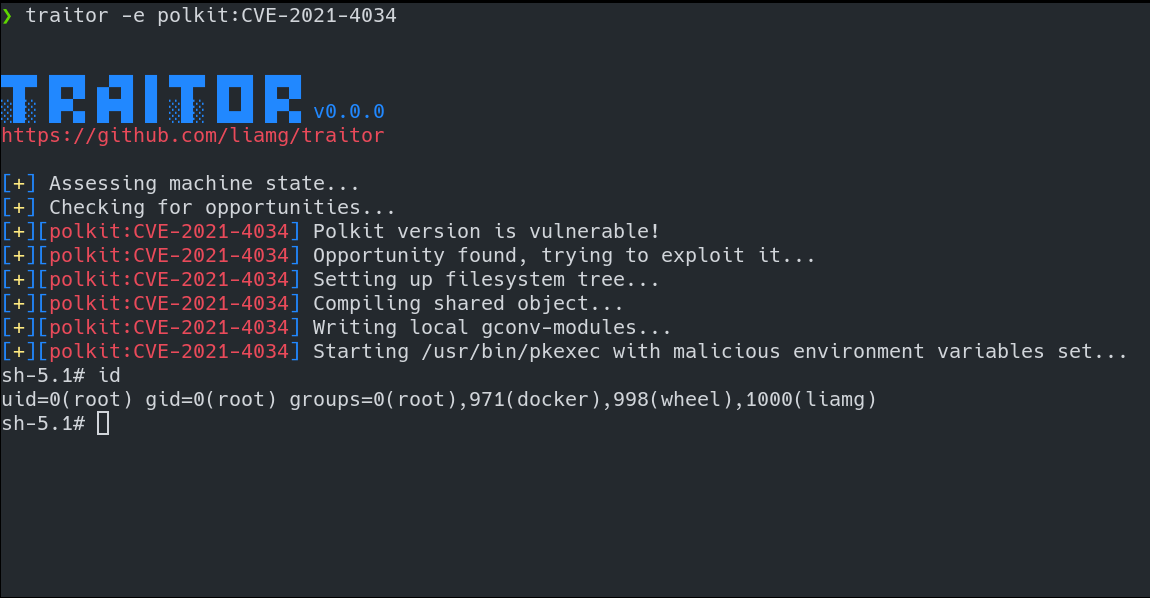 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 scumjr/dirtycow-vdso
PoC for Dirty COW (CVE-2016-5195)
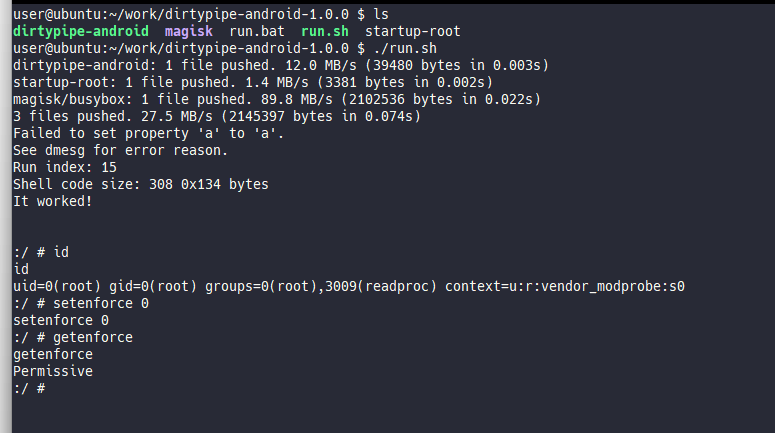 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 bindecy/hugedirtycowpoc
A POC for the Huge Dirty Cow vulnerability (CVE-2017-1000405)
 zhuowei/macdirtycowdemo
Get root on macOS 13.0.1 with CVE-2022-46689 (macOS equivalent of the Dirty Cow bug), using the testcase extracted from Apple's XNU source.
 knqyf263/cve-2022-0847
Go-based proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) demonstrating arbitrary file overwrite via uninitialized pipe buffers, intended for…
 greenhandatsjtu/cve-2022-0847-container-escape
CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸
 sarabpal-dev/cheese-cake
A proof-of-concept for CVE-2025-21479, chained with a Dirty Pagetable technique.
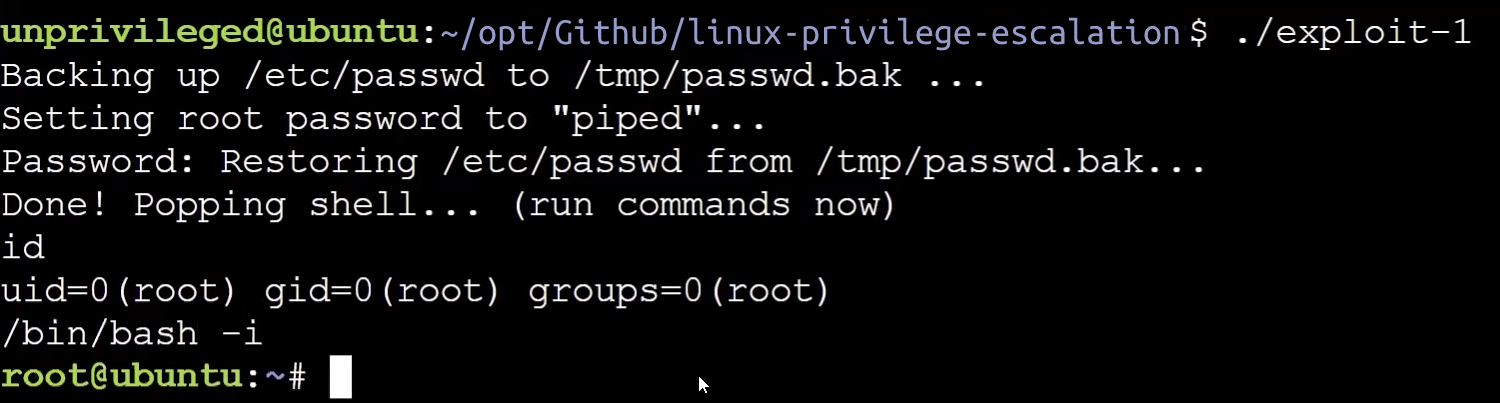 rexpository/linux-privilege-escalation
Scripted Linux Privilege Escalation for the CVE-2022-0847 "Dirty Pipe" vulnerability
 kuzeyardabulut/cve-2025-8045
Dirty Pagetable Exploit for CVE-2025-8045
 sideeffect42/dirtycowtester
Dirty COW (CVE-2016-5195) vulnerability testing utility for Linux-based systems.
 oleg-fiksel/ansible_cve-2016-5195_check
Ansible playbook to test systems for the Dirty COW privilege escalation vulnerability (CVE-2016-5195) with automated local exploitation checks.
 nihan-silent-reign/cve-2026-43284-dirty-frag-
Technical analysis of CVE-2026-43284 (Dirty Frag), a Linux kernel xfrm ESP local privilege escalation enabling page-cache writes to read-only files…
 vudangducminh/cve-2016-5195
Proof-of-concept exploit for CVE-2016-5195 (Dirty COW), a Linux kernel race condition enabling local privilege escalation to root.
 kianabin/cve-2022-0847-container-escape
CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸
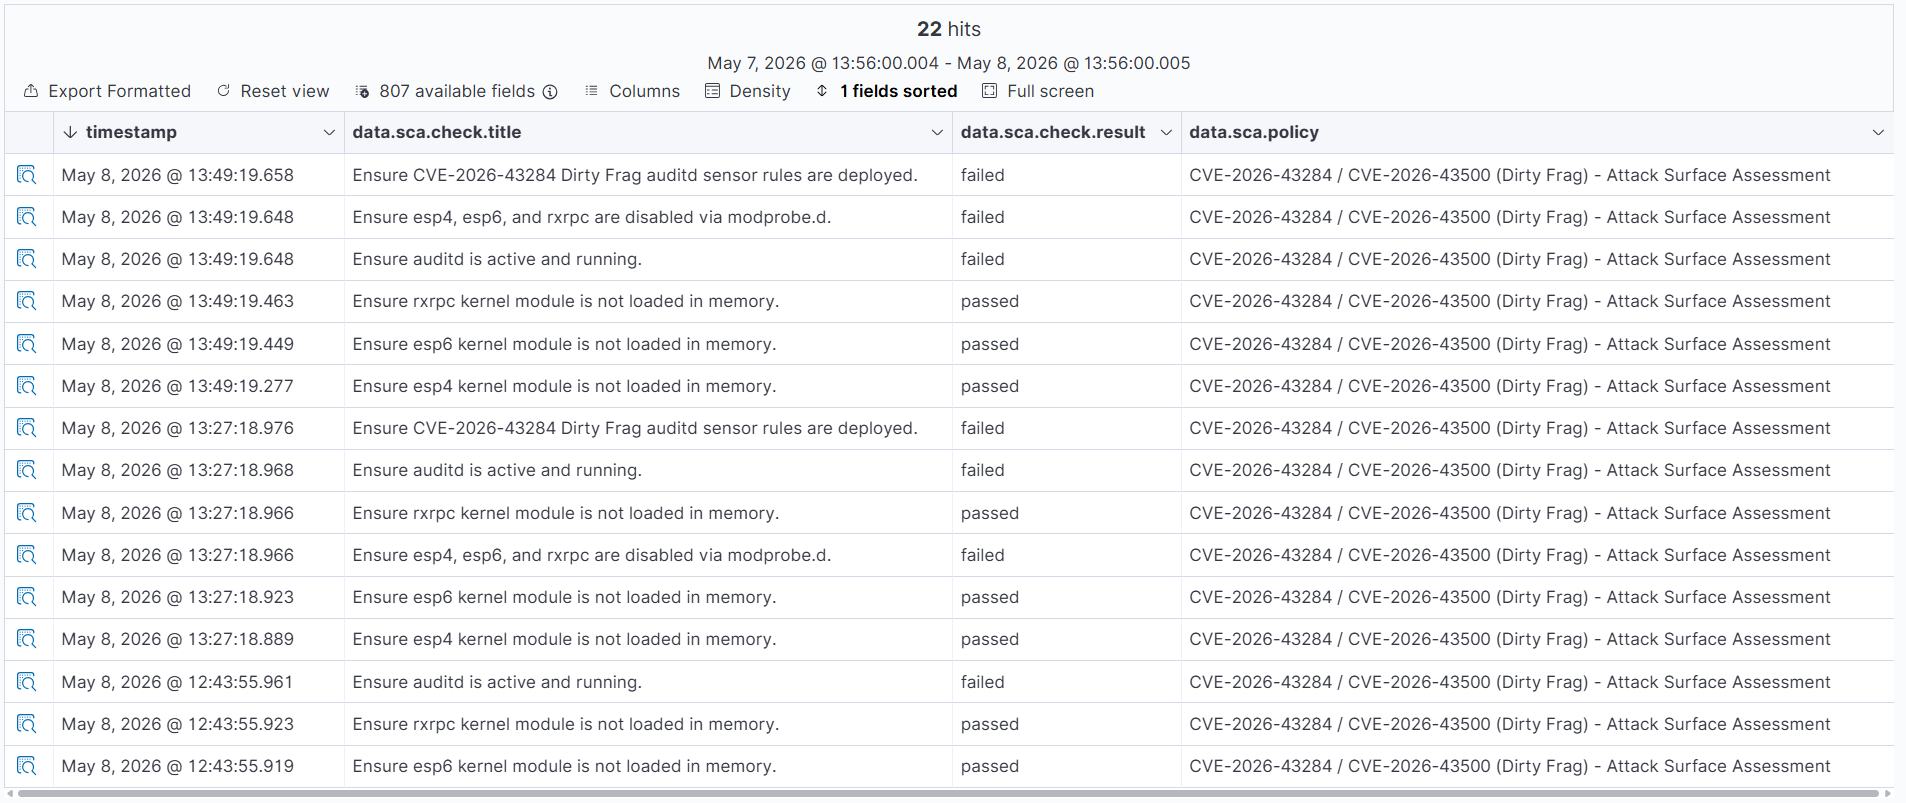 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write
 sa-infinity8888/dirty-pipe-cve-2022-0847
CVE-2022-0847 (Dirty Pipe) is an arbitrary file overwrite vulnerability that allows escalation of privileges by modifying or overwriting arbitrary…