

CVE-2025-1974
 boianeduard/cve-2025-1974
ingress-nginx admission controller RCE escalation PoC
cloud-securitycontainer-securityeducation+8
boianeduard/cve-2025-1974ingress-nginx admission controller RCE escalation PoC
 fahmifj/docker-breakout-runc
Modified version of CVE-2019-5736-PoC by Frichetten
 kondordevsecuritycorp/cve-2025-60709
Windows CLFS LPE exploit PoC for security research
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 ishankaru/cve-2026-23111-nftables-lab
Exposure checker and safe disposable-VM lab for CVE-2026-23111 (Linux nf_tables use-after-free local privilege escalation). Defensive: detection,…
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 chenaotian/cve-2022-0847
Proof-of-concept exploit and detailed analysis of CVE-2022-0847 (Dirty Pipe) Linux kernel privilege escalation vulnerability, including Docker…
 horkimhab/cve-2015-5287
Local privilege escalation exploit for CVE-2015-5287 targeting RHEL 7.0/7.1 via abrt/sosreport, intended for authorized security testing and…
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 0x7183/cve-2021-3156
Sudo Heap Overflow Baron Samedit
 chenaotian/cve-2021-4034
Detailed write-up and proof-of-concept exploit for CVE-2021-4034 (PolKit pkexec local privilege escalation), including a Docker lab environment for…
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 ccchme/cve-2018-1058
Reproducible Docker-based demonstration of CVE-2018-1058 PostgreSQL privilege escalation via uncontrolled search path, with vulnerable and patched…
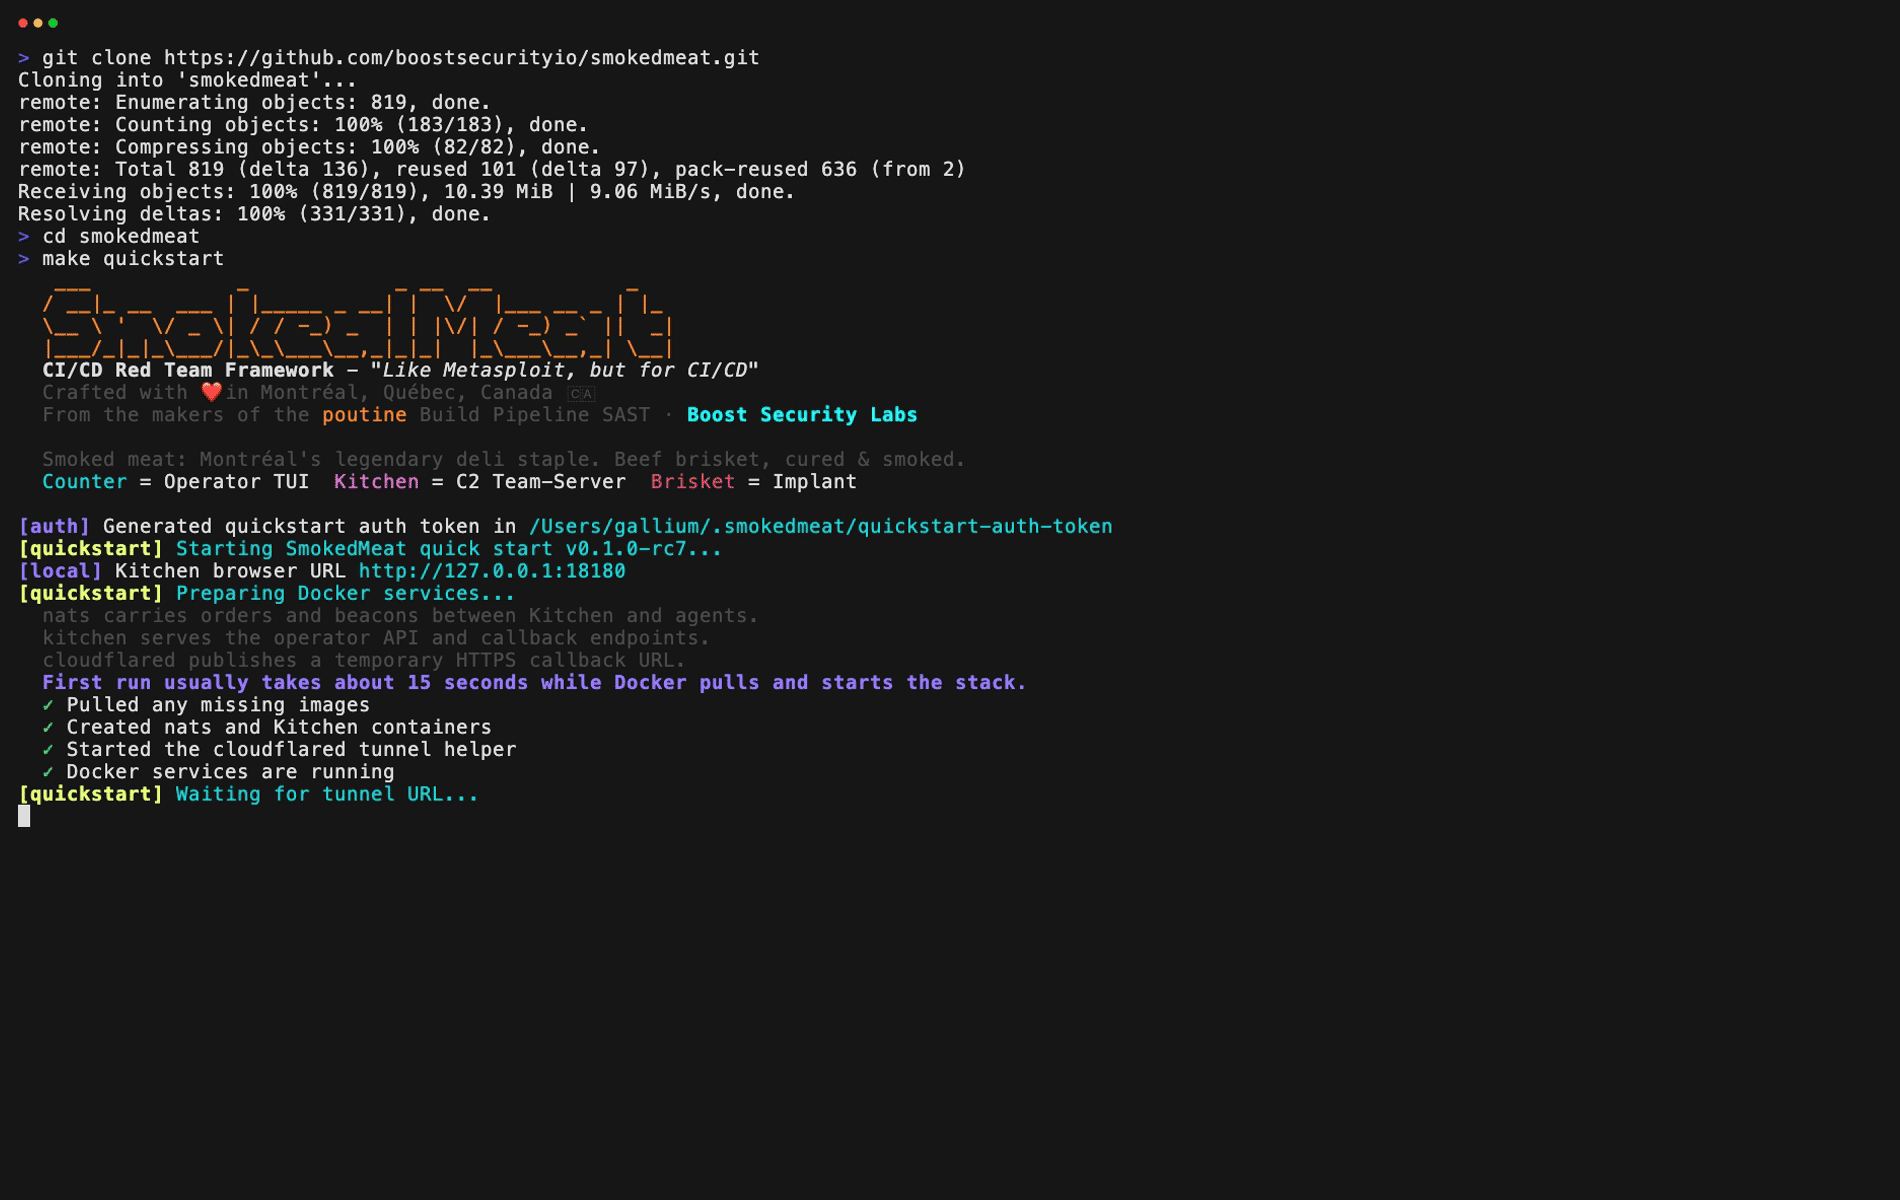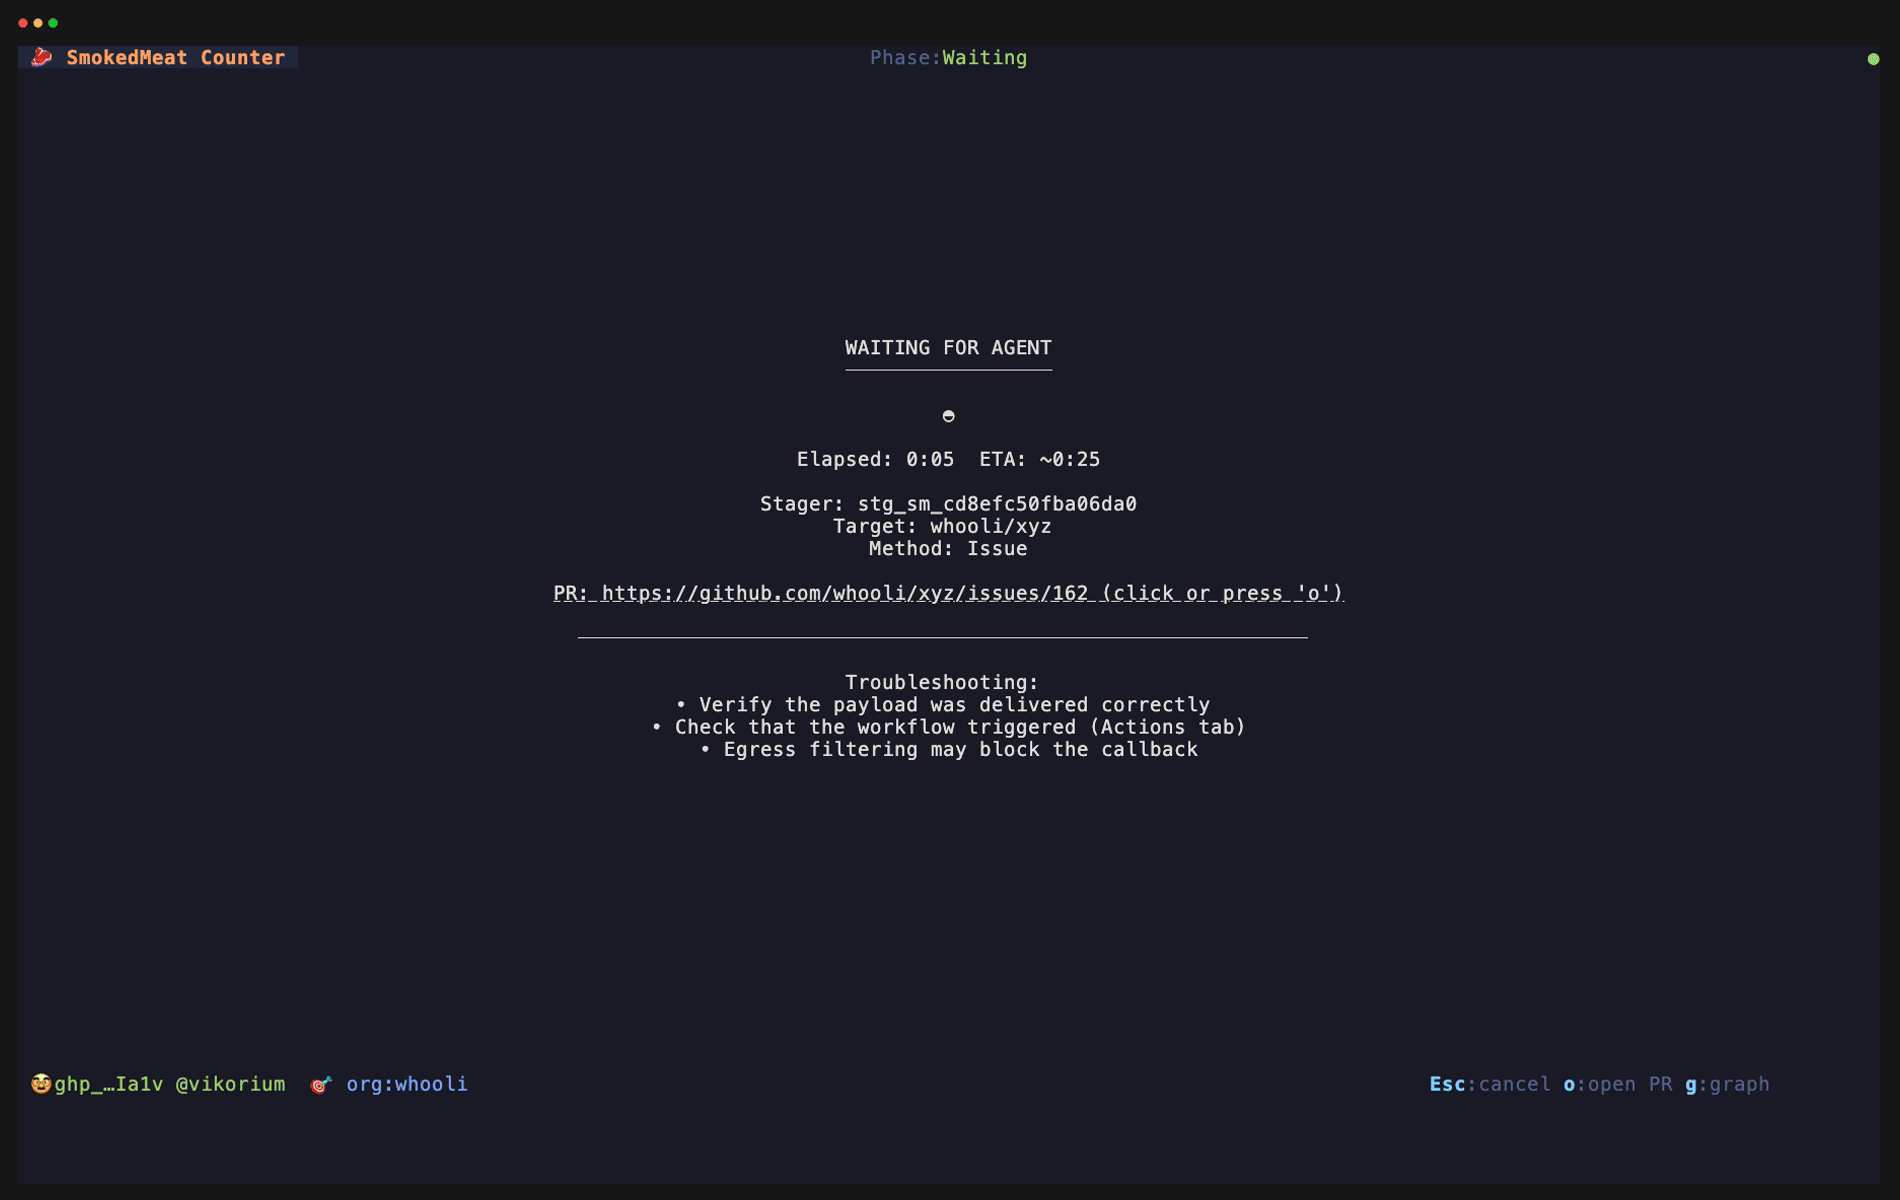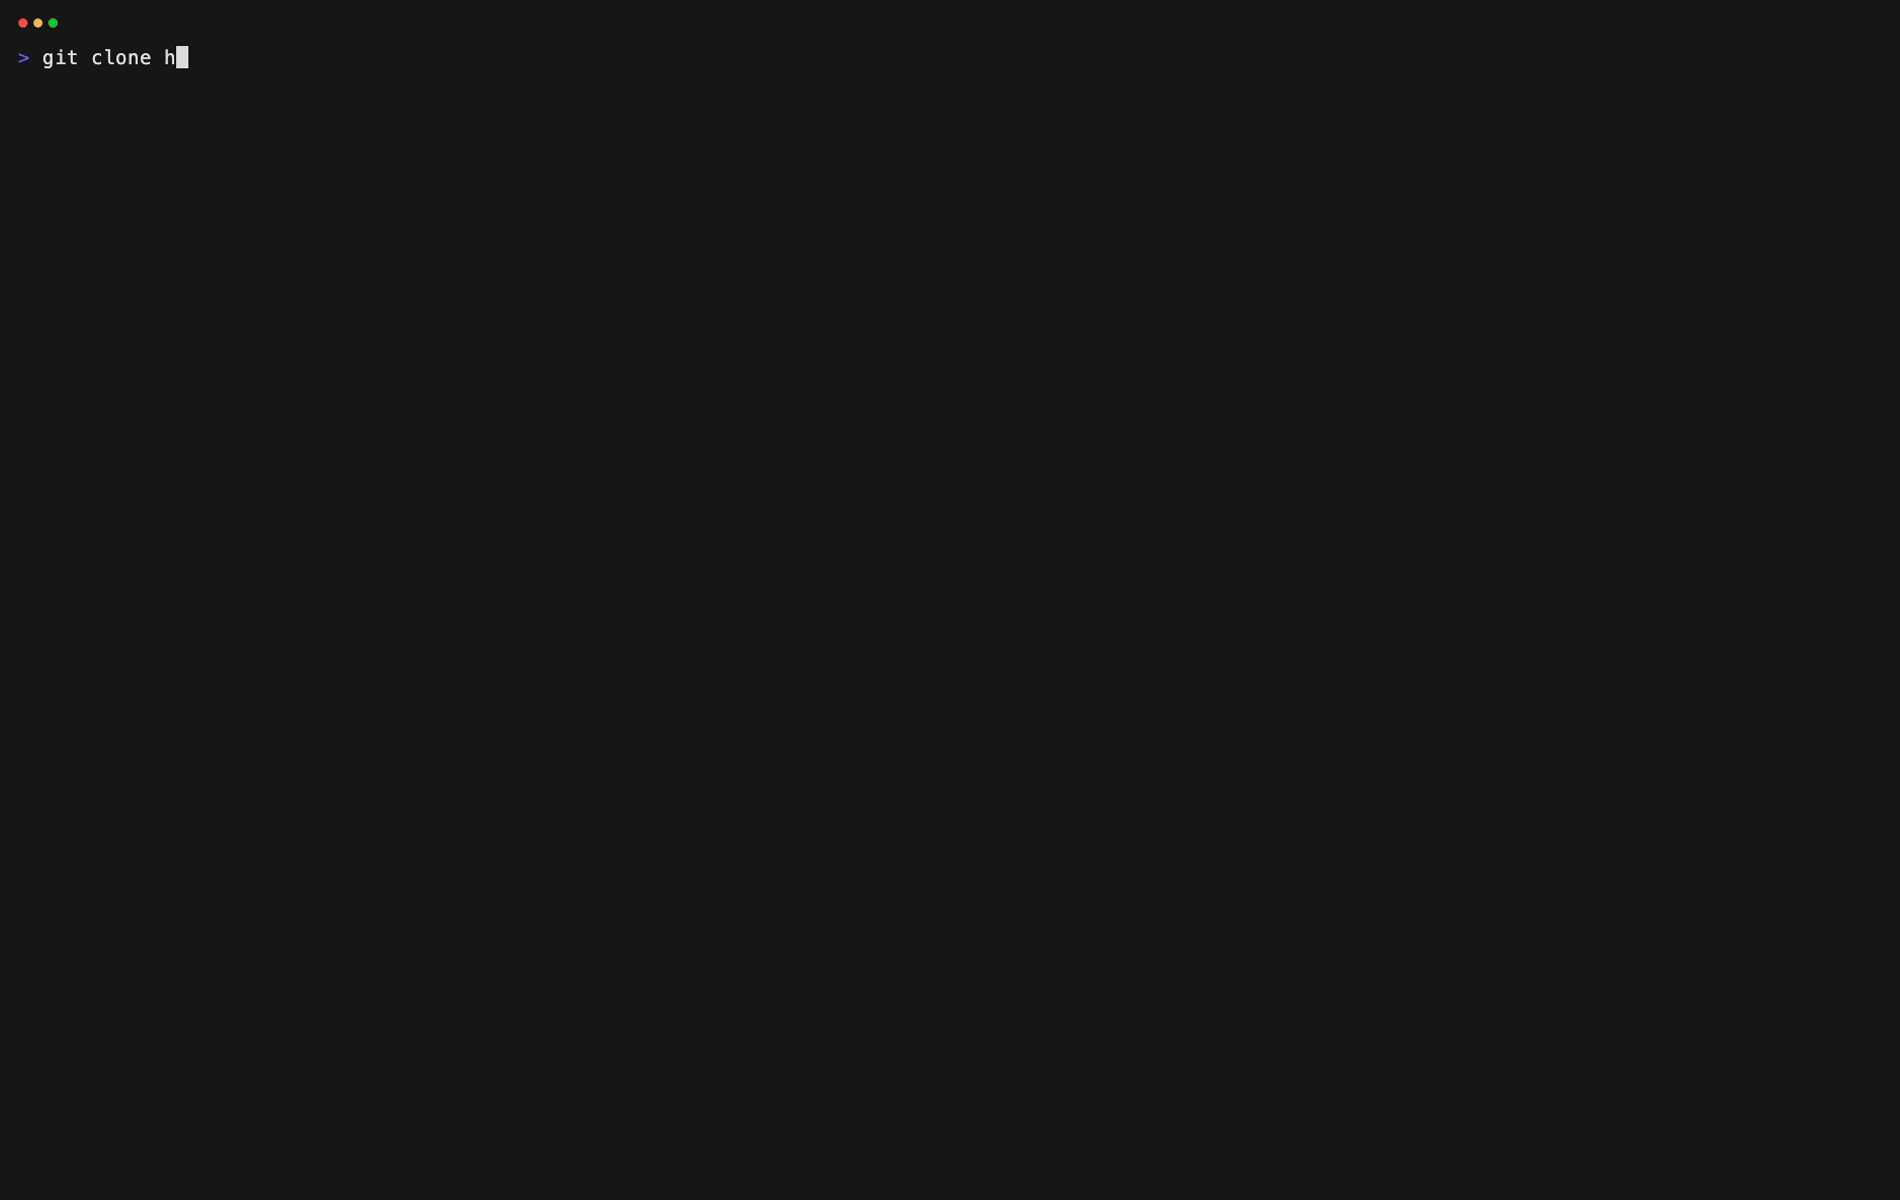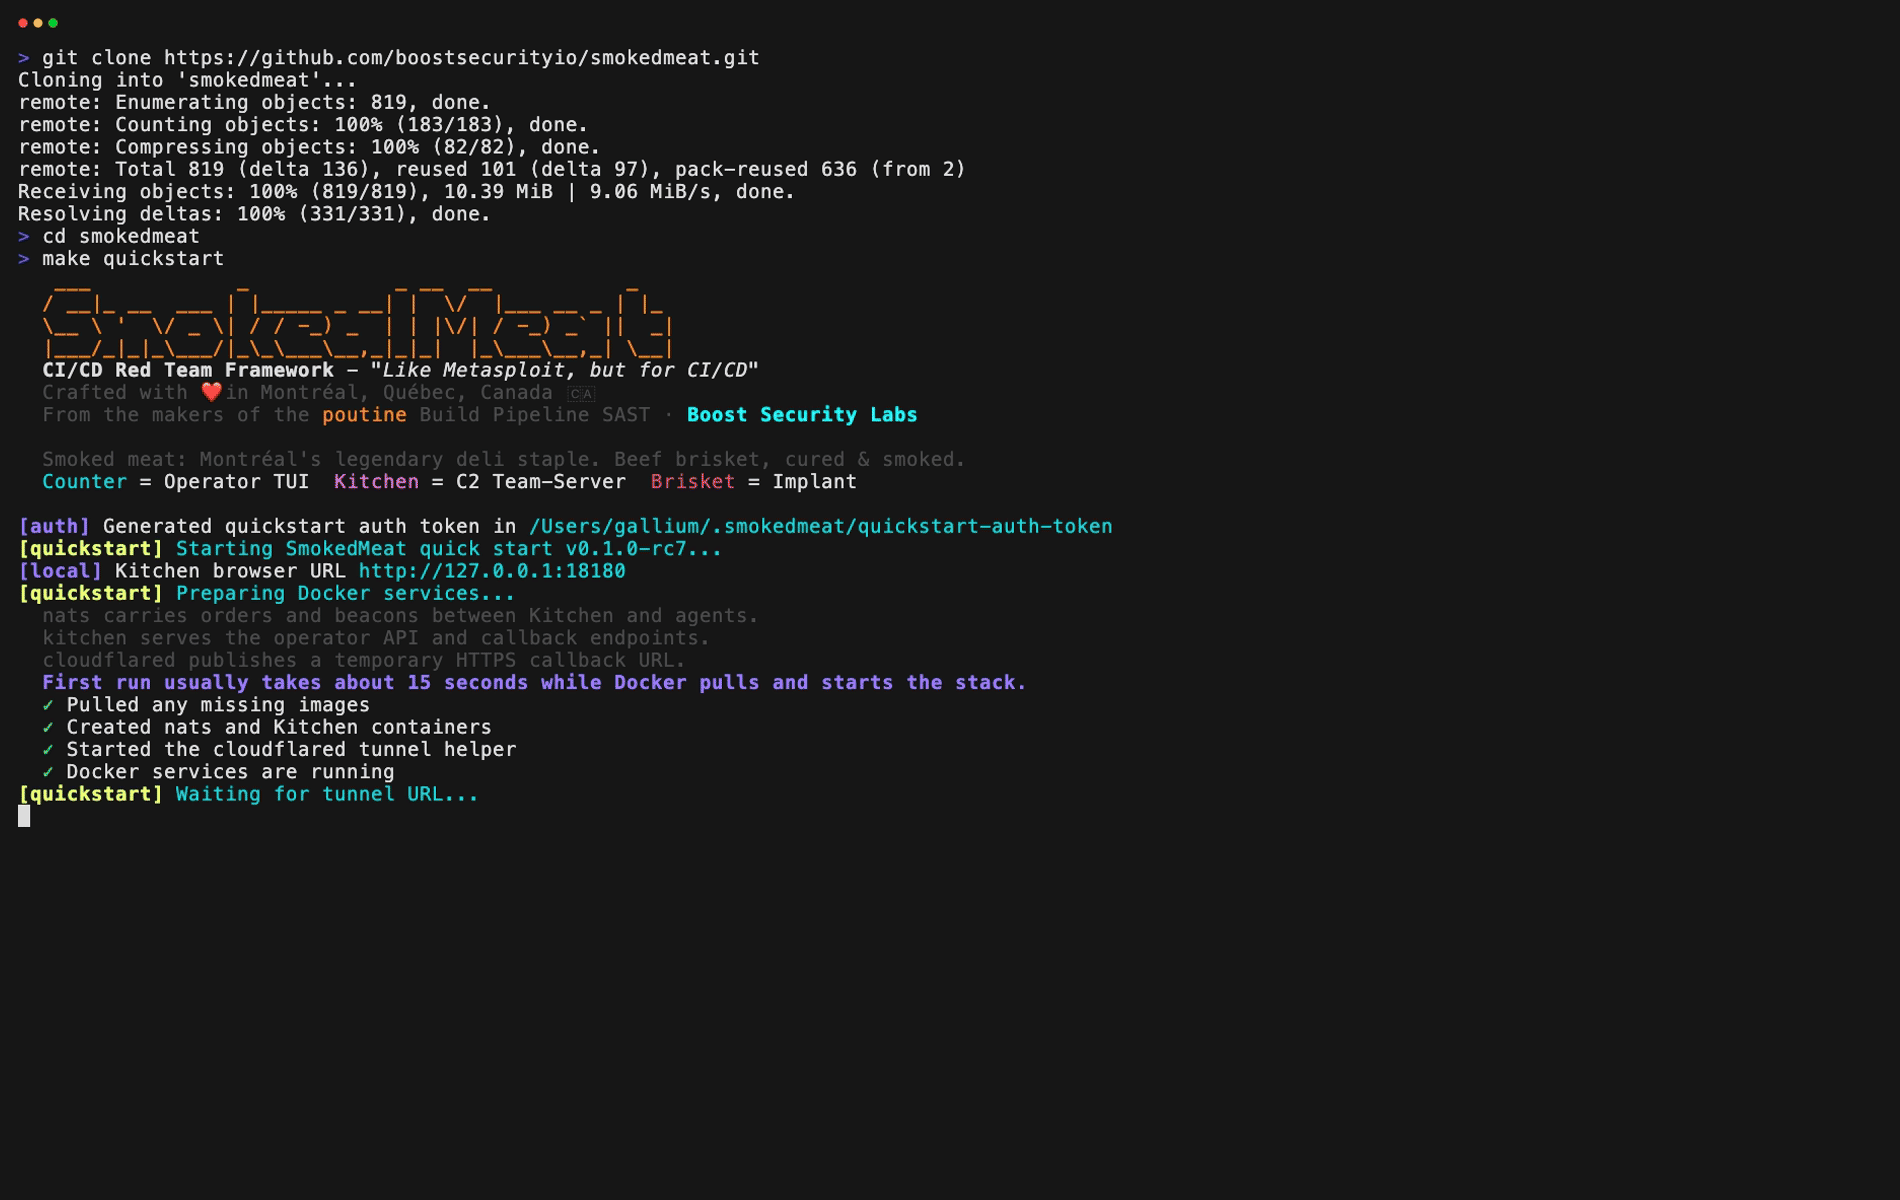 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 vrtlbob/linux-kernel-vulnerabilities-cve-2026-23111
High Severity LPE vulnerability in Linux Kernel, with a CVS score of 7.8. An inverted check from user enables a process inside the container to break…