

PowerLurk
 sw4mpf0x/powerlurk
Malicious WMI Events using PowerShell
information-gatheringpayload-generationpenetration-testing+5
398
sw4mpf0x/powerlurkMalicious WMI Events using PowerShell
 tobor88/powershell-red-team
Collection of PowerShell functions a Red Teamer may use in an engagement
 rhinosecuritylabs/gcpbucketbrute
A script to enumerate Google Storage buckets, determine what access you have to them, and determine if they can be privilege escalated.
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
 t3l3machus/eviltree
A python3 remake of the classic "tree" command with the additional feature of searching for user provided keywords/regex in files, highlighting those…
 punk-security/smbeagle
SMBeagle - Fileshare auditing tool.
 illusionofchaos/ios-gamed-0day
iOS gamed exploit (fixed in 15.0.2)
 bytewreck/dumpguard
Proof-of-Concept tool for extracting credential material from protected sessions on modern Windows systems.
 omergunal/hackerbot
Chat with hacker assistant
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 nullarray/mida-multitool
Bash script purposed for system enumeration, vulnerability identification and privilege escalation.
 redsiege/edd
.NET-based Active Directory enumeration tool inspired by PowerView. Enumerates domains, users, computers, groups, shares, and sessions. Supports LDAP…
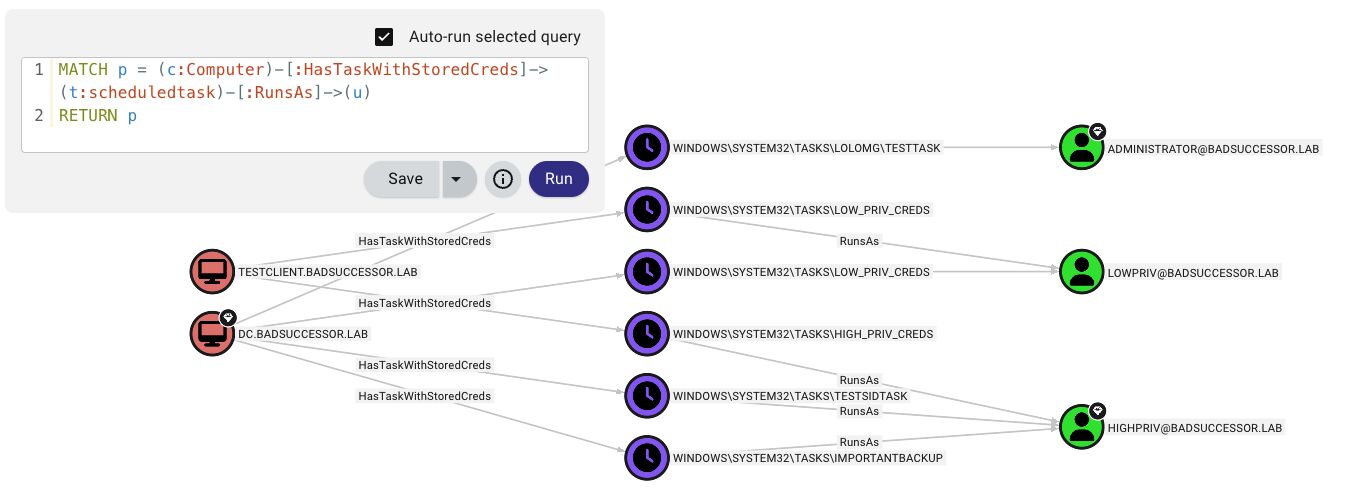 1r0bit/taskhound
Tool to enumerate privileged Scheduled Tasks on Remote Systems
 skiller9090/lucifer
A Powerful Penetration Tool For Automating Penetration Tasks Such As Local Privilege Escalation, Enumeration, Exfiltration and More... Use Or Build…
 chocapikk/cve-2026-21858
n8n Ni8mare - Unauthenticated Arbitrary File Read to RCE Chain (CVSS 10.0)
 improsec/improhound
Identify the attack paths in BloodHound breaking your AD tiering
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…