
noPac
 cube0x0/nopac
CVE-2021-42287/CVE-2021-42278 Scanner & Exploiter.
authentication-authorizationexploitationpenetration-testing+2
cube0x0/nopacCVE-2021-42287/CVE-2021-42278 Scanner & Exploiter.
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
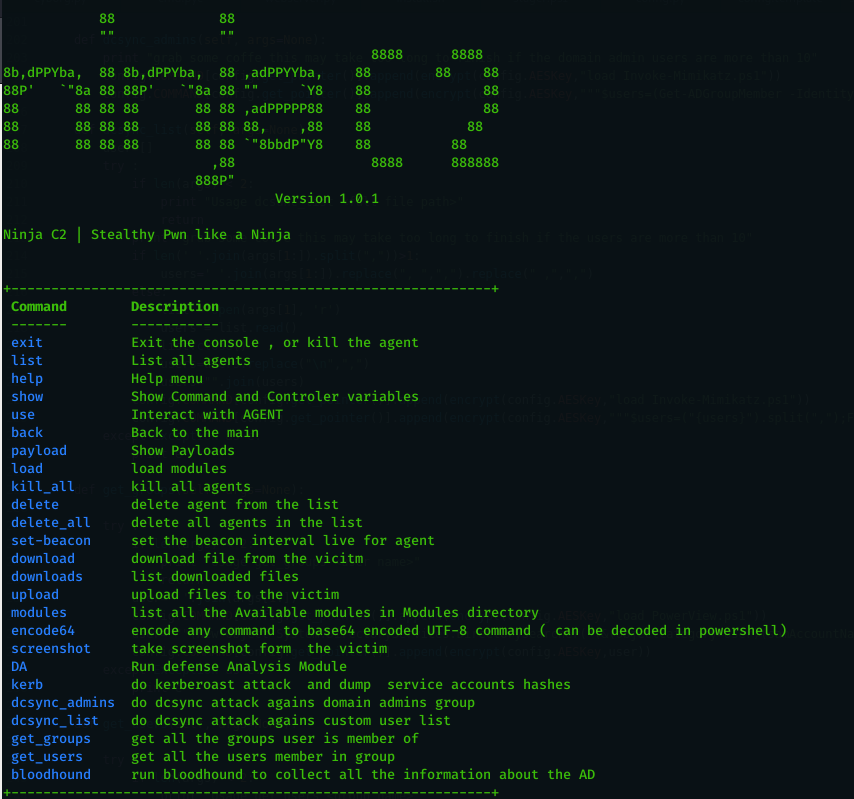 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 dev-2null/adcollector
A lightweight tool to quickly extract valuable information from the Active Directory environment for both attacking and defending.
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data
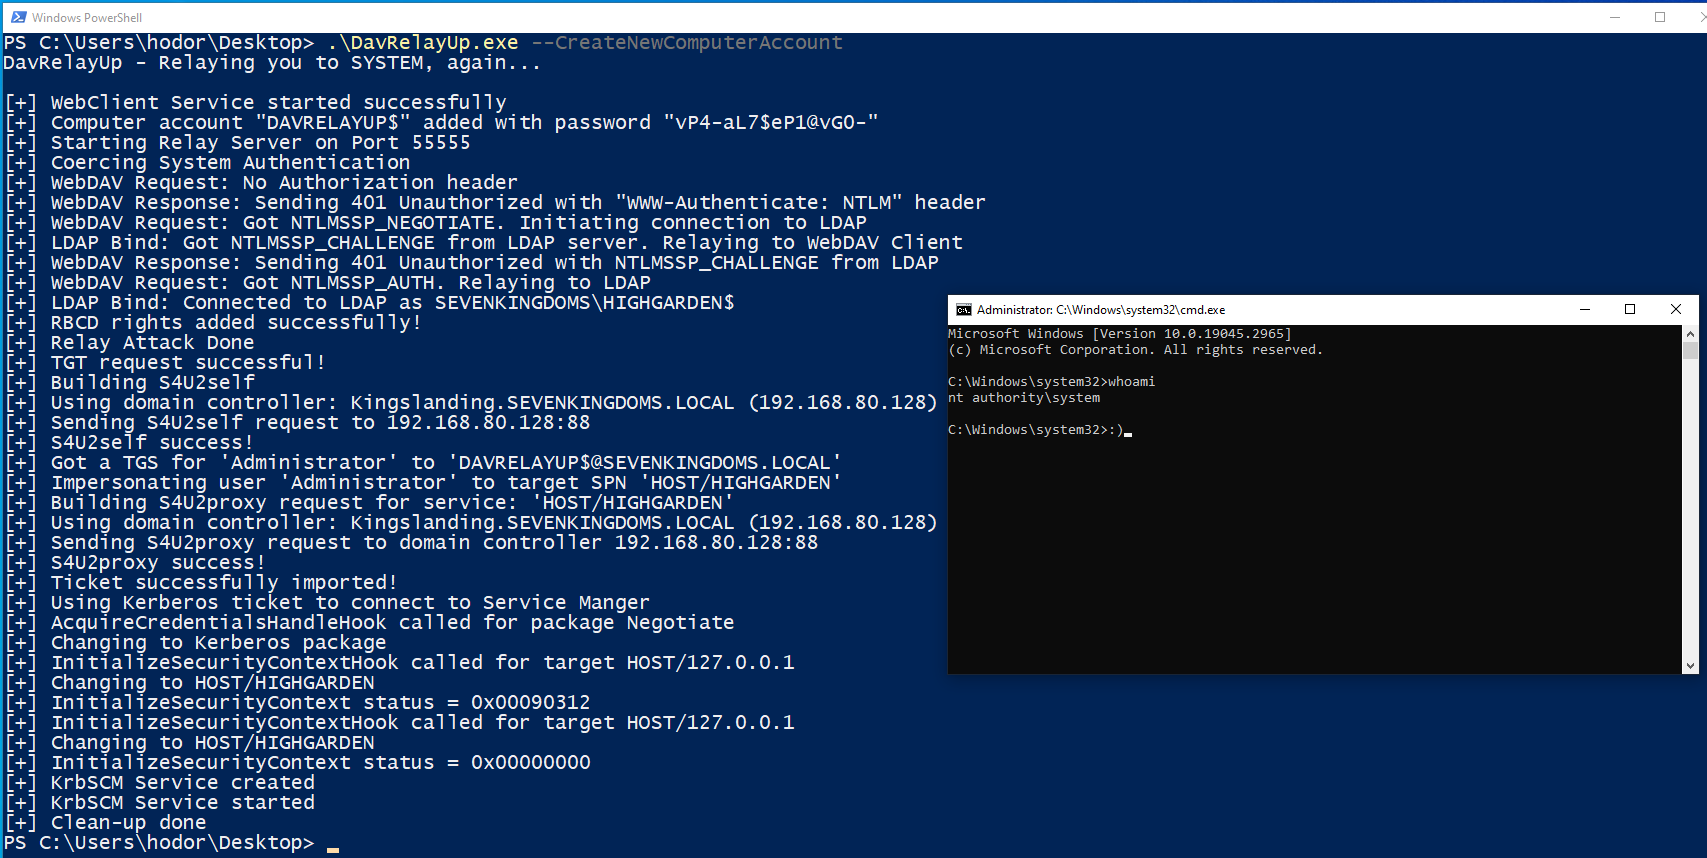 dec0ne/davrelayup
Automates local privilege escalation to SYSTEM on domain-joined Windows workstations by relaying NTLM authentication from WebDAV to LDAP, leveraging…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…

 mverschu/adwsdomaindump
Active Directory information dumper via ADWS for evasion purposes.
 neffisback/wsuks
Automating the MITM attack on WSUS
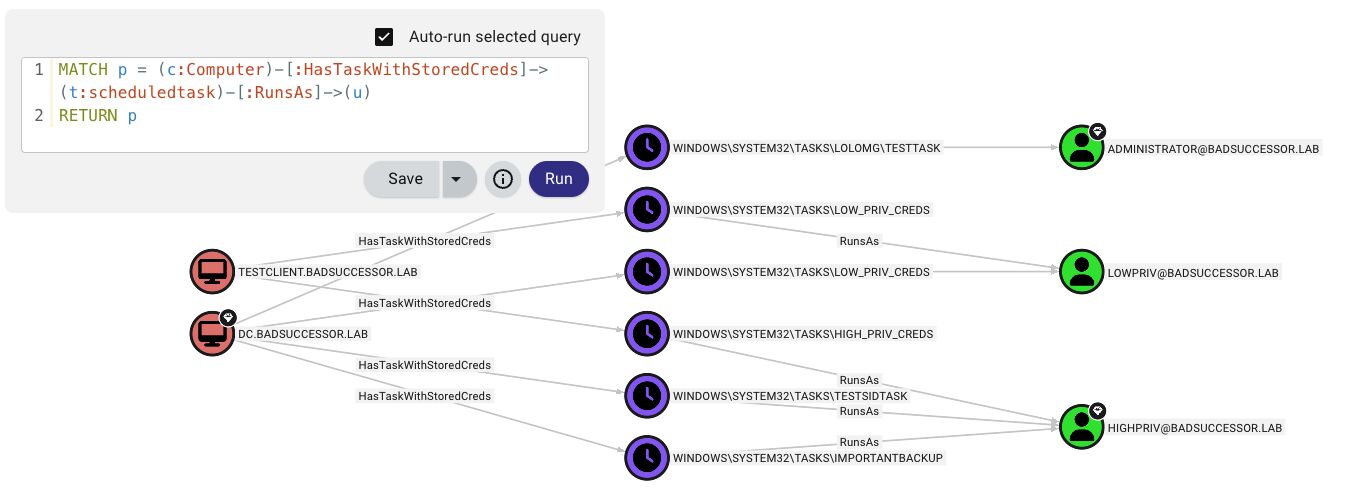 1r0bit/taskhound
Tool to enumerate privileged Scheduled Tasks on Remote Systems
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.
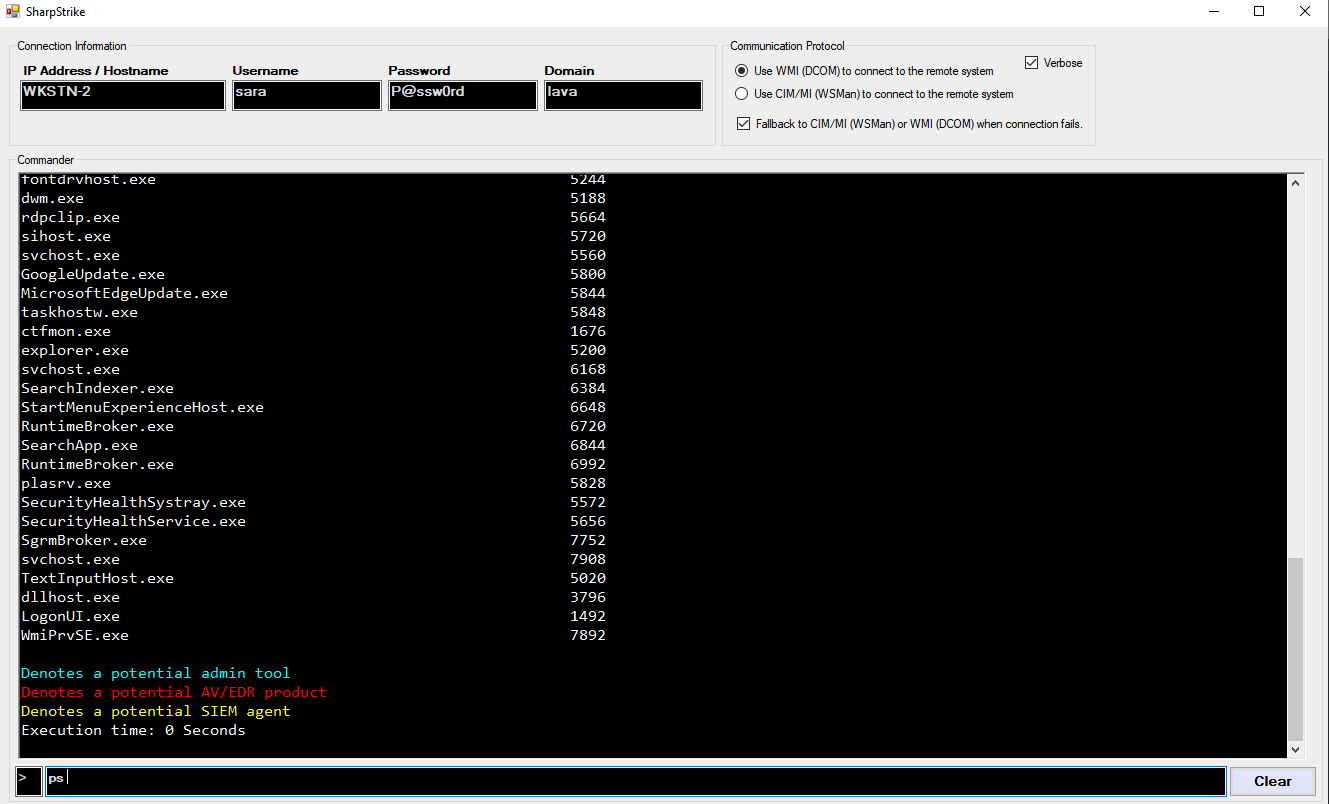 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.