
MAL-002
 mbadanoiu/mal-002
MAL-002: Force System Restart via Installed Windows MSIs
educationexploitationpost-exploitation+1
mbadanoiu/mal-002MAL-002: Force System Restart via Installed Windows MSIs
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 thesecretclub/sandboxbootkit
Bootkit for Windows Sandbox to disable DSE/PatchGuard.
 withsecurelabs/ppid-spoofing
Scripts for performing and detecting parent PID spoofing
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 oxfemale/killchain
Kernel Process Termination Tool ( CVE-2026-0828 exploit)
 shubham0d/cve-2021-30657
A sample POC for CVE-2021-30657 affecting MacOS
 malwareman007/cve-2022-21970
POC OF CVE-2022-21970
 afanpan/cve-2025-29824-exploit
Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.
 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
 xm0kht4r/cve-2025-7771
A simple PoC demonstrating the vulnerability in the ThrottleStop.sys driver, showcasing arbitrary physical memory read and write capabilities, as…
 kernelm0de/cve-2018-8090
DLL Hijacking in Quickheal Total Security/ Internet Security/ Antivirus Pro (Installers)
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 krakeneu/cve-2024-54910
Demonstrates arbitrary file write and privilege escalation in Hasleo Backup Suite Free <= 4.9.4 via symbolic links, enabling attackers to overwrite…
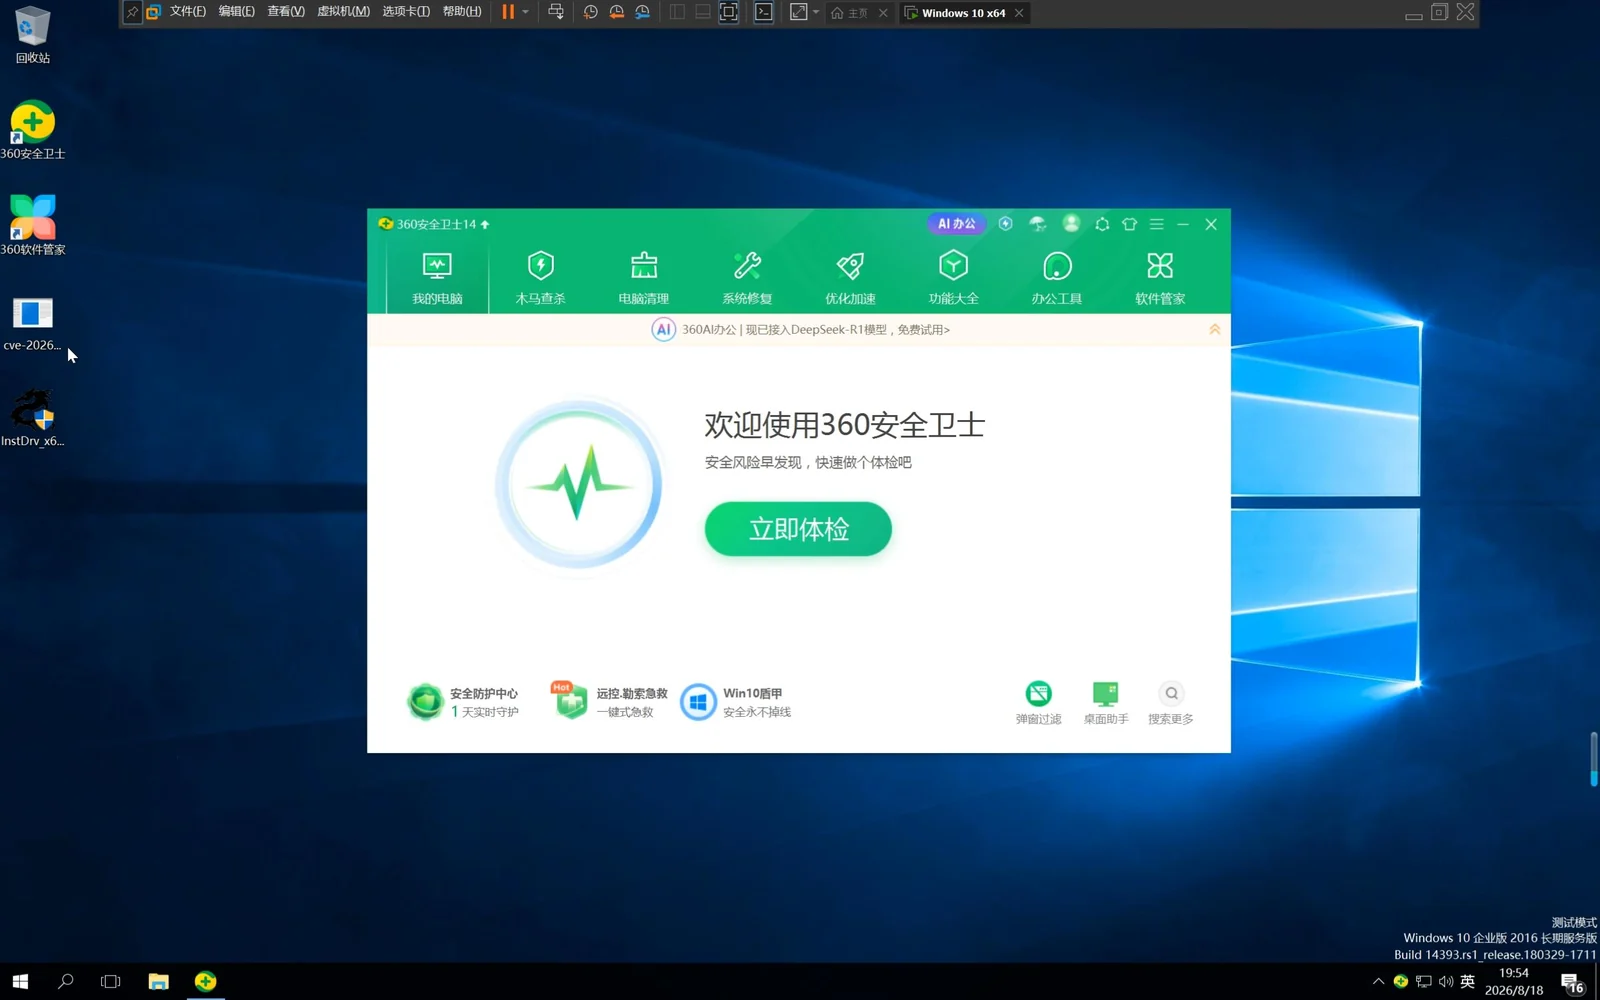 gongchuang1089/edrkiller
Use cve-2026-36425 killer edr,360 can killer