CVE-2026-24516-DigitalOcean-RCE.

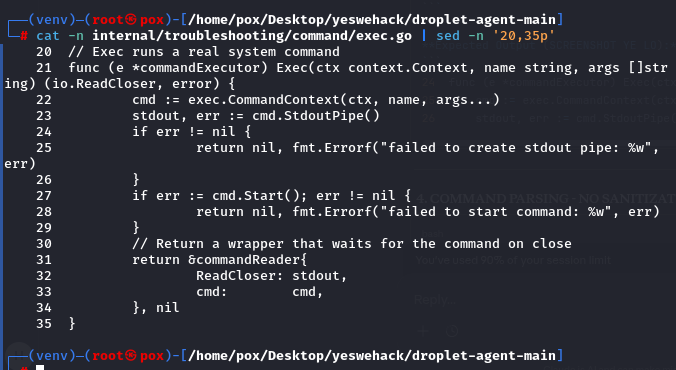
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).

Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).

An interactive command-line shell for BloodHound API.

C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.

Shell script to detect CVE-2019-14287 sudo privilege escalation vulnerability. Scans systems for the flaw and reports affected configurations.

Wing FTP Server 6.2.3 - Privilege Escalation

Identify privilege escalation paths within and across different clouds

SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS

A script to enumerate Google Storage buckets, determine what access you have to them, and determine if they can be privilege escalated.

PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…

AzureRT - A Powershell module implementing various Azure Red Team tactics

Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…

MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…

Security advisory detailing a critical authentication vulnerability (CVE-2025-4162029) in Copilot, enabling unauthorized account access via user ID…

Windows protocol library, including SMB and RPC implementations, among others.

Bash script purposed for system enumeration, vulnerability identification and privilege escalation.

Multithreaded C# .NET assembly for enumerating local administrative privileges across Windows hosts via SMB, WMI, and WinRM, with BloodHound…

Seatbelt is a C# project that performs a number of security oriented host-survey "safety checks" relevant from both offensive and defensive security…

LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.