
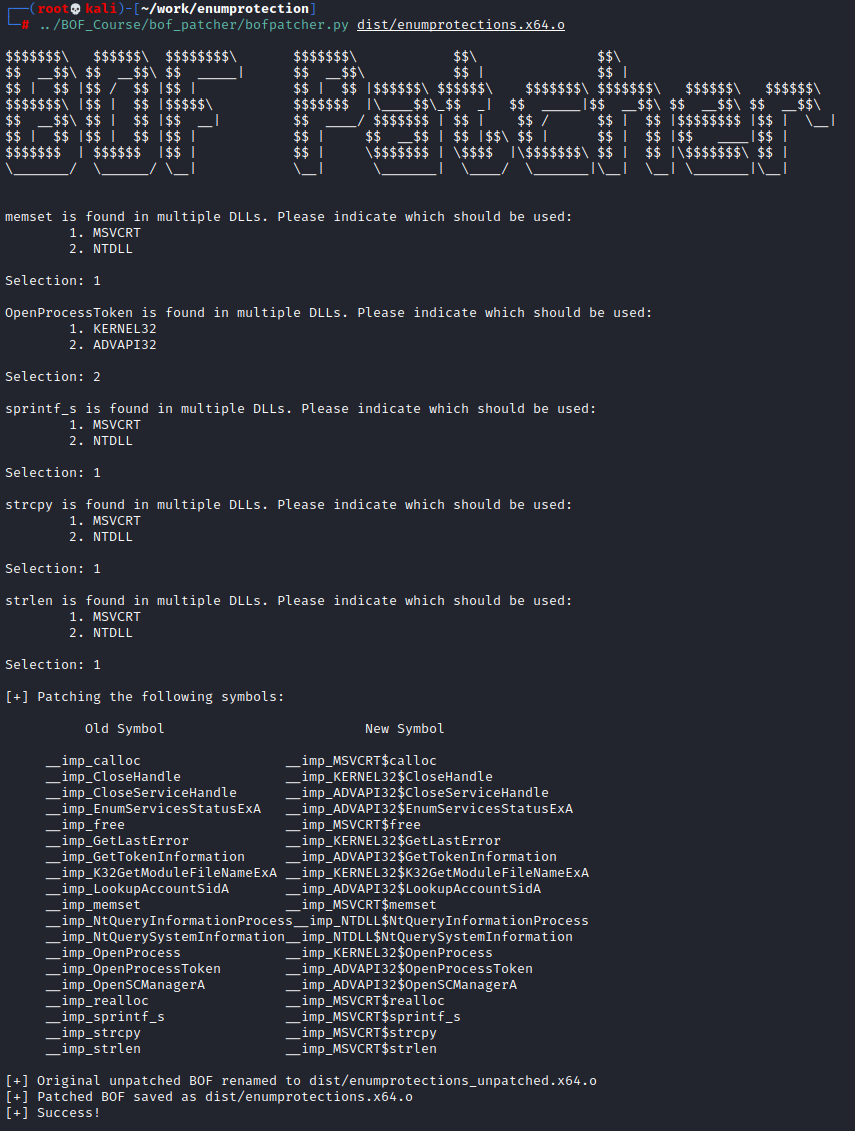
Enumprotections_BOF
 octoberfest7/enumprotections_bof
A BOF to enumerate system process, their protection levels, and more.
information-gatheringpenetration-testingpost-exploitation+4
126
octoberfest7/enumprotections_bofA BOF to enumerate system process, their protection levels, and more.
 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
 ffri/cve-2025-24204
PoC and technical details of CVE-2025-24204
 nccgroup/ncloader
A session-0 capable dll injection utility
 anylnk/ksldbyovdark
Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…
 h4rk3nz0/cve-2023-20598-pdfwkrnl
CVE-2023-20598 Kernel Driver - Elevation of Privilege
 irsl/google-osconfig-privesc
Proof of concept about the privilege escalation flaw identified in Google's Osconfig
 homjxi0e/cve-2017-1000367
Proof-of-concept exploit for CVE-2017-1000367, a local privilege escalation vulnerability in Sudo's get_process_ttyname() on Linux, allowing…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 netbiosx/checklists
Red Teaming & Pentesting checklists for various engagements
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 mutur4/cve-2022-0847
Drity Pipe Linux Kernel 1-Day Exploit
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.
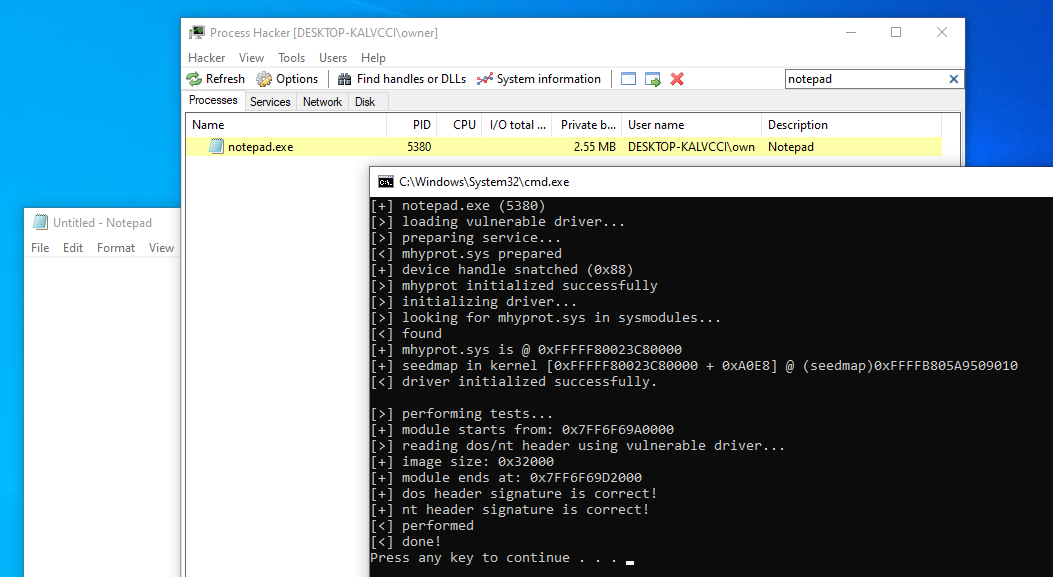 kkent030315/evil-mhyprot-cli
A PoC for Mhyprot2.sys vulnerable driver that allowing read/write memory in kernel/user via unprivileged user process.
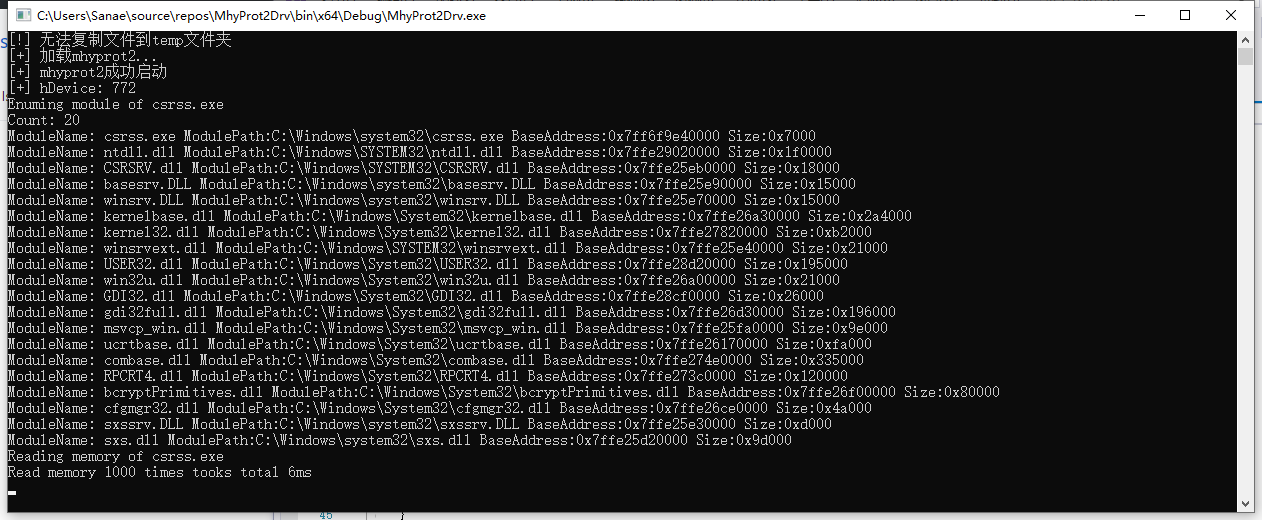 kagurazakasanae/mhyprot2drvcontrol
A lib that allows using mhyprot2 driver for enum process modules, r/w process memory and kill process.