

Linux_Exploit_Suggester
 intelisecurelabs/linux_exploit_suggester
Linux Exploit Suggester; based on operating system release number
exploitationinformation-gatheringpenetration-testing+3
1.8k
intelisecurelabs/linux_exploit_suggesterLinux Exploit Suggester; based on operating system release number
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 xairy/kernel-exploits
My proof-of-concept exploits for the Linux kernel
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 dirkjanm/bloodhound.py
A Python based ingestor for BloodHound
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 tevora-threat/sharpview
C# implementation of harmj0y's PowerView
 wireghoul/htshells
Self contained htaccess shells and attacks
 quentinhardy/msdat
MSDAT: Microsoft SQL Database Attacking Tool
 cyberark/skyark
SkyArk helps to discover, assess and secure the most privileged entities in Azure and AWS
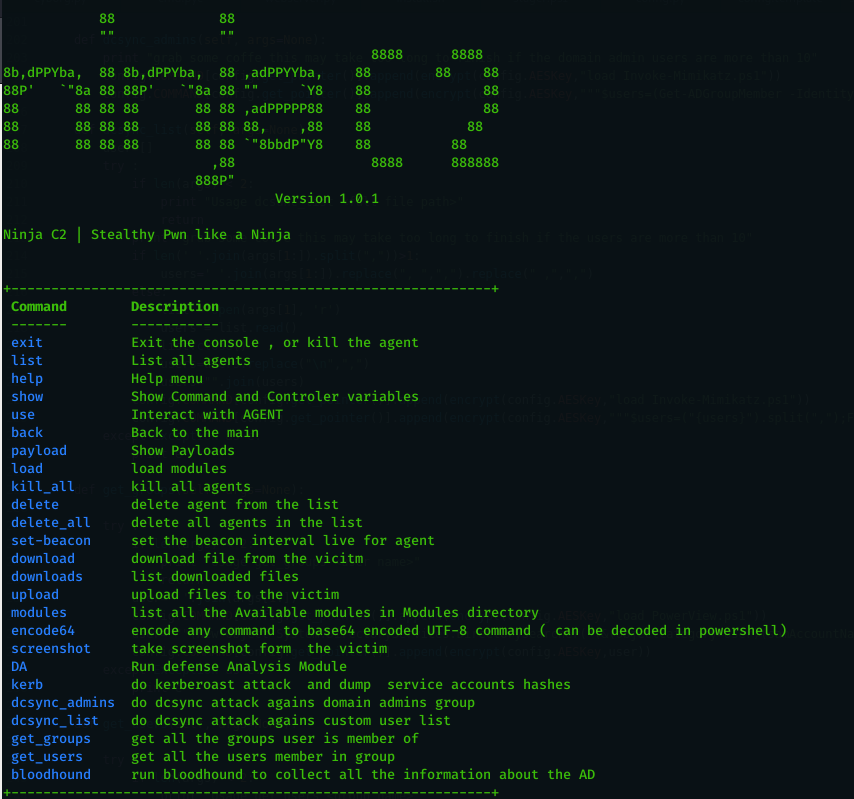 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 al1ex/pentest-tools
Intranet penetration tools
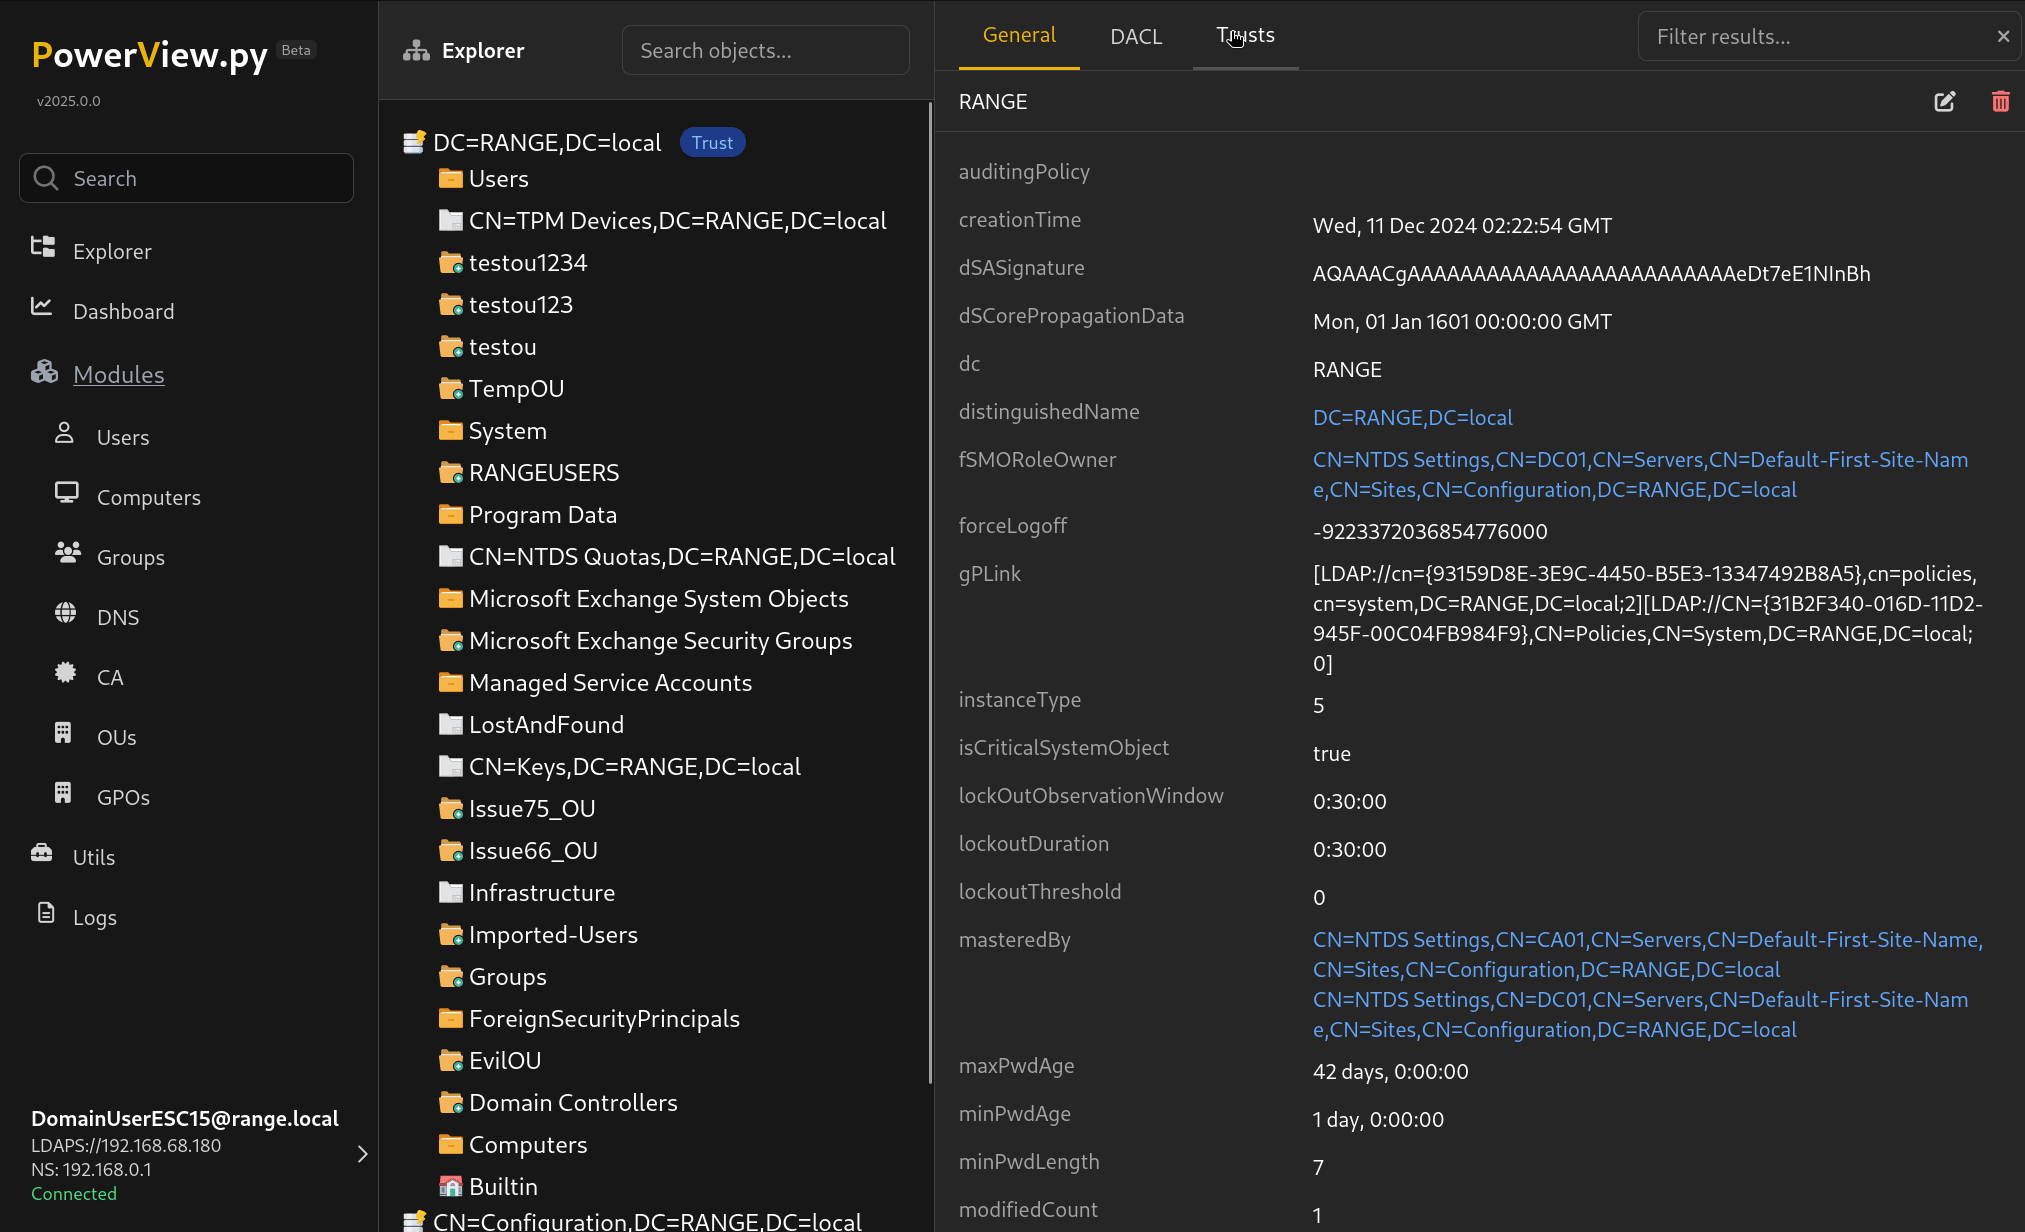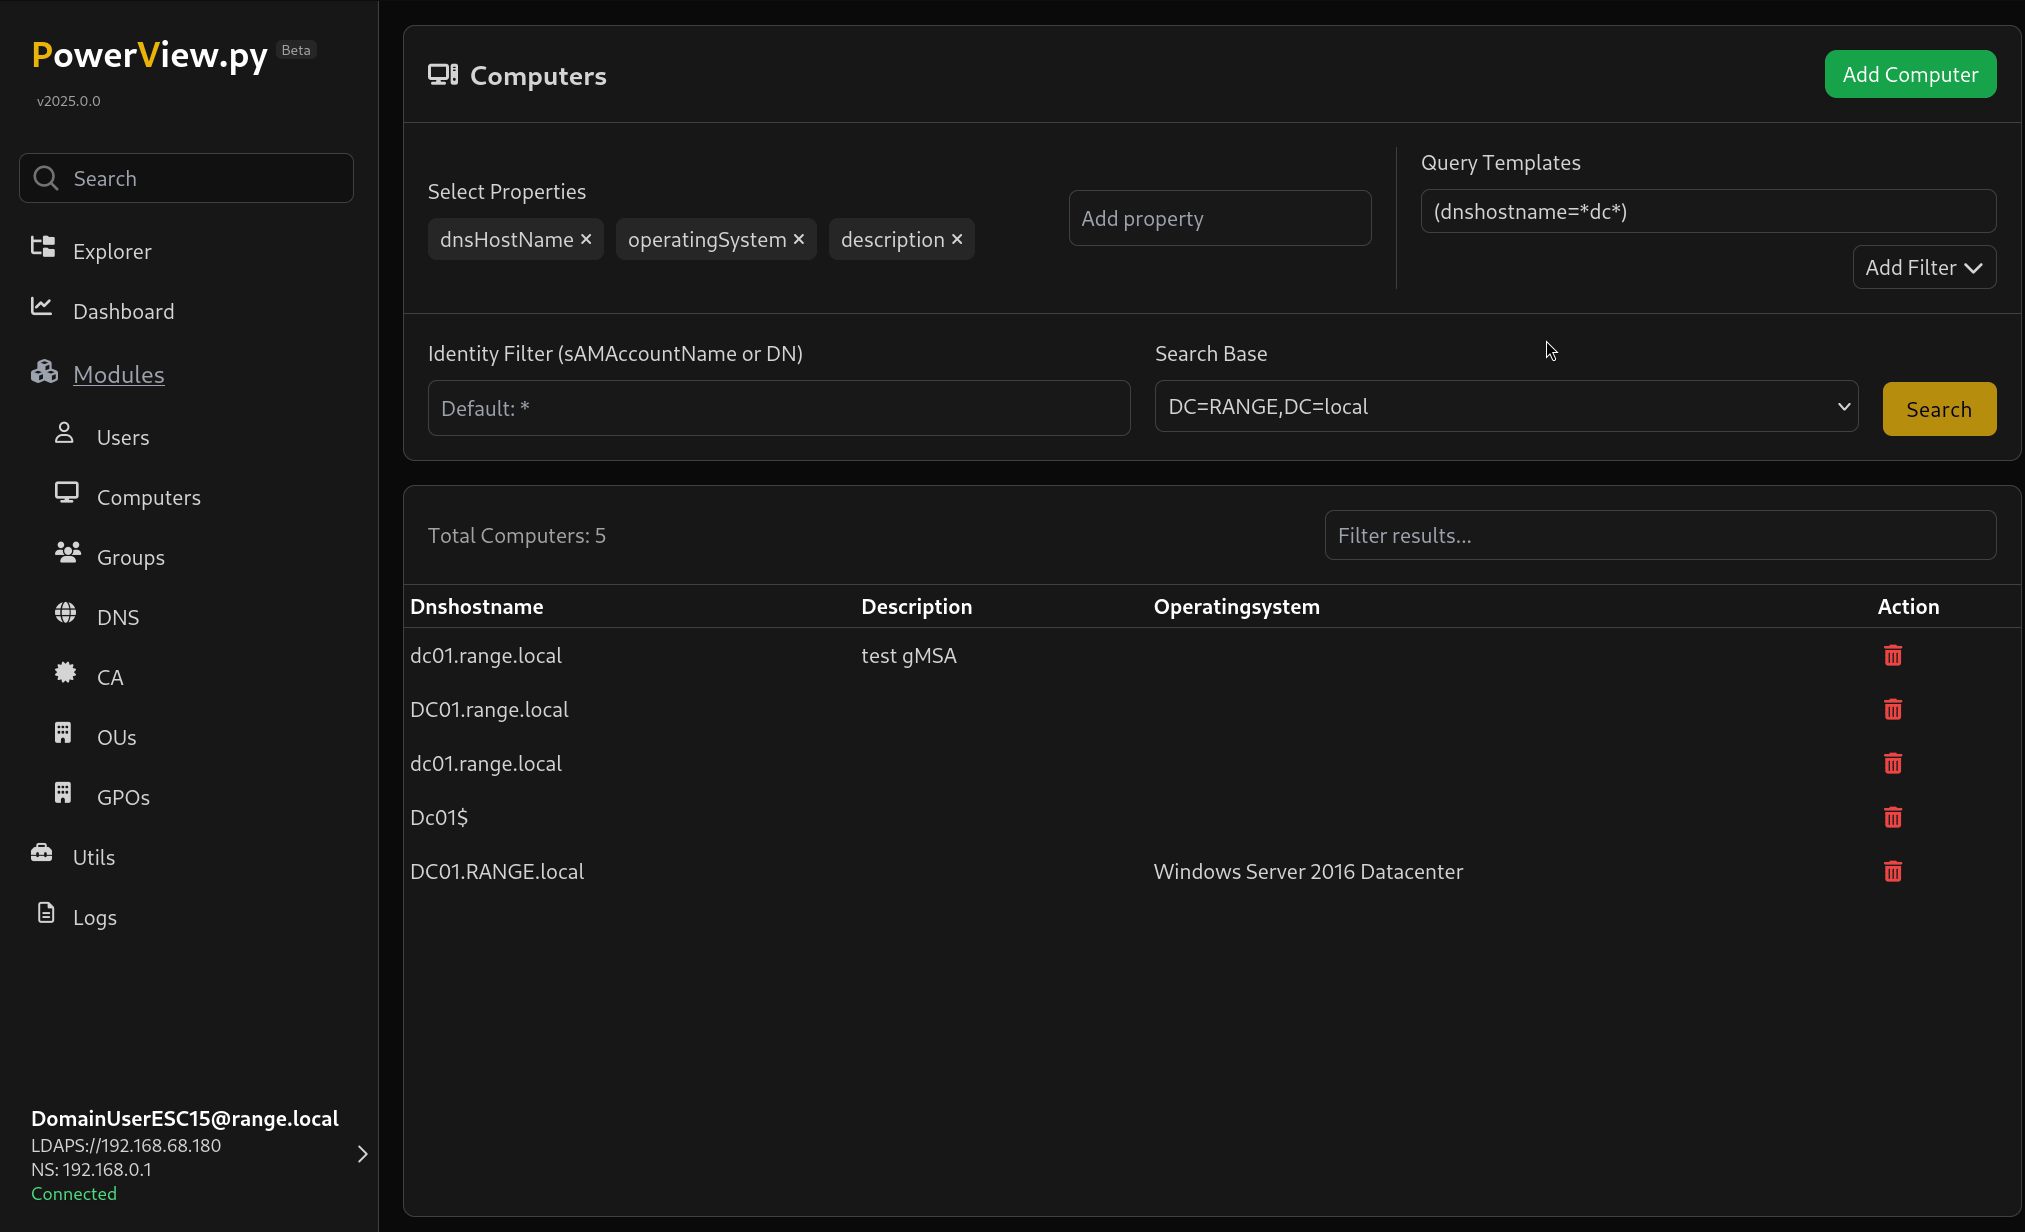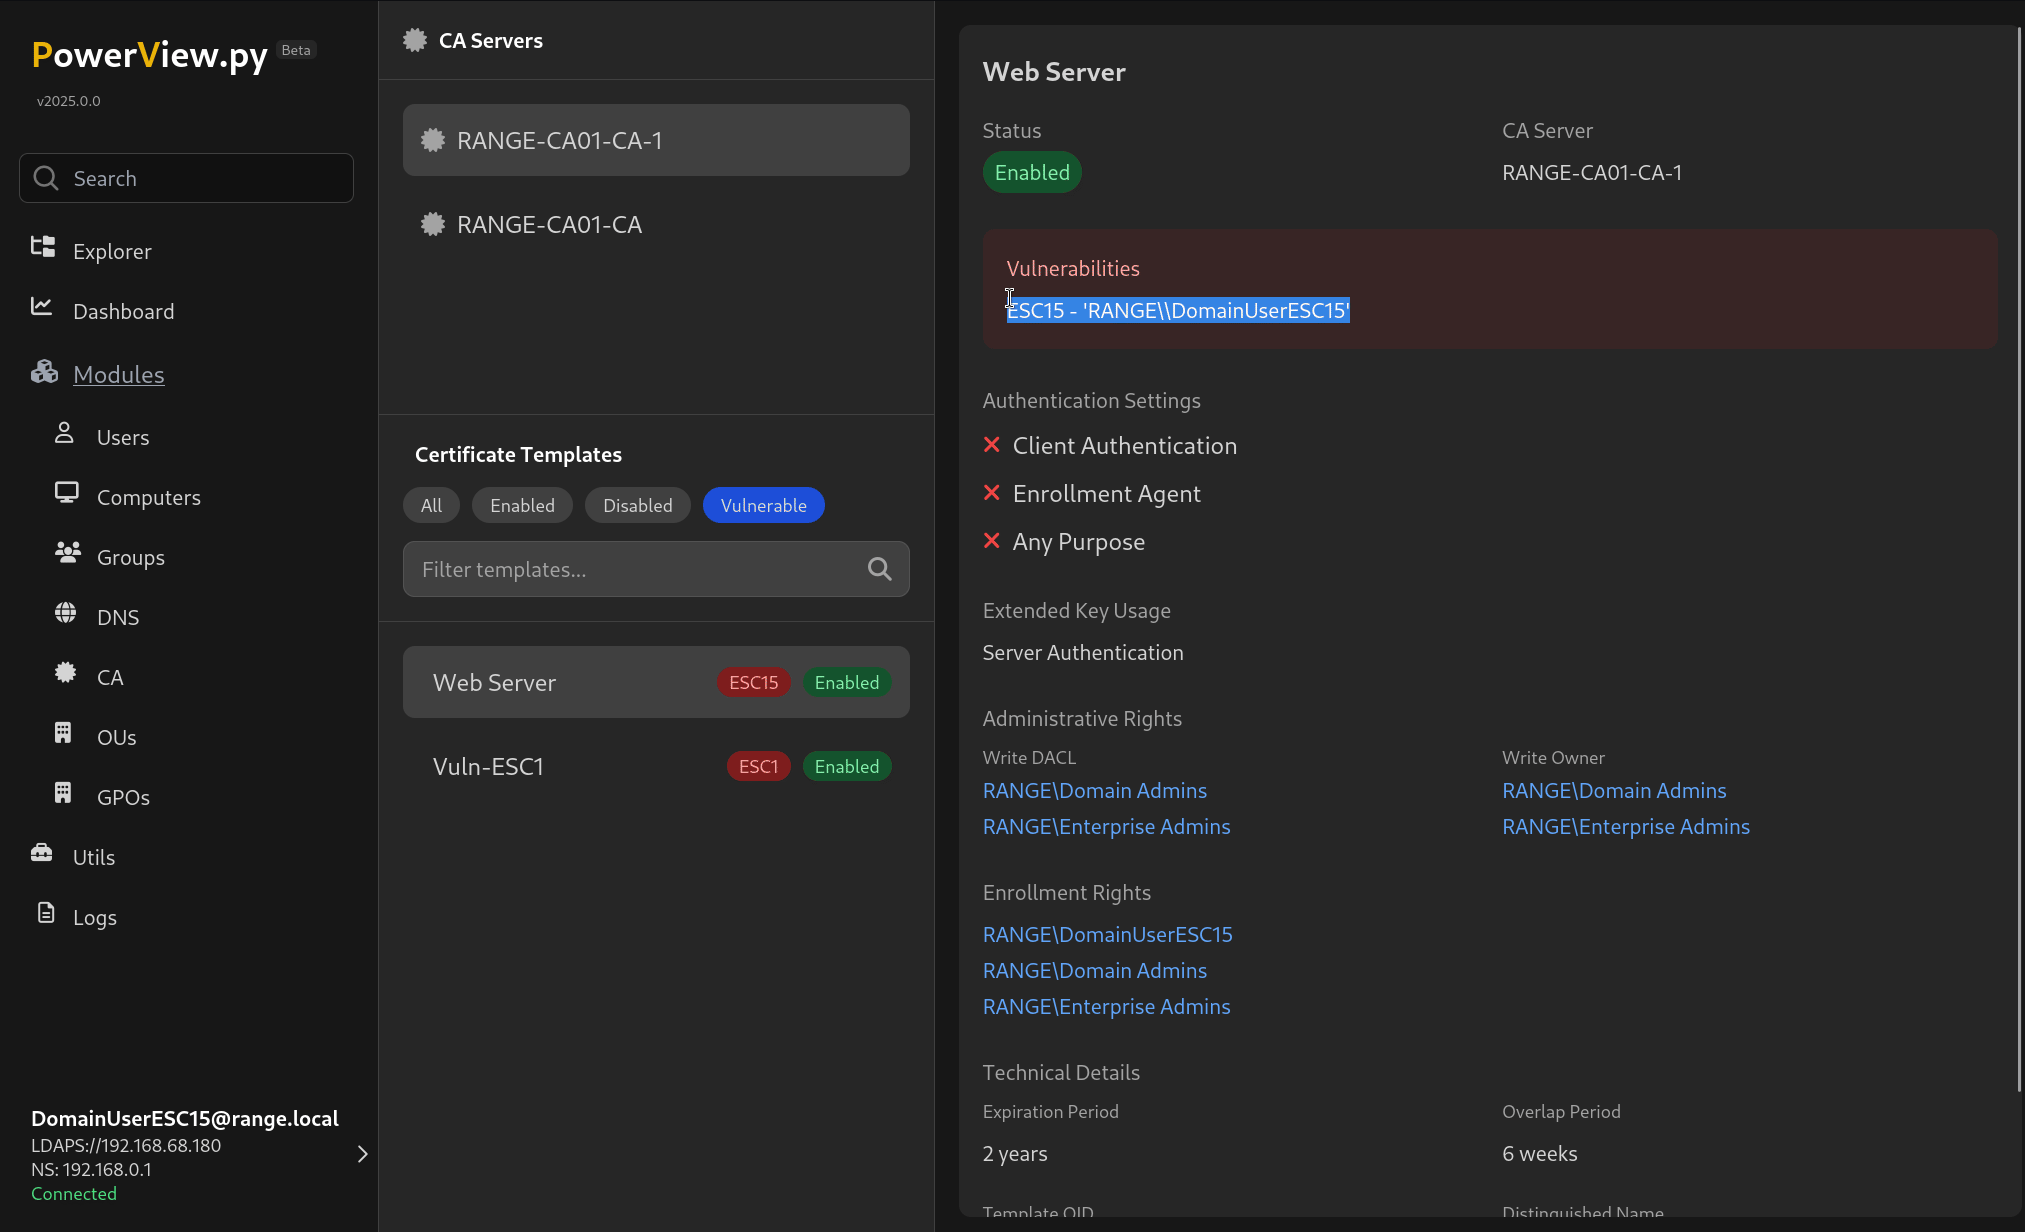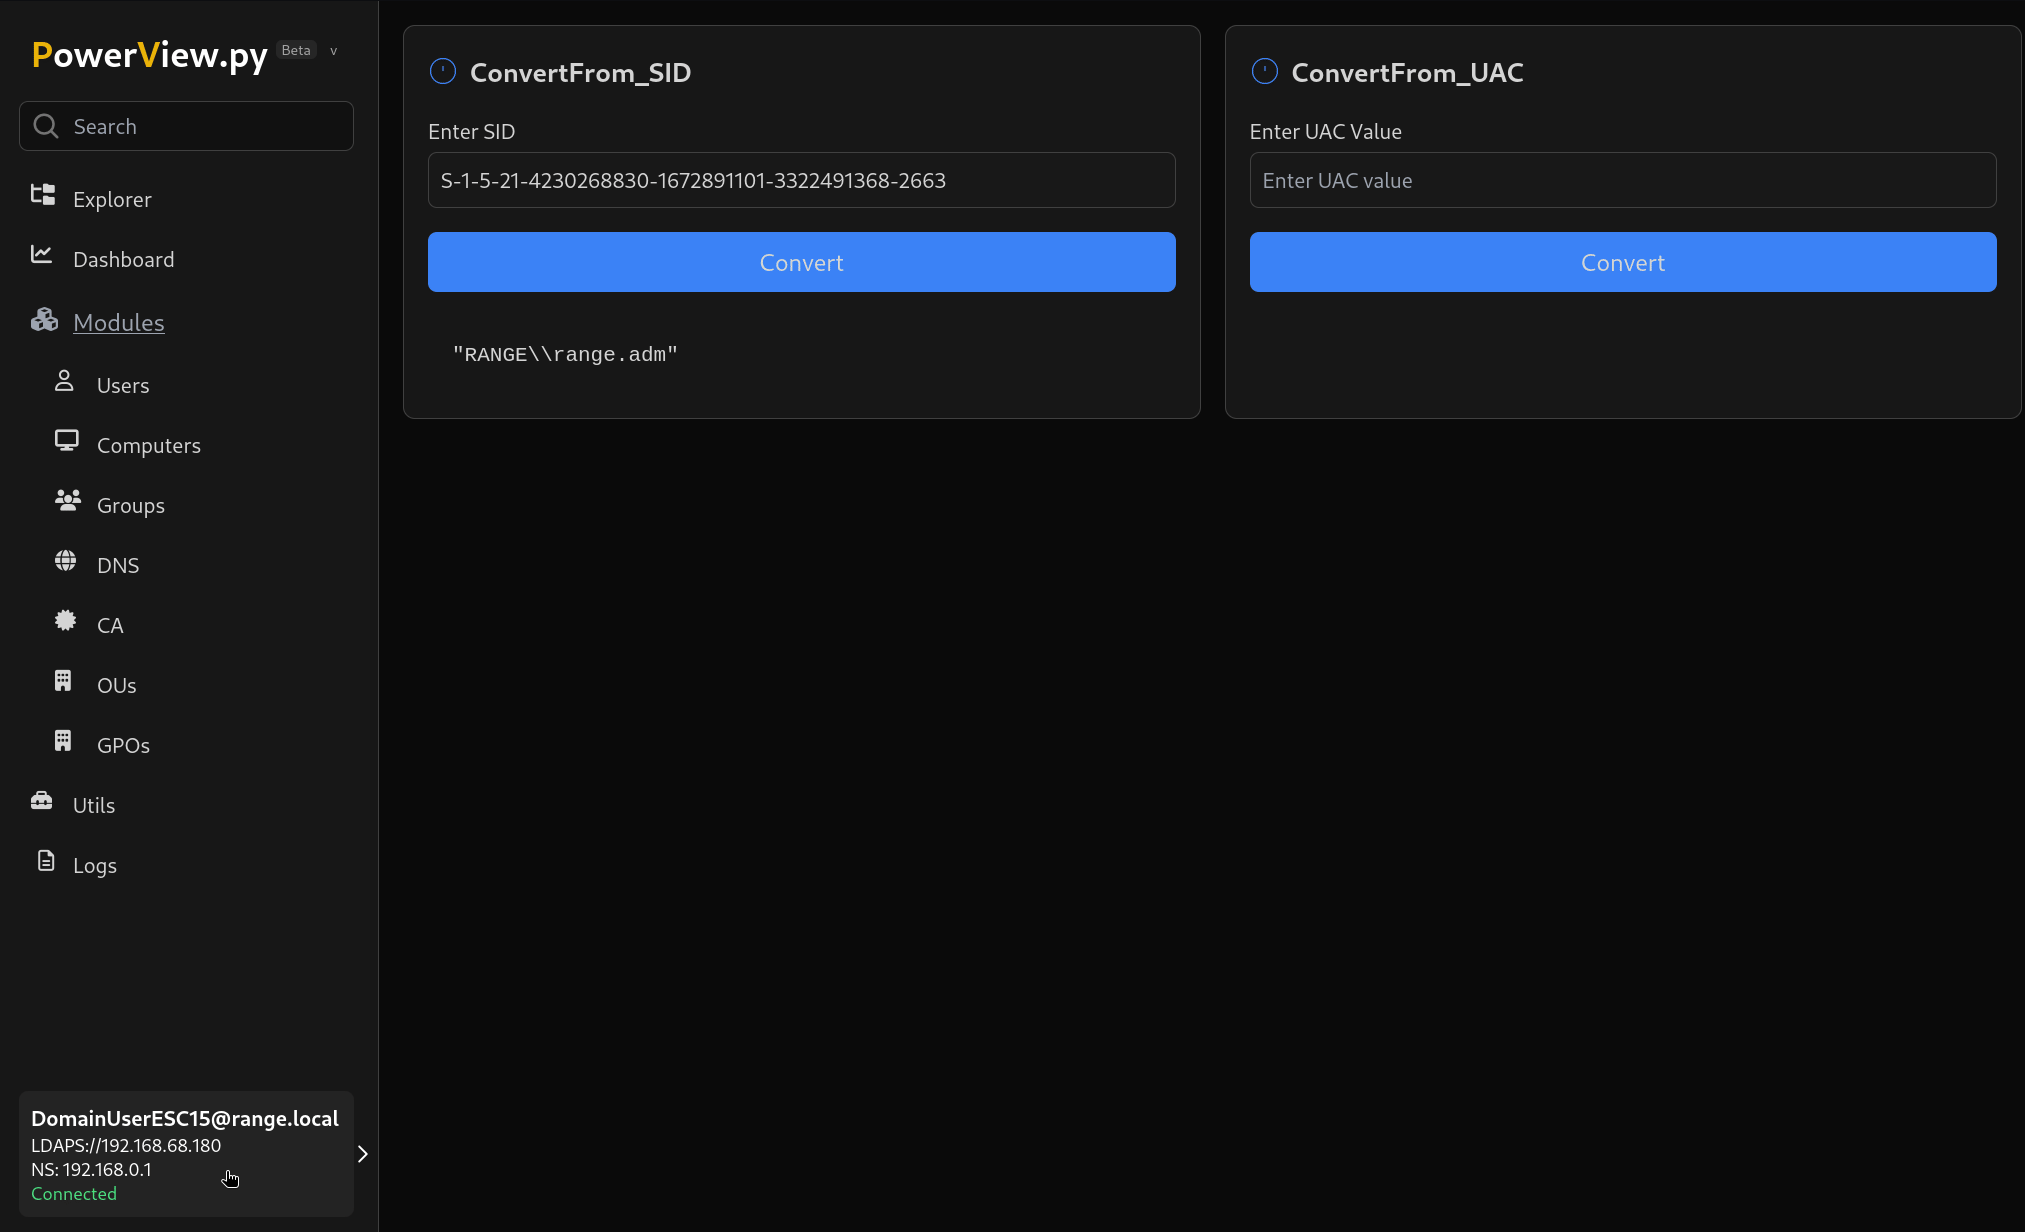 aniqfakhrul/powerview.py
Powerview on steroids
 leoloobeek/lapstoolkit
Tool to audit and attack LAPS environments