
nanodump
 fortra/nanodump
The swiss army knife of LSASS dumping
exploitationmemory-forensicspayload-development+4
fortra/nanodumpThe swiss army knife of LSASS dumping
 waawaa/breakcyserver
Red-team EDR evasion utility that terminates security services by abusing Process Explorer driver functionality to bypass PPL and ObRegisterCallbacks.
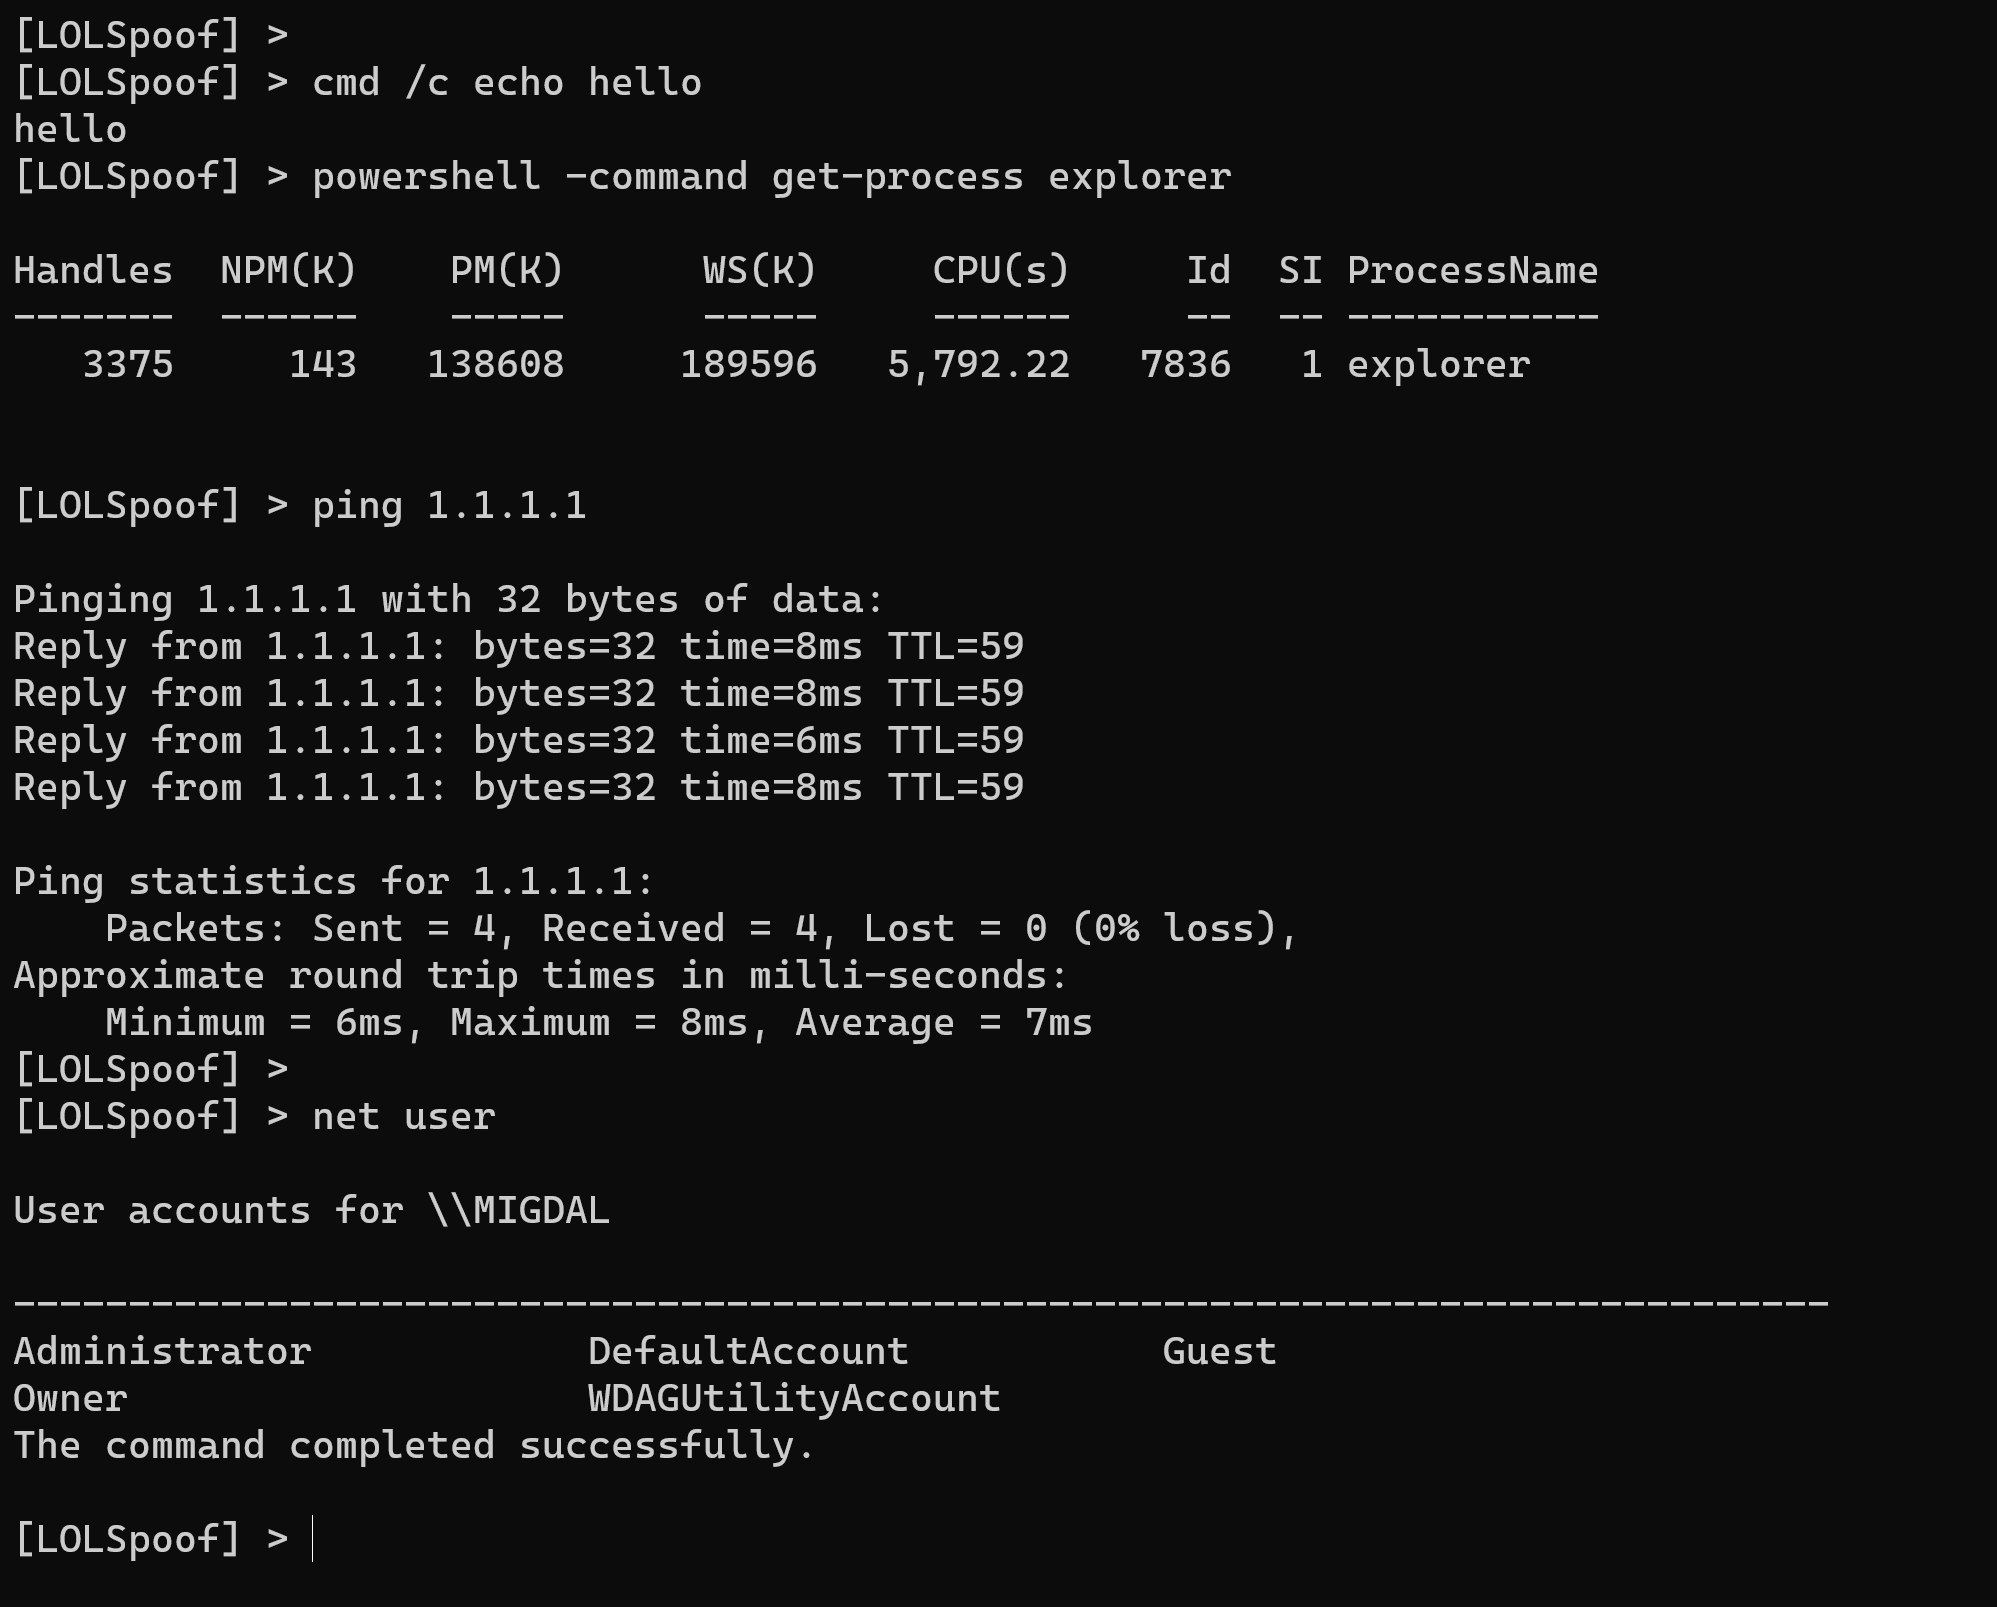 itaymigdal/lolspoof
An interactive shell to spoof some LOLBins command line
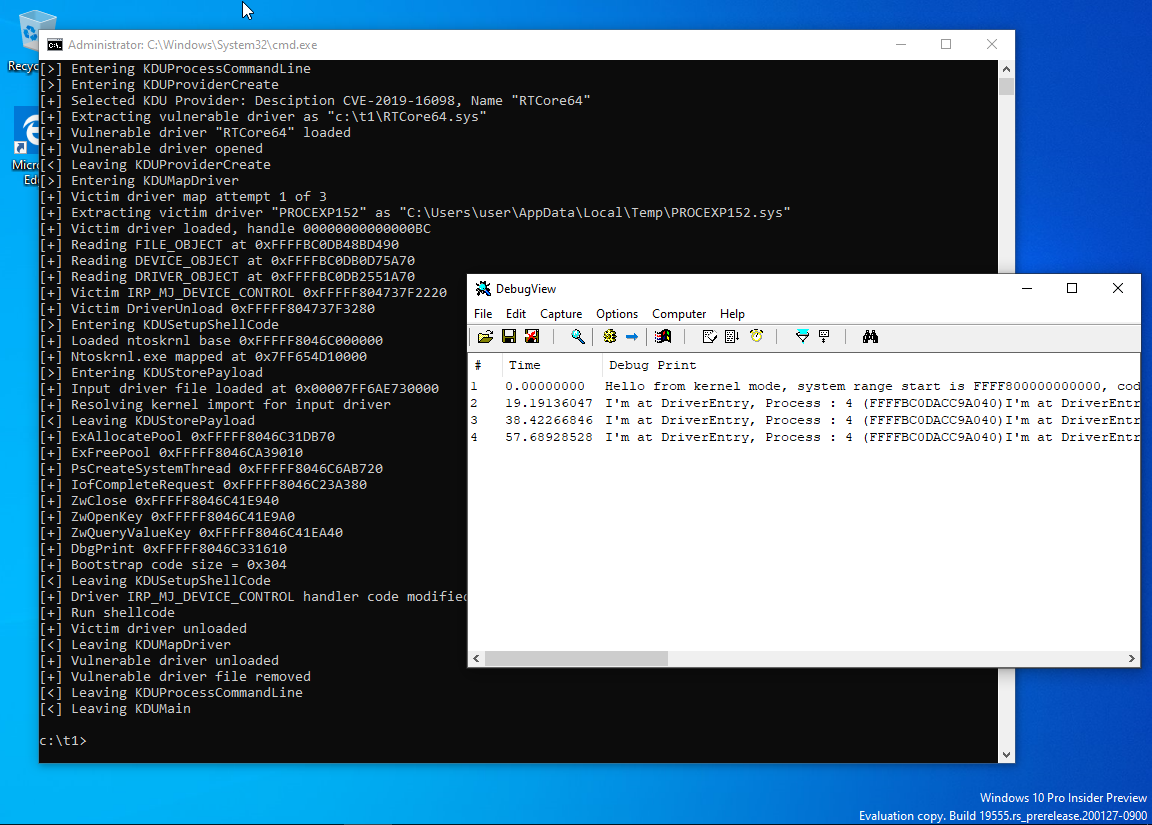 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…
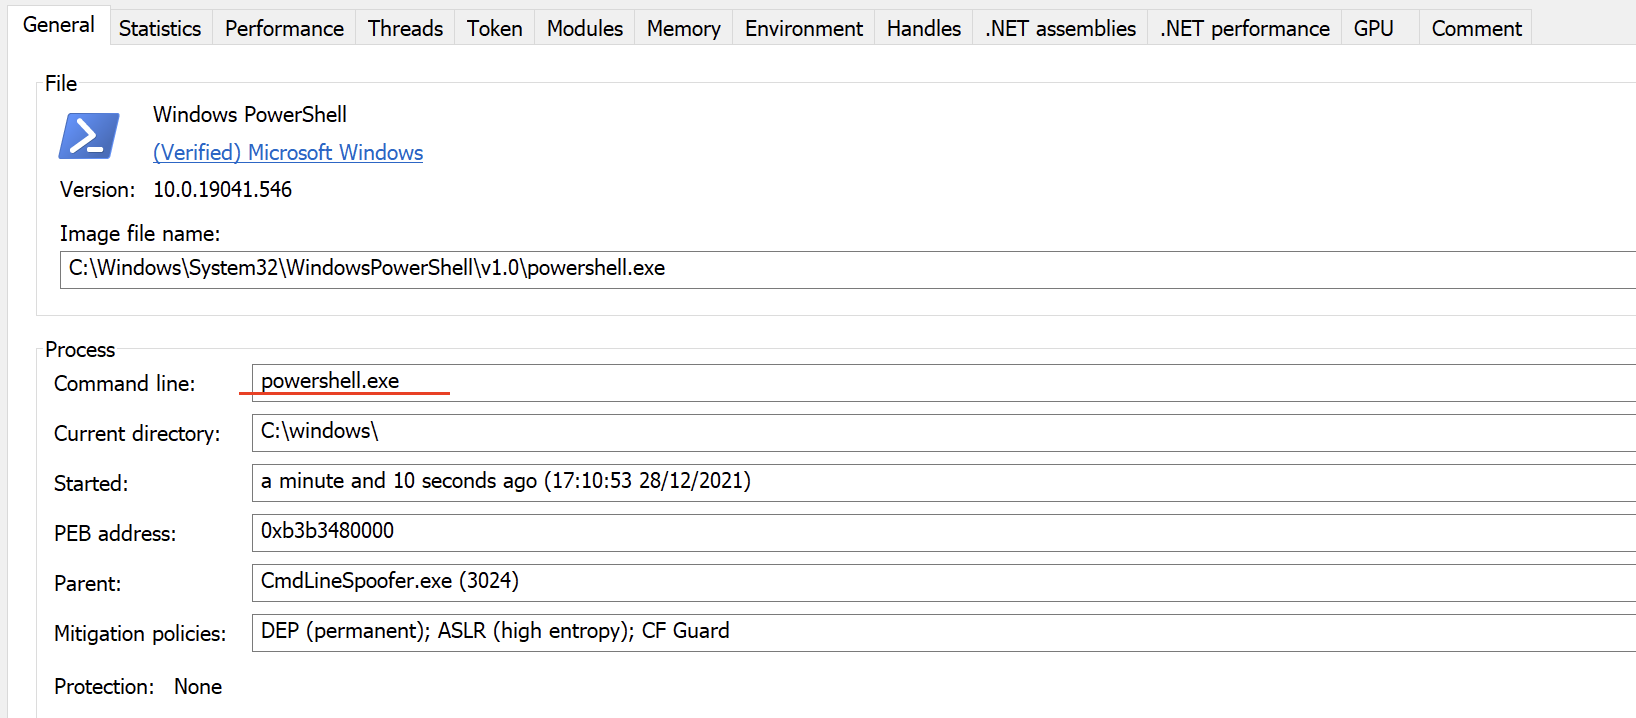 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
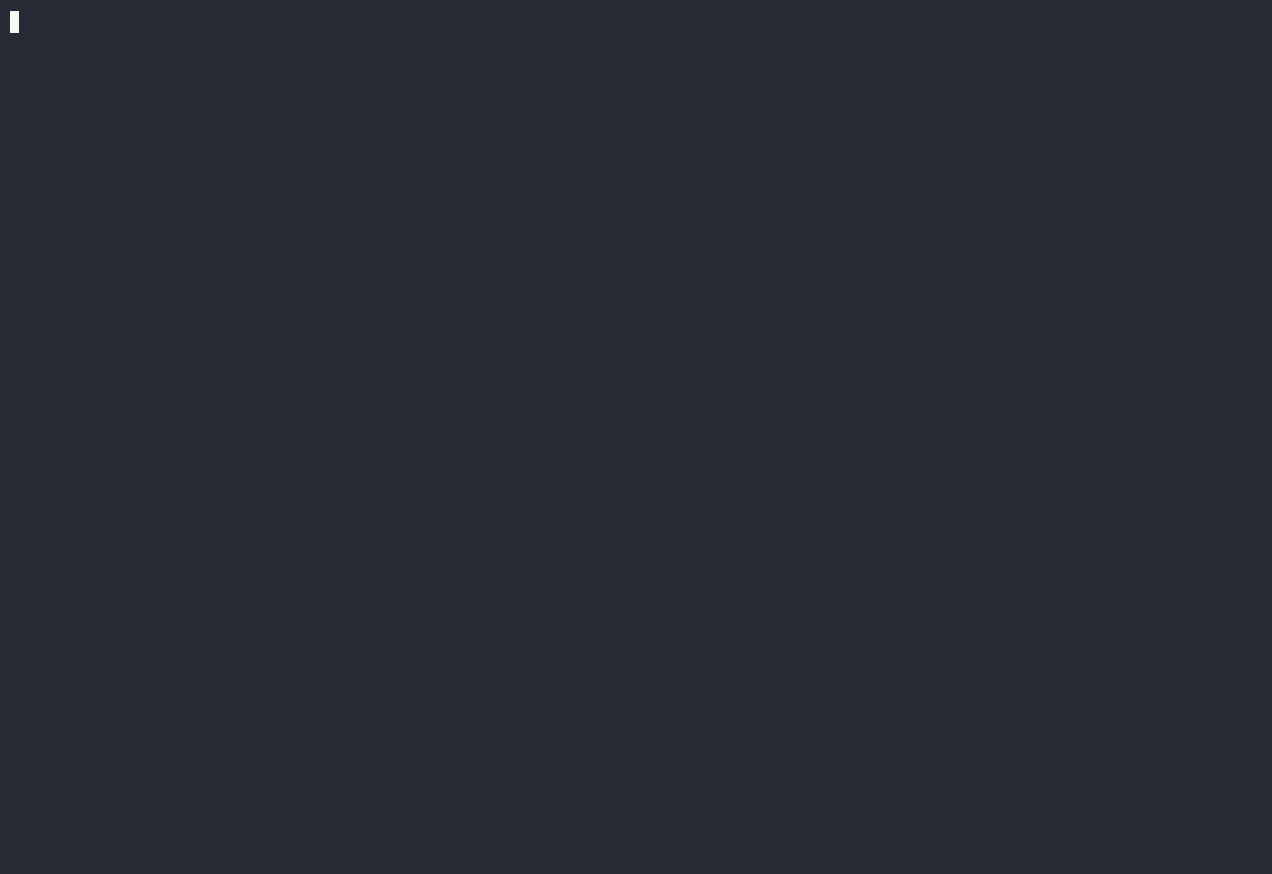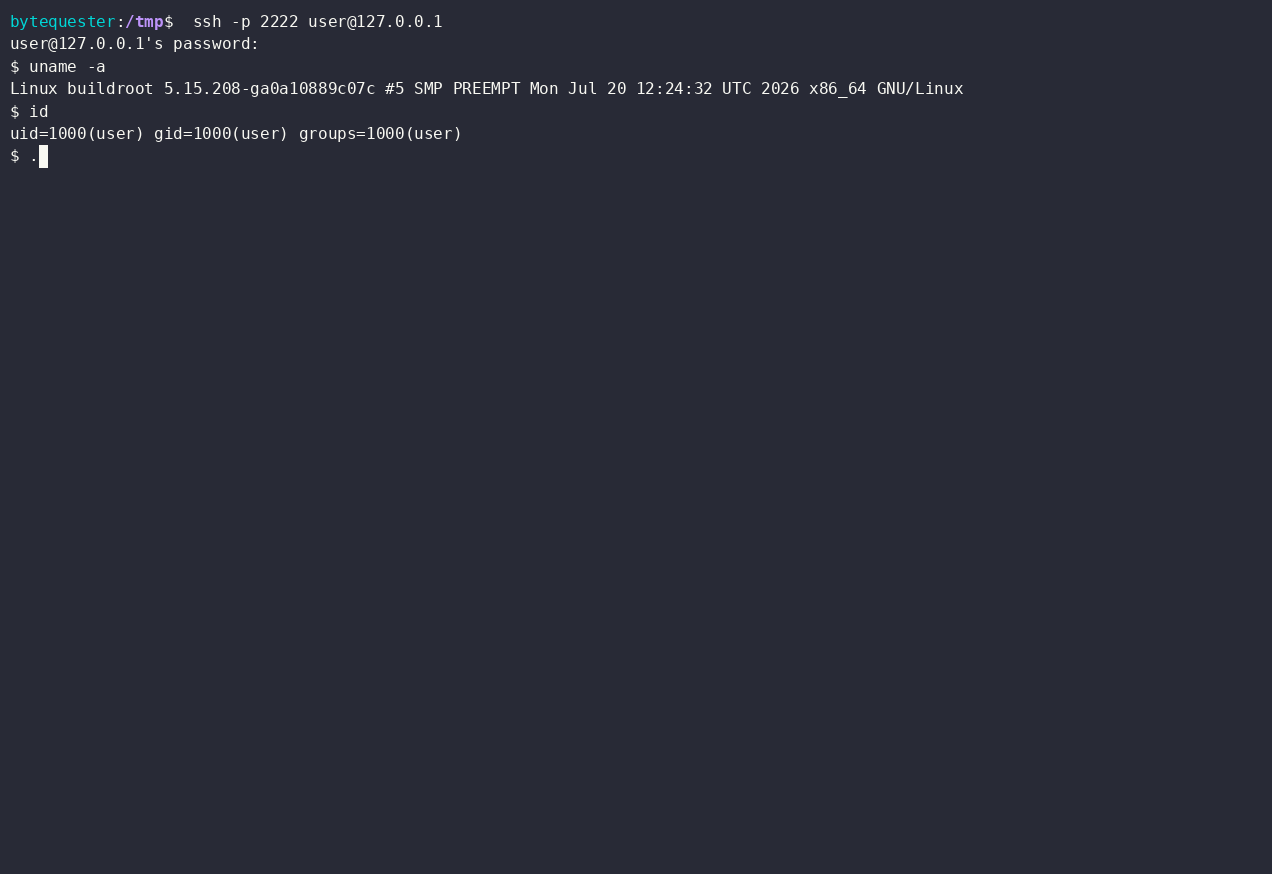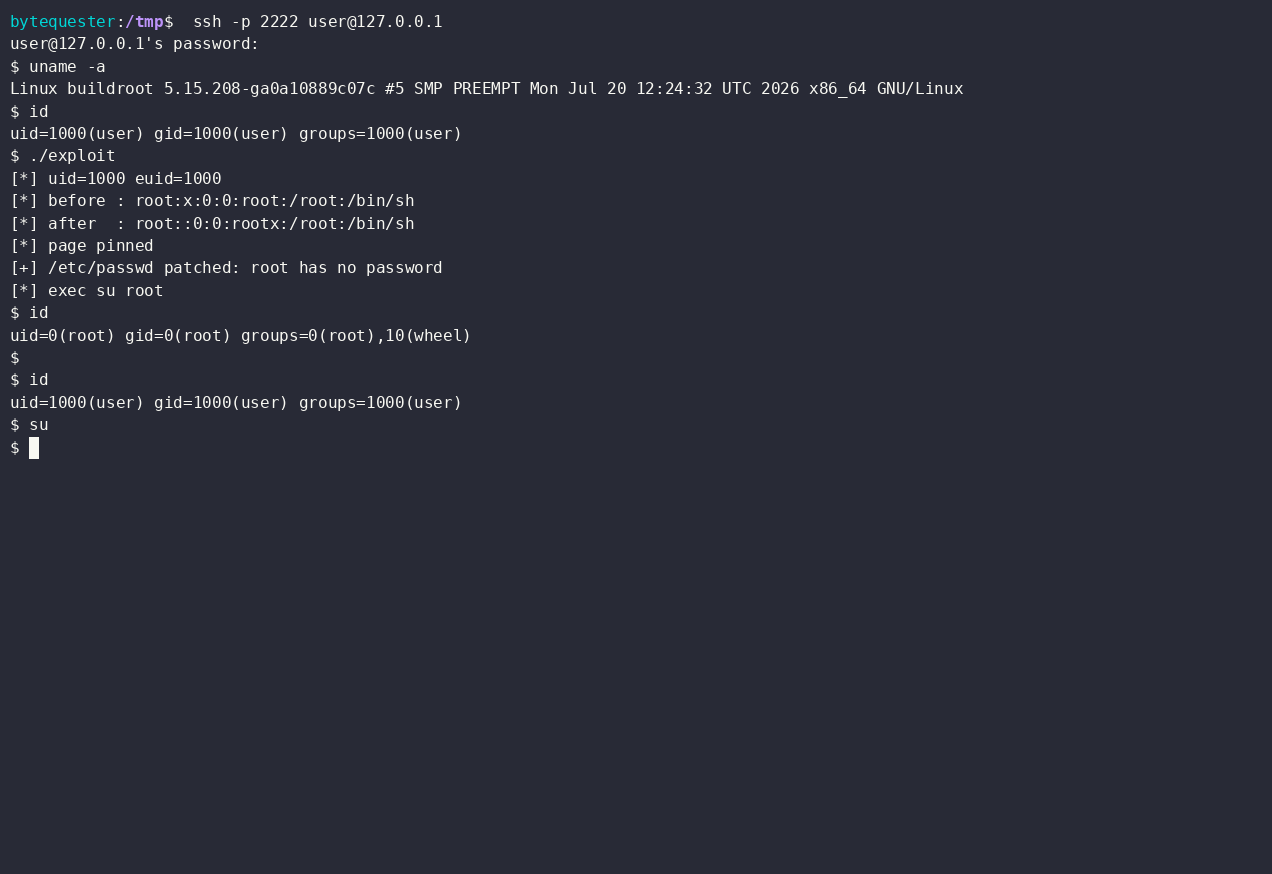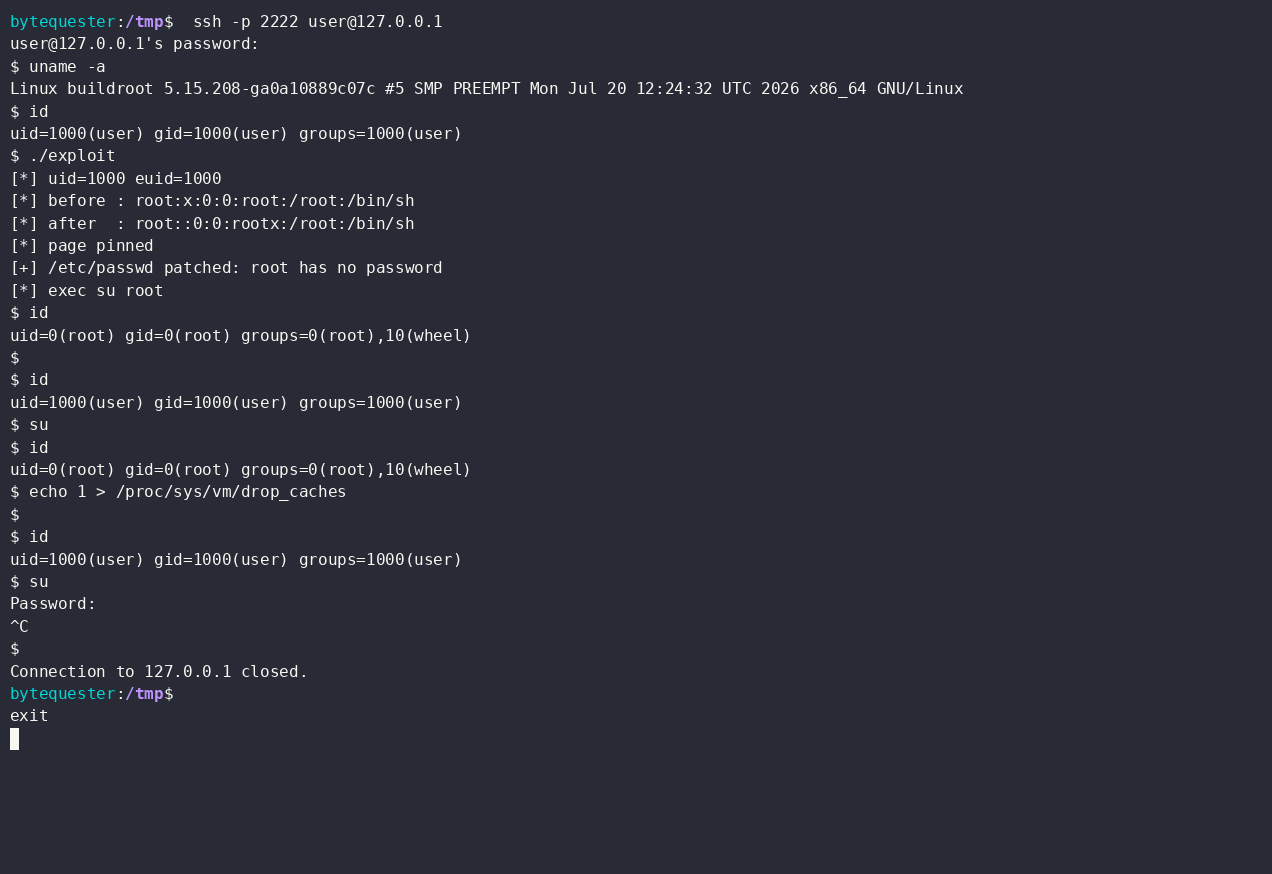 byt3quester/cve-2022-22706-poc
Proof-of-concept exploit for CVE-2022-22706: exploits a Mali GPU kernel driver page-cache write flaw to modify /etc/passwd in memory and obtain a…
 michalbednarski/resourcepoison
Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…
 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 zeromemoryex/tokenizer
Simple Kernel Mode Driver for Swapping Process Token
 blacksnufkin/credshunter
PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
 v31l0x1/throttlestopppl
Poc for CVE-2025-7771 to modify PPL Protection
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 r3vpwnx/cve-2025-8110
Proof-of-concept exploit for CVE-2025-8110 in Gogs <=0.13.x, enabling authenticated symlink bypass to arbitrary file write as the Gogs process user,…
 ustayready/wnfexec
WNF Code Execution Library Using C#
 cicada8-research/ihxexec
Process injection alternative
 deathshotxd/0xkern3lcrush
Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…
 sentinelblue/cve-2022-29072
** DISPUTED ** 7-Zip through 21.07 on Windows allows privilege escalation and command execution when a file with the .7z extension is dragged to the…