

SharpMapExec
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
authenticationdata-exfiltrationexploitation+9
666
cube0x0/sharpmapexecWindows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 fortalice/modifycerttemplate
ADCS cert template modification and ACL enumeration
 shellster/ldapper
LDAP Querying without the Suck
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 ad-security/ad_miner
AD Miner is an Active Directory audit tool that leverages cypher queries to crunch data from the #Bloodhound graph database to uncover security…
 fox-it/aclpwn.py
Active Directory ACL exploitation with BloodHound
 graniet/inspector
The Inspector tool is a privilege escalation helper (PoC), easy to deployed on web server, this tool can list process running with root, check kernel…
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
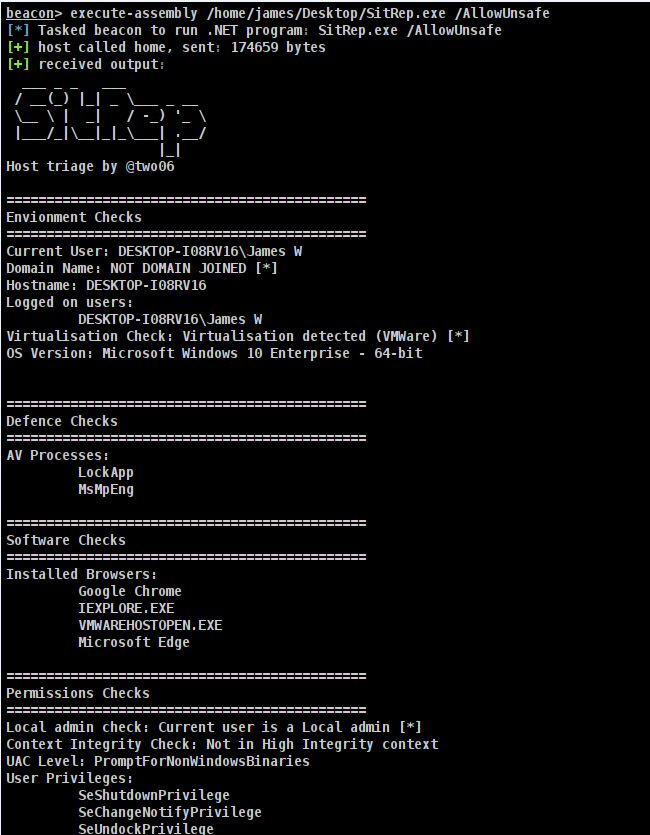 mdsecactivebreach/sitrep
Extensible host triage tool for red teams, dynamically loading OpSec-aware checks to gather user, domain, privilege, and credential information from…
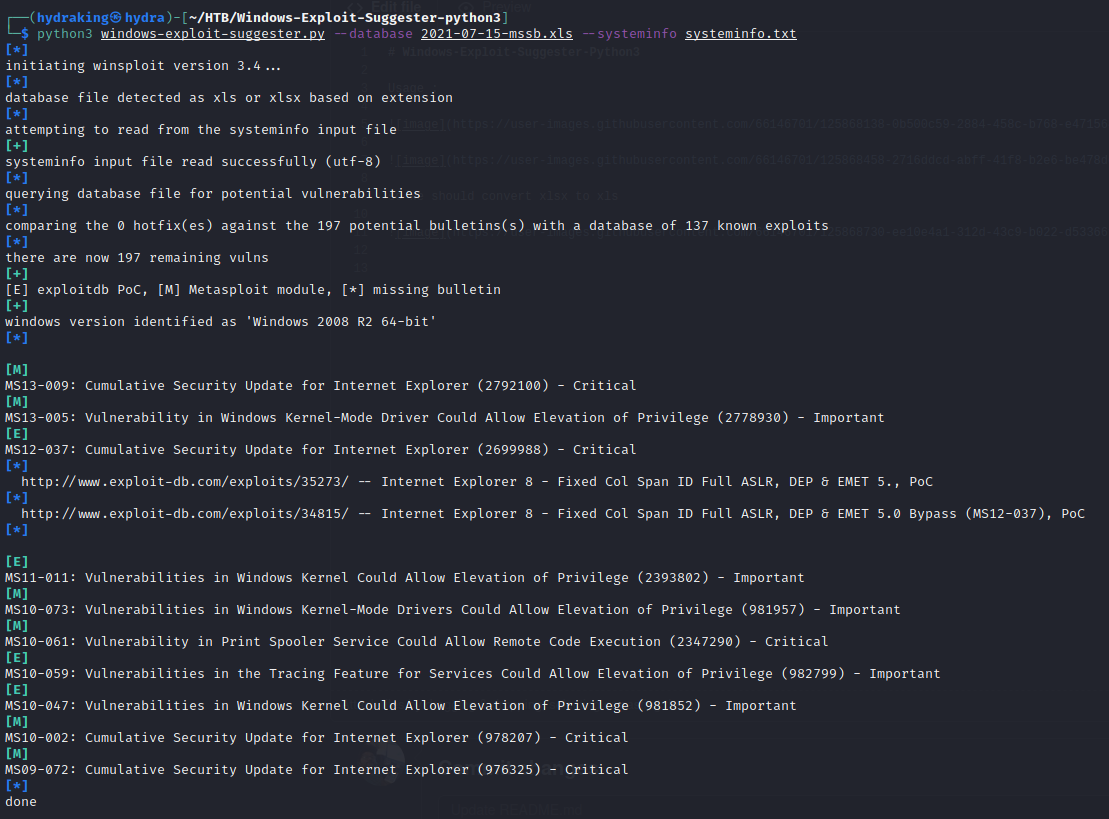 h3x0v3rl0rd/windows-exploit-suggester-python3
Python-based cross-referencing tool: uses Windows systeminfo and MS security bulletins to detect unpatched vulnerabilities and suggest privilege…
 hika-sec/terminator_killer
Kernel-mode process killer exploiting CVE-2026-0828 (BYOVD) to terminate protected processes via a vulnerable signed driver, bypassing PPL and…
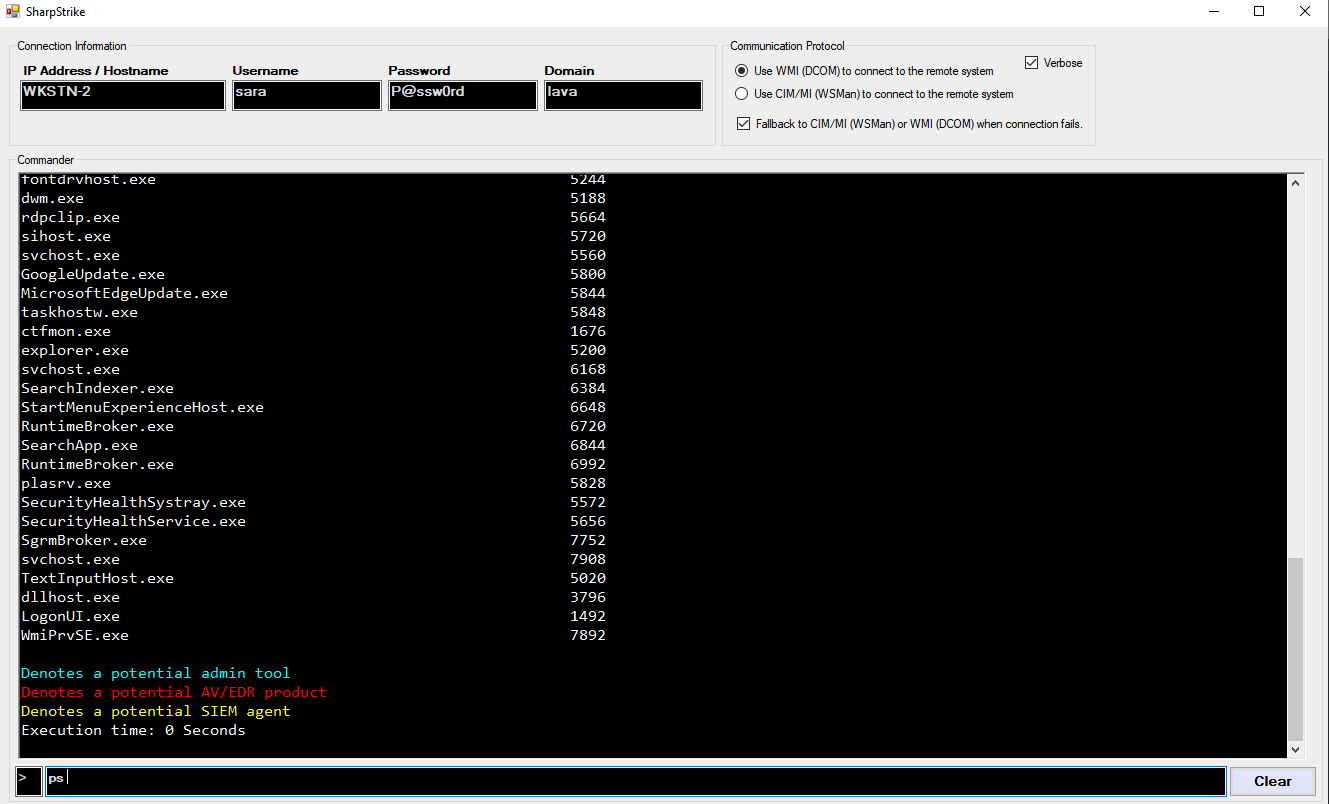 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 obscura-cert/cve-2025-33073
Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…
 h4wkst3r/scmkit
Source Code Management Attack Toolkit
 xforcered/scmkit
Source Code Management Attack Toolkit
 abstractclass/cloudprivs
Determine privileges from cloud credentials via brute-force testing.
 skiller9090/lucifer
A Powerful Penetration Tool For Automating Penetration Tasks Such As Local Privilege Escalation, Enumeration, Exfiltration and More... Use Or Build…
 xaitax/totalrecall
This tool extracts and displays data from the Recall feature in Windows 11, providing an easy way to access information about your PC's activity…