BADministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…

Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…

Check-LocalAdminHash is a PowerShell tool that attempts to authenticate to multiple hosts over either WMI or SMB using a password hash to determine…

This tool extracts and displays data from the Recall feature in Windows 11, providing an easy way to access information about your PC's activity…

Wonka is a sweet Windows tool that extracts Kerberos tickets from the Local Security Authority (LSA) cache. Like finding a ticket, but for security…

The Inspector tool is a privilege escalation helper (PoC), easy to deployed on web server, this tool can list process running with root, check kernel…

Low-observability Active Directory security enumeration tool using native ADSI/COM interfaces. Enumerates ACLs, delegation, trusts, ADCS, Kerberoast…

This C# tool sprays for admin access over the entire domain

Windows offline filesystem hacking tool for Linux

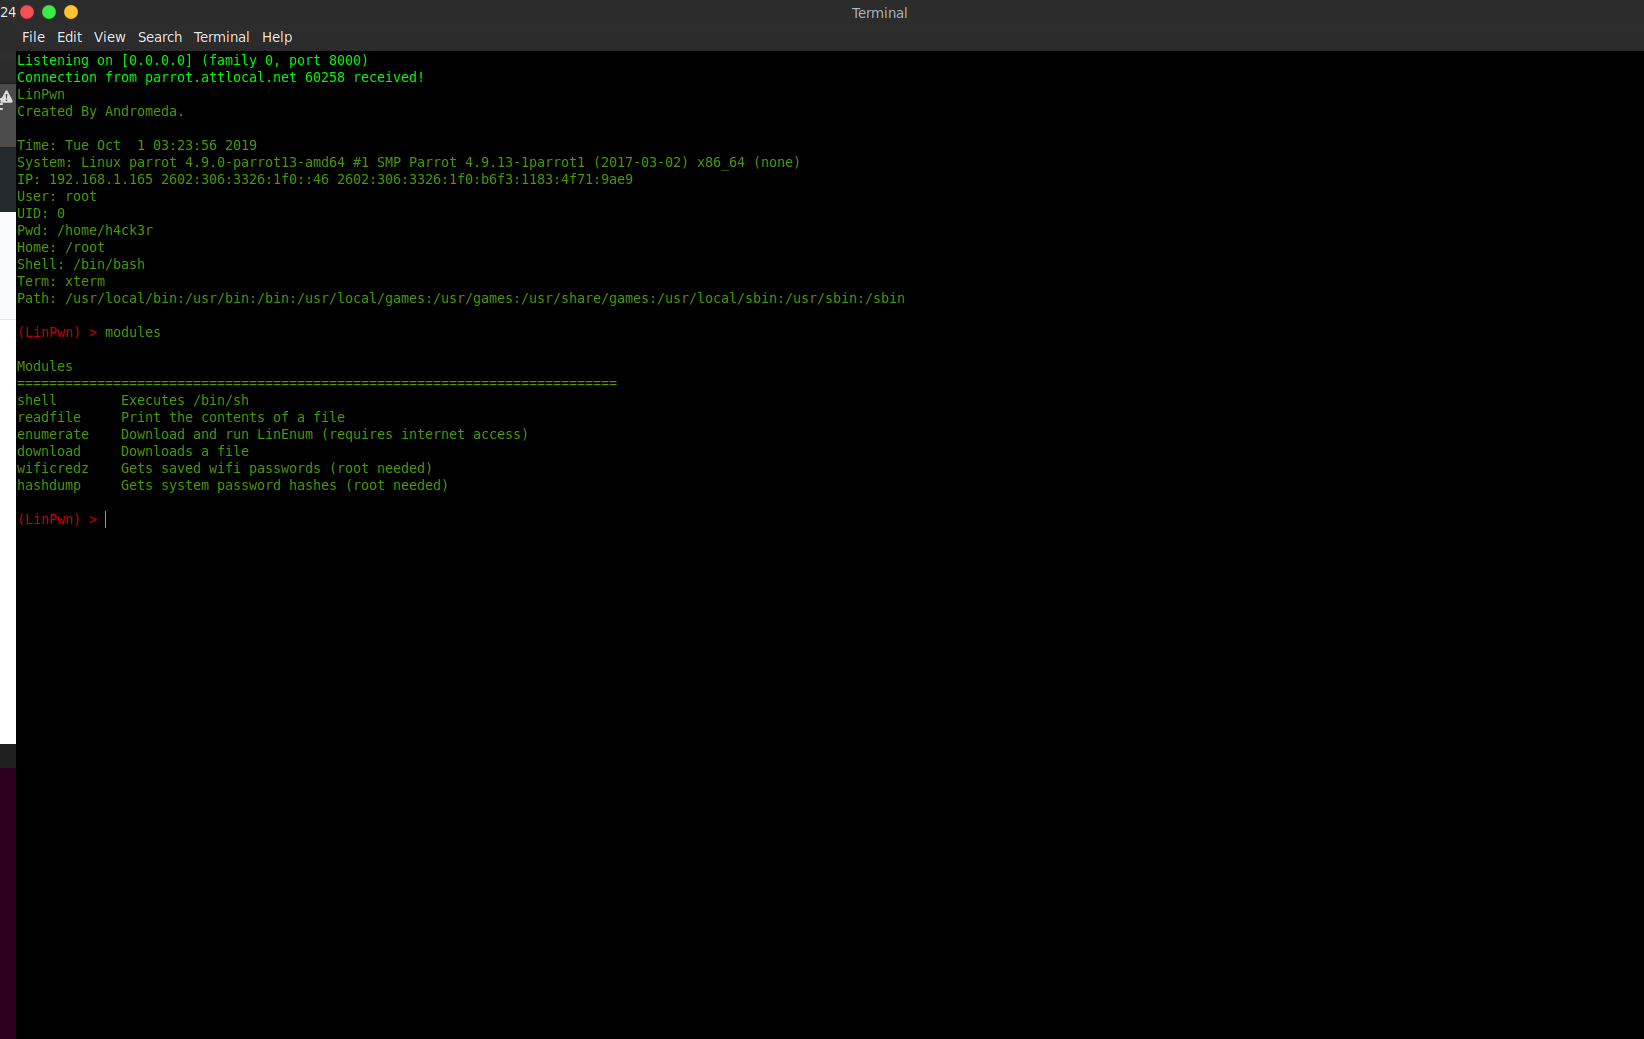
Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.

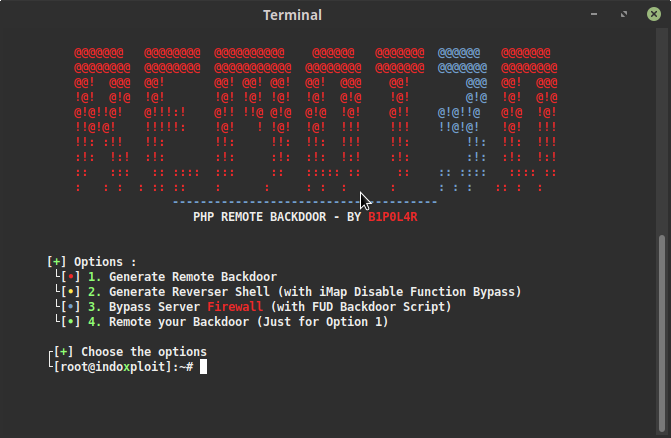
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…

Updated version for the tool UltraRealy with support of the CVE-2019-1040 exploit

Nerv0us r4bbit - Post Exploitation Windows Enumeration Tool

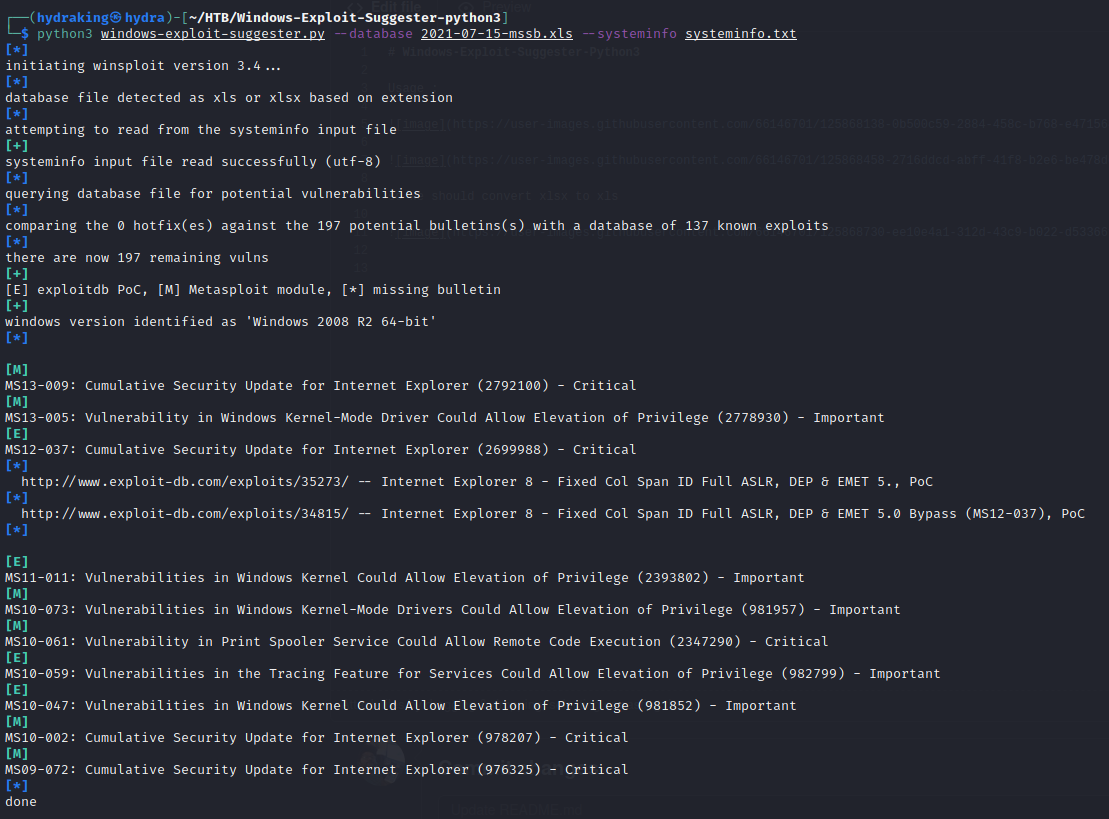
Python-based cross-referencing tool: uses Windows systeminfo and MS security bulletins to detect unpatched vulnerabilities and suggest privilege…

A PoC tool designed to enhance the effectiveness of your traps by spreading breadcrumbs & honeytokens across your systems to lure the attacker toward…

Windows Exploit Suggester - Next Generation

Monitor linux processes without root permissions

Active Directory ACL exploitation with BloodHound

Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.