CVE-2025-32463_exploit

Local privilege escalation exploit for sudo 1.9.14-1.9.17 that abuses CVE-2025-32463 chroot handling, planting a malicious NSS library constructor to…

Local privilege escalation exploit for sudo 1.9.14-1.9.17 that abuses CVE-2025-32463 chroot handling, planting a malicious NSS library constructor to…

Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence

Code sample for using exploit CVE-2019-5736 to mine bitcoin with no association to original container or user.

Proof-of-concept exploit for CVE-2024-27956 SQL injection in ValvePress Automatic plugin. Creates admin users in WordPress to achieve remote code…

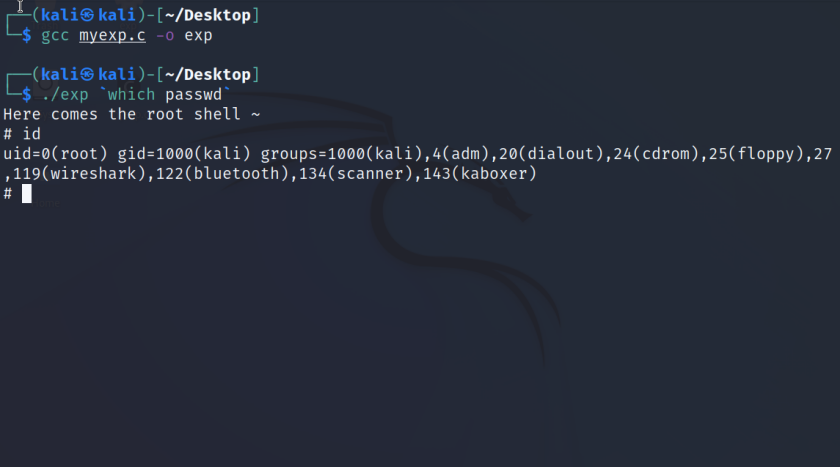
exp of CVE-2022-0847

Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…

Windows privilege escalation exploit that plants SprintCSP.dll in a user-writable HKLM PATH directory to hijack StorSvc and execute as SYSTEM.

Rust POC for CVE-2018-1932X kernel driver vulnerabilities

Full-chain CVE-2025-57819 PoC for FreePBX 15, 16, and 17: unauthenticated SQLi to RCE and root takeover.

Exploit PoC for CVE-2026-31431 that uses AF_ALG and splice() to overwrite Linux page cache and patch /usr/bin/su in memory, escalating unprivileged…

A simple exploit that uses dirtypipe to inject shellcode into runC entrypoint to implement container escapes.

An elevation of privilege vulnerability exists when the Windows Print Spooler service improperly allows arbitrary writing to the file system, aka…

Proof-of-concept exploit for CVE-2026-63030, a pre-authentication vulnerability in WordPress (versions 6.9.0 through 7.0.1).

Copy Fail - CVE-2026-31431 - Hardened C implementation for redteam and authorized penetration testing operations. ⚠️ Legal Notice: This tool is…

A version of CVE-2017-0213 that I plan to use with an Empire stager

Local privilege escalation exploit for CVE-2021-1732 targeting Windows 10 and Server versions, with PoC code and affected system enumeration.

Working PowerShell POC

Proof-of-concept exploit for Mailcow CVE-2022-31138 enabling RCE via perl code injection in Sync Job regex fields, with privilege escalation to…