
adPEAS
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
authenticationexploitationinformation-gathering+6
61106960/adpeasPowershell tool to automate Active Directory enumeration.
 abraxas/cve-2026-11387-woocommerce-sms-otp
SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress; SMS Alert <3.9.6; Unauthenticated Privilege Escalation…
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
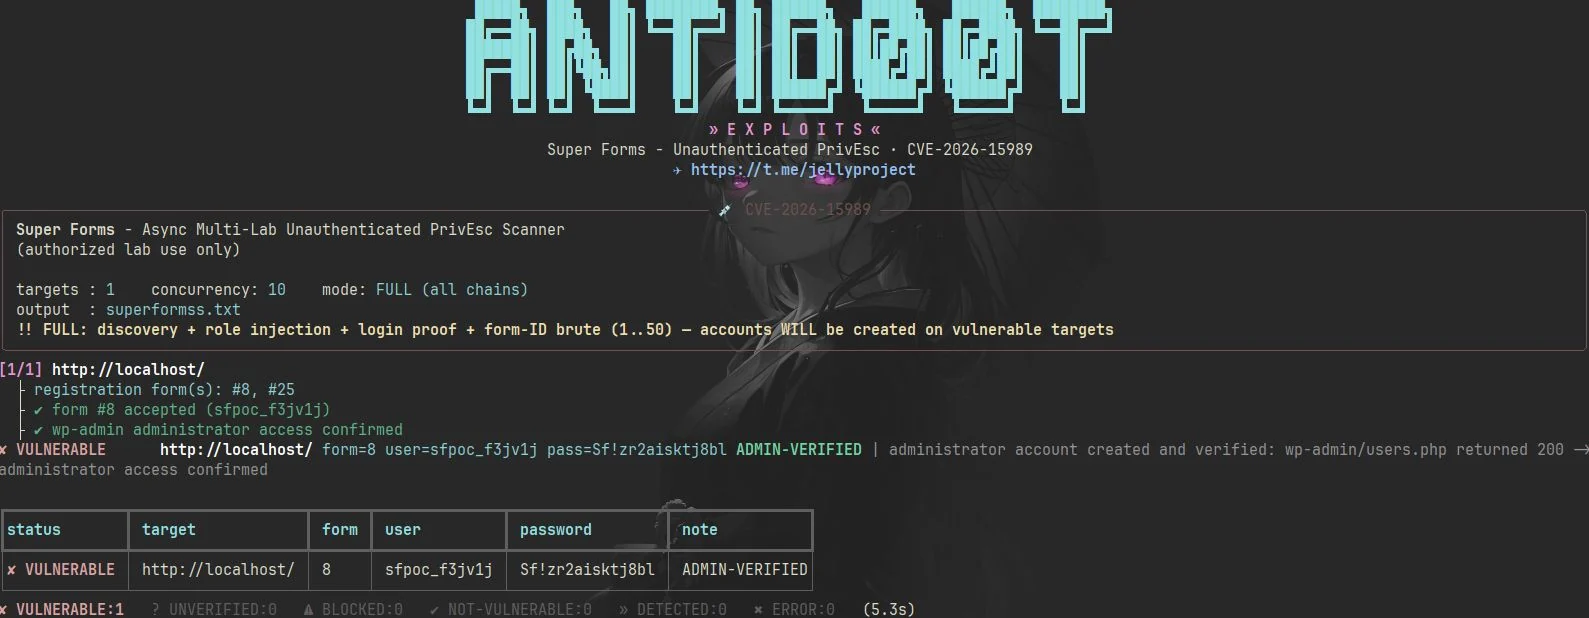 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
 pshlyundin/ldap_shell
Interactive shell for Active Directory enumeration and ACL abuse via LDAP/LDAPS. Supports DCSync, RBCD, Shadow Credentials, password changes, and…
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
 oxstussz-eng/kerberos-cve-2026-27912
PoC for CVE-2026-27912 - Windows Kerberos Elevation of Privilege (ResetNightmare). Unauthorized password reset via Kerberos flaw. For security…
 blacksnufkin/axhunter
PoCs for Wellbia XIGNCODE3 anti-cheat xhunter driver family - xhunter1.sys v2023.12.7.78 and xhunter2.sys v2026.6.1.192 (CVE-2026-15430,…
 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 redteambrasil/cve-2020-24028
PoC for CVE-2020-24028: privilege escalation via authenticated permission bypass in ForLogic Qualiex, allowing user creation and password changes.
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 mmoobbeeiidat-design/hack-the-box-enigma-findings-report
HTB_Enigma Security Assessment – Full pentest completed, chaining NFS disclosure, IMAPS password reuse, and OS Command Injection in OpenSTAManager…
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 ubaydev/cve-2026-11551-poc
Proof-of-concept exploit for CVE-2026-11551, an unauthenticated privilege escalation vulnerability in the Branda White Label plugin for WordPress,…