
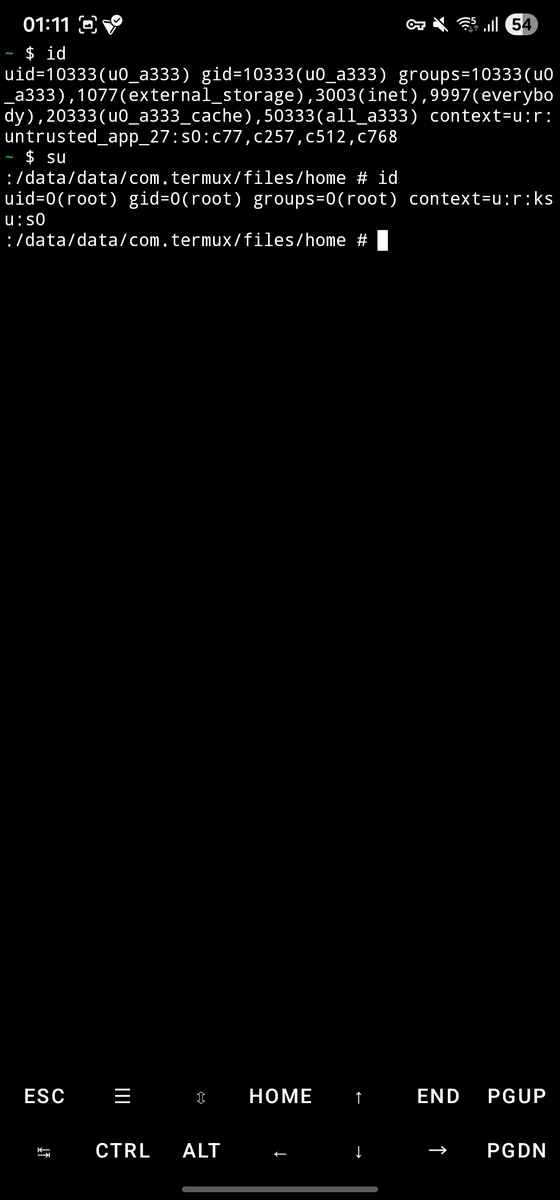
IonStack-S22U
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
android-securitybinary-exploitationexploitation+3
99
sarabpal-dev/ionstack-s22uCVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 kurtulusakyuz/ionstack_s21
Exploit chain research targeting CVE-2026-43499 on Samsung Galaxy S21
 fusiondrive/cve-2026-43499-s24u
CVE-2026-43499 research port for Galaxy S24 Ultra SM-S928U1 DZF2 (COMPLETED)
 khush-613/cve-2026-34990-poc
Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 pirosap/aquos-r7-ghostlock
Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.
 anksgls-sj/-help-vivo-y200i-5.10.218-gki-cve-2026-43499-stack-reclaim-reaches-0x300-need-0x318
Research notes and PoC development for CVE-2026-43499 (GhostLock) kernel UAF on vivo Y200i Android 14, covering futex PI-chain stack-reclaim…
 mouseos/aquos-r6-ghostlock
Temporary root exploit for Sharp AQUOS R6 A101SH S0029 using GhostLock CVE-2026-43499
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
 zhubaohe123/ghostlock-kit
One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.
 416rehman/razer-lycosa-kernel-lpe-byovd-vulnerability-poc
Two kernel vulnerabilities in Razer Lycosa.sys (CWE-125 memory disclosure + CWE-121 stack overflow) chained to local privilege escalation.…
 kemrec/cve-2025-0324-axis-vapix-privesc
Root-cause analysis and safety-gated verification tool for CVE-2025-0324, a privilege-escalation flaw in AXIS OS VAPIX allowing any authenticated…
 cypherhippie/cve-2026-66804
Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.
 rat5ak/cve-2026-66804-crossdevice-service-eop
CVE-2026-66804 Windows Cross Device virtual camera EoP - Standard user to SYSTEM
 skimask1690/wisedelete
Windows utility that uses the vulnerable WiseDelfile64.sys driver affected by CVE-2025-66680 to enable kernel-assisted file deletion.
 majorjayyy1/cve-2026-0092
CVE-2026-0092- Possible device lock controller bypass due to a missing permission check.