
Boucle-framework
 bande-a-bonnot/boucle-framework
Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.
ai-securityconfiguration-auditingdata-exfiltration+3
124
bande-a-bonnot/boucle-frameworkAutonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 kikiuuw/cve-2025-68921
Analyze and demonstrate the local privilege escalation vulnerability (CVE-2025-68921) in Nahimic audio software on gaming laptops, with automated…
 coactionbrittlemaidenhair51/cve-2026-42978-poc-research
Exploit and analyze CVE-2026-42978 with a Windows Push Notifications module for AI security, multi-protocol terminal, and autonomous agent suite.
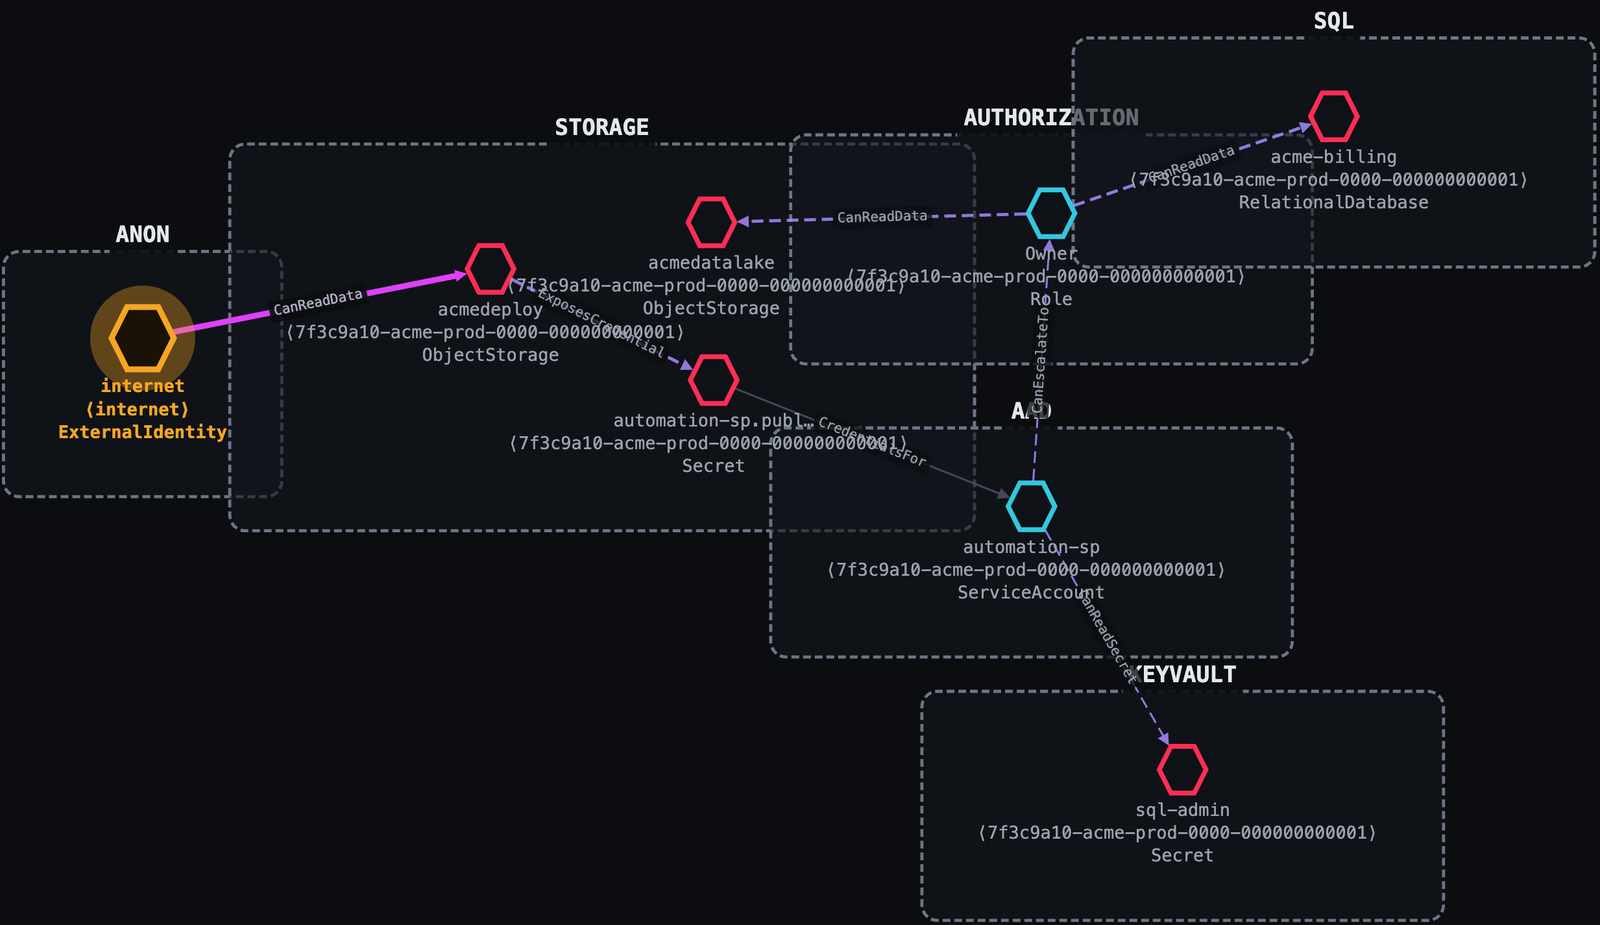 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 nanoturtle1145/root-my-s24
Using CVE-2026-43499 to root your Galaxy S24 Series(SM-S92X0 ,(China / Hong Kong SAR / Taiwan))
 aaron-kidwell/couchpotato
Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
 warpedatom/noisehound
Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
 begitdj/cve-2019-2215-markw
Exploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 gopartner/realme-c53-unlock-root
Bootloader unlock (CVE-2022-38694) & root guide for Realme C53 / RMX3760 (Unisoc T612)
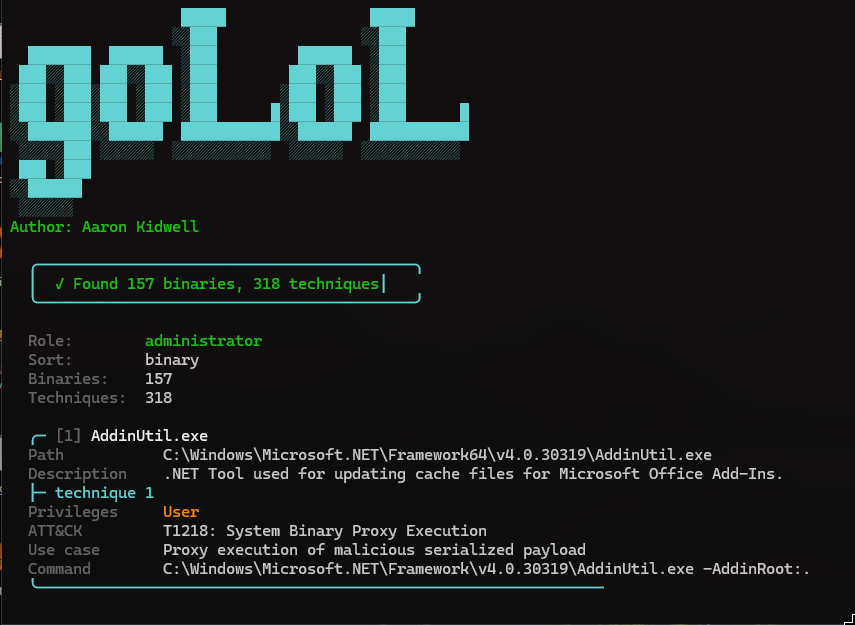 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
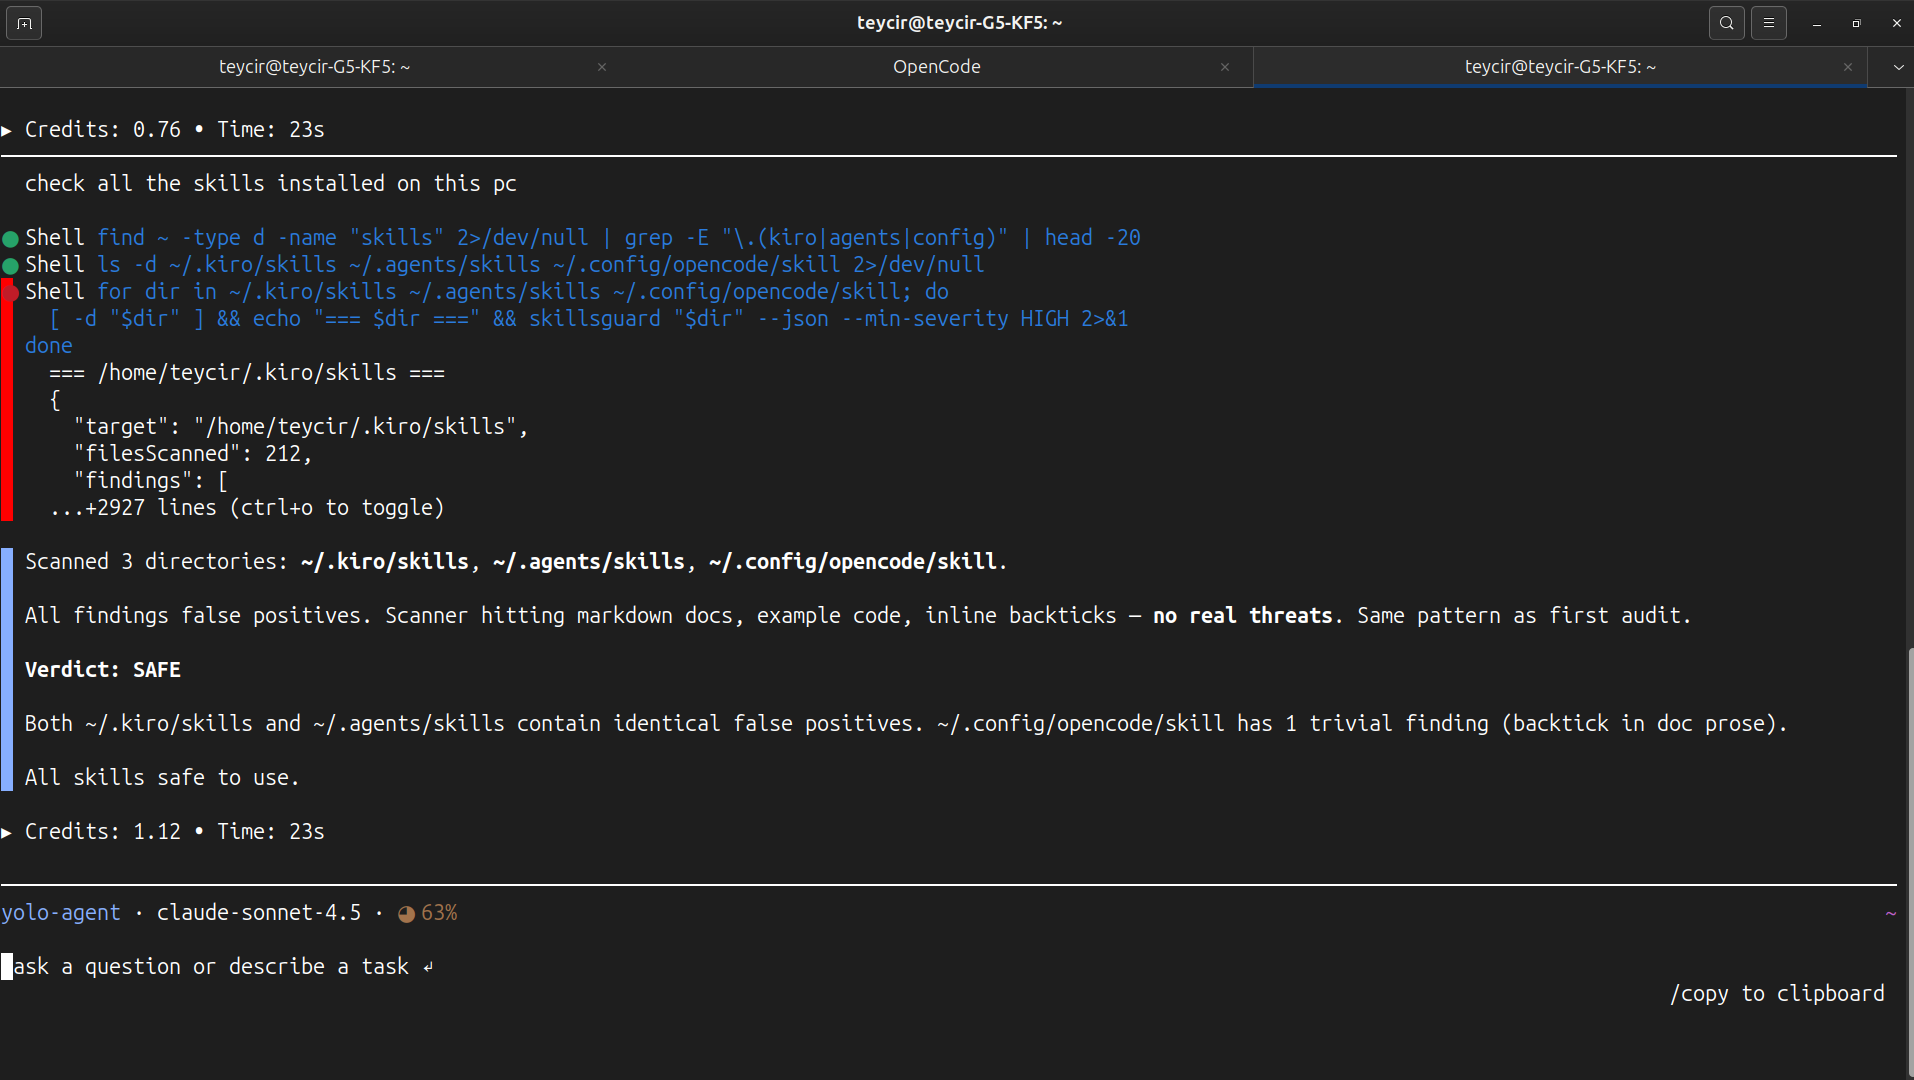 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
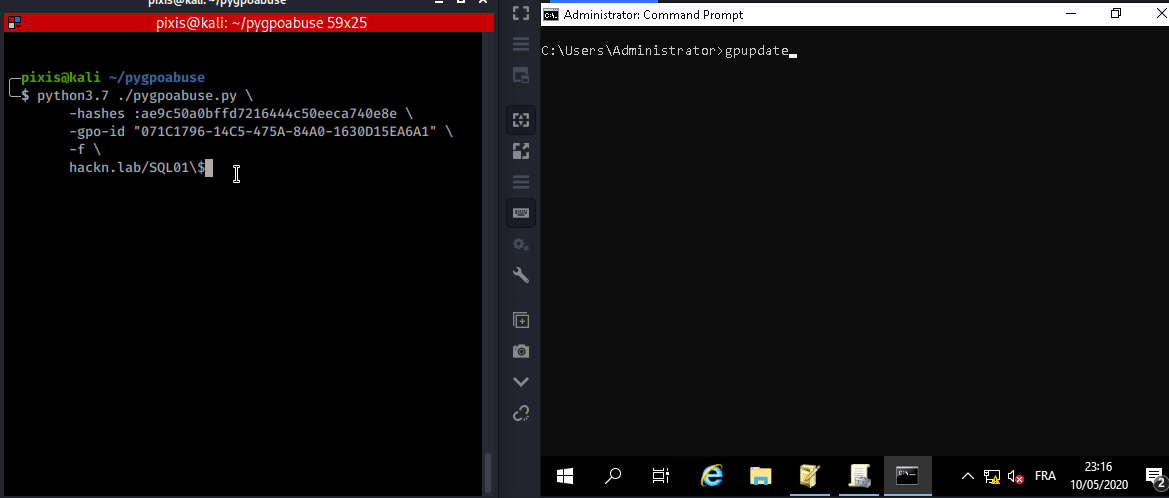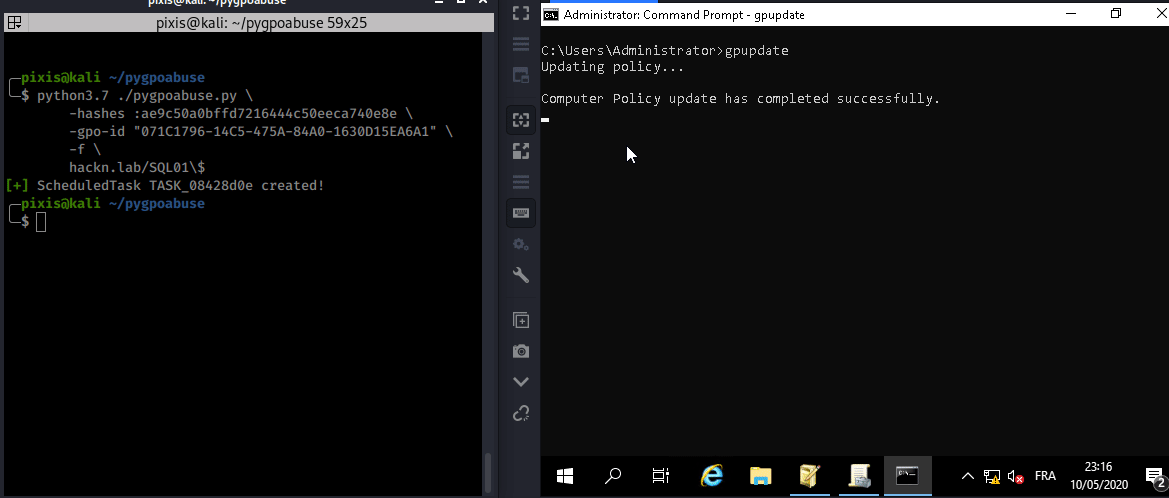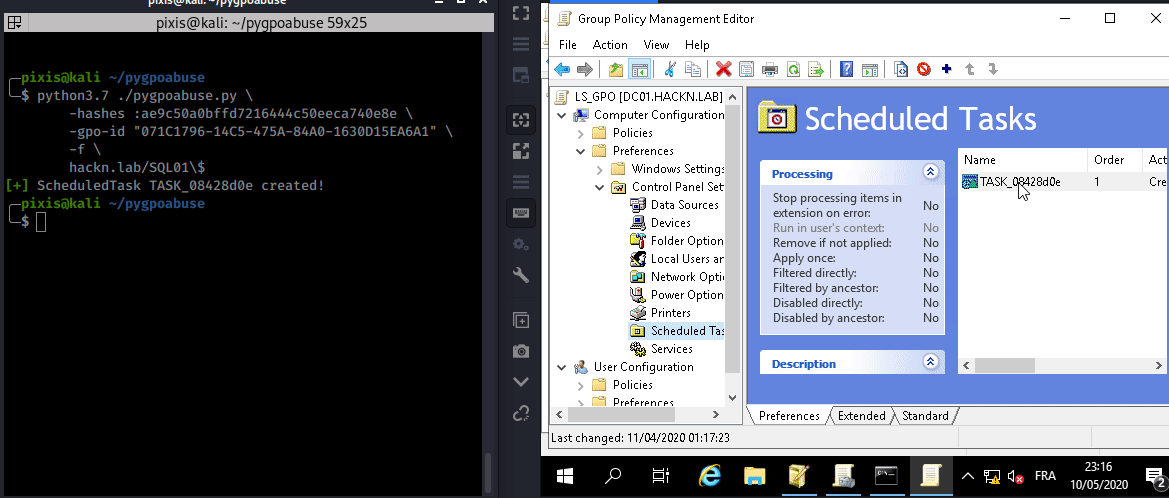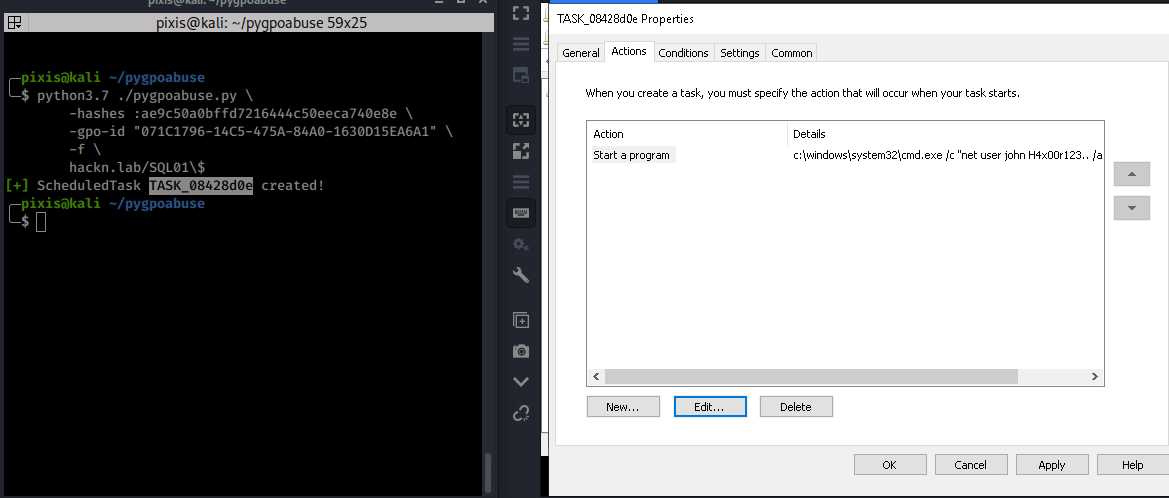 hackndo/pygpoabuse
Partial python implementation of SharpGPOAbuse
 fuzzlove/sparstanboogie
Exploit chain utilizing directory traversal and iOS restore to overwrite protected files.
 bsauce/kernel-exploit-factory
Linux kernel CVE exploit analysis report and relative debug environment. You don't need to compile Linux kernel and configure your environment…