
couchdb-exploit
 darabium/couchdb-exploit
Exploits CouchDB CVE-2017-12635/12636 for privilege escalation and RCE, then provides an interactive shell with command execution, database browsing,…
exploitationinformation-gatheringpenetration-testing+4
darabium/couchdb-exploitExploits CouchDB CVE-2017-12635/12636 for privilege escalation and RCE, then provides an interactive shell with command execution, database browsing,…
 sweatyrocket/huawei-p10-cve-2017-8890-unlock
Huawei P10 VTR-L29C432B151 CVE-2017-8890 exploit research and bootloader-unlock journey
 ryan2929/cve-2026-31431
Public exploit for a Linux kernel zero-day (CVE-2026-31431) enabling local privilege escalation to root on distributions since 2017. Includes a…
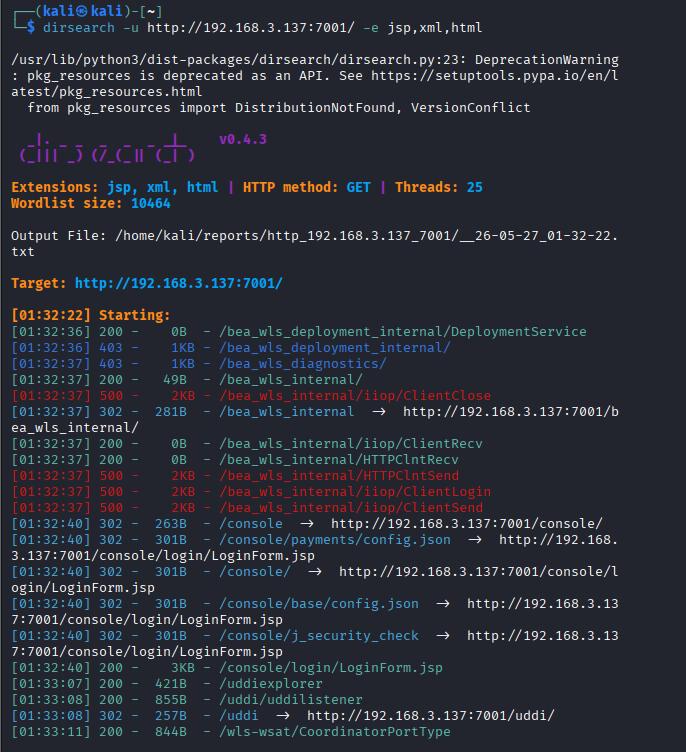 dungsocool/cve-2017-10271
Step-by-step lab guide for exploiting CVE-2017-10271 (WebLogic XMLDecoder deserialization RCE) with manual payload construction, blind RCE bypass,…
 ochebotar/copy-fail-cve-2026-31431-detection-probe
Safe detection tooling for CVE-2026-31431 "Copy Fail" and CVE-2026-43284 "Dirty Frag" — a local privilege escalation in the Linux kernel's algif_aead…
 xd20111/cve-2026-43284
Deterministic Linux kernel local privilege escalation exploit chaining two page-cache write primitives (xfrm/ESP and RxRPC) for reliable root access…
 sebastian294/cve-2026-31431
Analísis - POC - Mitigación
 rvzsec/cve-2026-31431
PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros…
 ozergoker/cve-2026-31431-copy-fail
Exploit for CVE-2026-31431: a 732-byte Python script that exploits a straight-line logic flaw to gain root on all Linux distributions since 2017.
 silent0x0/copy-fail---cve-2026-31431
CVE-2026-31431 "Copy Fail" - Analysis and defensive research for the Linux kernel AF_ALG privilege escalation vulnerability affecting all major…
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 wuzuowei/copy-fail-cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root and container escape via AF_ALG and…
 zephrfish/copyfail-cve-2026-31431
Linux kernel LPE exploit (CVE-2026-31431) using AF_ALG + splice to overwrite setuid-binary page cache for root. No race conditions, works on all…
 painoob/copy-fail-exploit-cve-2026-31431
Most Linux LPEs need a race window or a kernel-specific offset. Copy Fail is a straight-line logic flaw, it needs neither. The same 732-byte Python…
 spydomain/cve-2017-1000112-poc
Exploit for CVE-2017-1000112, a buffer overflow in Ubuntu 16.10, providing privilege escalation to root.
 grish-pradhan/cve-2017-7184
Proof-of-concept local privilege escalation exploit for CVE-2017-7184, a Linux kernel XFRM netlink stack overflow. Demonstrates namespace abuse and…
 nabilboudra/cve-2017-5123
Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…