CVE-2019-11707-from-an-IonMonkey-type-confusion-to-SYSTEM-

Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…

Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…

Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.

Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…

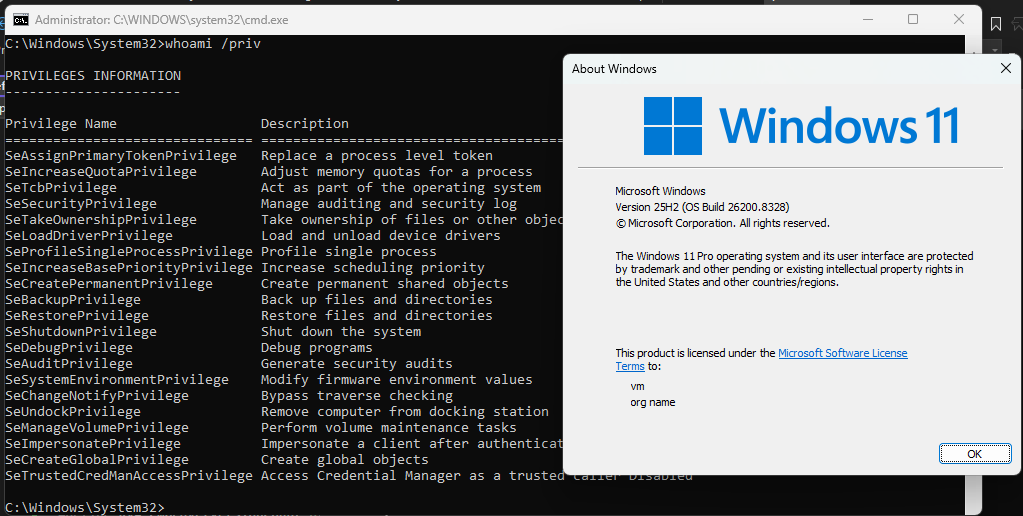
Full exploit code for CVE-2026-40369 - A Windows kernel arbitrary write vulnerability that allows browser sandbox escape from all browsers render…

CVE-2021-21220 Exploitation infrastructure

A tool to transform Chromium browsers into a C2 Implant

Proof-of-concept exploit for CVE-2023-21674, a Windows ALPC vulnerability enabling browser sandbox escape and SYSTEM privilege escalation via kernel…

A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…

Python exploit script for CVE-2020-14321, enabling privilege escalation from teacher to manager in Moodle via cookie-based session hijacking and role…

CVE-2019-1388 Abuse UAC Windows Certificate Dialog

Privilege escalation in QQBrowser