
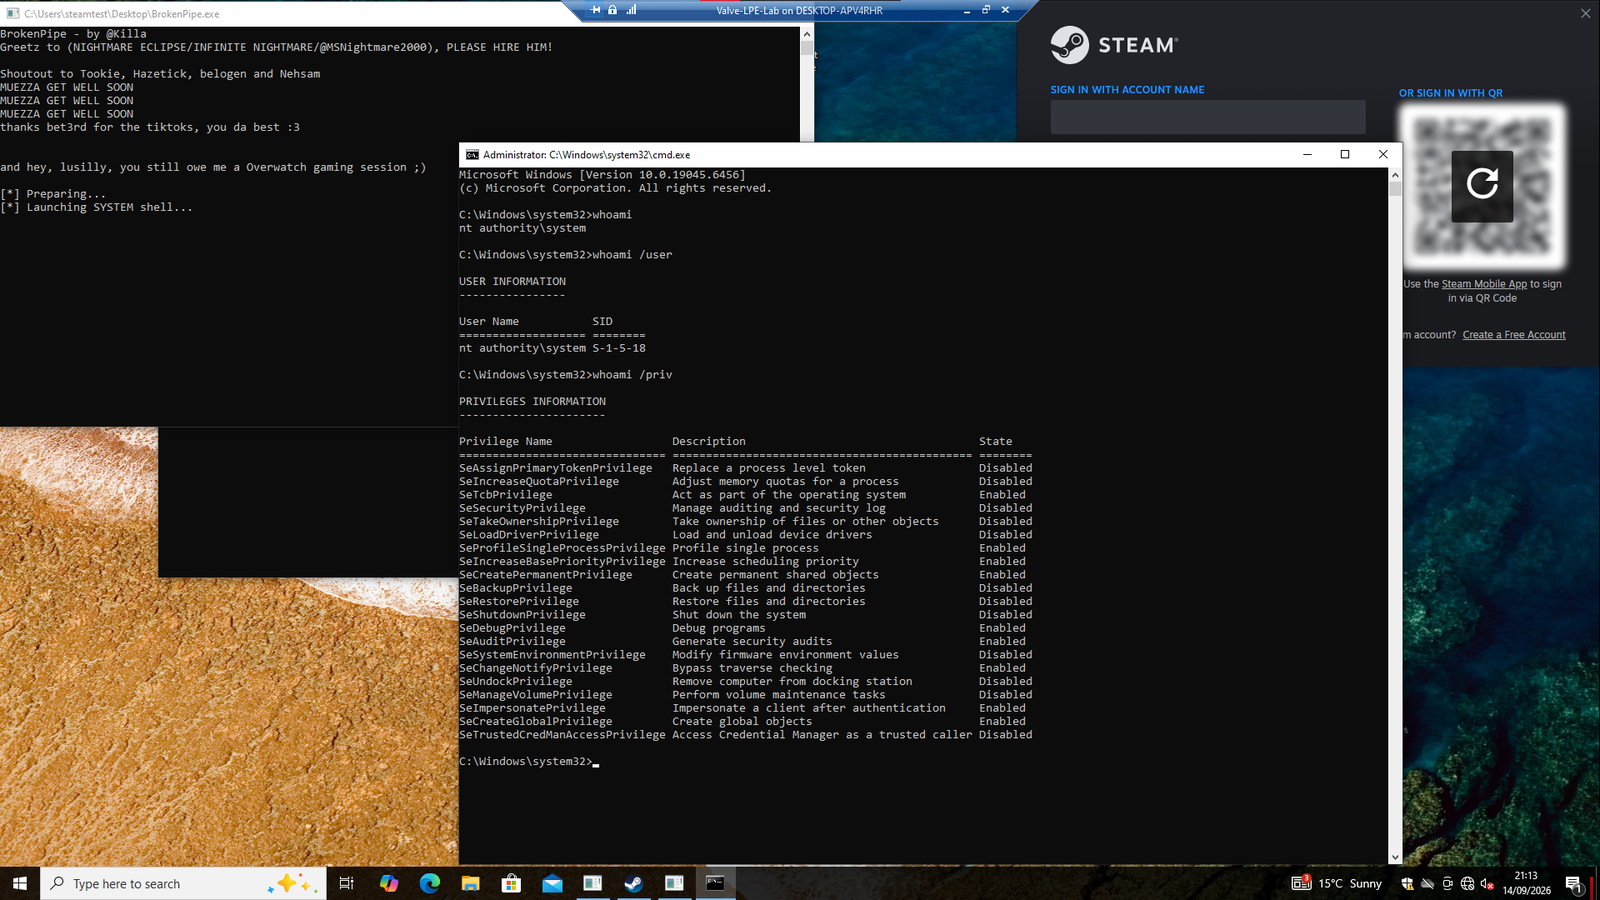
BrokenPipe
 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
exploitationpenetration-testingpost-exploitation+3
159
killaboi/brokenpipeSteam Client Service Local Privilege Escalation Vulnerability


 sentinel-aidefense/cve-2025-33073
CVE-2025-33073 Research writeup
 liamromanis101/cifswitch-check
Detection script for CIFSwitch - CVE-2026-46243
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 jacobtaylor3/c2-and-post-exploitation-framework
CVE-2021-21220 Exploitation infrastructure
 uname1able/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a Windows kernel privilege escalation vulnerability targeting win10_21h2 and win11_23h2 x64 systems with…
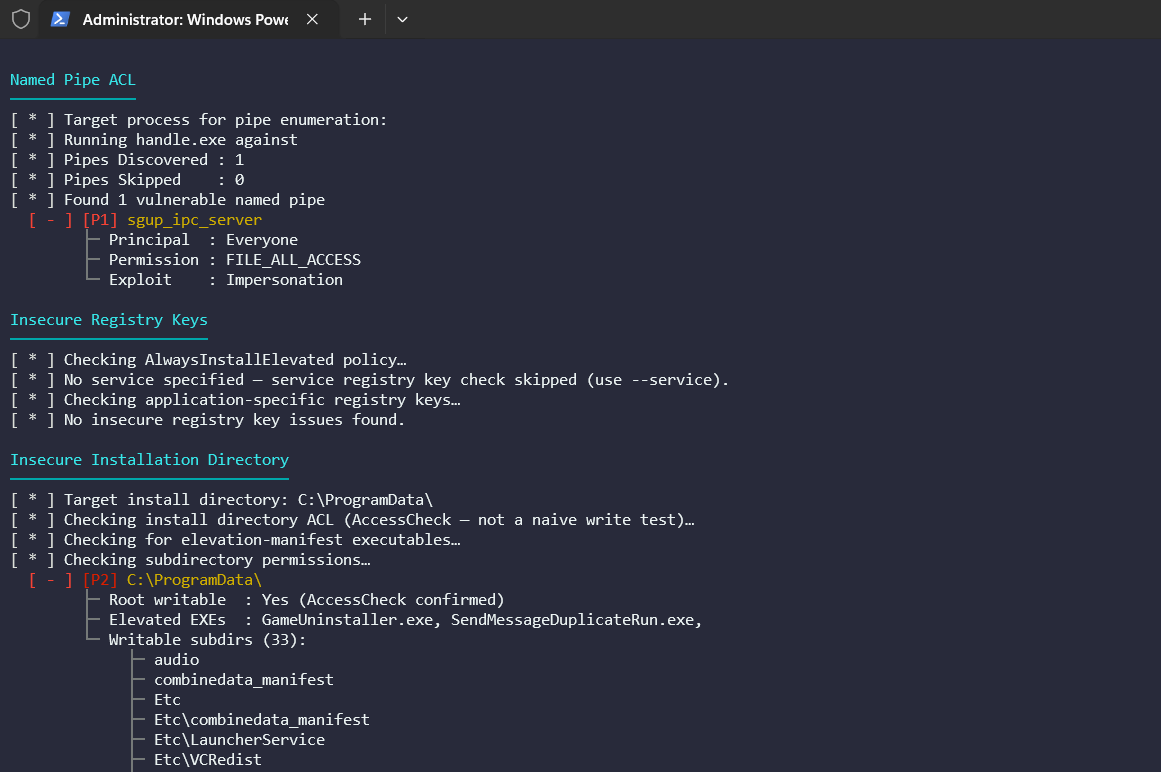 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
 null-event/cve-2024-11467
VMWare Horizon client for macOS LPE due to an XPC logic flaw. Belated POC for an 0-day I responsibly disclosed to Omnissa.
 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
 x0rbeexd/cve-2020-5752
Local Priviledge Escalation for Druva
 sfrdevelopment/windows-smb-vulnerability-framework-cve-2025-33073
Research framework for CVE-2025-33073, a Windows SMB Client privilege escalation vulnerability. Provides malicious SMB server and client exploit…
 wi1dn00b/cve-2024-55968
Exploit POC Code for CVE-2024-55968
 calligraf0/cve-2024-0311
Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…
 apeppels/cve-2022-37017
Bypass for Symantec Endpoint Protection's Client User Interface Password
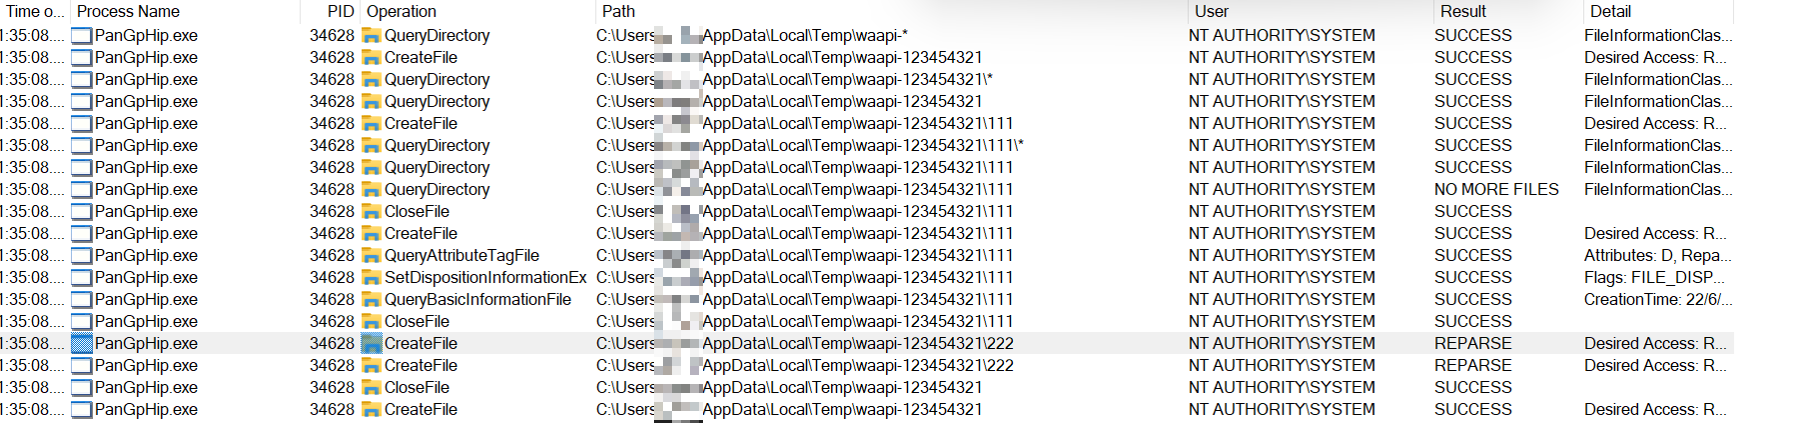 hagrid29/cve-2024-2432-paloalto-globalprotect-eop
Proof-of-concept exploit for CVE-2024-2432 demonstrating local privilege escalation on Windows via arbitrary file delete through symbolic link attack…
 ewilded/cve-2023-7016-poc
POC for the flaw in Thales SafeNet Authentication Client prior to 10.8 R10 on Windows that allows an attacker to execute code at a SYSTEM level via…