

Win10Pcap-Exploit
 rootkitsmm-zz/win10pcap-exploit
Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )
binary-exploitationexploitationpost-exploitation+2
rootkitsmm-zz/win10pcap-exploitExploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )
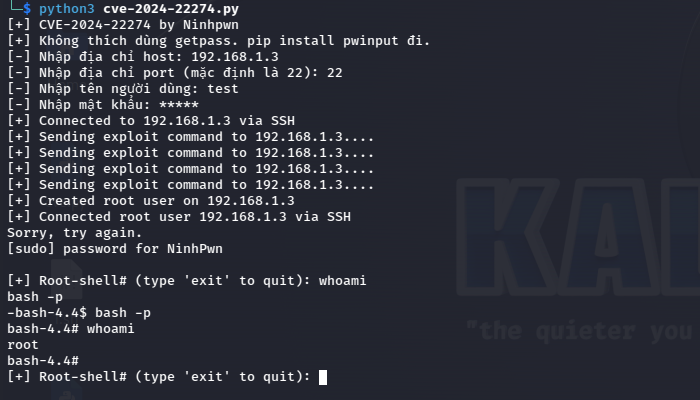 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 sparrowhawk1113/exploit-for-cve-2025-2304
Exploit for CVE-2025-2304
 mrroma577/exploit_cve-2007-2447_again
just remeber how small mistake in santisize username could give yoy root access to the full machine
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 msnightmare/legacyhive
Windows ProfSvc 0day