
CVE-2021-3560
 neonwhiterabbit/cve-2021-3560
One-command Polkit privilege escalation exploit for CVE-2021-3560, creating a passwordless user and switching to root on vulnerable Linux systems.
exploitationpenetration-testingprivilege-escalation+2
3
neonwhiterabbit/cve-2021-3560One-command Polkit privilege escalation exploit for CVE-2021-3560, creating a passwordless user and switching to root on vulnerable Linux systems.
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 dzonerzy/poc-cve-2021-4034
PoC for CVE-2021-4034 dubbed pwnkit
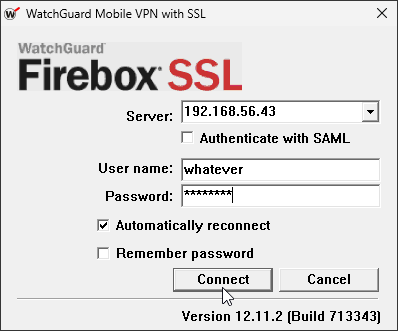 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
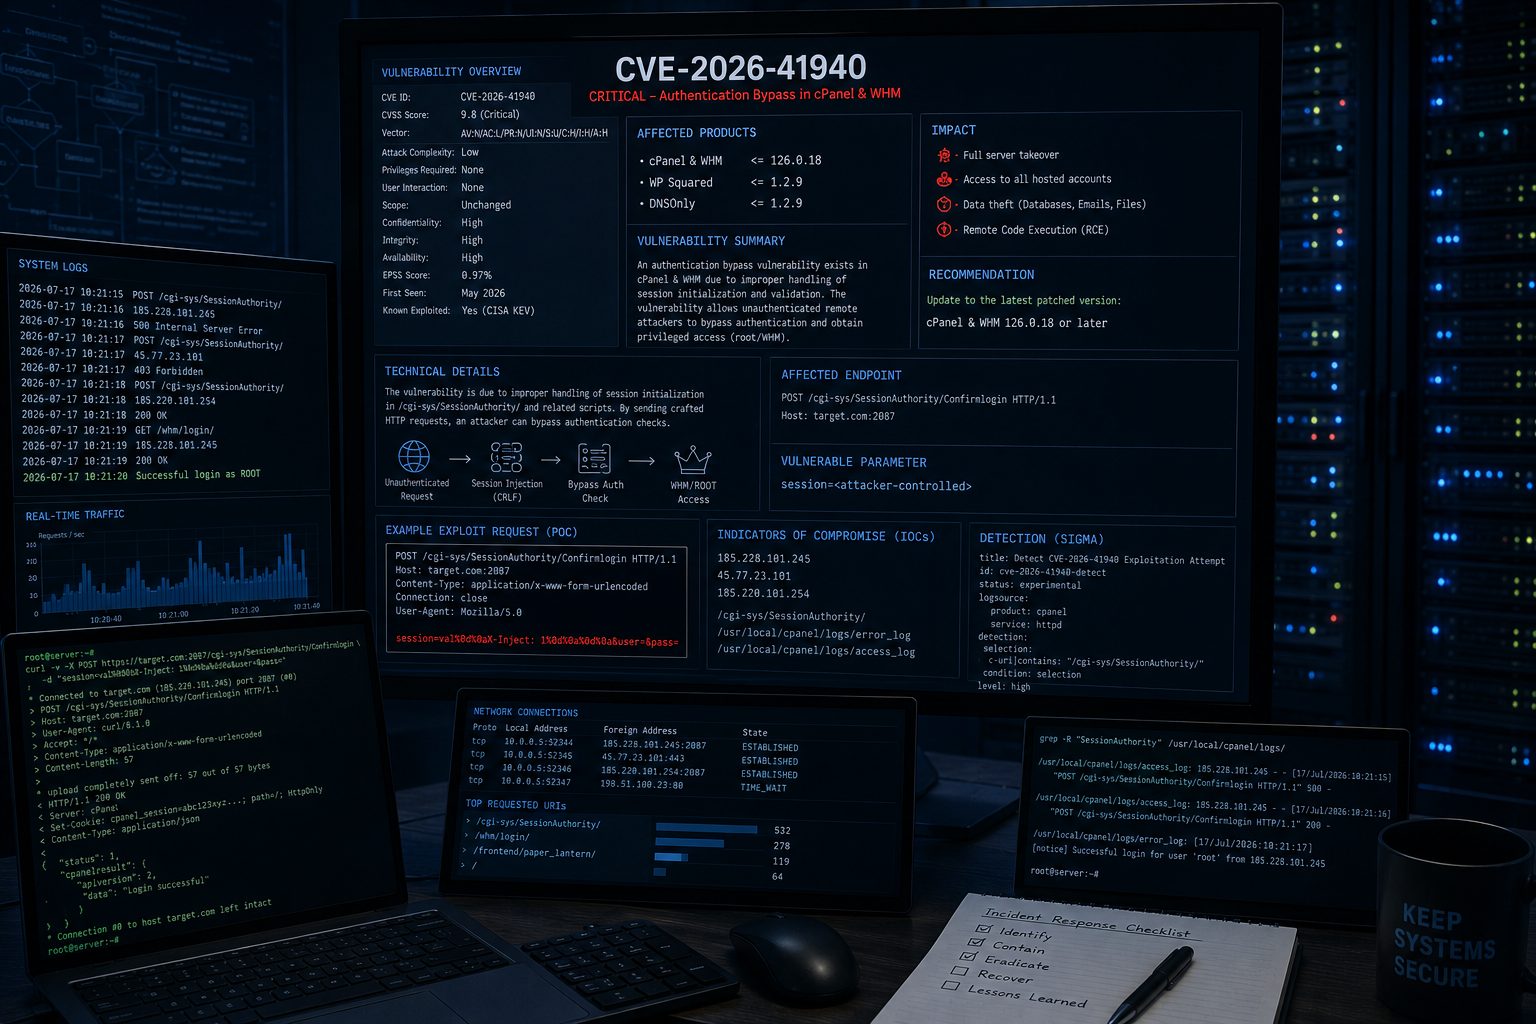 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
 geffner/cve-2020-8289
Proof-of-concept exploit for CVE-2020-8289 demonstrating remote code execution as SYSTEM/root via Backblaze backup client's SSL verification bypass…