
CVE-2026-68121
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
binary-exploitationeducationexploitation+6
0xblackash/cve-2026-68121Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
 0xblackash/cve-2026-80844
Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 wangqian06/cve-2021-3156
Root shell proof-of-concept exploit for CVE-2021-3156 (sudo Baron Samedit) heap-based buffer overflow, enabling local privilege escalation on…
 chrisbarack/cve-2025-55182
Technical penetration testing writeup demonstrating exploitation of CVE-2025-55182 in Next.js, credential harvesting from SQLite, and privilege…
 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…
 kaleth4/cve-2026-21250
Technical documentation and resources for CVE-2026-21250, a Windows HTTP.sys local privilege escalation vulnerability, including affected versions,…
 jesrat/make_me_root
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, enabling privilege escalation on vulnerable…
 h1sok444/cve-2026-25232-poc
Proof of concept for the recent CVE-2026-25232 which is a priv esc vulnerability present in Gogs.
 ciphercloak/cve-2026-41651
Provides technical details and mitigation guidance for the Pack2TheRoot privilege escalation vulnerability (CVE-2026-41651) affecting Linux systems.
 nxploited/cve-2026-18366
Events Manager < 7.4.1 - Unauthenticated Privilege Escalation to Administrator
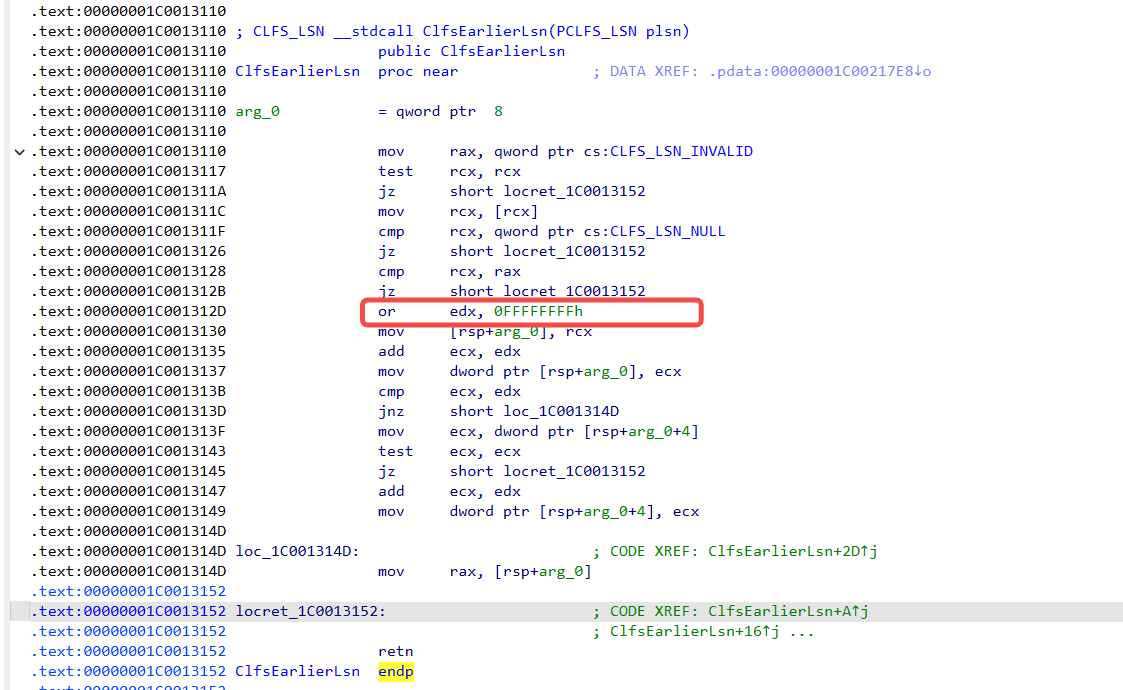 uname1able/cve-2022-24481-analysis
Deep-dive analysis of Windows CLFS type confusion (CVE-2022-24481) with root-cause explanation, exploitation flow, kernel gadget details, and working…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 ascotbe/kernelhub
🌴Linux、macOS、Windows Kernel privilege escalation vulnerability collection, with compilation environment, demo GIF map, vulnerability details,…
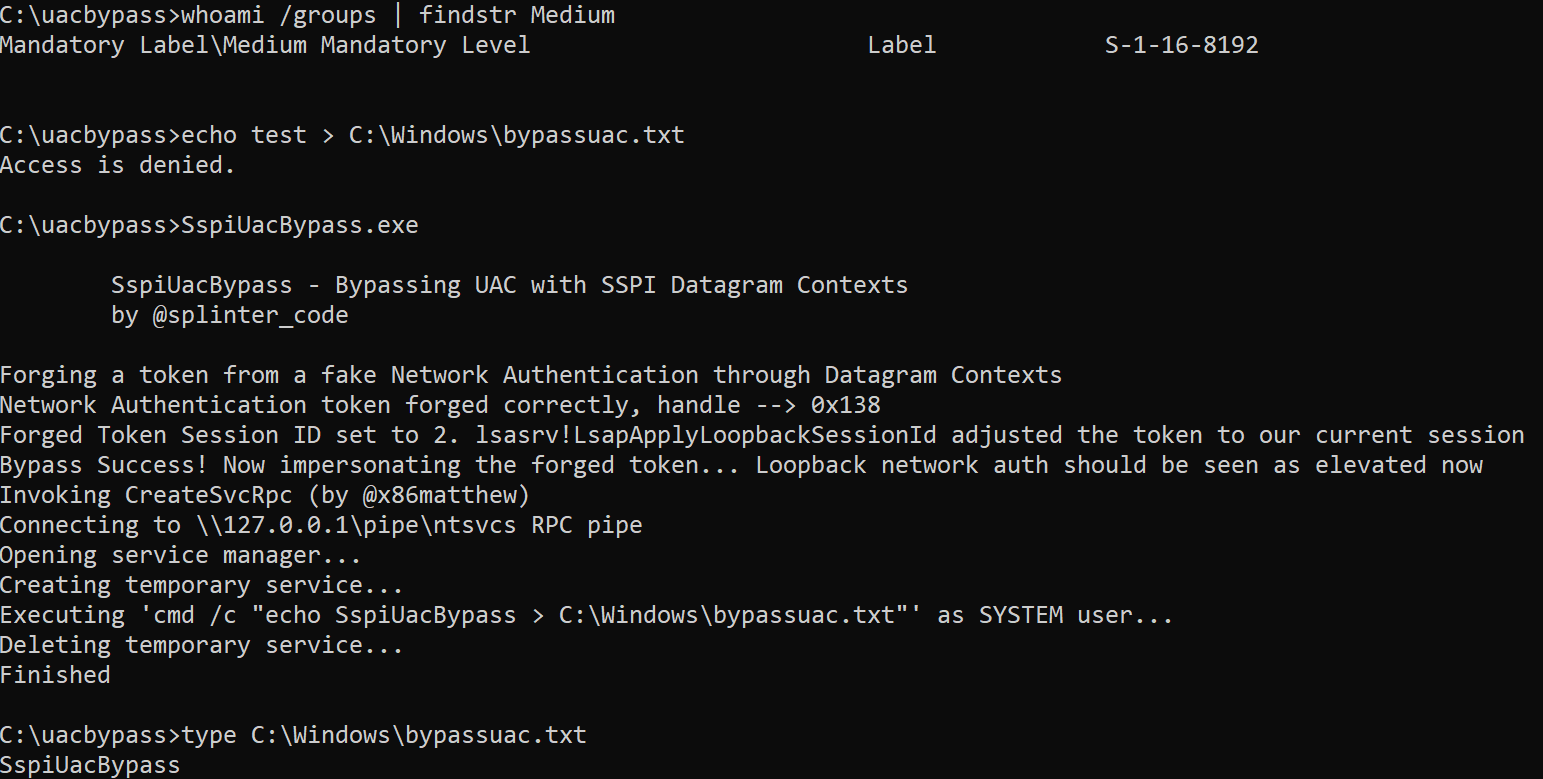 antoniococo/sspiuacbypass
Bypassing UAC with SSPI Datagram Contexts

 h3x0v3rl0rd/dirtyc0w
Exploit for Dirty COW (CVE-2016-5195) enabling local privilege escalation on vulnerable Linux kernels via a race condition in the copy-on-write…