

Oihk-pentesting
 broskigx/oihk-pentesting
Autonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
ai-securityeducationexploit-frameworks+7
4
broskigx/oihk-pentestingAutonomous multi-agent AI penetration-testing engine: a governed tool sandbox, an immutable evidence-and-validation gate, and a reproducible…
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 nanashibx2/bx2-writeups
Cybersecurity writeups, walkthroughs, and technical notes by Nanashi Bx2.
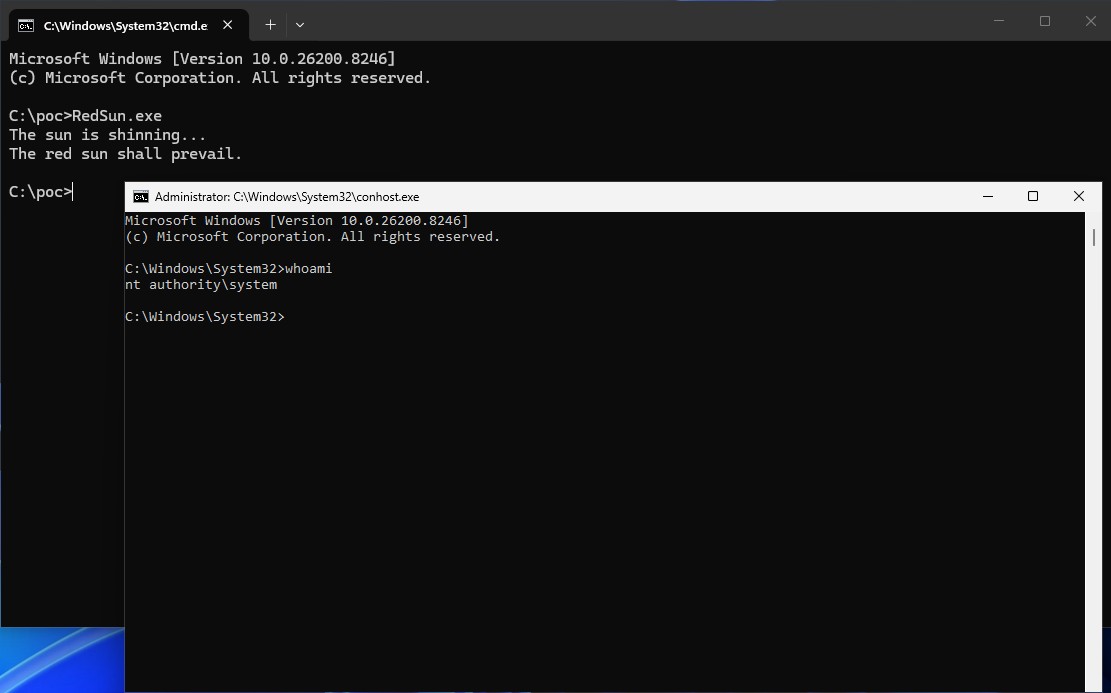 s4m98/redsun-
Windwos Zero Day Local PrivESc Exploit (CVE-2026-41091)
 jsecu/bof-pack-1
A care package of useful bofs for red team engagments
 netbiosx/checklists
Red Teaming & Pentesting checklists for various engagements
 redteamguides/redteamguides.github.io
Red Team Guides
 deepinstinct/nofilter
Abuses Windows Filtering Platform to launch a console as NT AUTHORITY\SYSTEM or impersonate another logged-on user for privilege escalation during…
 hackerhouse-opensource/offensivelua
Offensive Lua.
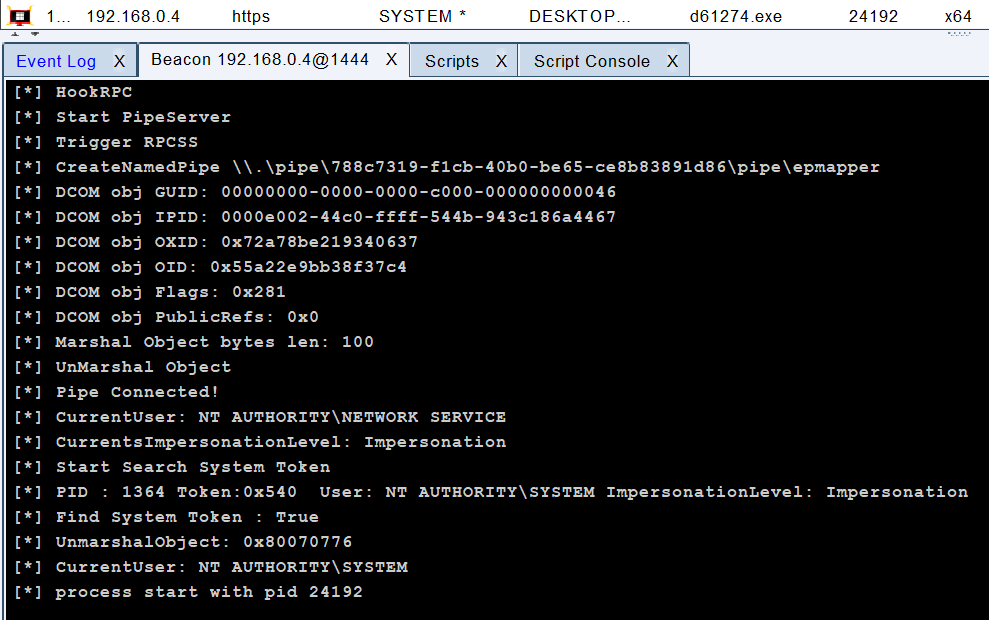 weaselsec/godpotato-aggressor-script
Cobalt Strike Aggressor script that automates Windows service-account-to-SYSTEM privilege escalation via GodPotato during red team operations.
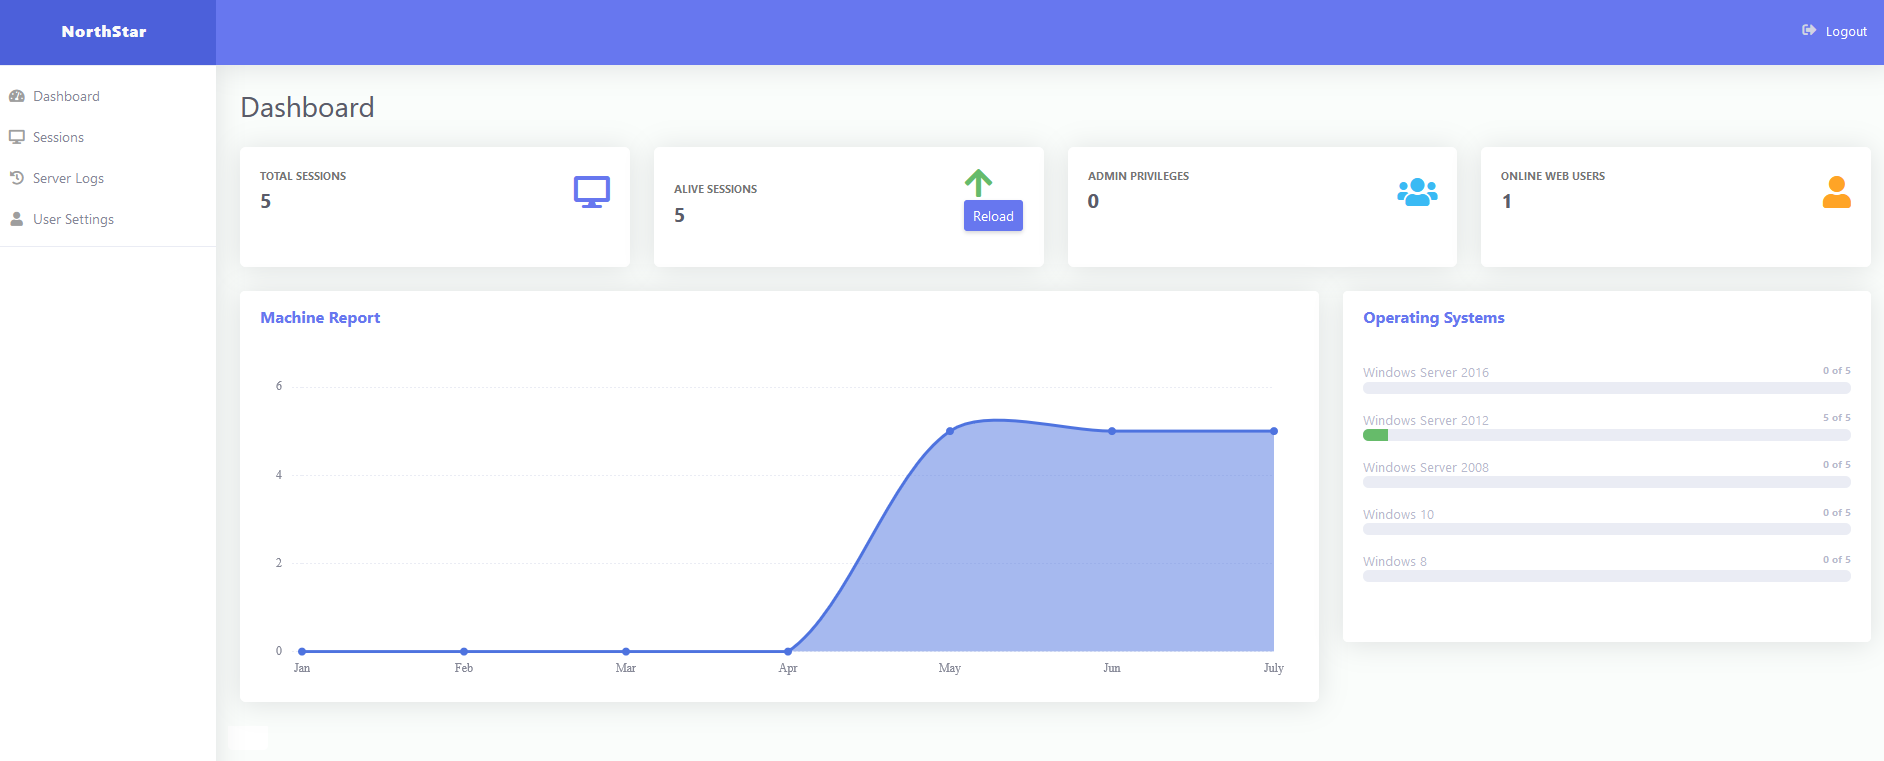 eng1ndes/northstarc2
Web Based Command Control Framework (C2) #C2 #PostExploitation #CommandControl #RedTeam #C2Framework #PHPC2 #.NETMalware #Malware #PHPMalware #CnC…
 pawlokk/mindmanager-poc
public disclosure
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…