

byd-dolphin-hacking
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
android-securitybinary-analysisembedded-systems-security+7
62
wheregoes/byd-dolphin-hackingReverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
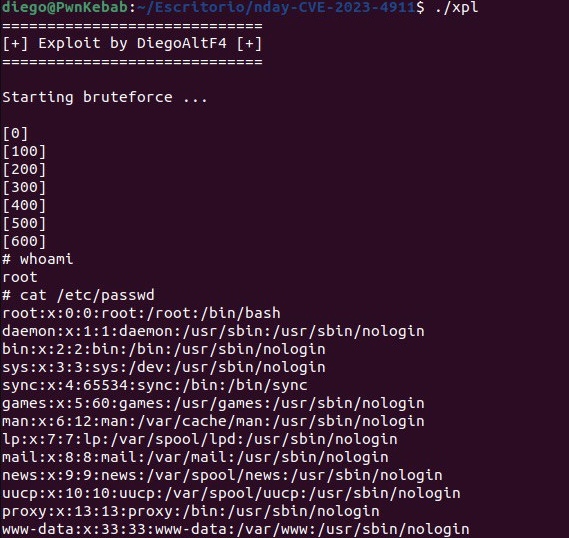 diego-altf4/cve-2023-4911
Proof of concept for CVE-2023-4911 (Looney Tunables) discovered by Qualys Threat Research Unit
 it19083124/snp-assignment
Exploit work Privilege Escalation CVE-2017-1000112
 lionelmusonza/cve-2023-26866
Proof-of-concept exploit for CVE-2023-26866: remote command injection in GreenPacket WR-1200 and OT-235 routers enabling pre-login root-level device…
 initstring/uptux
Linux privilege escalation checks (systemd, dbus, socket fun, etc)