Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

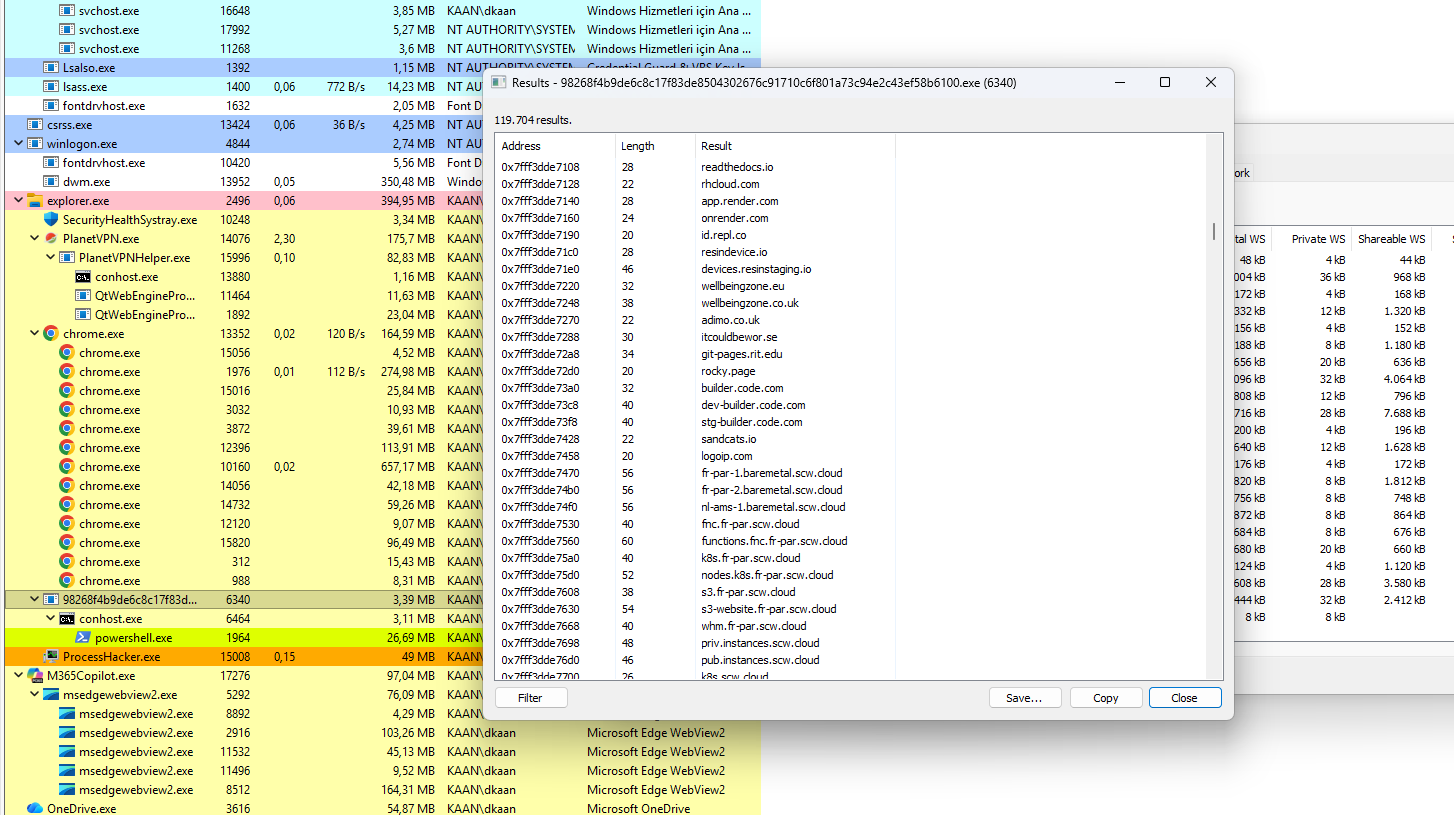
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.

🐐 GoAT (Golang Advanced Trojan) is a trojan that uses Twitter as a C&C server

An exploit for vulnerable versions of fontforge and setuptools plus a practical example.

Exploit for CVE-2024-32002, a Git RCE vulnerability that uses recursive submodule cloning and symlinks to execute arbitrary commands on Windows and…

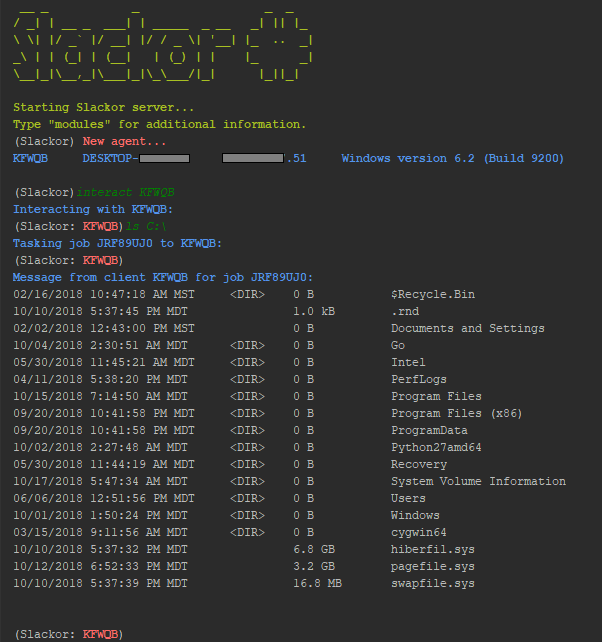
A Golang implant that uses Slack as a command and control server

** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…

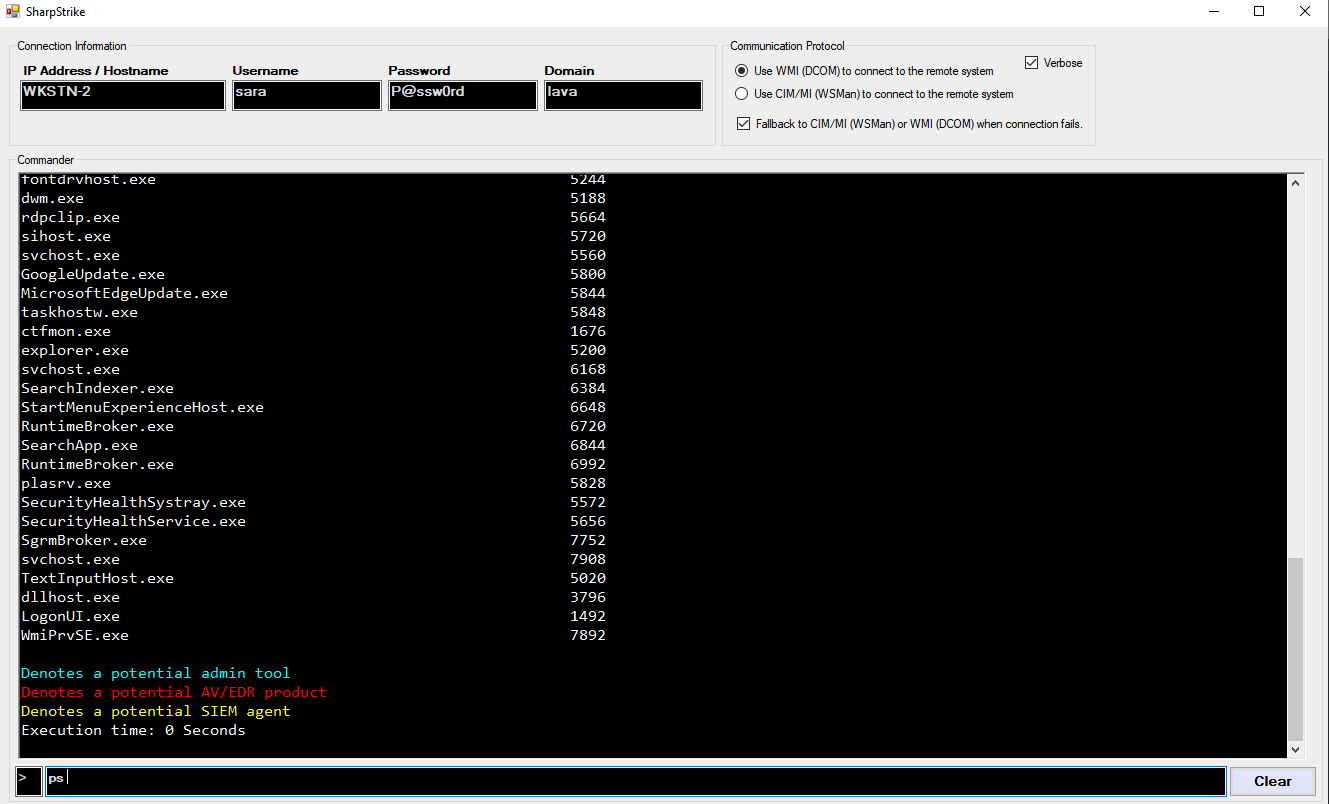
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.