
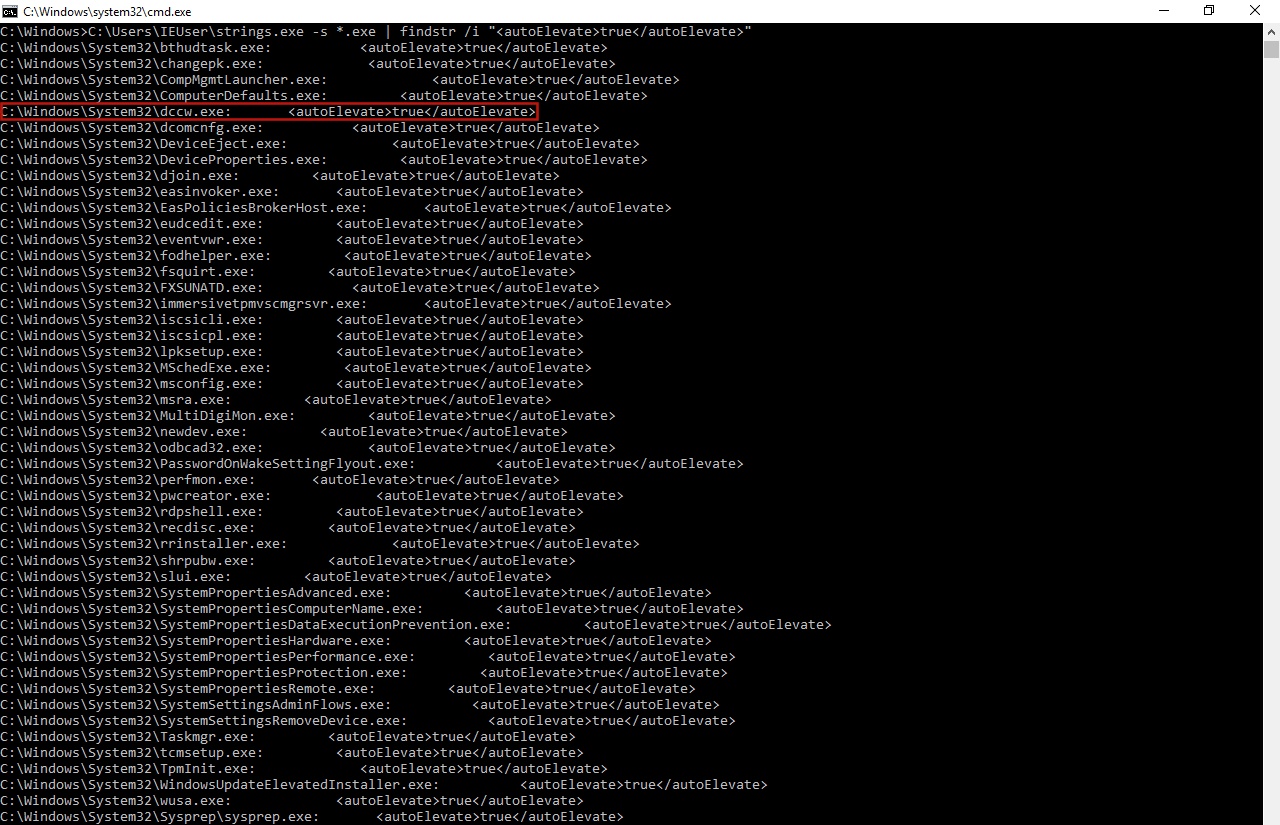
DccwBypassUAC
 l3cr0f/dccwbypassuac
Windows 8.1 and 10 UAC bypass abusing WinSxS in "dccw.exe".
exploitationpayload-developmentpost-exploitation+1
3976 years ago
l3cr0f/dccwbypassuacWindows 8.1 and 10 UAC bypass abusing WinSxS in "dccw.exe".
 nullbyte-7w7/cve-2024-48990
Proof-of-concept exploit for CVE-2024-48990 demonstrating PYTHONPATH hijacking in needrestart to achieve local privilege escalation via SUID binary…
 k0mraid3/k0mraid3s-system-shell-prebuilt
Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…